CryptoPayment Gateway Flaw: CVSS 10.0 Exploited
Some WordPress plugin vulnerabilities need a clever chain of conditions. A specific role, a particular setting, a user who clicks something they should not...
Found 22 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Some WordPress plugin vulnerabilities need a clever chain of conditions. A specific role, a particular setting, a user who clicks something they should not...
Your WordPress site might be handing anonymous visitors a route straight into your server's filesystem, because a security researcher just published a proo...
A high-severity flaw in the Elementor Website Builder plugin could let an unauthenticated attacker create rogue administrator accounts and take full contro...
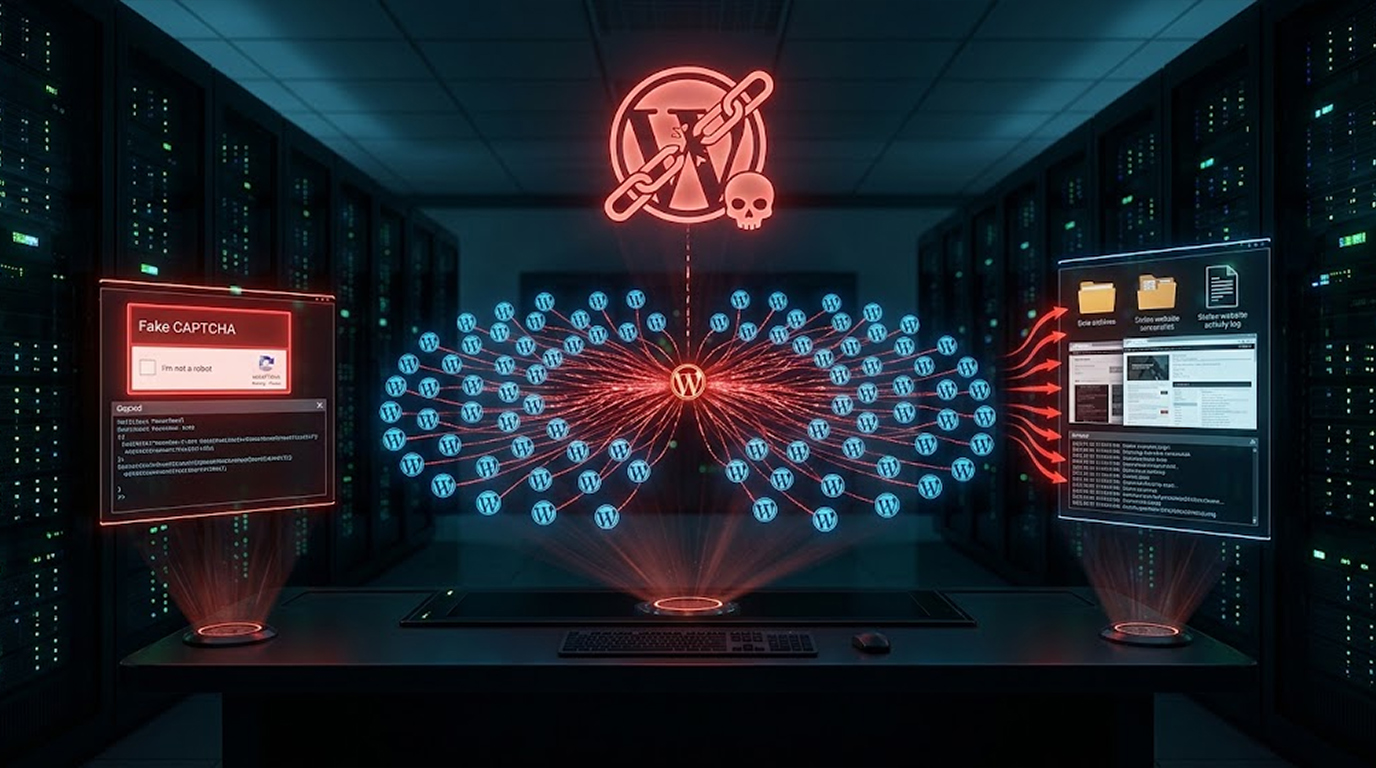
A huge worldwide cybercrime campaign is employing close to 2,000 hacked WordPress websites as a criminal infrastructure for spread malware, steal data, and...
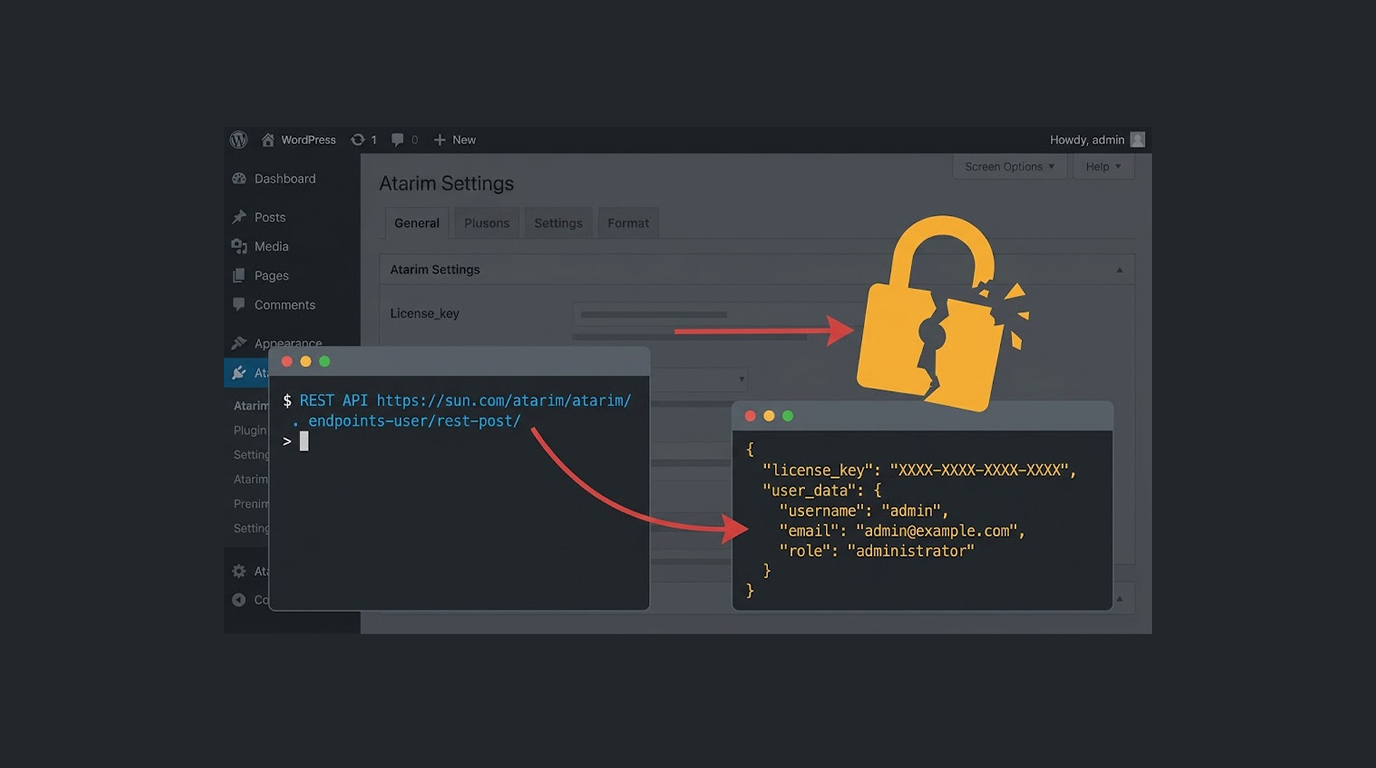
There exists a security vulnerability in the Atarim plug-in which exposes attackers to steal sensitive data without going through any kind of authenticatio...
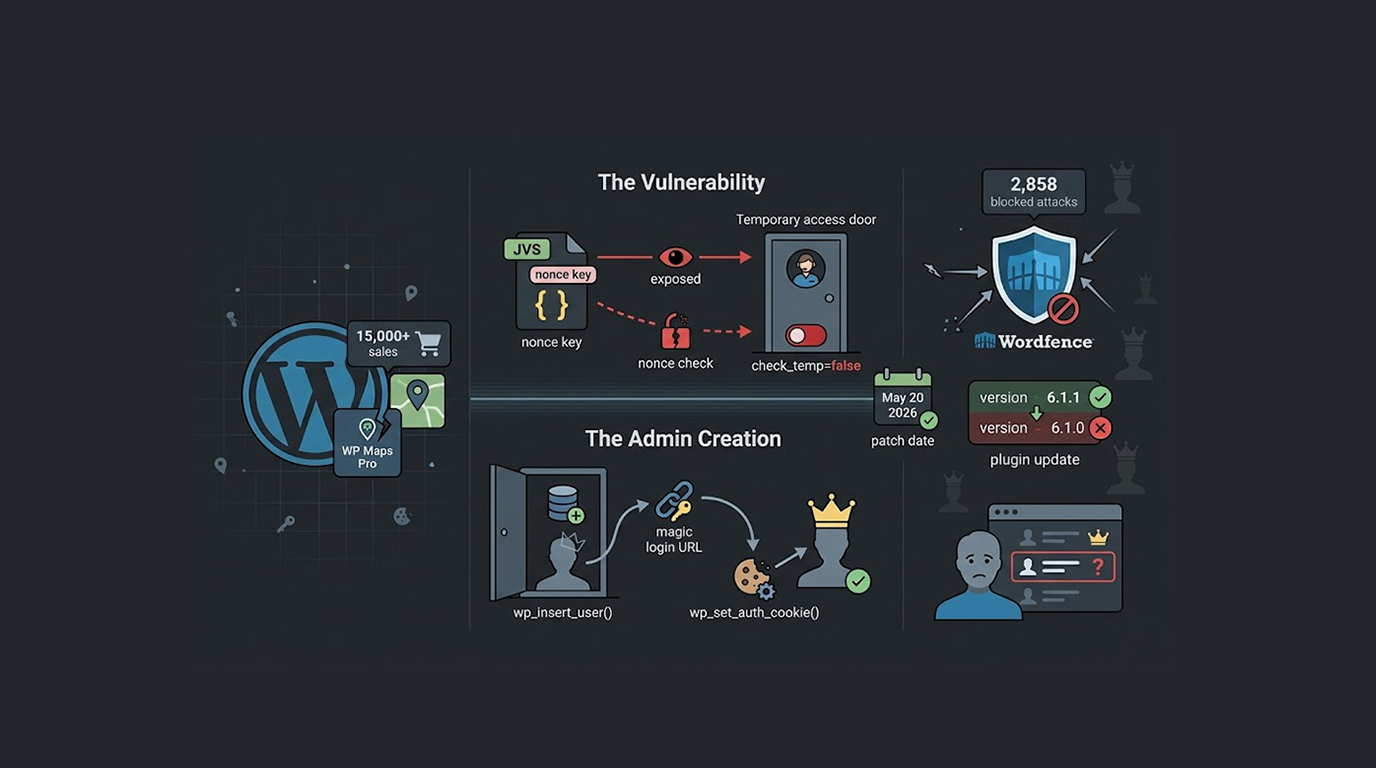
A critical vulnerability has recently come to light in the WP Maps Pro WordPress plugin that is currently being actively exploited. As a result, unauthenti...
Your website traffic suddenly crashes. Google shows scary warnings. Orders stop coming in. This nightmare scenario hits thousands of WordPress owners every...
Local File Inclusion (LFI) is flagged as a high-severity vulnerability within the Madara Theme for Wordpress that permits unauthenticated attackers to read...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067