Optimizely Injection: 178 Sites Served Malicious Code
The trust model behind third-party experimentation tools is simple. You put a script tag on your page, the vendor serves the code, and you trust the vendor...
Found 24 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
The trust model behind third-party experimentation tools is simple. You put a script tag on your page, the vendor serves the code, and you trust the vendor...
Scoping sounds like the easy part of incident response, because you already know how to search a filesystem and you already know how to read an audit log,...
Two incidents can look identical in the alert queue and be entirely different animals underneath, because one of them means somebody read data they shouldn...
Attackers are actively exploiting a zero-day SQL injection flaw in Arista's VeloCloud Orchestrator, which is the central management system for VeloCloud SD...
You patched the vulnerability, you removed the suspicious file, and you thought the incident was over, then two weeks later the same thing happens again, b...
Two critical WordPress plugin vulnerabilities are making the rounds. One is being actively exploited right now. The other is a pair of flaws that could let...
Everyone's talking about how AI is speeding up attacks. And it is. But here's the thing. Skilled humans can still move just as fast. Sometimes faster. Sys...
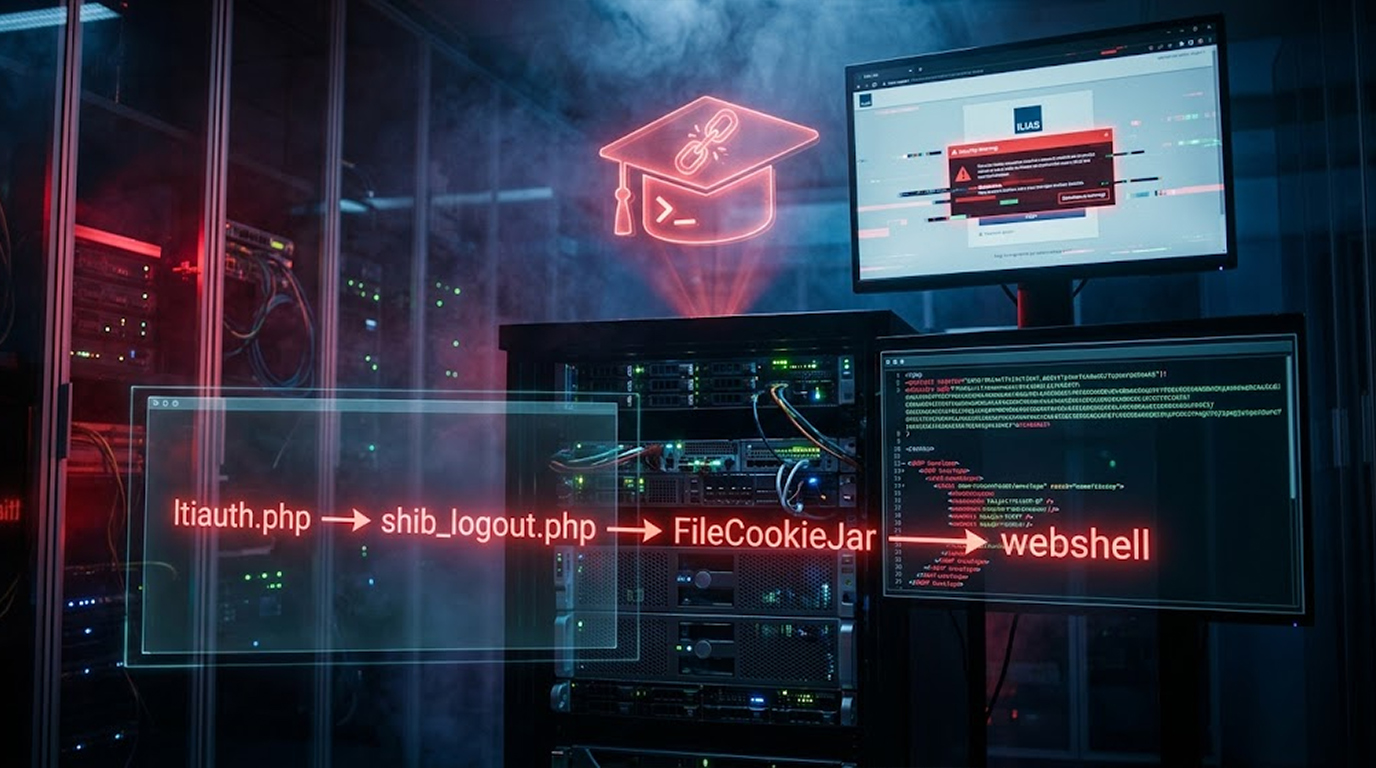
Here's a fun one. ILIAS has two endpoints that don't require authentication. One of them writes to your session. The other one reads your session back and...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067