Generative AI for Event ID 4625 Simulation: Training ML Models
You are building a machine learning model to detect failed logon attempts. You need thousands of Event ID 4625 samples. But you only have a few hundred in...
Found 37 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You are building a machine learning model to detect failed logon attempts. You need thousands of Event ID 4625 samples. But you only have a few hundred in...
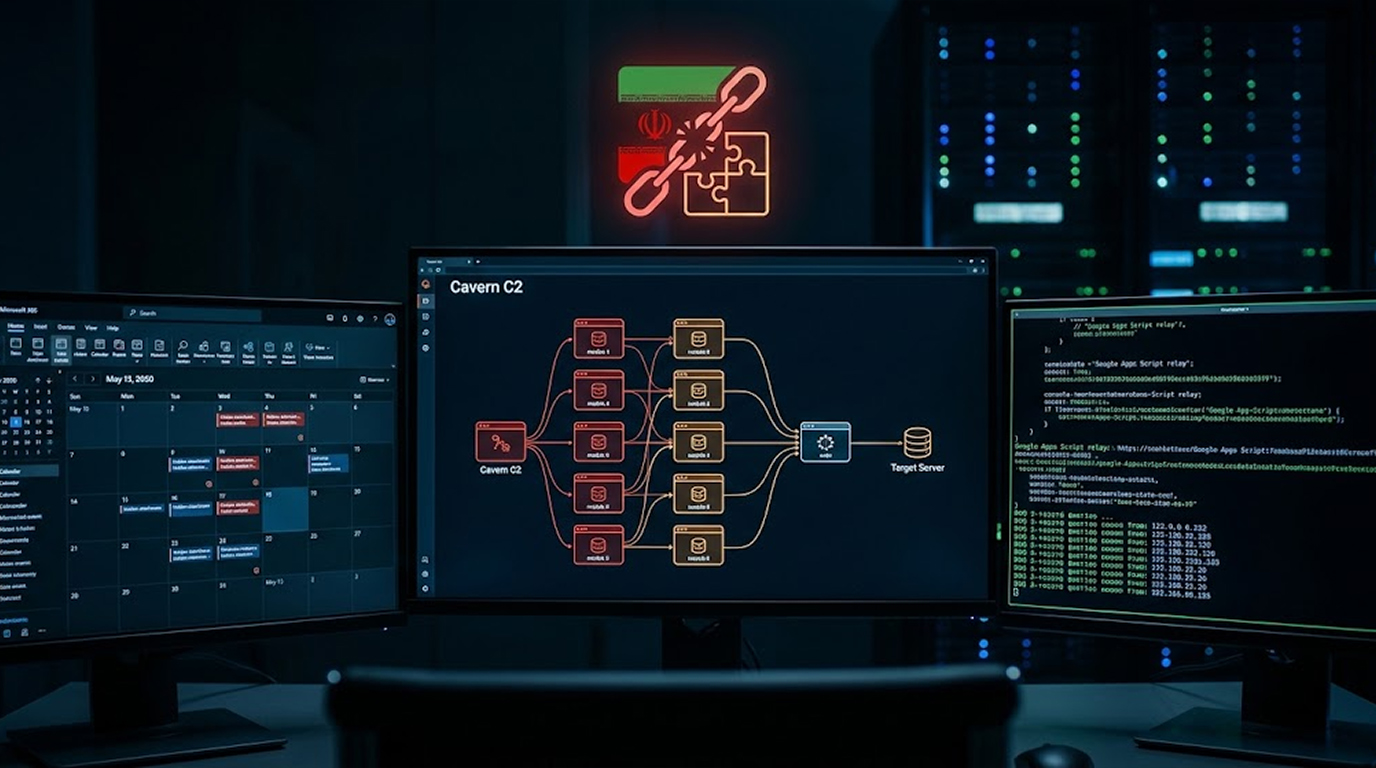
Cybersecurity researchers have found that the Cavern command and control framework set continues to evolve. The toolkit is used by Iranian nation-sta...
Vulnerability in KNX visualisering panels can compromise the smart building control system due to an unauthorized access attack. The vulnerability is broug...
You have heard the terms. Red team attacks. Blue team defends. But when you look at the actual commands, what is the difference? The answer is not the too...
You are scrolling through your feed, and you see a video of a missile strike. It looks dramatic, urgent, and real. You share it, because people need to kno...
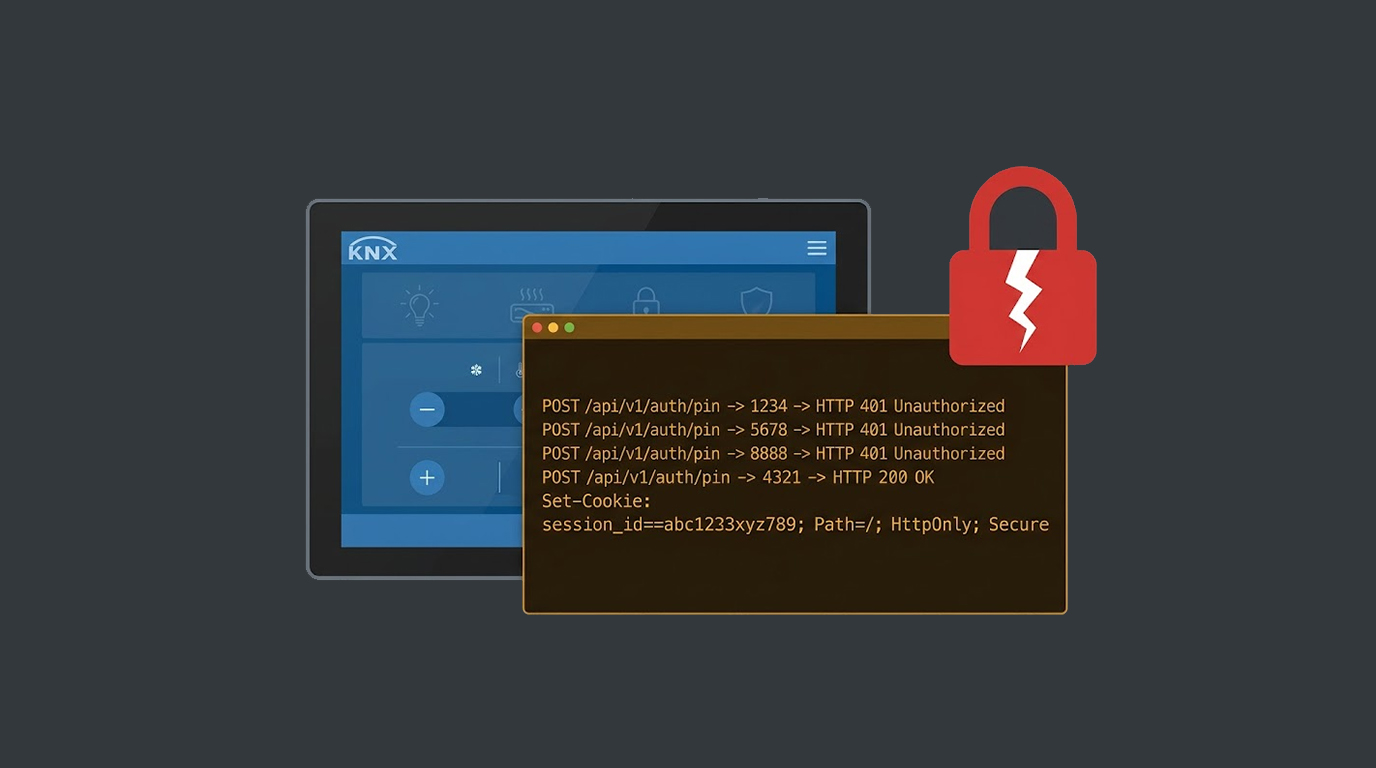
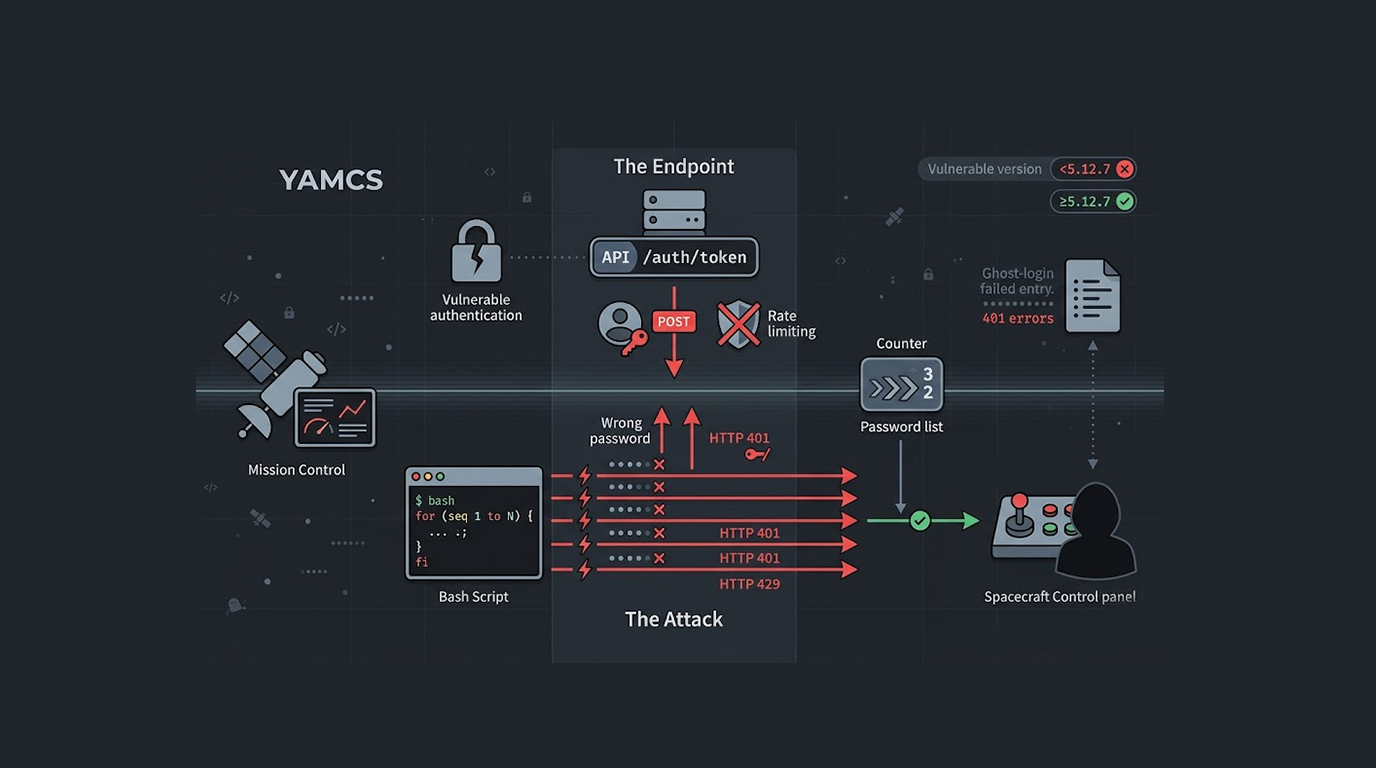
YAMCS contains an exploitable security vulnerability that allows endless brute-force attempts to log into the user accounts, meaning there is no limit on t...
You finally did the right thing, you hired a penetration testing firm to find security holes before the criminals do.You expected a few minor issues, maybe...
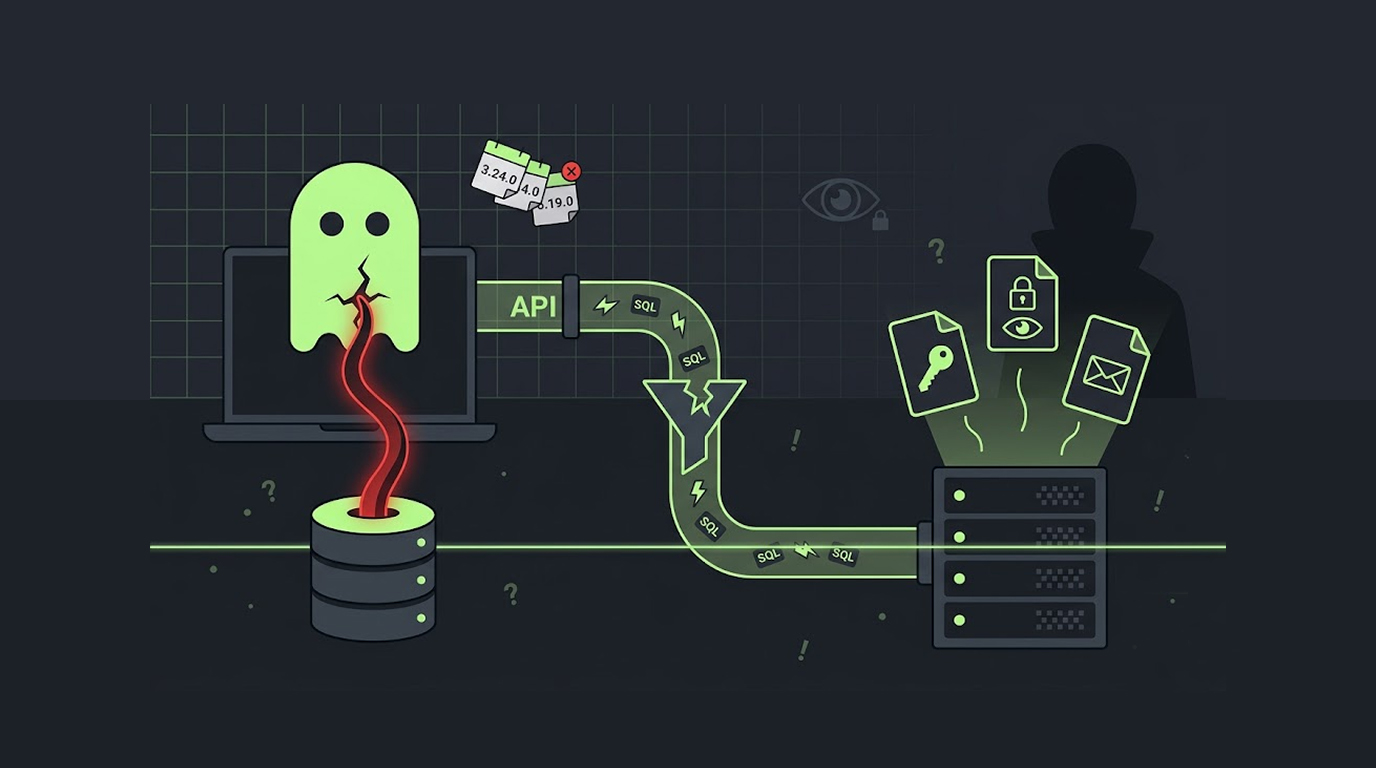
A popular blogging platform has a serious problem, attackers can steal admin passwords and API keys without ever logging in, and the vulnerability has exis...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067