AI-Generated Code Security Risks for Web Apps
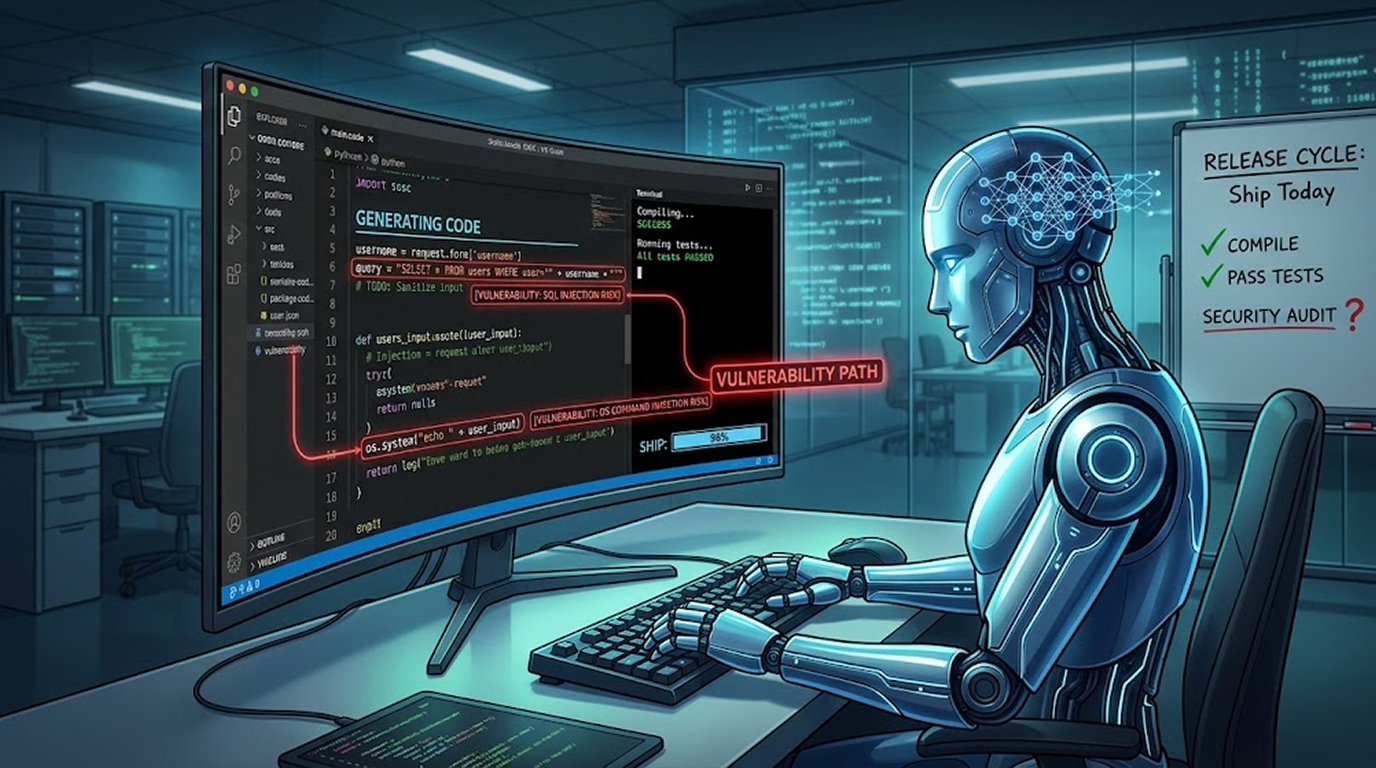
If you've read a headline claiming that roughly half of AI-generated code fails security testing, the number itself is less interesting than what it descri...
Found 40 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
If you've read a headline claiming that roughly half of AI-generated code fails security testing, the number itself is less interesting than what it descri...
You open an attachment, it looks like a normal invoice, a standard contract, a routine report, nothing about it triggers suspicion, and yet the moment your...
There is a version of credential hunting that most teams still picture in their heads, it involves a person, a lot of manual searching, some guesswork, and...
There is a comfortable assumption most teams carry around, and it sounds like this, we use HTTPS everywhere, so tokens are safe in transit. That assumptio...
Your dashboards are green, your EDR is running, your SIEM is ingesting logs, and your SOC is staffed, everything looks healthy, and yet attackers are insid...
You have probably heard the warning, do not unpickle untrusted data, and you probably nodded along because it makes sense, pickle is dangerous, we know thi...
Your open source AI security roadmap for 2027 starts right here. This is your playbook for keeping artificial intelligence systems safe in a world where cy...
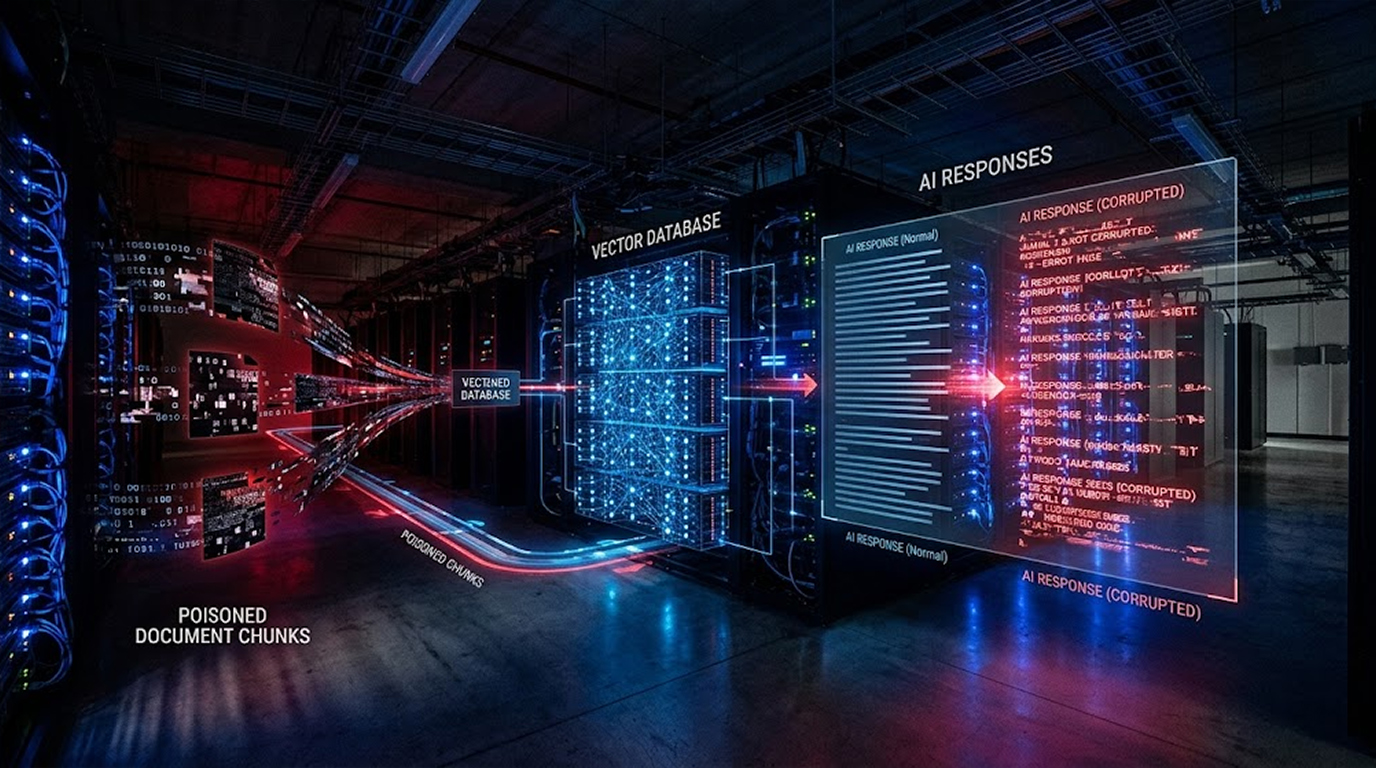
Your AI assistant just told a developer to install a malicious package. It cited a "trusted" internal document as the source. The document looked legitimat...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067