Chainalysis Breach: LLMjacking Goes Industrial
Chainalysis went public this week with the full scope of what it is calling a multi-front cyber attack, and the number is worse than the initial disclosure...
Found 55 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Chainalysis went public this week with the full scope of what it is calling a multi-front cyber attack, and the number is worse than the initial disclosure...
VulnCheck has confirmed what every industrial security team was dreading. A maximum-severity vulnerability in Siemens SIMATIC IoT2050 Advanced devices is n...
Most people treat their Google account as one account among many, a login they use for email and a few apps, and that mental model is dangerously out of da...
Stealers have always been blunt instruments. They grab everything, dump it on a Telegram channel, and let whoever buys the logs sort out what matters. VOL...
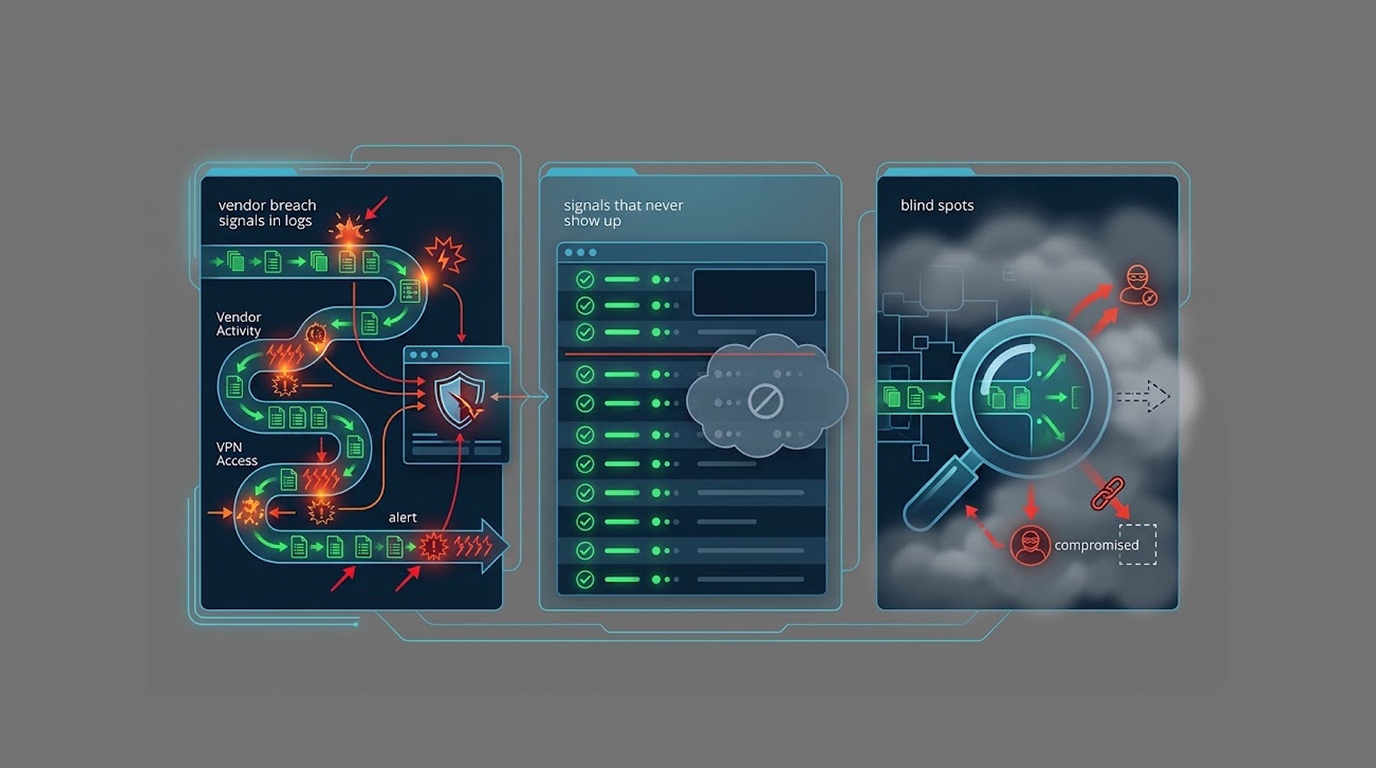
When a vendor gets breached, the first thing most organizations discover is that they have almost no visibility into what happened, because the compromised...
Your AI coding agent might have executed an attacker's command just because you tried to log in, because a flaw in the OpenCode AI coding agent allowed a m...
Your AI gateway might have handed over cloud credentials to an attacker this week, because LiteLLM just disclosed a severe compromise that pushed a malicio...
Your self-managed GitLab server might be accepting remote code execution from anyone who sends the right request, because GitLab just released emergency fi...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067