How Attackers Use Patience to Bypass EDR & SIEM
In 2026, the loud, noisy attacks that light up every alert in your EDR and SIEM are becoming less common among sophisticated actors. The new gold standard...
Found 14 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
In 2026, the loud, noisy attacks that light up every alert in your EDR and SIEM are becoming less common among sophisticated actors. The new gold standard...
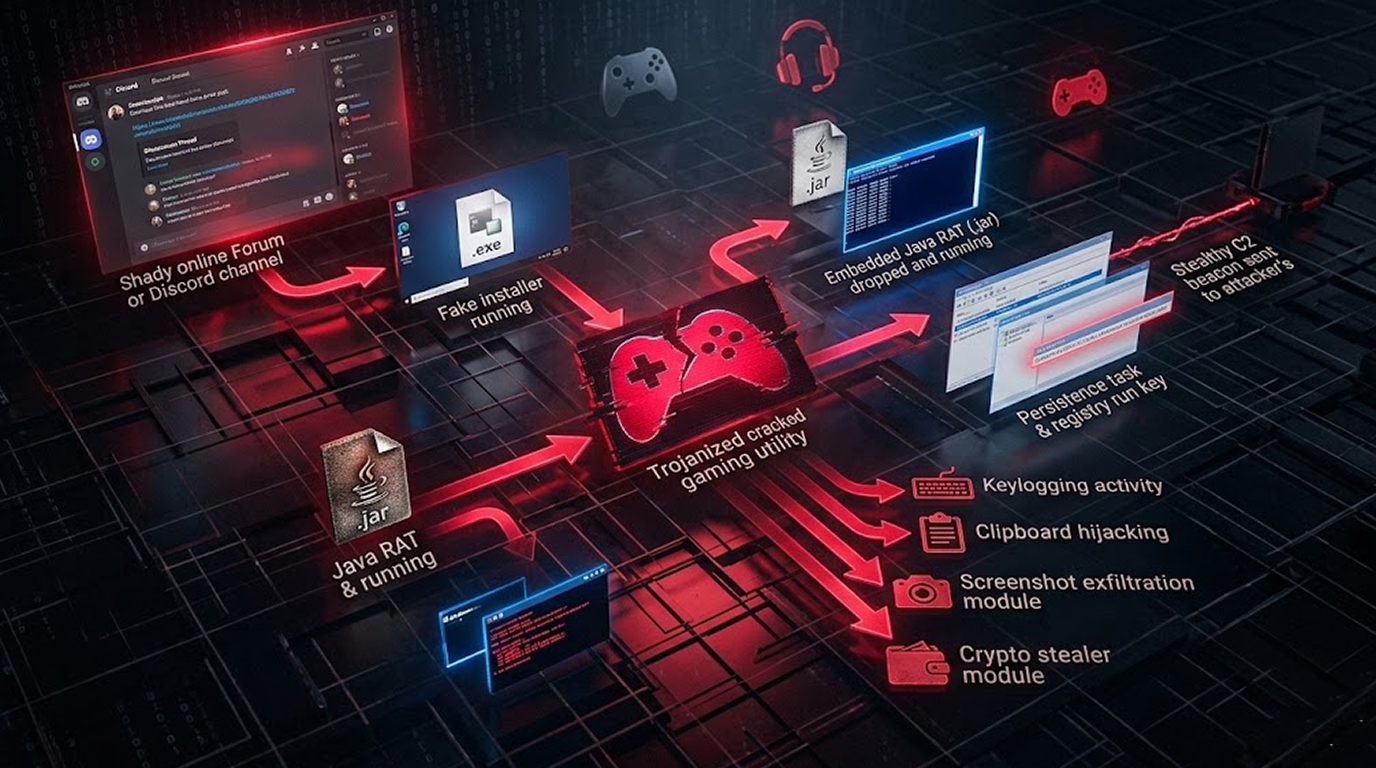
Threat actors have found a new way to hook gamers: they're slipping remote access trojans (RATs) into what look like handy gaming utilities, then spreading...
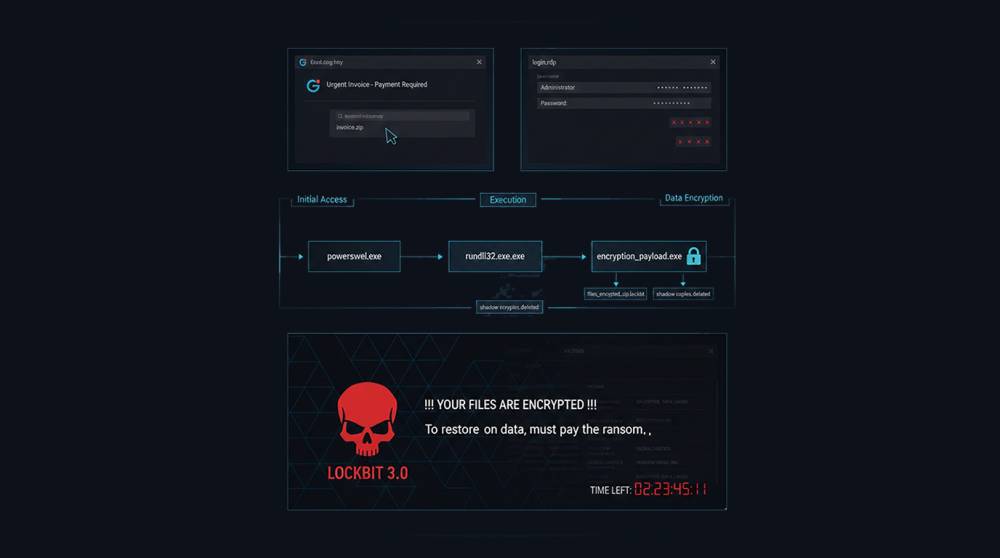
LockBit is (or was) the most active and profitable ransomware-as-a-service (RaaS) operation in recent years. The group provides the LockBit ransomware buil...
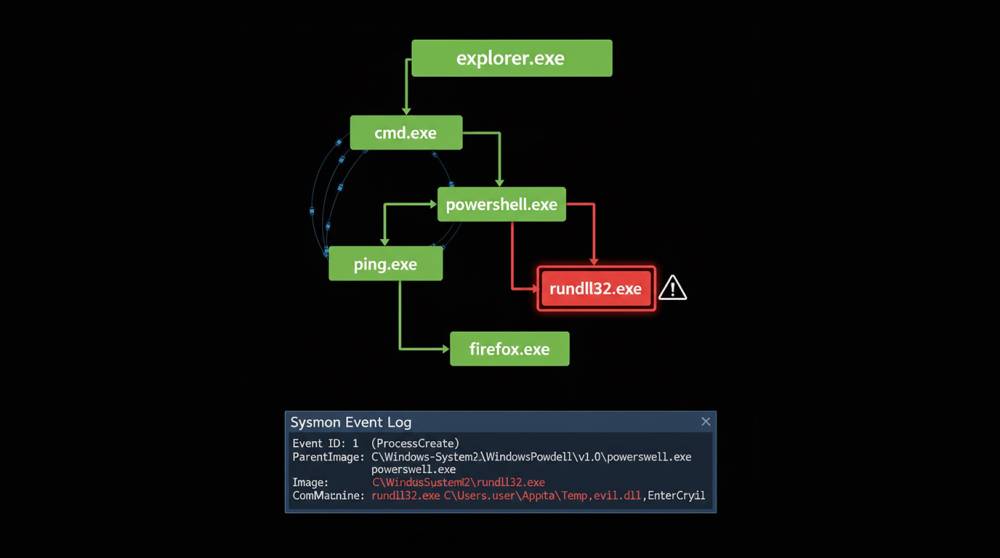
Process ancestry monitoring tracks the parent-child relationships between processes (who spawned what). This is one of the most reliable ways to detect liv...
You can’t patch what you don’t know exists. Zero-day exploits, unknown vulnerabilities, and novel attack chains are the nightmare scenario for...
Living off the Land is a modern malware technique that exploits built-in Windows tools, and legitimate programs, as opposed to leaving behind nefarious fil...
The ClickFix method of social manipulation is not the use of an individual malware file but rather refers to a process that has been established to persuad...
Digital signatures were created to build trust.They answer a simple question:“Was this file changed, and who signed it?”The problem is not the...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067