Types of Videoconferencing Malware and How Each One Works
"Videoconferencing malware" gets used as if it describes a single thing, and it doesn't, because the software in question is abused in at least a dozen dis...
Found 24 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
"Videoconferencing malware" gets used as if it describes a single thing, and it doesn't, because the software in question is abused in at least a dozen dis...
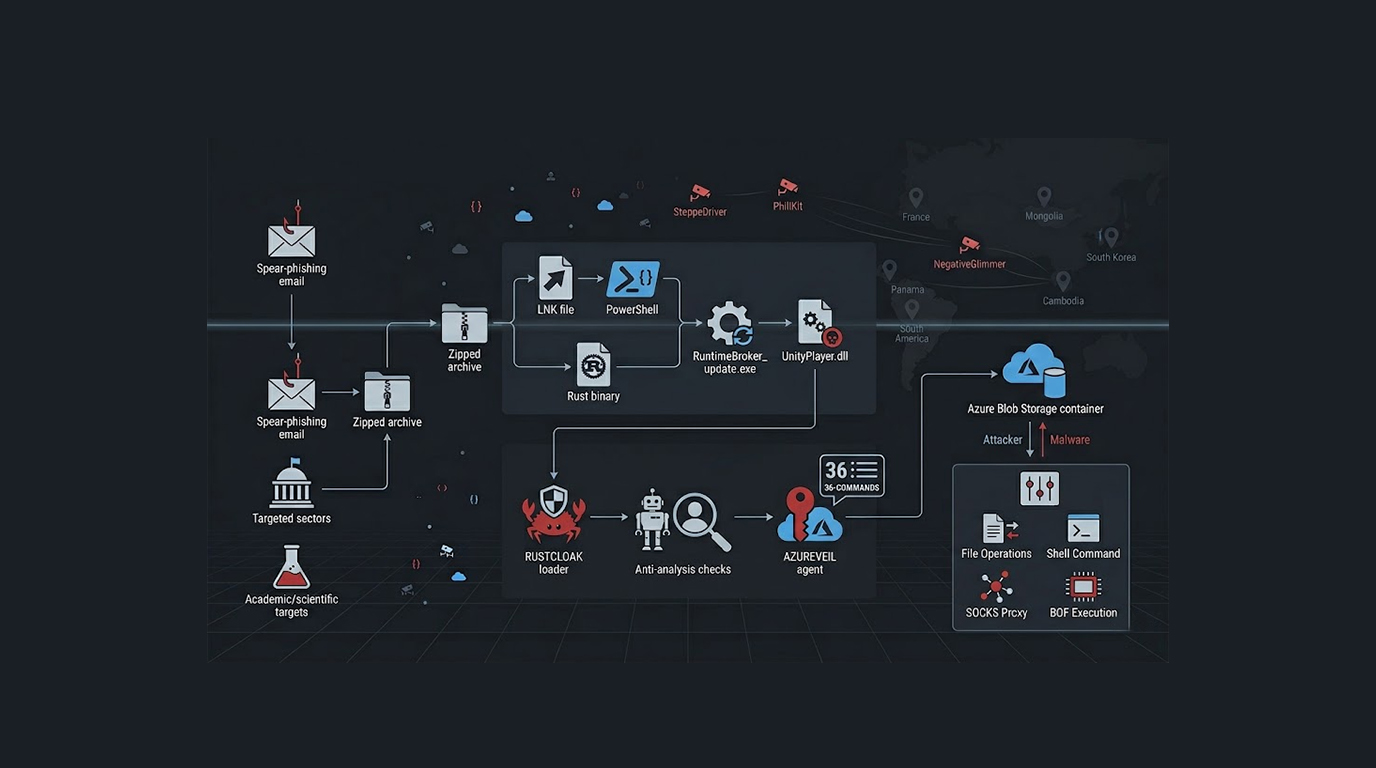
There is an email sitting in a university researcher's inbox right now. It looks like a research proposal, or a conference invitation, or a document from a...
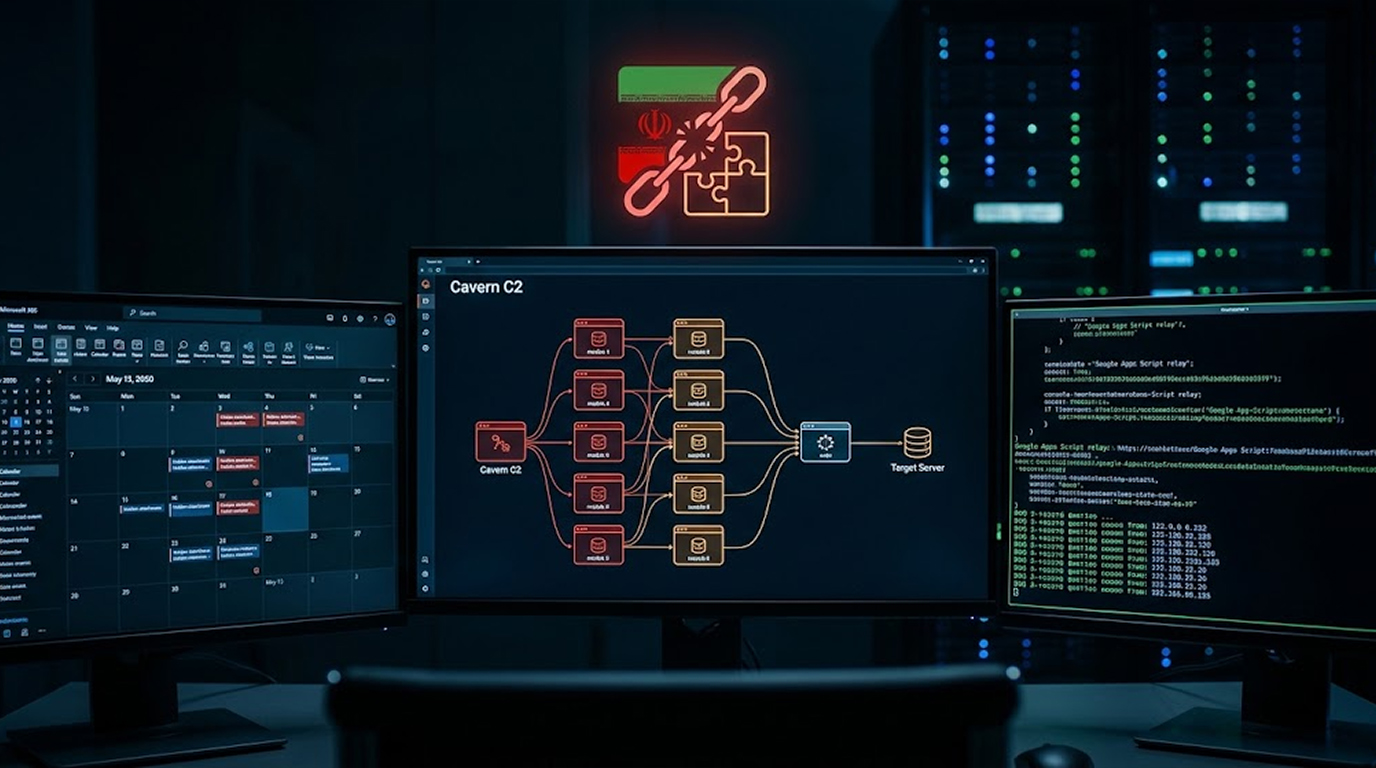
Cybersecurity researchers have found that the Cavern command and control framework set continues to evolve. The toolkit is used by Iranian nation-sta...
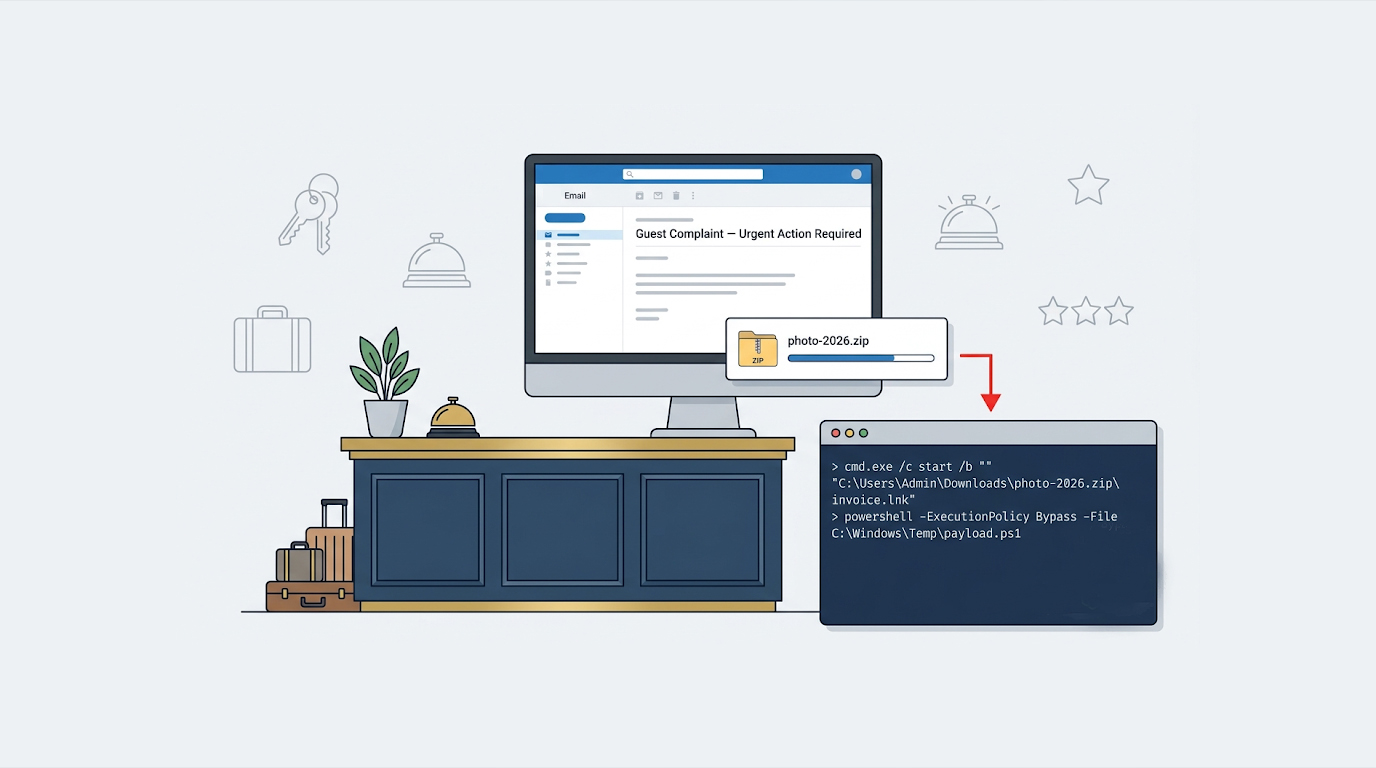
Your front desk receives an email. It looks like it came from Calendly. The display name says "Booking Manager." The subject mentions a guest complaint. Th...
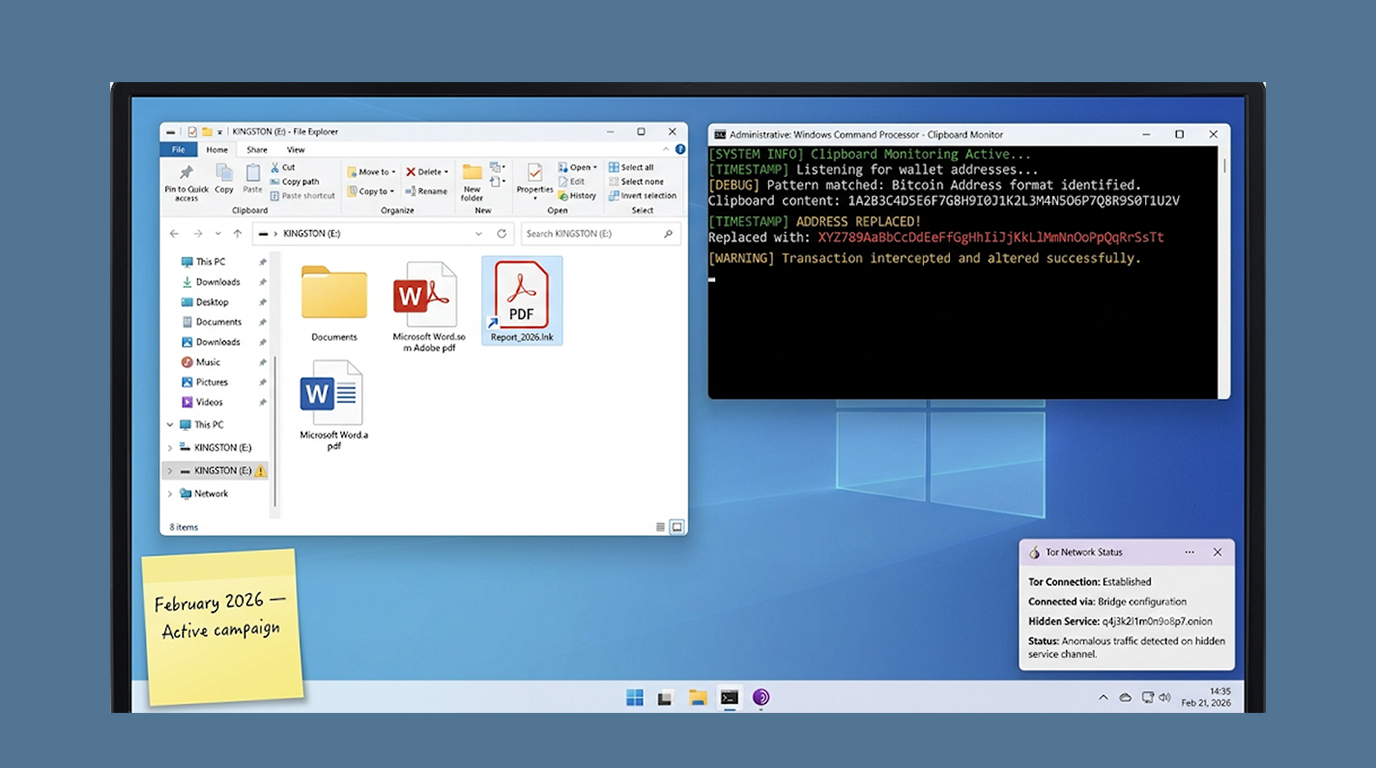
In a new report from Microsoft, window-based cryptocurrency clipper campaign, running since February 2026, has been disclosed. The malware intercepts clipb...
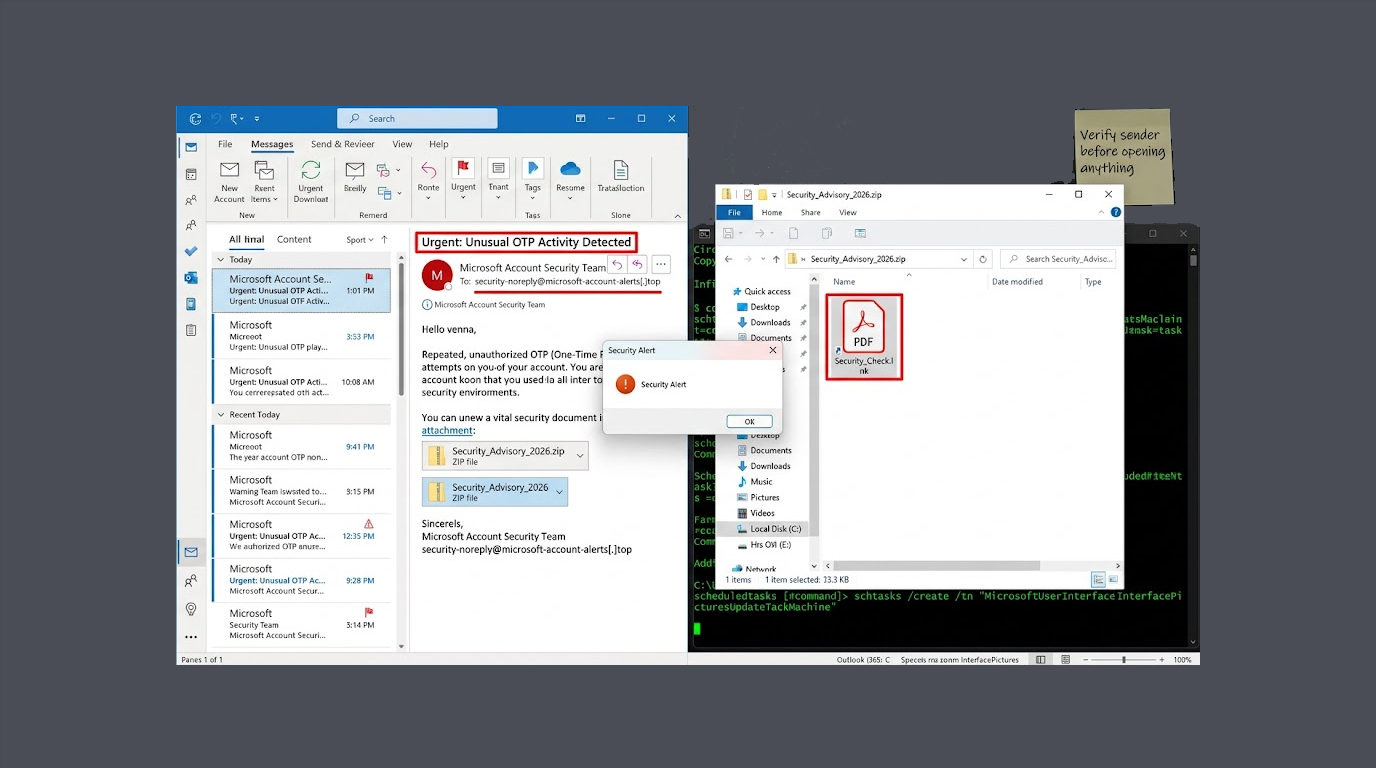
You receive an email. It looks like it is from Microsoft. It warns about suspicious activity on your Microsoft Account. Someone is generating one-time pass...
Officials and citizens in the Czech Republic and Taiwan have become victims of a new cyber espionage operation called Operation Dragon Weave. Attackers are...
Microsoft fixed a security flaw in February. Attackers found a way around it. Now the company has admitted the incomplete patch left a different vulnerabil...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067