Network Interception for Tokens: When HTTPS Isn't Enough
There is a comfortable assumption most teams carry around, and it sounds like this, we use HTTPS everywhere, so tokens are safe in transit. That assumptio...
Found 7 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
There is a comfortable assumption most teams carry around, and it sounds like this, we use HTTPS everywhere, so tokens are safe in transit. That assumptio...
Picture this. You check into a hotel, connect to the Wi-Fi, and see a browser update prompt. It looks legitimate. You click it, install the update, and go...
Many times, an attacker will still be acquiring knowledge about their target via reconnaissance activities when their campaign is in the initial phases at...
What “Malware Free” Actually MeansNot all compromises involve payloads, binaries, or dropped files.Some of the most persistent incidents never...
Recently, an exploit has been discovered in older model routers from D-Link (Product Code: DGS-2100) due to a security vulnerability identified with the CV...
Hackers can take control of your browser through a method known as browser hijacking. By exploiting vulnerabilities, malicious software can manipulate your...
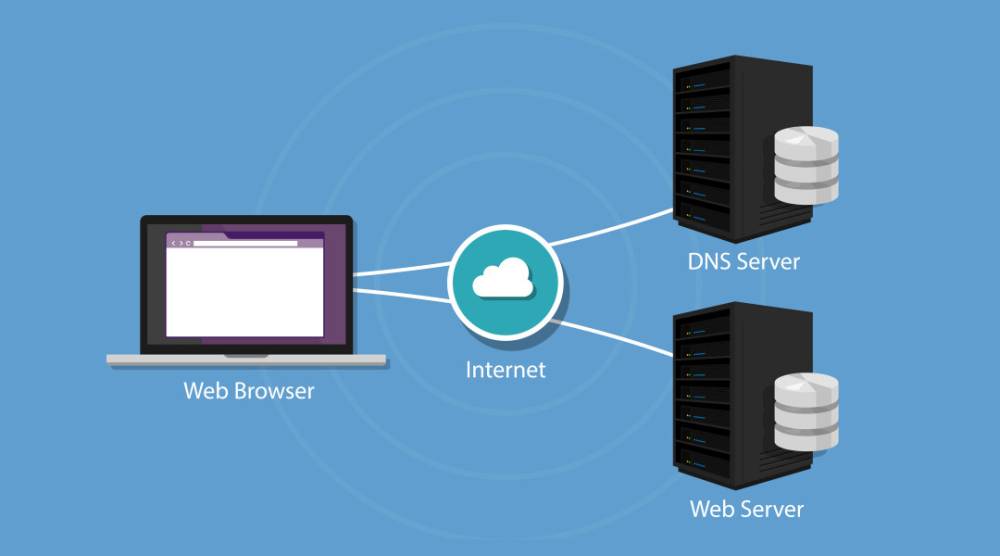
DNS attacks exploit vulnerabilities in the Domain Name System (DNS), the internet's "address book" that translates domain names into IP addresses. Hackers...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067