Measuring Security Culture: What Predicts Fewer Incidents
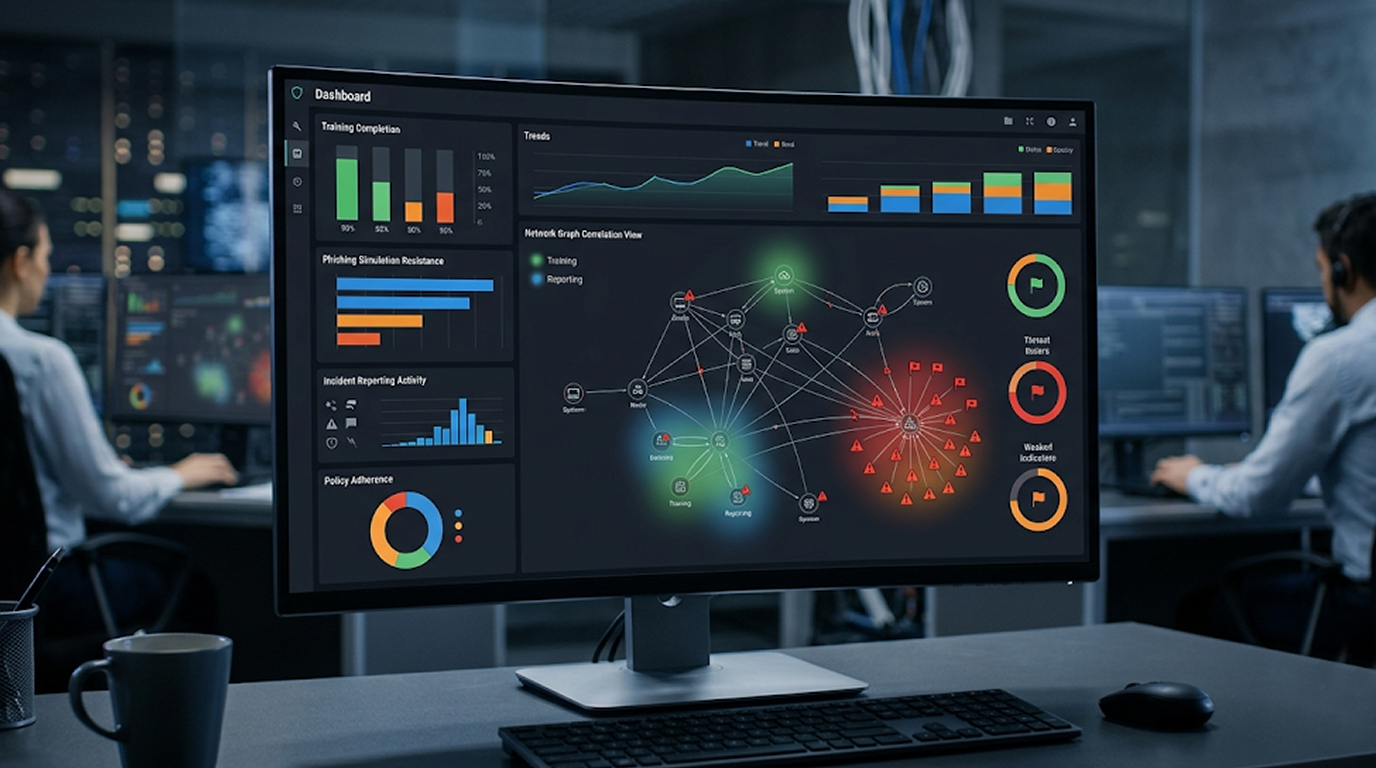
Many organizations invest heavily in security tools, training completion rates, and compliance checklists, yet these often do not lead to a reduction of ac...
Found 135 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Many organizations invest heavily in security tools, training completion rates, and compliance checklists, yet these often do not lead to a reduction of ac...
In 2026, malware developers are becoming interested in Zig due to its use as a modern day replacement for C as a systems programming language. Whereas legi...
Your business relies on service accounts. They connect your website to email platforms, your CRM to marketing tools, your cloud storage to backup systems....
SSTI (Server Side Template Injection) is an incredibly hazardous as well as often overlooked method of code injection that has been used against modern web...
A China-aligned threat actor has resumed targeting European government and diplomatic organizations after a two-year period of relative inactivity in the r...
As of 2026, webshells still rank among the most consistent methods attackers use to retain persistent access once they achieve RCE for the first time. Alth...
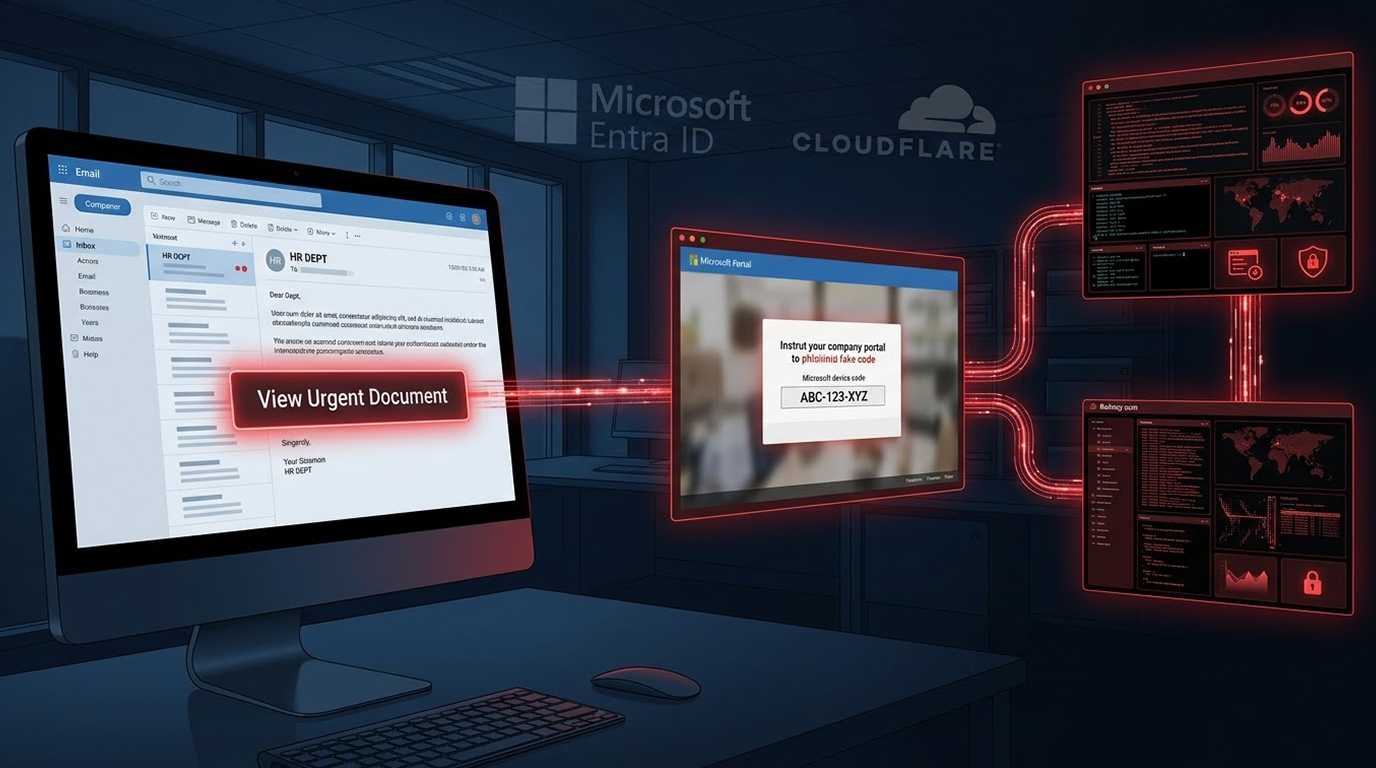
Cybersecurity researchers at Huntress have raised the alarm about a fast-moving device code phishing campaign that is actively targeting Microsoft 365 acco...
Building a strong cybersecurity defense or launching an offensive red team op, rarely happens in isolation. The best insights come from real conversations...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067