Detecting a Vendor Breach From Your Own Logs
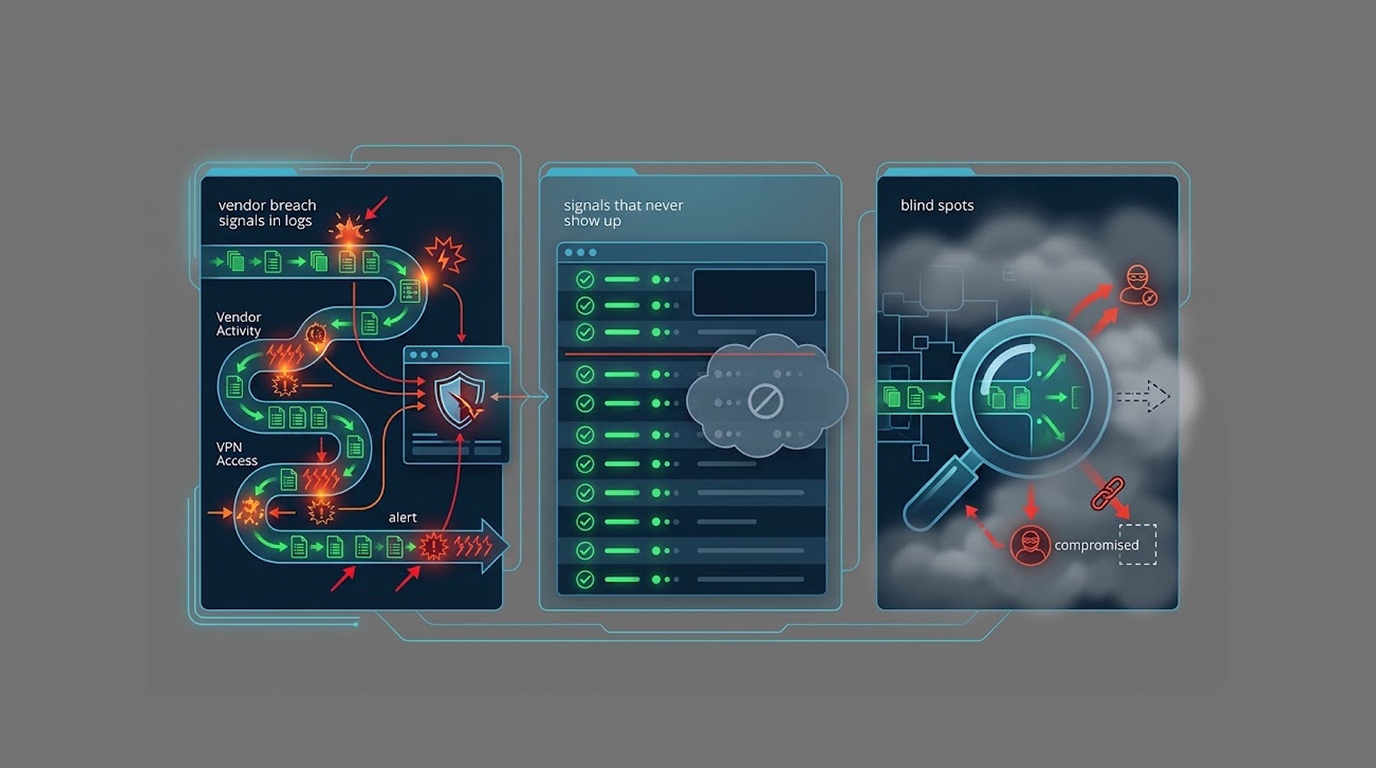
When a vendor gets breached, the first thing most organizations discover is that they have almost no visibility into what happened, because the compromised...
Found 1469 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
When a vendor gets breached, the first thing most organizations discover is that they have almost no visibility into what happened, because the compromised...
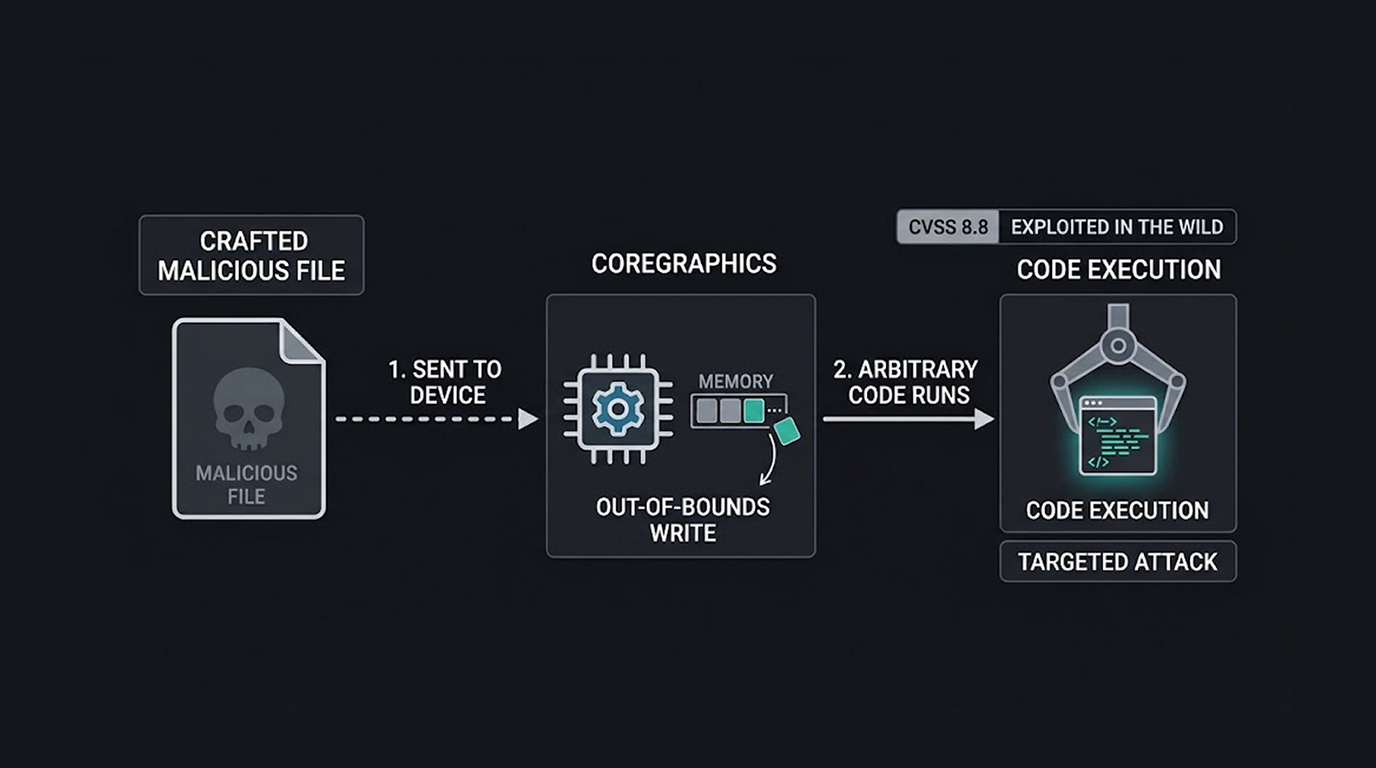
If you are holding onto an older iPhone or iPad, you need to update it right now. Apple just quietly pushed out a critical security patch because a zero-da...
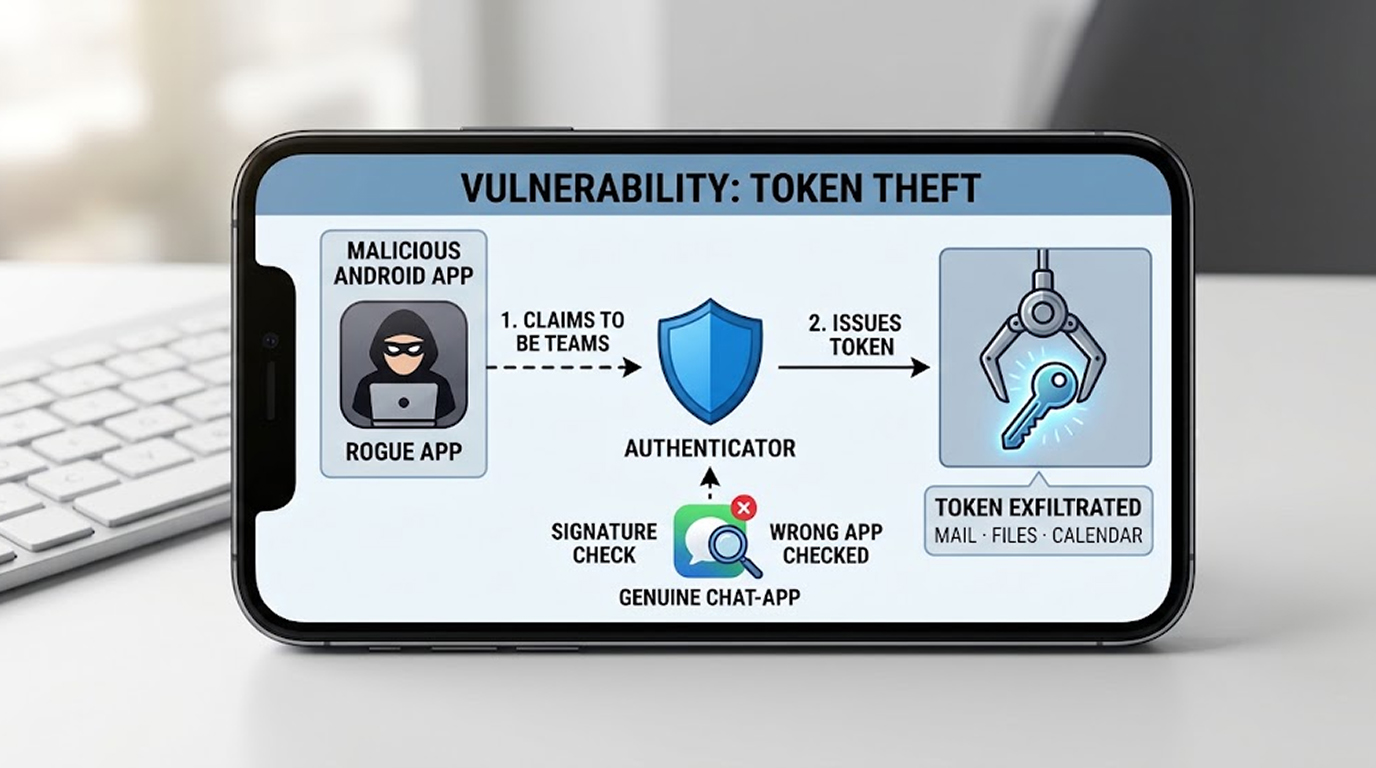
Microsoft just patched a nasty flaw in its Authenticator app for Android, because a malicious app with zero permissions could pose as a trusted Microsoft a...
Your Keystone hardware wallet might not be the genuine article, because an attacker who breached the company's website walked away with the cryptographic k...
You've just shared a Google Drive link with a colleague, a client, or a friend, and then a thought hits you a few minutes later: who else can open this lin...
A severe memory-corruption flaw in Google's Brotli decoder is currently sitting inside many of the programs you use to unpack compressed data, and because...
Security researchers often find themselves waiting for a vendor to release a patch, but when the vendor is a decade-old abandoned piracy app, waiting is no...
Ruby just released versions 4.0.9, 3.4.12, and 3.3.13 to fix three specific bugs inside Onigmo, the regular expression engine built directly into the langu...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067