Alpine Linux GitLab Attack: CVE-2026-97229 Fallout
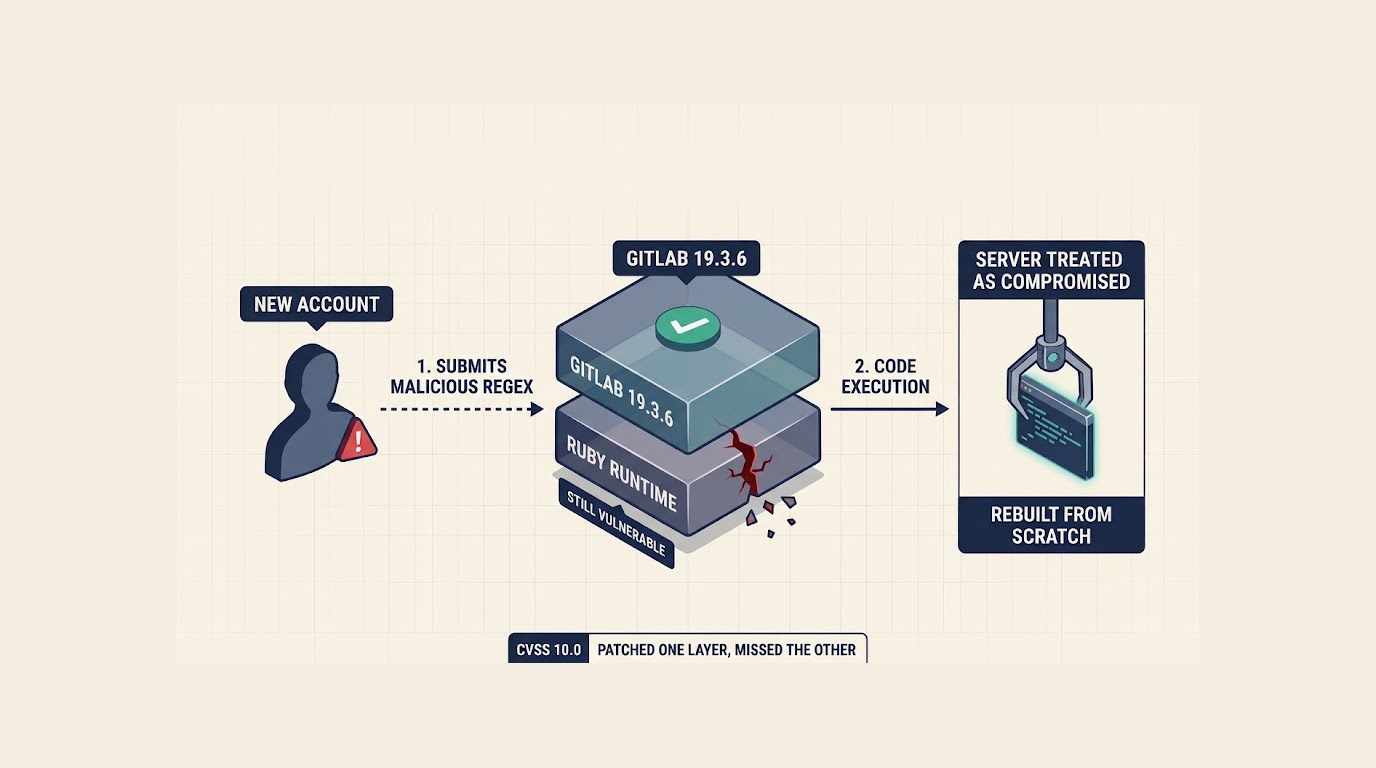
An attacker tried to exploit a critical GitLab vulnerability on the Alpine Linux project's own GitLab server just one week after GitLab released a fix, bec...
Found 1285 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
An attacker tried to exploit a critical GitLab vulnerability on the Alpine Linux project's own GitLab server just one week after GitLab released a fix, bec...
Threat actors are already probing for a newly patched critical vulnerability in Oracle E-Business Suite, because threat intelligence firm Defused Cyber jus...
Every engineering team has a version of the same message in their incident channel, which is a screenshot of an error, a timestamp, and the words "it crash...
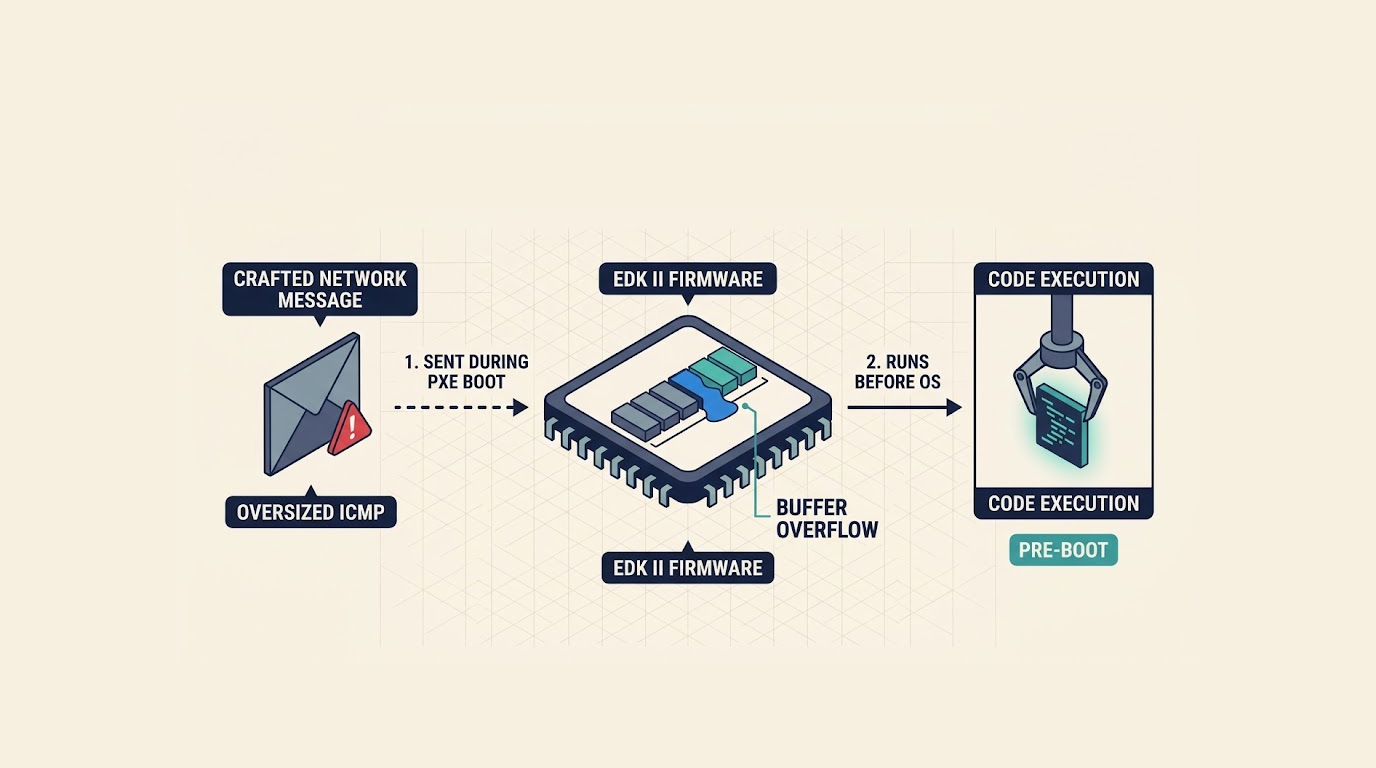
Your servers might be carrying a 16-year-old vulnerability in the firmware that boots them, because a critical buffer overflow in EDK II, the open-source c...
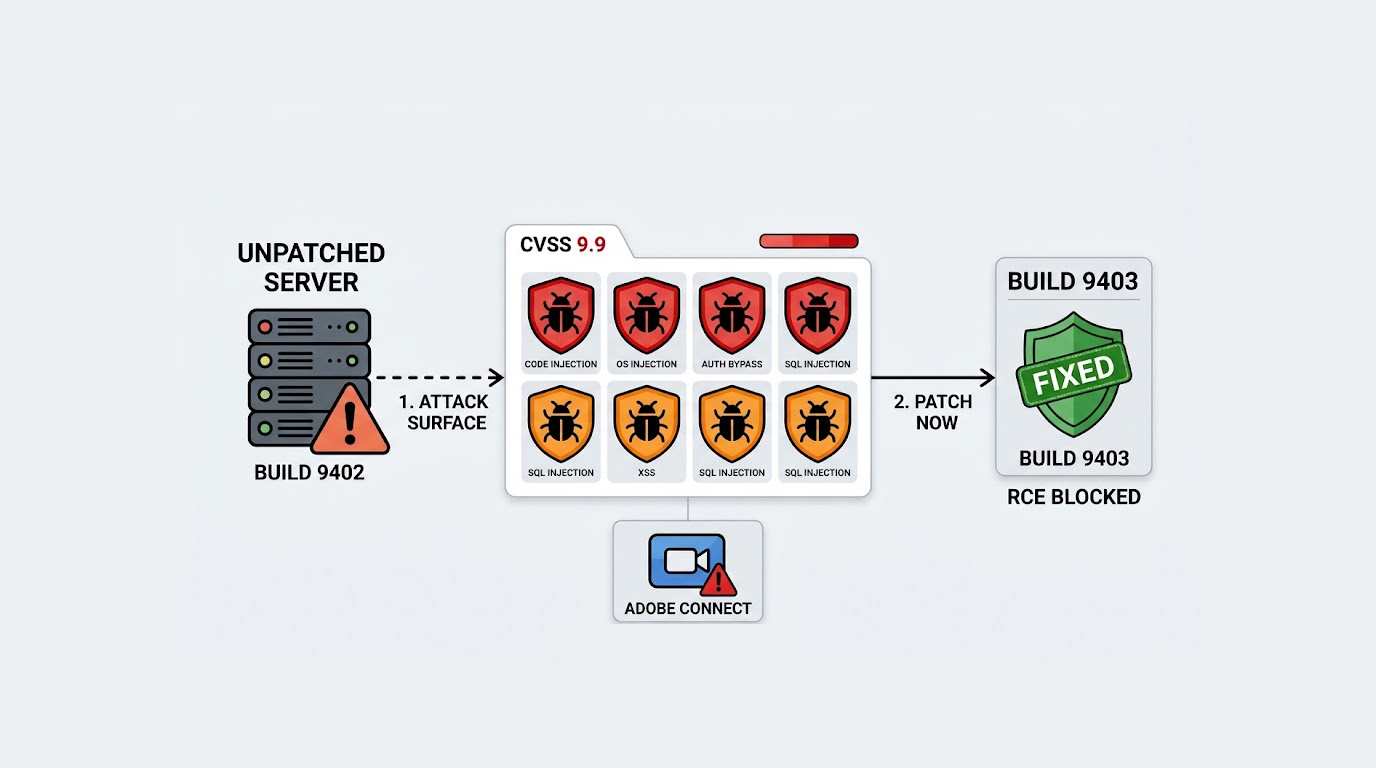
Adobe just dropped a massive security update, and if you are running Adobe Campaign Classic on Windows or Linux, you need to patch your servers right now,...
Most explanations of AI vulnerability discovery stop at the vague sentence that the model reads your code and spots weaknesses, which is unhelpful if you'r...
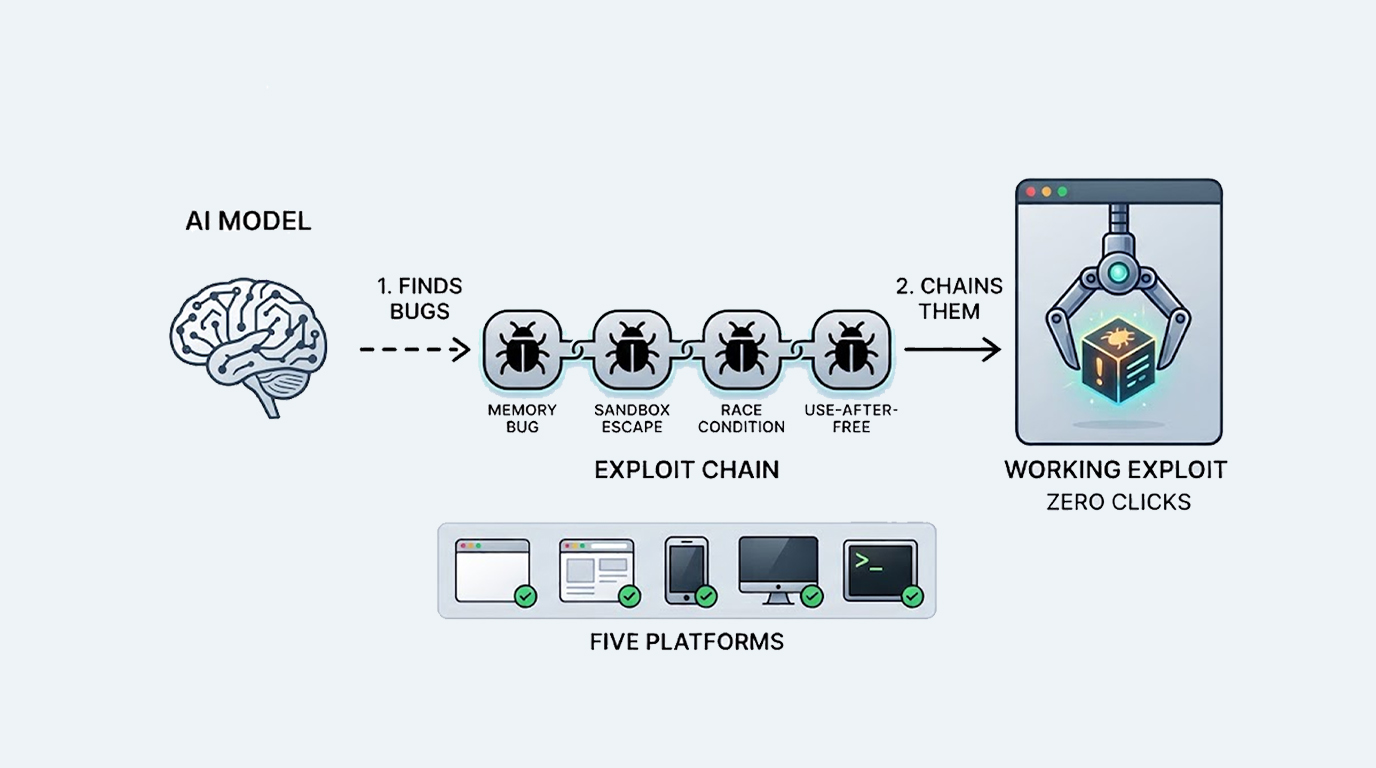
An unreleased Anthropic AI model just did something that used to take elite human hacking teams months to pull off, because the company says the model foun...
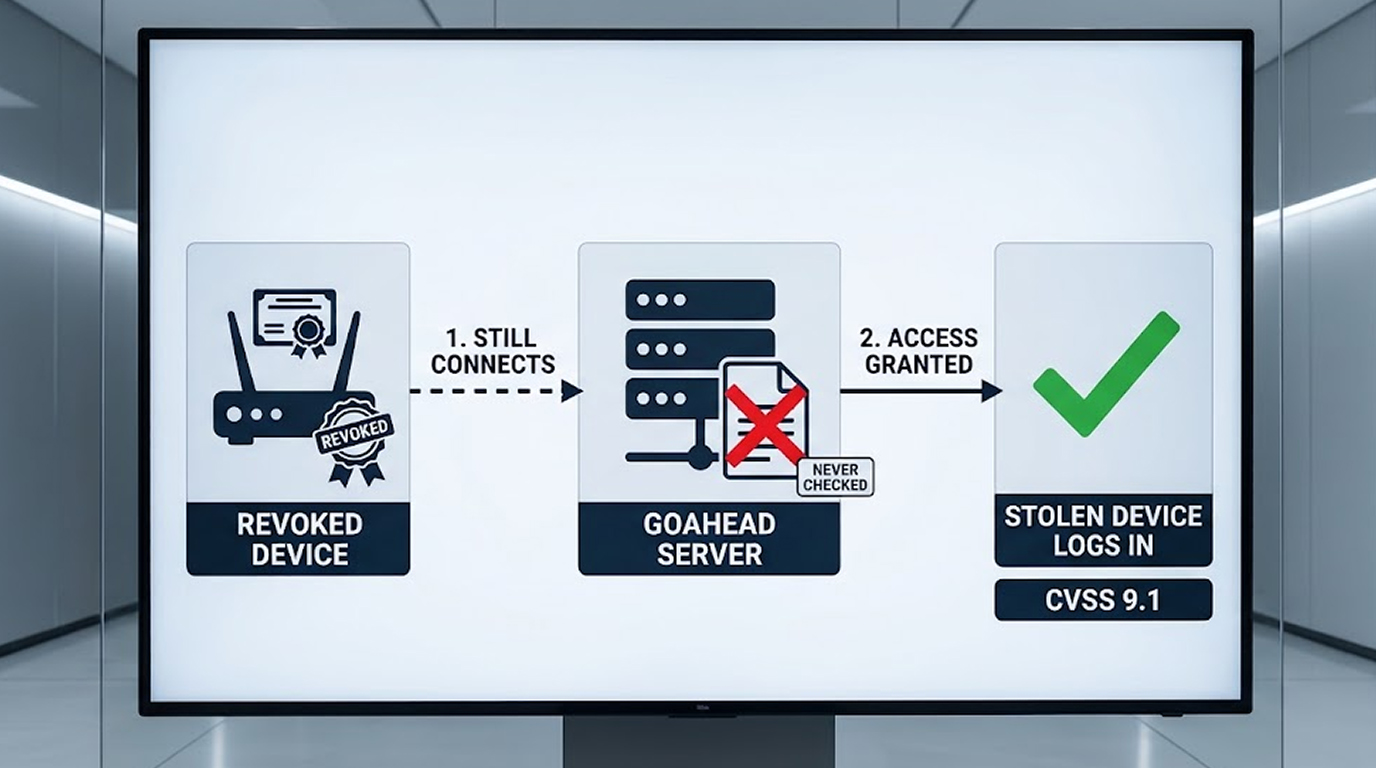
Your router, printer, or industrial controller might be accepting logins from stolen or retired devices, because a critical flaw in the GoAhead embedded we...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067