FatFs File System Flaws Expose Embedded Devices
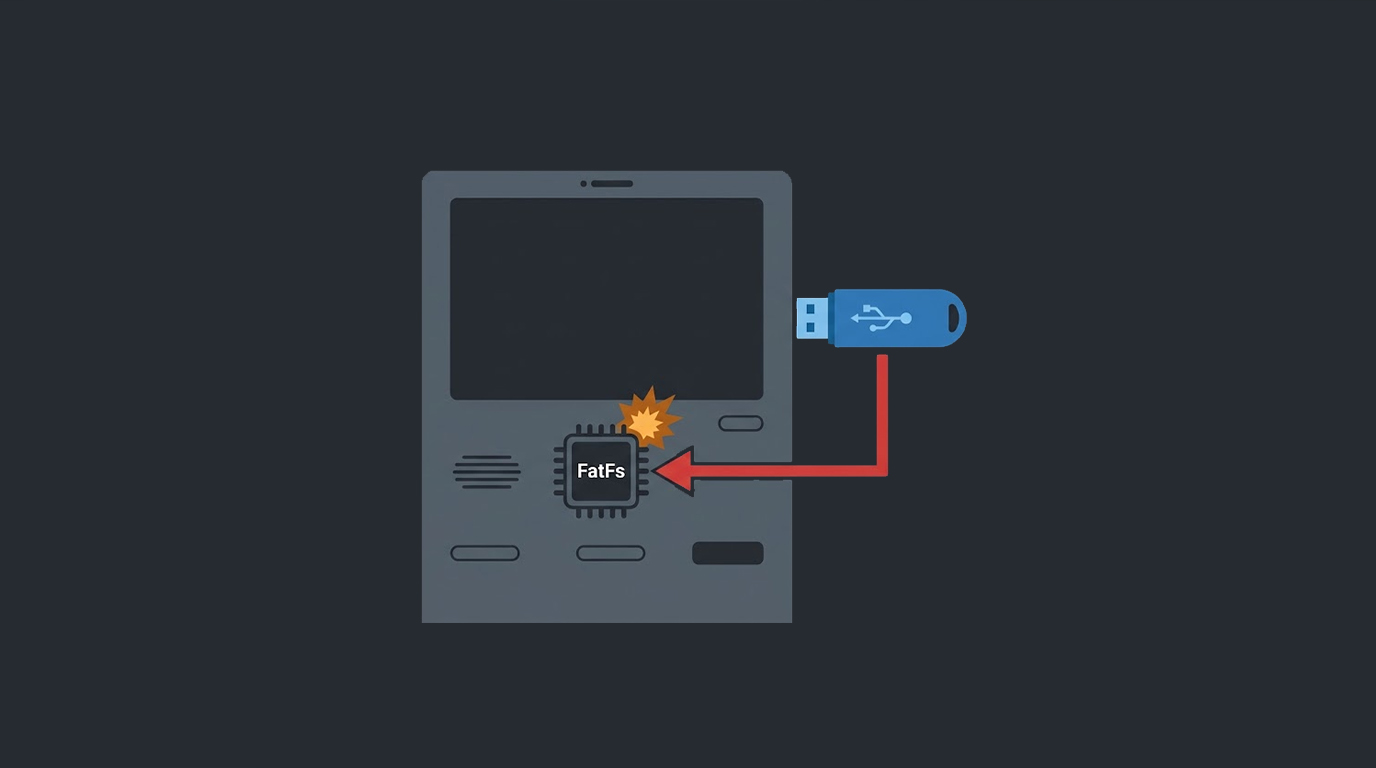
Security firm runZero has uncovered seven vulnerabilities in FatFs, a lightweight filesystem library that handles FAT and exFAT formats for USB drives and...
Found 174 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Security firm runZero has uncovered seven vulnerabilities in FatFs, a lightweight filesystem library that handles FAT and exFAT formats for USB drives and...
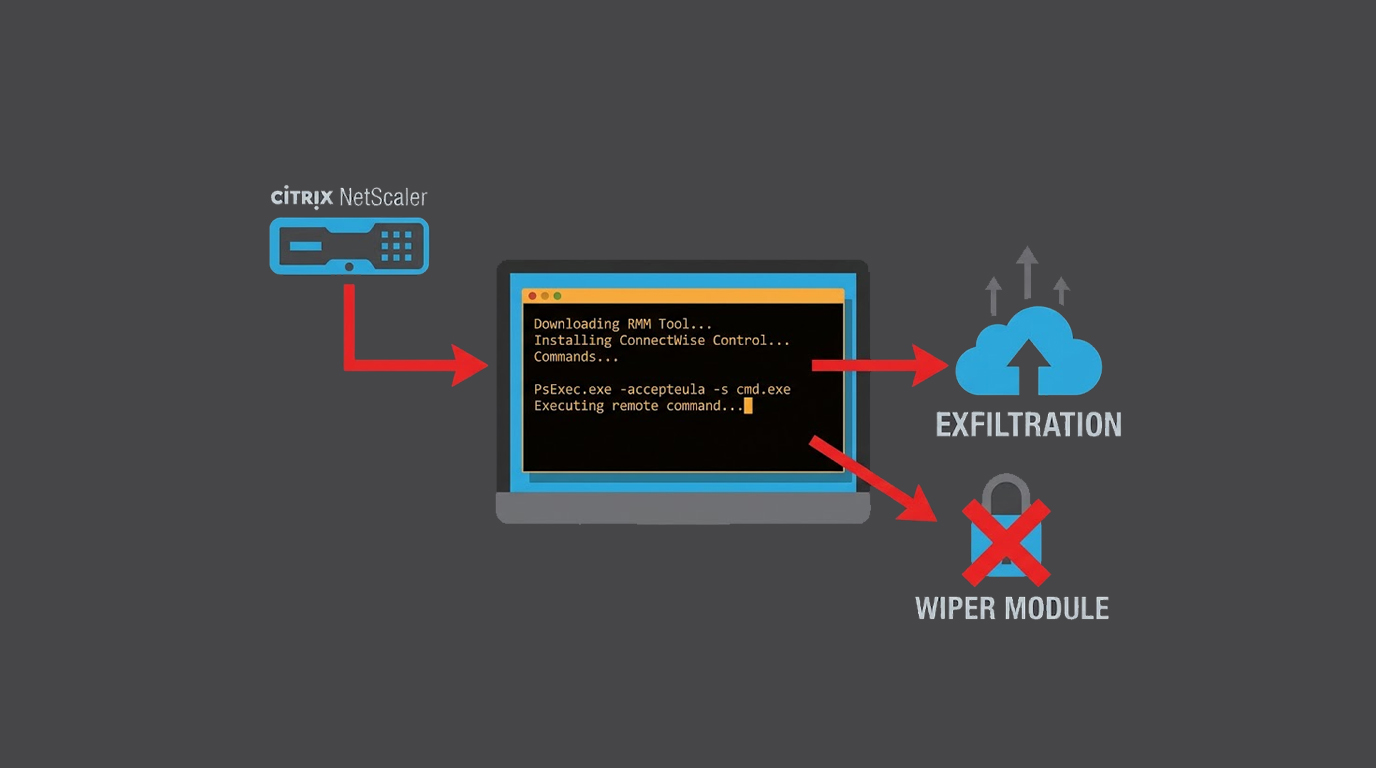
The Anubis Ransomware Campaigns are known to exploit the Citrix Bleed 2 Vulnerability as an initial access vector. The Citrix Bleed 2 Vulnerability i...
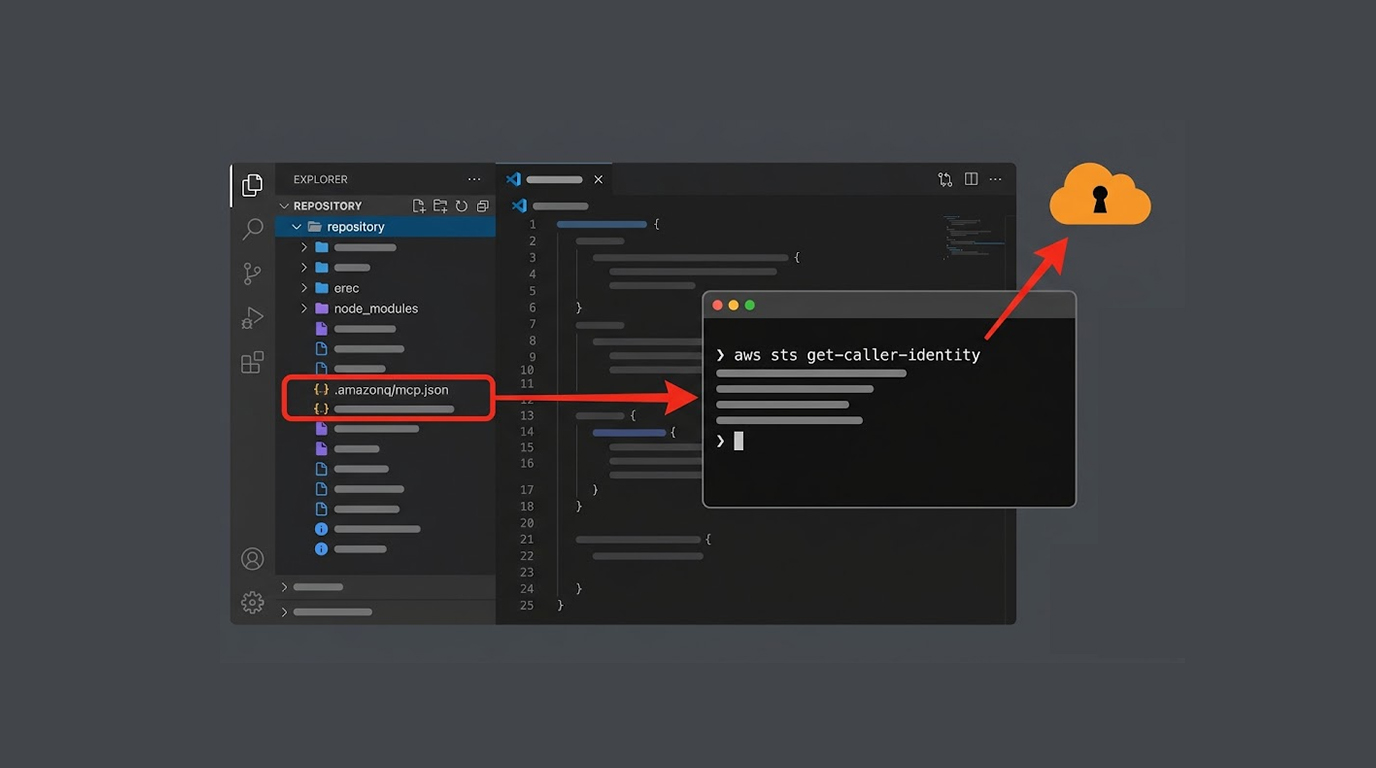
You clone a repository. You trust the workspace. Your AI coding assistant does the rest. That's the path Wiz Research demonstrated with Amazon Q Developer...
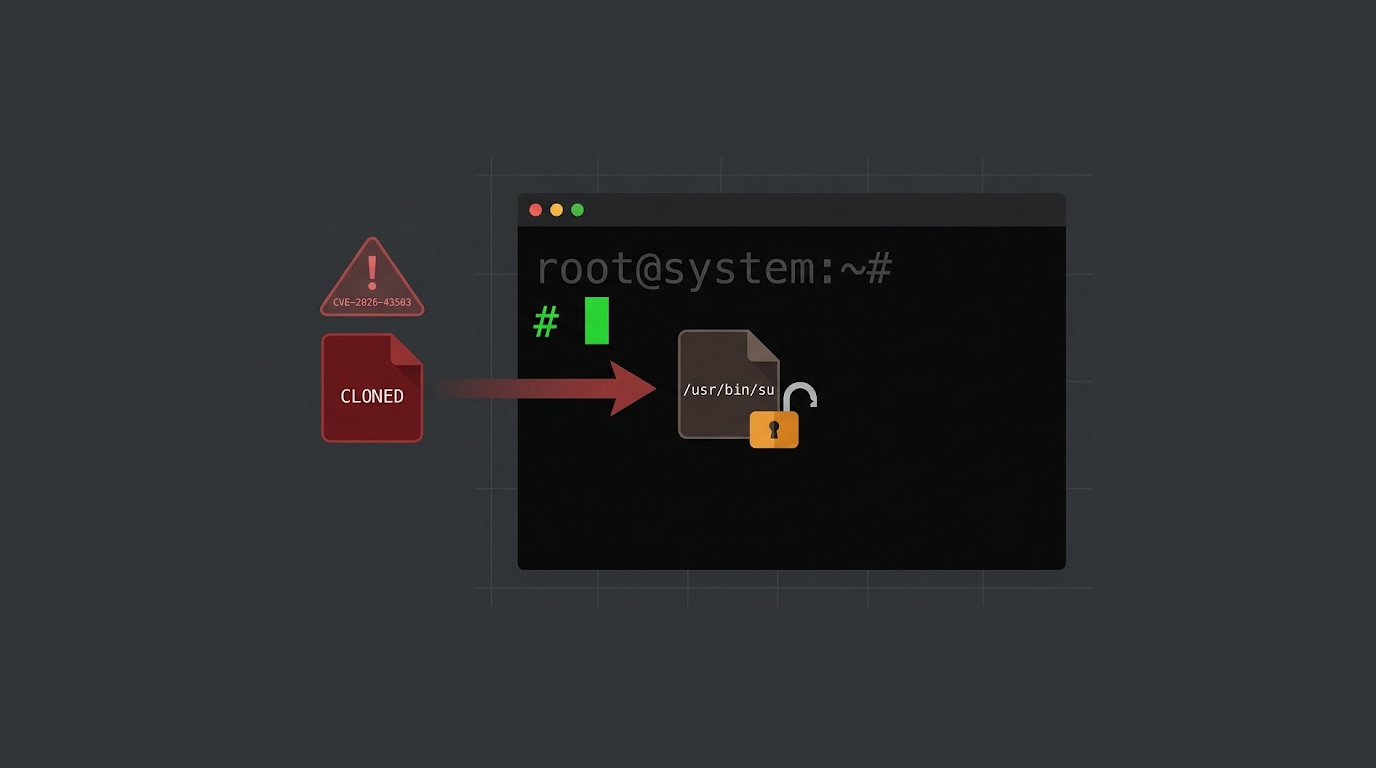
A new Linux kernel privilege escalation vulnerability has been published. It's called DirtyClone, and it belongs to the DirtyFrag family of flaws. A workin...
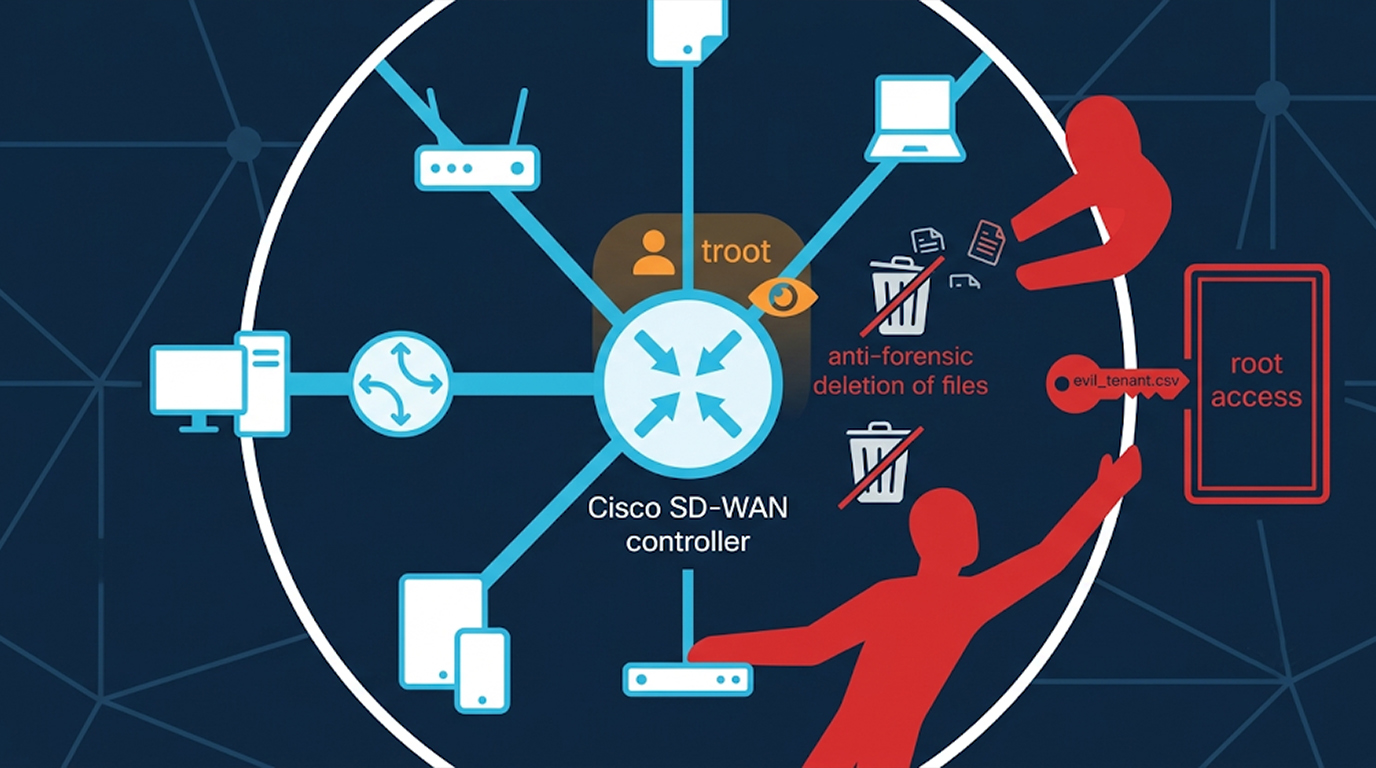
When Cisco disclosed CVE-2026-20245 earlier this month, the company acknowledged that it was already aware of exploitation. Now Mandiant has revealed the f...
Is your business truly safe from a cyberattack? Many managers and entrepreneurs are somewhat ignorant toward digital resources, so many of them feel that...
Immediate action is necessary if you use the Gravity SMTP plugin for sending emails through WordPress, as there is currently a vulnerability being exploite...
Beats Studio Buds. A critical flaw-causing vulnerability was found in Apple’s wireless earbuds and the company has issued firmware patches to address...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067