Malicious npm Packages Spread Worm-Like Stealer & RATs
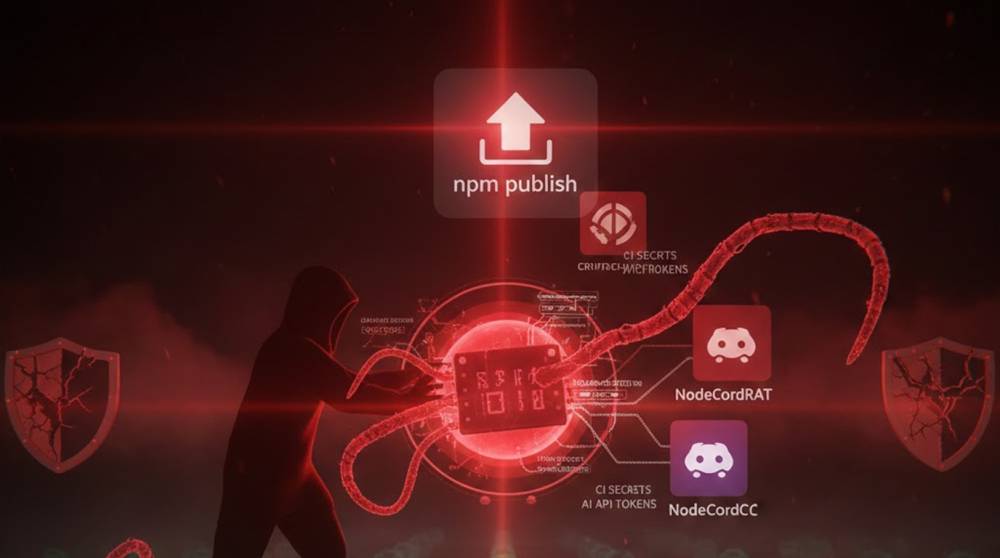
Cybersecurity firm Socket has uncovered an active supply-chain worm campaign codenamed SANDWORM_MODE that abuses at least 19 malicious npm packages to harv...
Found 104 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Cybersecurity firm Socket has uncovered an active supply-chain worm campaign codenamed SANDWORM_MODE that abuses at least 19 malicious npm packages to harv...
There is an urgent update from Google for their browser due to a zero-day vulnerability that is currently being used by attackers in the wild. CVE-2026-24...
Apple has released emergency security updates across its entire operating system lineup to patch a actively exploited zero-day vulnerability in the dyld (d...
Versions of Docker Desktop before 4.44.3 (released on 20 August 2025) had a serious vulnerability that could enable an attacker to use Linux containers to...
The Microsoft Defender team has issued an explicit alert that, for many years, malware has been a threat to Windows computer users; however, starting in la...
Olevba is a powerful, free tool specifically designed to analyze Microsoft Office documents (Word, Excel, PowerPoint) for malicious VBA macros and other em...
ExifTool is a free, open-source command-line tool written by Phil Harvey that reads, writes, and edits metadata in hundreds of file types, especially image...
In cyber security, string analysis refers to the process of retrieving human-readable text from a binary file, sample of malware or from network traffic an...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067