Joomla SP LMS PHP Object Injection Leads to RCE
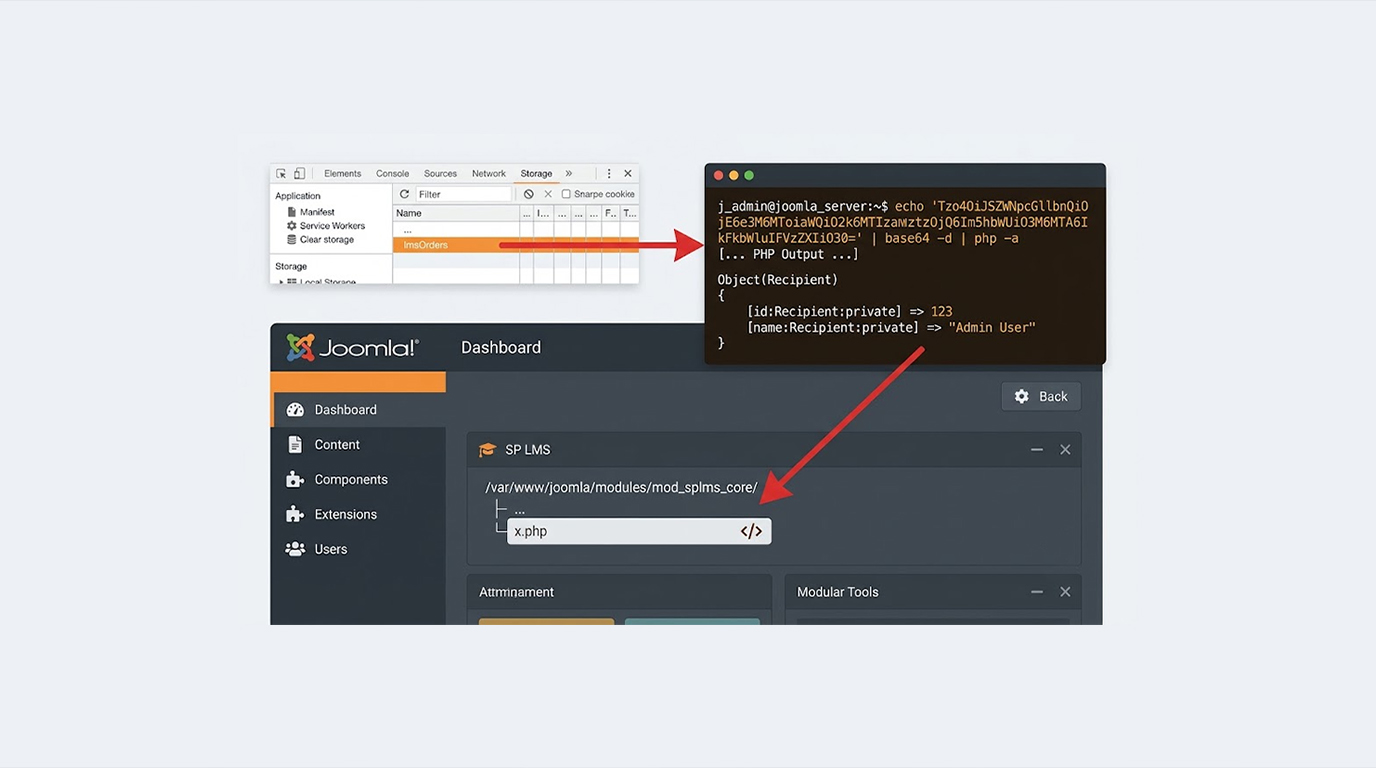
Joomla extension JoomShaper SP LMS contains an object injection vulnerability leading to remote code execution for the attacker. This vulnerability is iden...
Found 167 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Joomla extension JoomShaper SP LMS contains an object injection vulnerability leading to remote code execution for the attacker. This vulnerability is iden...
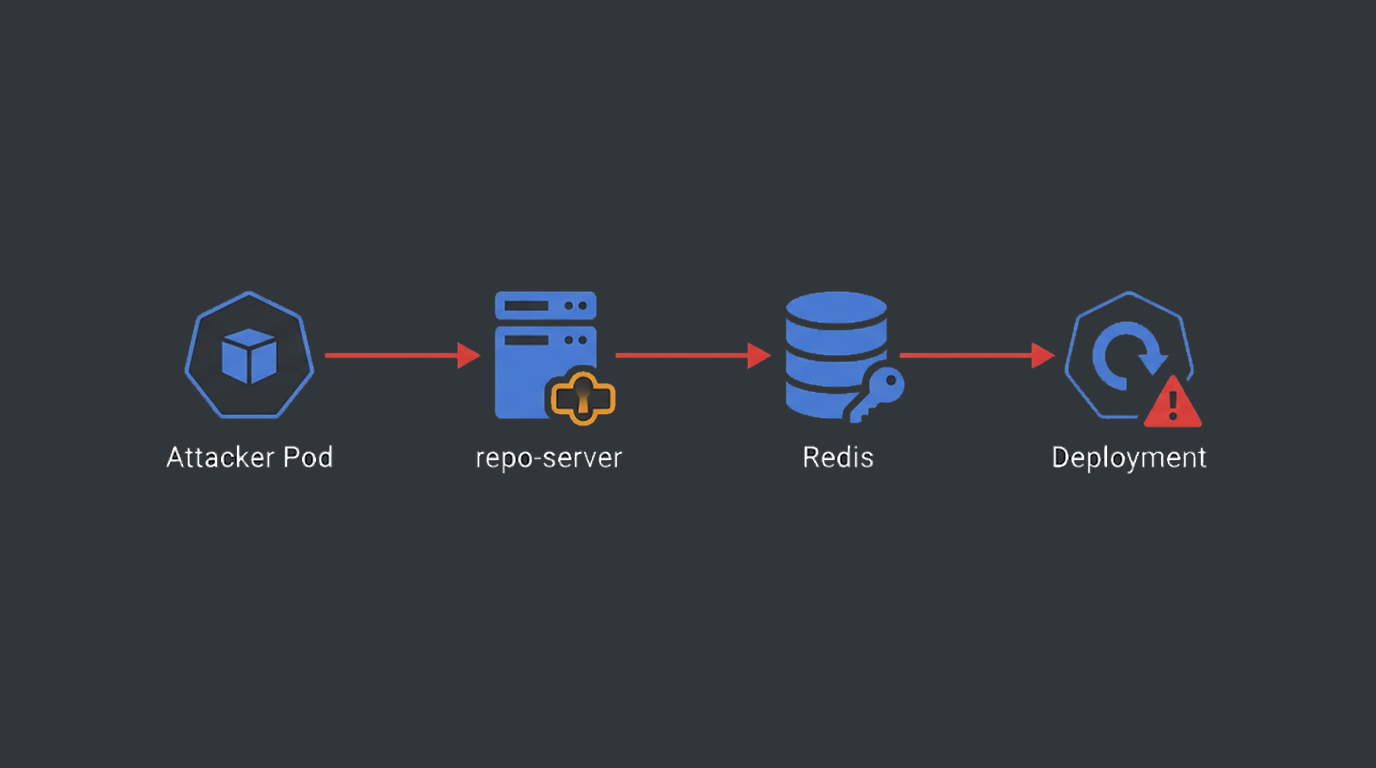
Argo CD is the backbone of GitOps for countless Kubernetes deployments. It reads Git repositories, builds manifests, and keeps clusters in sync. It also ha...
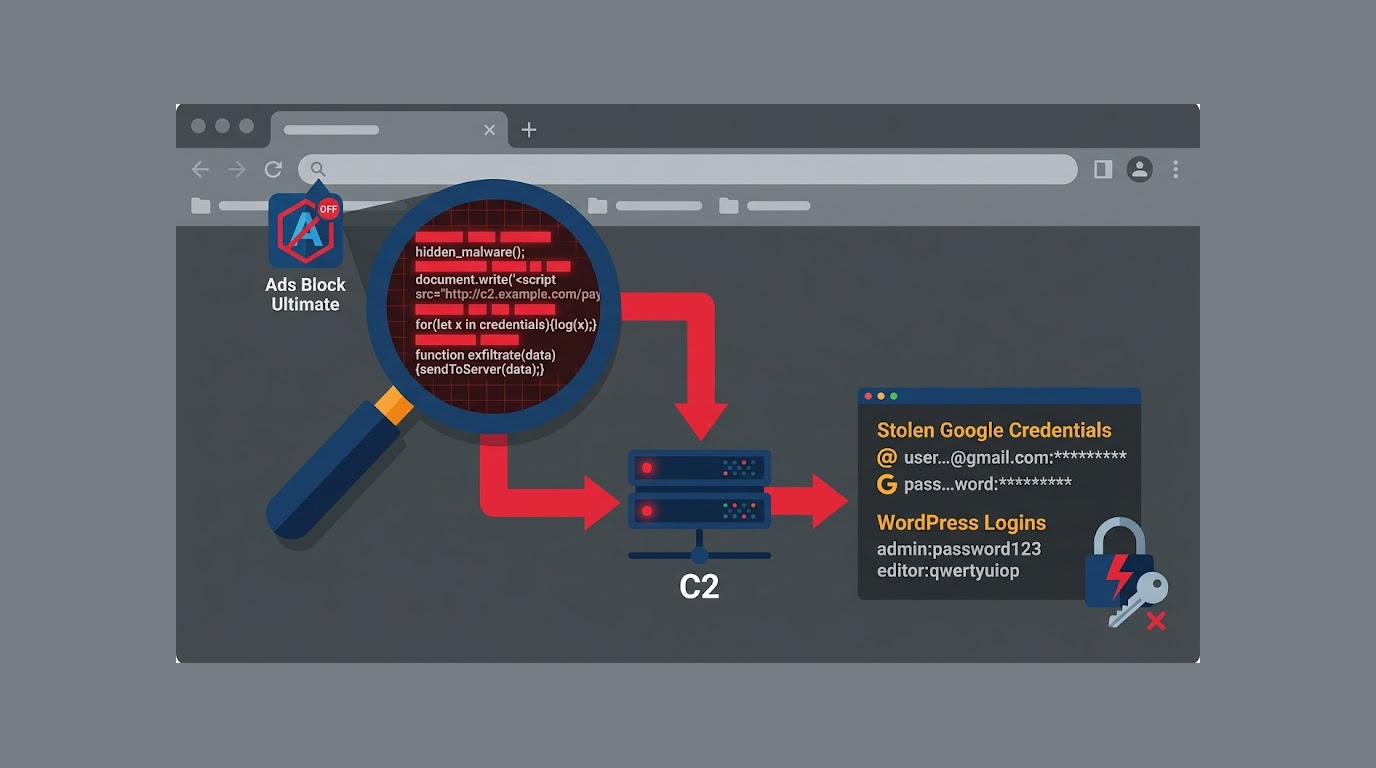
You install an ad blocker. It blocks ads. It has good reviews. You forget about it. For years, it sat quietly in your browser. Then one day, it woke up. I...
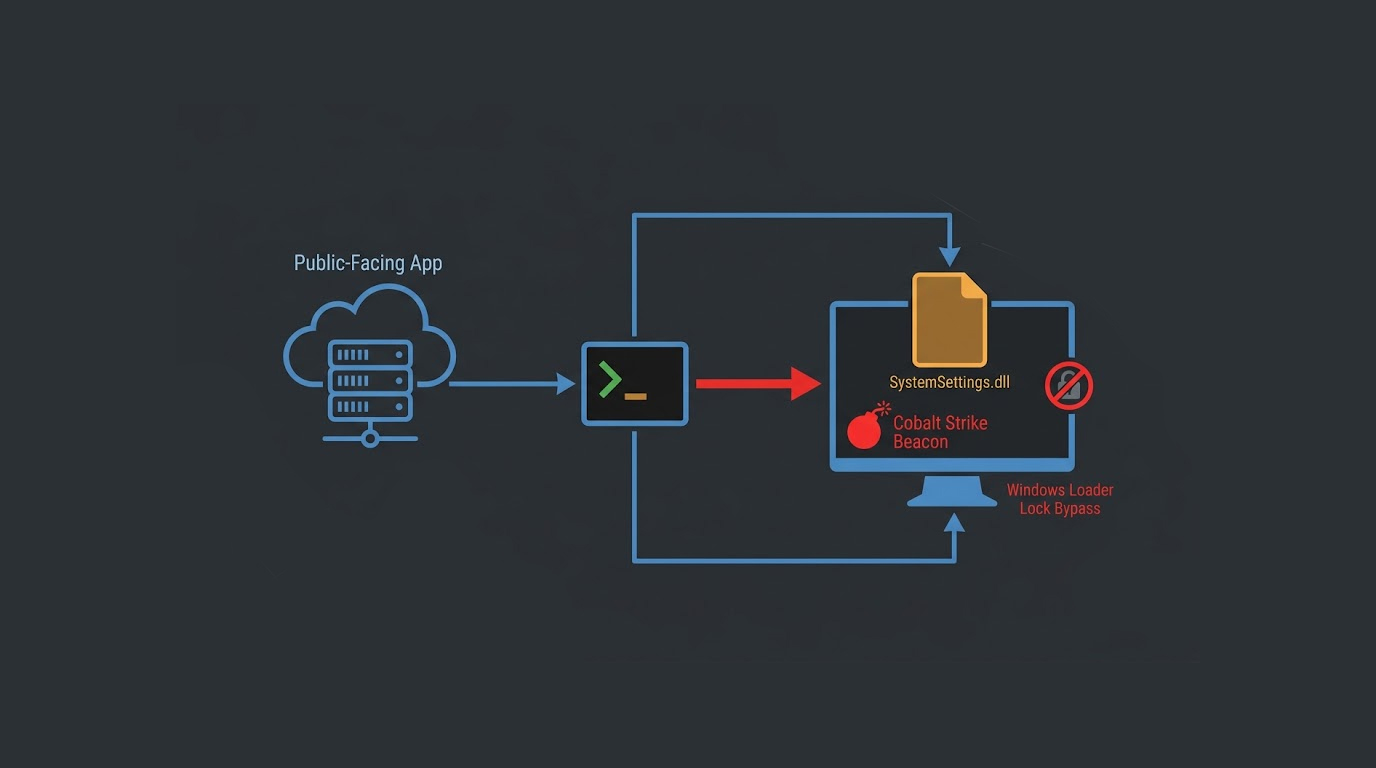
This new wave of attacks includes an unknown variant of malware known as SharkLoader. SharkLoader functions as a loader for distributing Cobalt Strike Beac...
This is a nightmare scenario for any business owner. One minute everything is fine, and the next, your website is either redirecting to spam pages or displ...
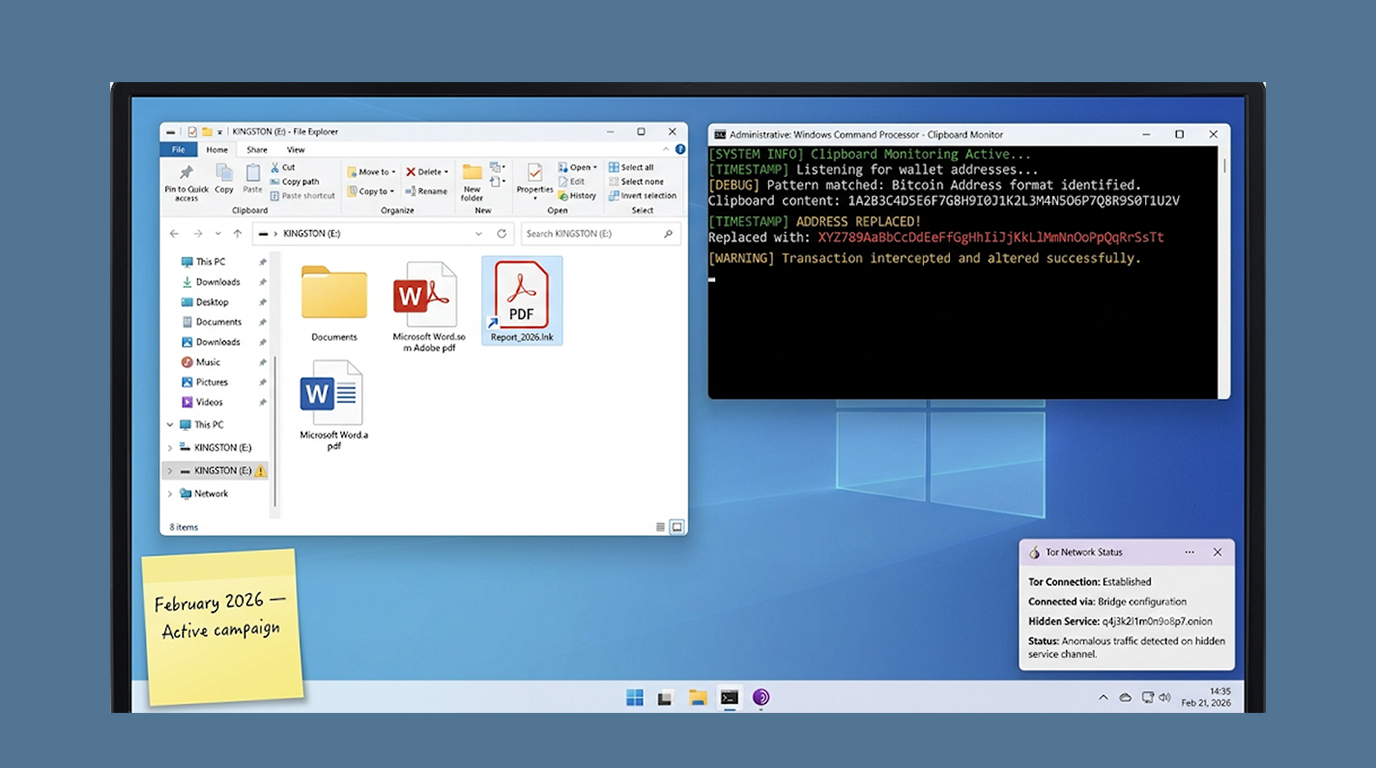
In a new report from Microsoft, window-based cryptocurrency clipper campaign, running since February 2026, has been disclosed. The malware intercepts clipb...
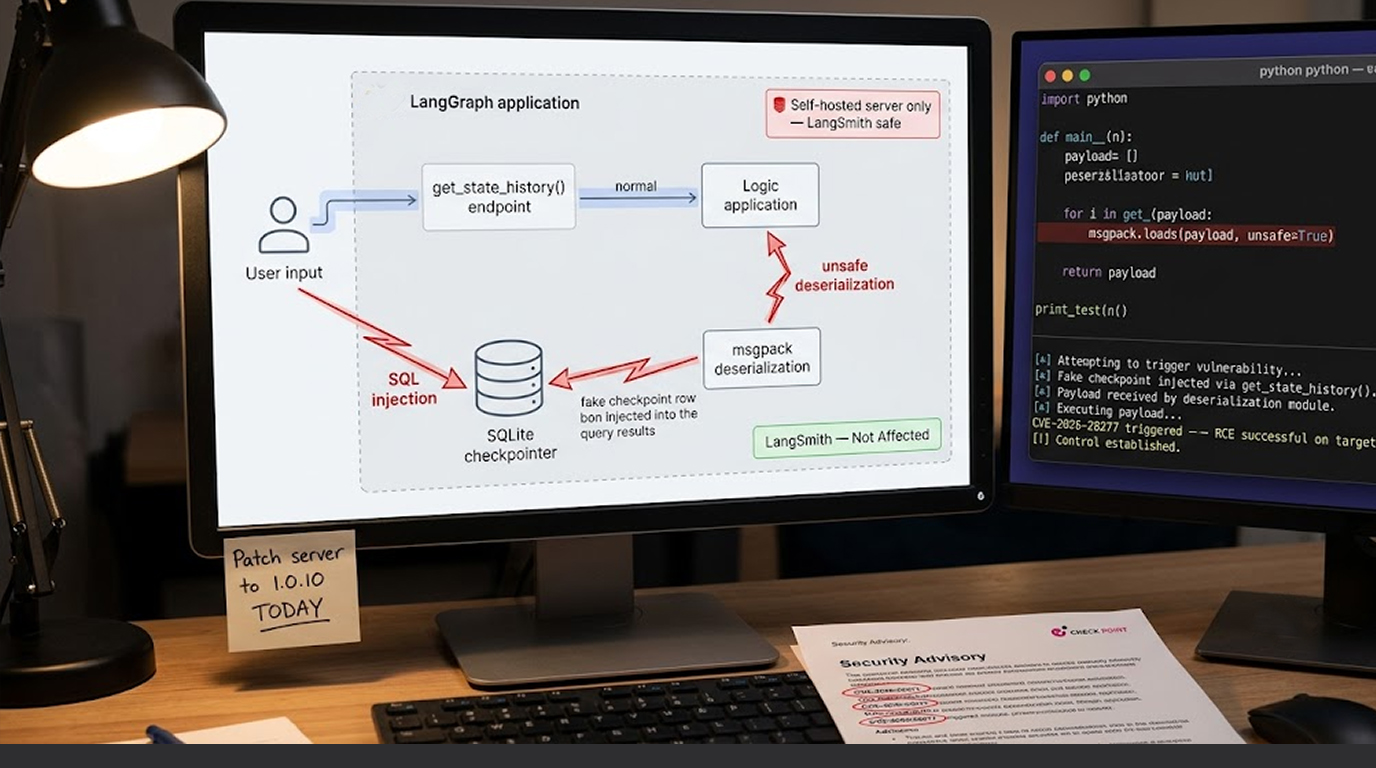
LangGraph is helping you build complex, stateful, multi-agent AI applications. It's open-source, built by LangChain, and widely used by developers who want...
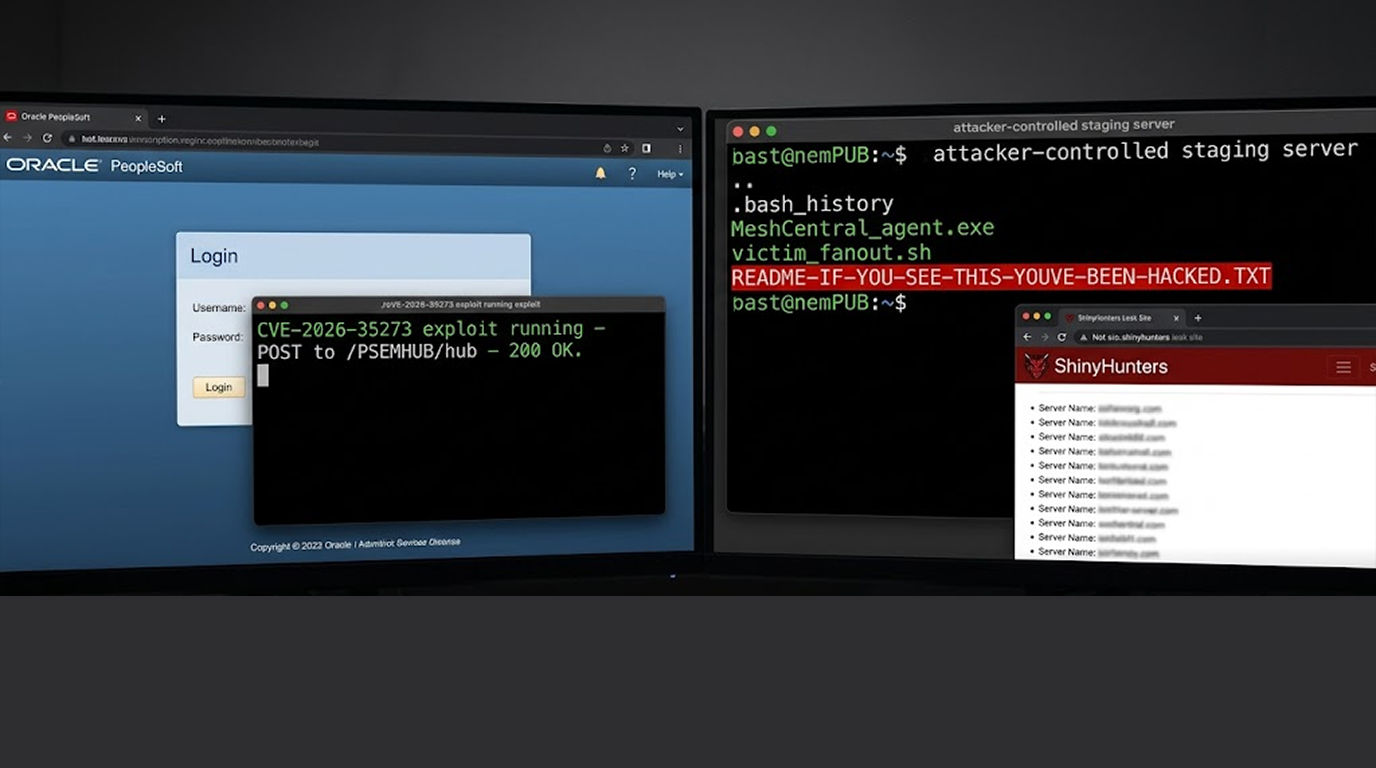
The ShinyHunters extortion crew pulled off something unusual. They exploited an unpatched vulnerability in Oracle PeopleSoft to break into enterprise syste...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067