VMware vCenter CVE-2026-59310 Tied to China-Nexus APT
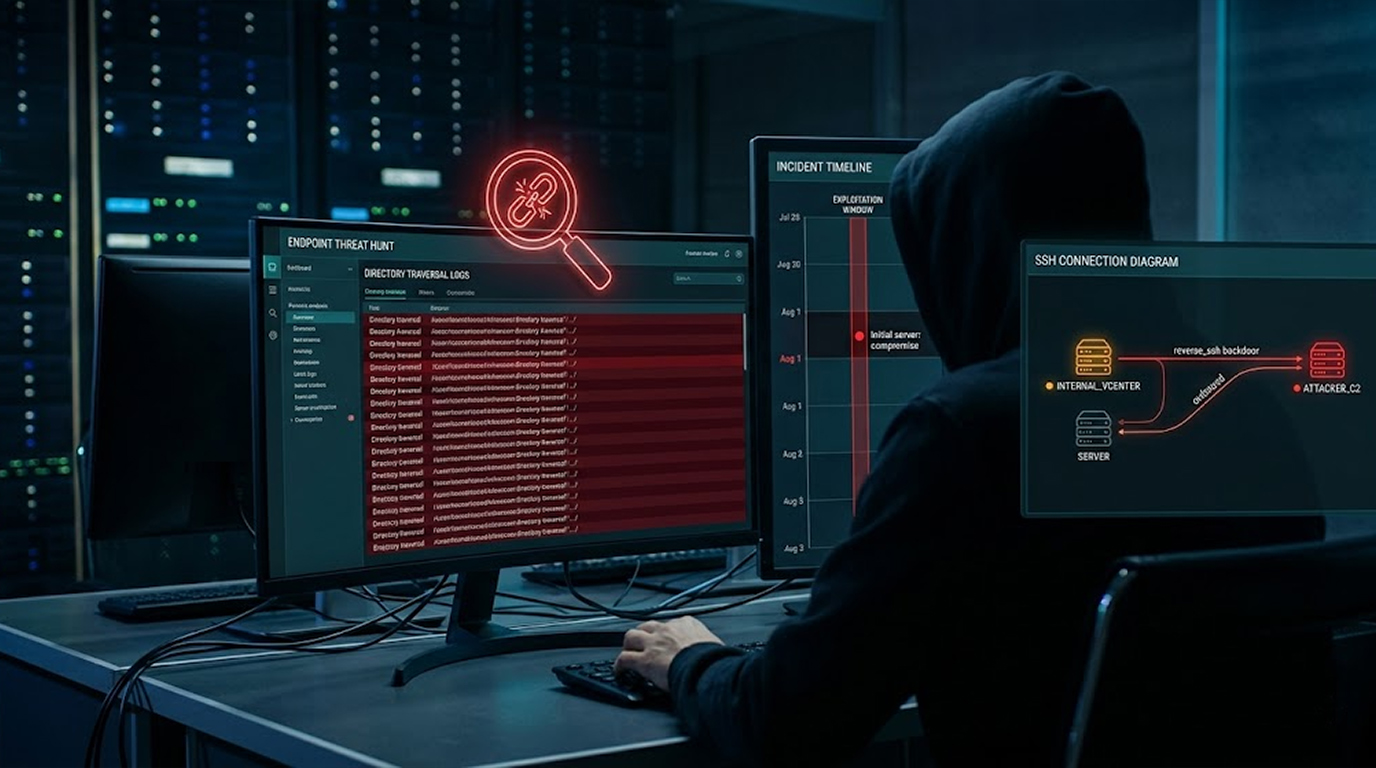
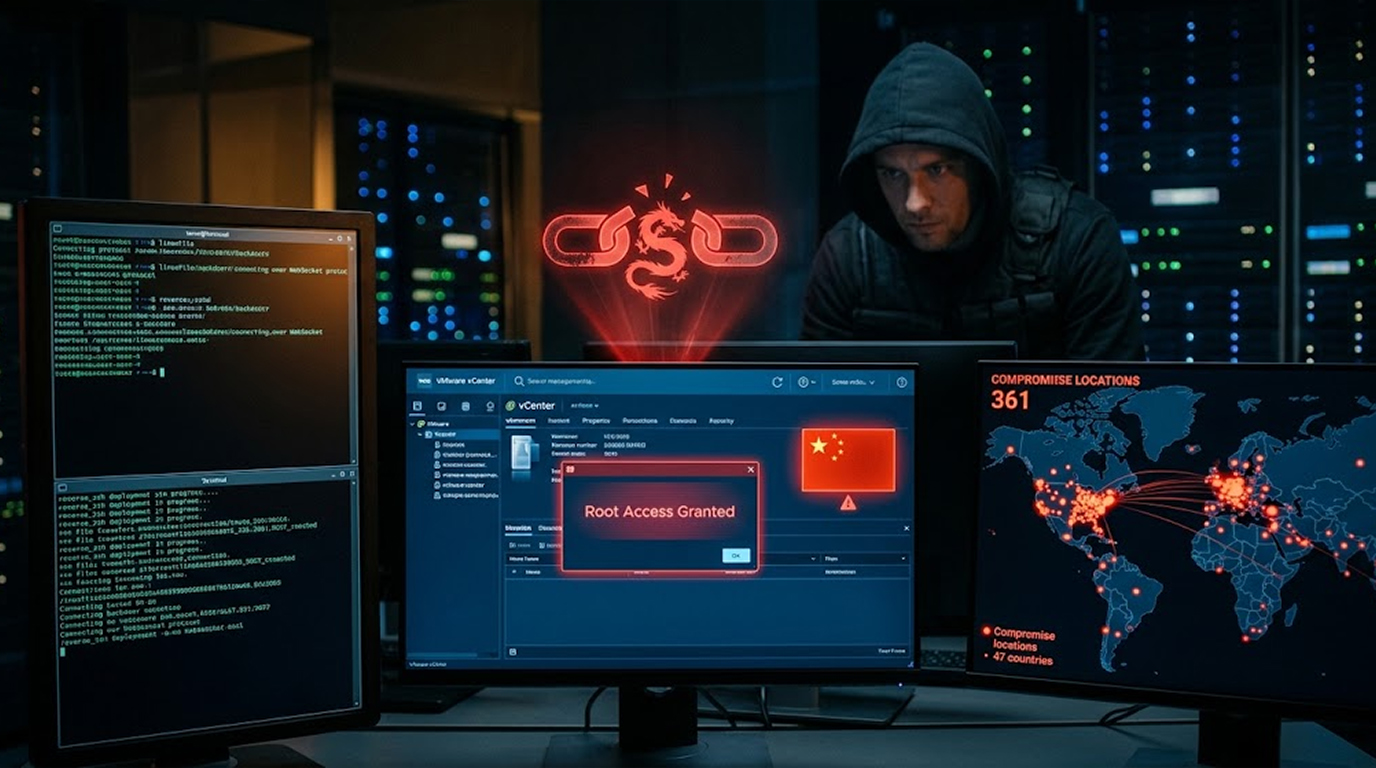
Cybersecurity researchers have linked the exploitation of a recently patched VMware vCenter vulnerability to a suspected Chinese state-sponsored hacking gr...
Found 287 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Cybersecurity researchers have linked the exploitation of a recently patched VMware vCenter vulnerability to a suspected Chinese state-sponsored hacking gr...
You are a security engineer working for a company which has just released an AI-based assistant which takes care of all the customer needs. This AI assista...
The threat actor from North Korea, Lazarus Group, is responsible for the use of the zero day vulnerability in Microsoft Windows that is recently patched. T...
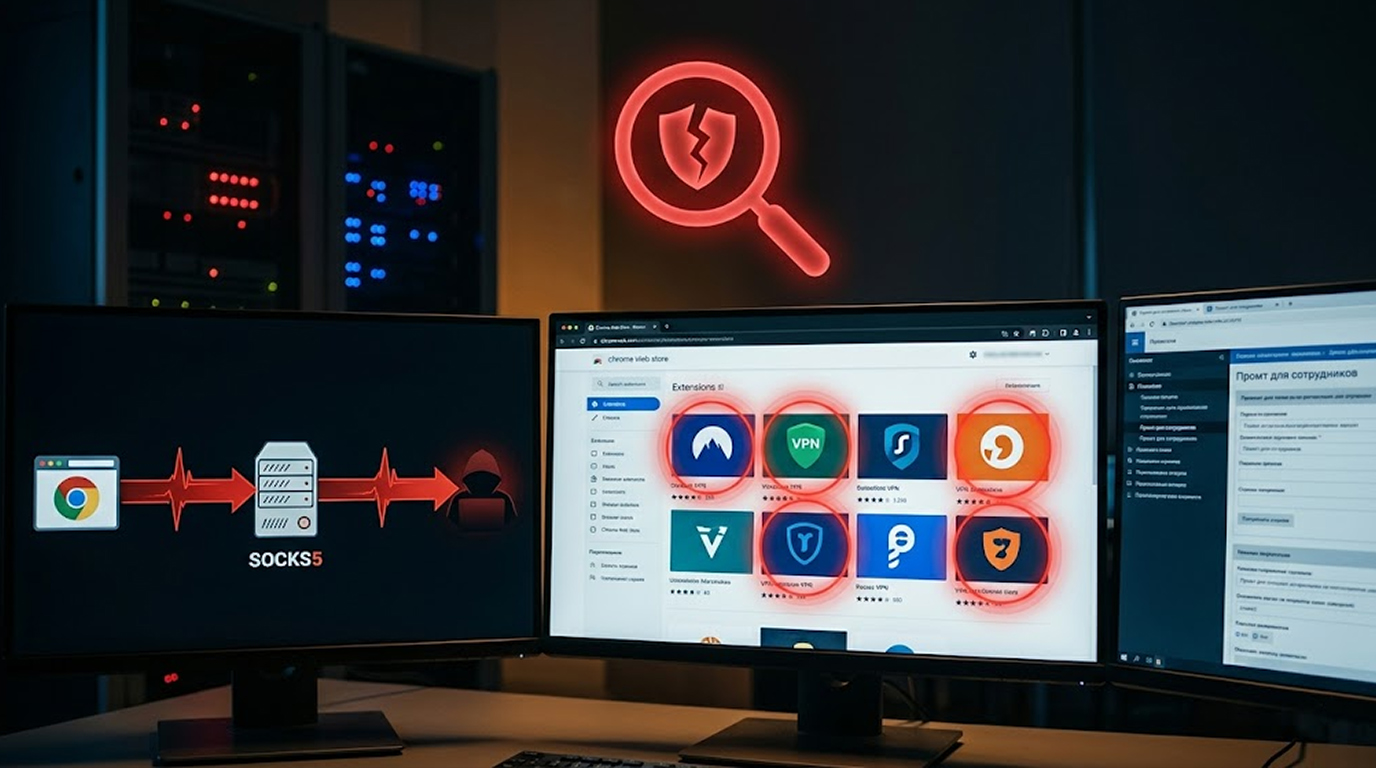
A massive set of 737 free VPN and proxy extensions have been discovered in the Chrome Web Store. Extensions mostly target the Russian speaking users seekin...
Threat actors have started to target a critical security vulnerability that has been recently patched by Broadcom VMware vCenter. The vulnerability gives a...
Windows Plug and Play may be leveraged to fetch signed vendor software for an emulated USB device and run the installation component at elevated privileges...
OpenAI has stated that it will suspend certain internal activities involving its upcoming AI model called Astra. This is due to the internal evaluation sho...
What differentiates running tests once versus having continuous mitigation is the difference between a stop-gap solution versus a long-term one. Running te...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067