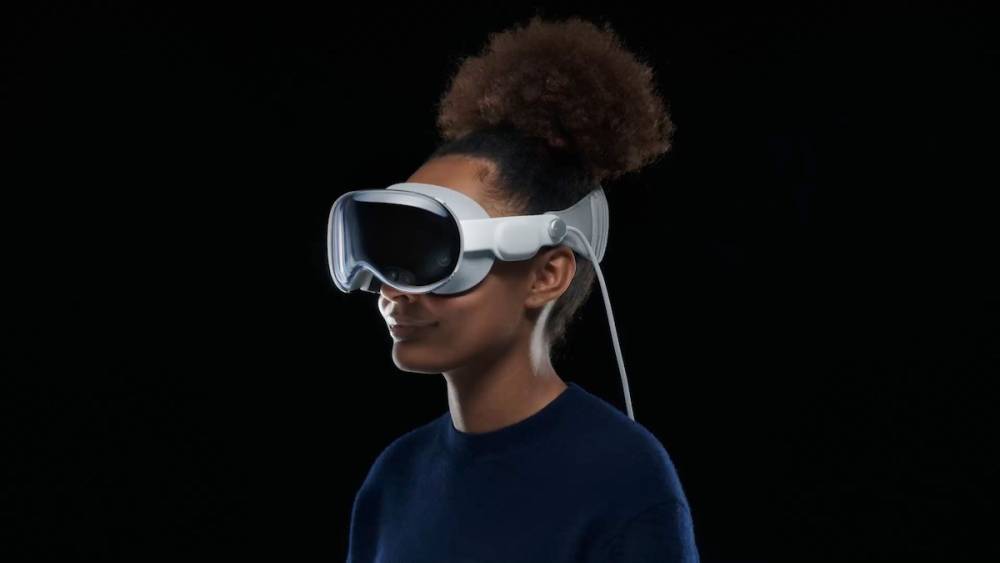
GAZEploit Attack: CVE-2024-40865 Exploits Gaze to Infer Typing in Vision Pro
Details have emerged about a now-patched security flaw in Apple's Vision Pro mixed reality headset that could have allowed attackers to infer what users we...
Found 620 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Details have emerged about a now-patched security flaw in Apple's Vision Pro mixed reality headset that could have allowed attackers to infer what users we...
Ivanti has disclosed that a newly patched security flaw in its Cloud Service Appliance (CSA) is actively being exploited in the wild. The vulnerability, tr...
Malicious actors have been quick to exploit publicly available proof-of-concept (PoC) exploits for newly disclosed vulnerabilities in Progress Software's W...
GitLab has rolled out security updates to fix 17 vulnerabilities, including a critical flaw (CVE-2024-6678) with a CVSS score of 9.9, which allows attacker...
Internet-exposed Selenium Grid servers are being targeted by cybercriminals for illicit cryptocurrency mining and proxyjacking operations, according to a n...
On Tuesday, Microsoft disclosed the active exploitation of three new security vulnerabilities as part of its Patch Tuesday update for September 2024. The m...
Ivanti has released software updates to address multiple vulnerabilities impacting Endpoint Manager (EPM), including 10 critical flaws that could lead to r...
SonicWall has disclosed that a recently patched critical security flaw in SonicOS (CVE-2024-40766, CVSS score: 9.3) may have been actively exploited. The f...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067