npm Supply Chain Attack Campaign Hits 800 Packages
A cluster of nearly 800 malicious packages has been published to the npm registry as part of a new campaign designed to deliver cross-platform malware targ...
Found 246 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A cluster of nearly 800 malicious packages has been published to the npm registry as part of a new campaign designed to deliver cross-platform malware targ...
Entra ID researcher Dirk-jan Mollema has uncovered a technique that allows malware already running on a compromised Windows machine to silently use a victi...
Picture this. You check into a hotel, connect to the Wi-Fi, and see a browser update prompt. It looks legitimate. You click it, install the update, and go...
North Korean threat actors are back at it. This time, however, they are using an advanced macOS malvertising attack where they trick their victims into cli...
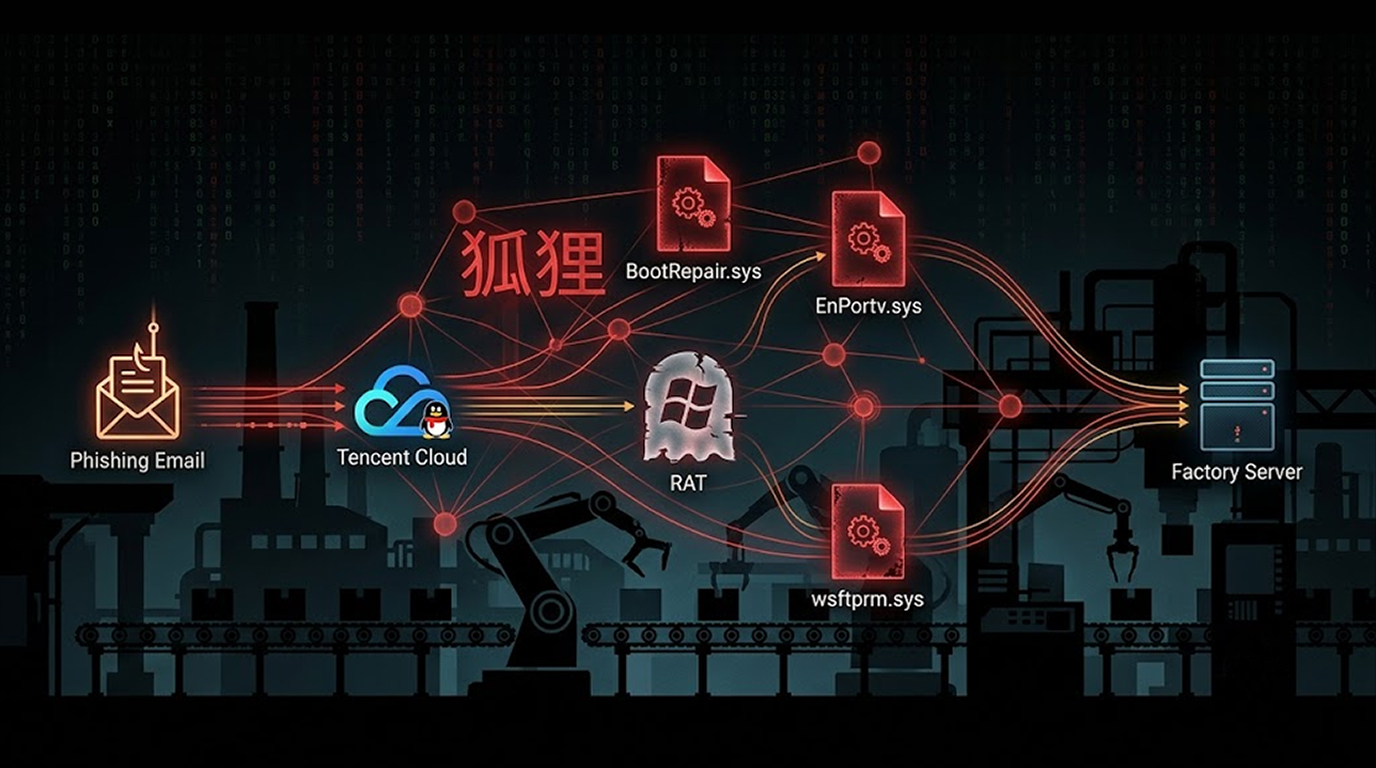
A Chinese cybercrime group known as Silver Fox is back with new tricks. The threat actors have been observed using previously unreported drivers as part of...
What if, for example, one of your staff members clicks on an apparently safe link, only to have an autonomous AI agent start operating within your company...
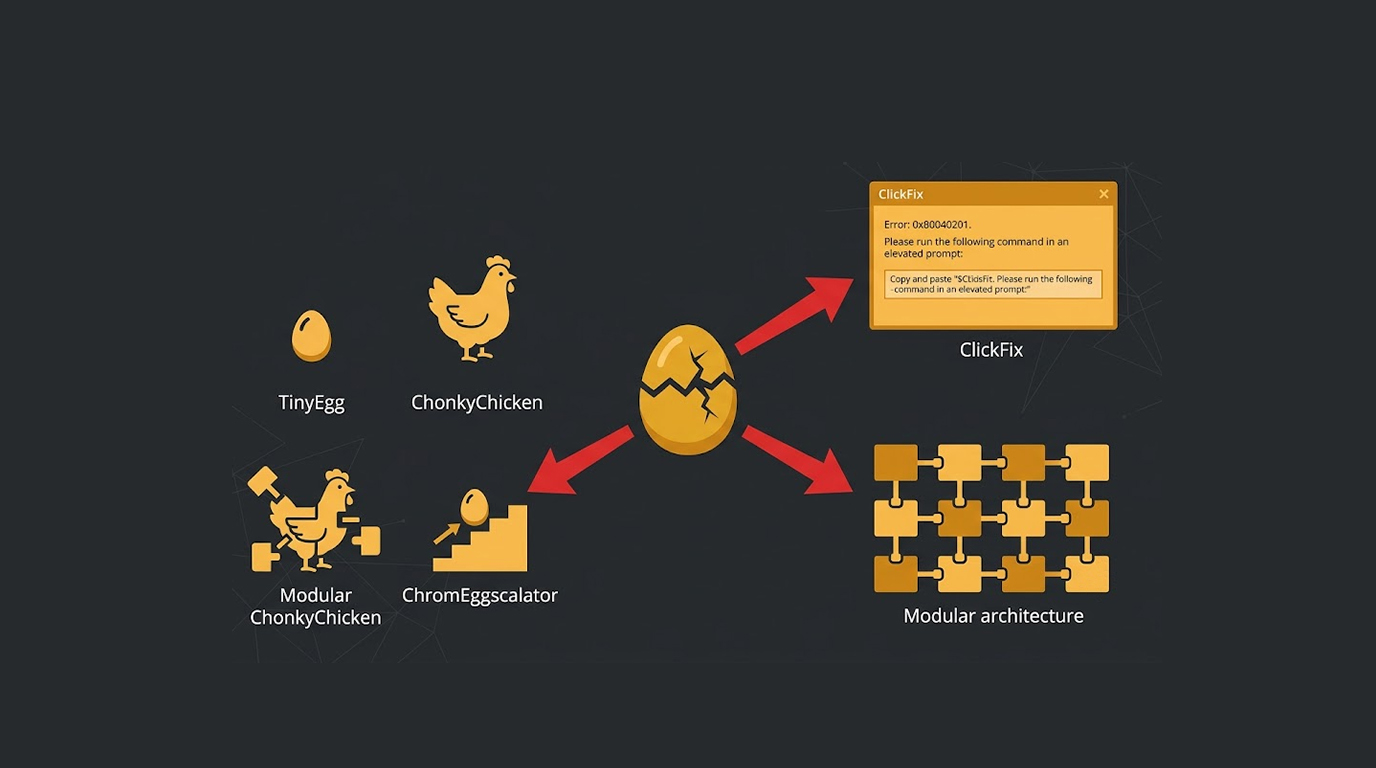
You would think that getting caught in the spotlight would make a cybercriminal group pack up and disappear. But with the Golden Chickens malware-as-a-serv...
You are browsing a news site. A page loads. You see the article. Everything looks normal. But behind the scenes, something else is happening. A WebAssembly...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067