npm Supply Chain Attack Campaign Hits 800 Packages
A cluster of nearly 800 malicious packages has been published to the npm registry as part of a new campaign designed to deliver cross-platform malware targ...
Found 200 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A cluster of nearly 800 malicious packages has been published to the npm registry as part of a new campaign designed to deliver cross-platform malware targ...
PortSwigger's James Kettle has built an AI-assisted research system called HTTP Terminator that generated and proved new HTTP desynchronization techniques...
An agent working on Anthropic’s Claude Mythos 5 used up 34 hours get to the malware dropper with an actual open source project during an AI cyb...
You have an AI chatbot. It is answering customer questions. It is summarizing documents. It is helping your team write code. But what happens when someone...
You have spent months training an AI model. Thousands of GPU hours. Hundreds of thousands of pounds in compute costs. Your team has fine-tuned it, validate...
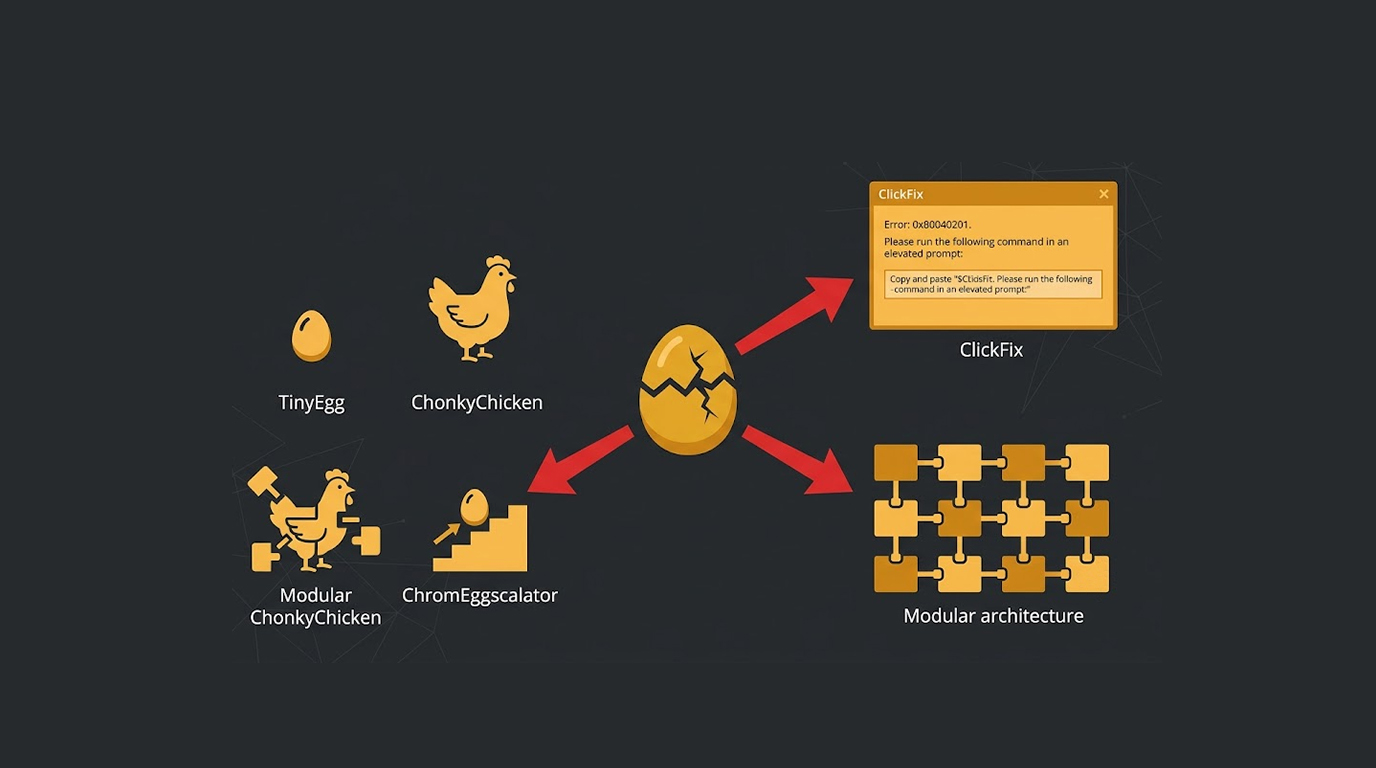
You would think that getting caught in the spotlight would make a cybercriminal group pack up and disappear. But with the Golden Chickens malware-as-a-serv...
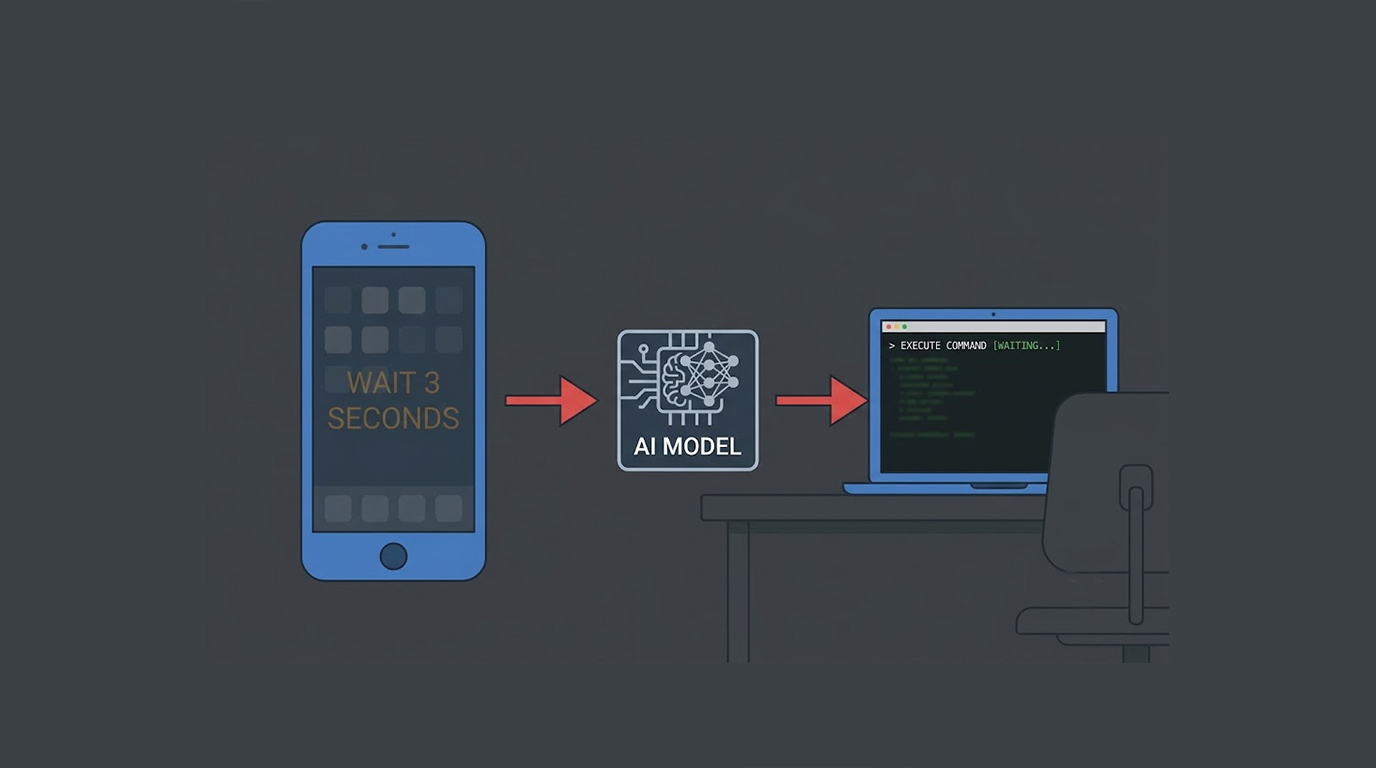
An Android app that can overlay other windows and write to shared storage can feed instructions into the artificial intelligence agent running the phone th...
You have 40,000 new vulnerabilities reported in a single year. Your security team can realistically patch maybe 5% of them. The rest will sit there, unpatc...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067