Veeam Urges Updates to Fix Critical Vulnerabilities in Service Provider Console
Veeam has released patches to address two critical vulnerabilities in its Service Provider Console (VSPC) that could leave systems open to serious threats,...
Found 57 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Veeam has released patches to address two critical vulnerabilities in its Service Provider Console (VSPC) that could leave systems open to serious threats,...
Data privacy and protection in robotic systems is emerging as a critical concern as the integration of robotics into various industries continues to grow....
In the vast realm of cybersecurity, hackers play diverse roles, each with distinct motivations, methods, and impacts. Understanding the different types of...
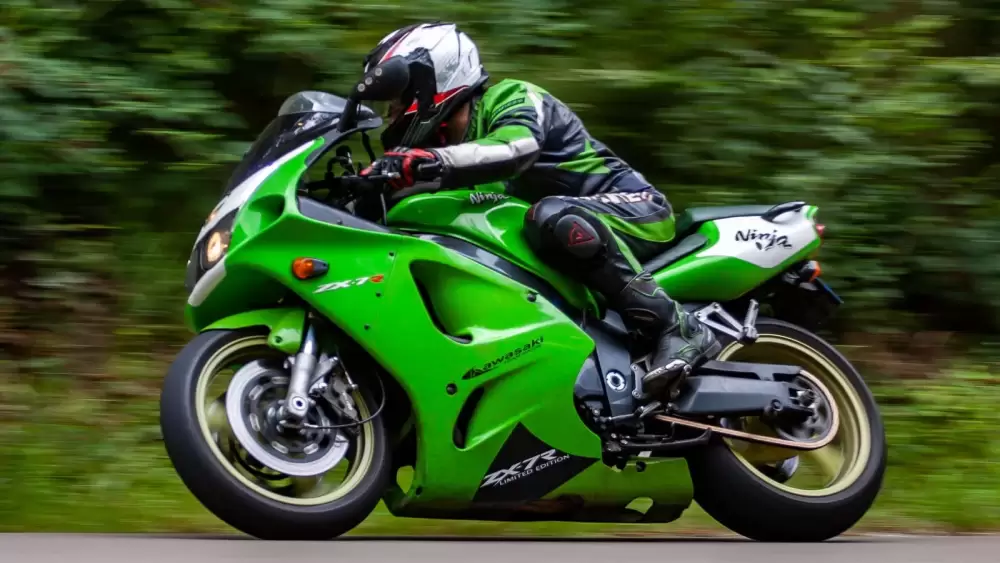
The notorious RansomHub ransomware group has recently leaked 487 gigabytes of data, allegedly stolen from Kawasaki Motors Europe (KME). This cyberattack wa...
Cloud computing has revolutionized the way businesses store and access data, offering flexibility, scalability, and cost savings. However, with these benef...
In today's interconnected world, supply chains are more vulnerable than ever to cyber threats. Businesses often rely on third-party vendors, service provid...
Details have surfaced regarding a previously undisclosed vulnerability in Microsoft 365 Copilot that could have enabled attackers to steal sensitive user d...
In what's a case of an operational security (OPSEC) lapse, the operator behind a new information stealer called Styx Stealer leaked data from their own com...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067