WordPress Supsystic Contact Form SSTI Exploit CVE-2026-4257
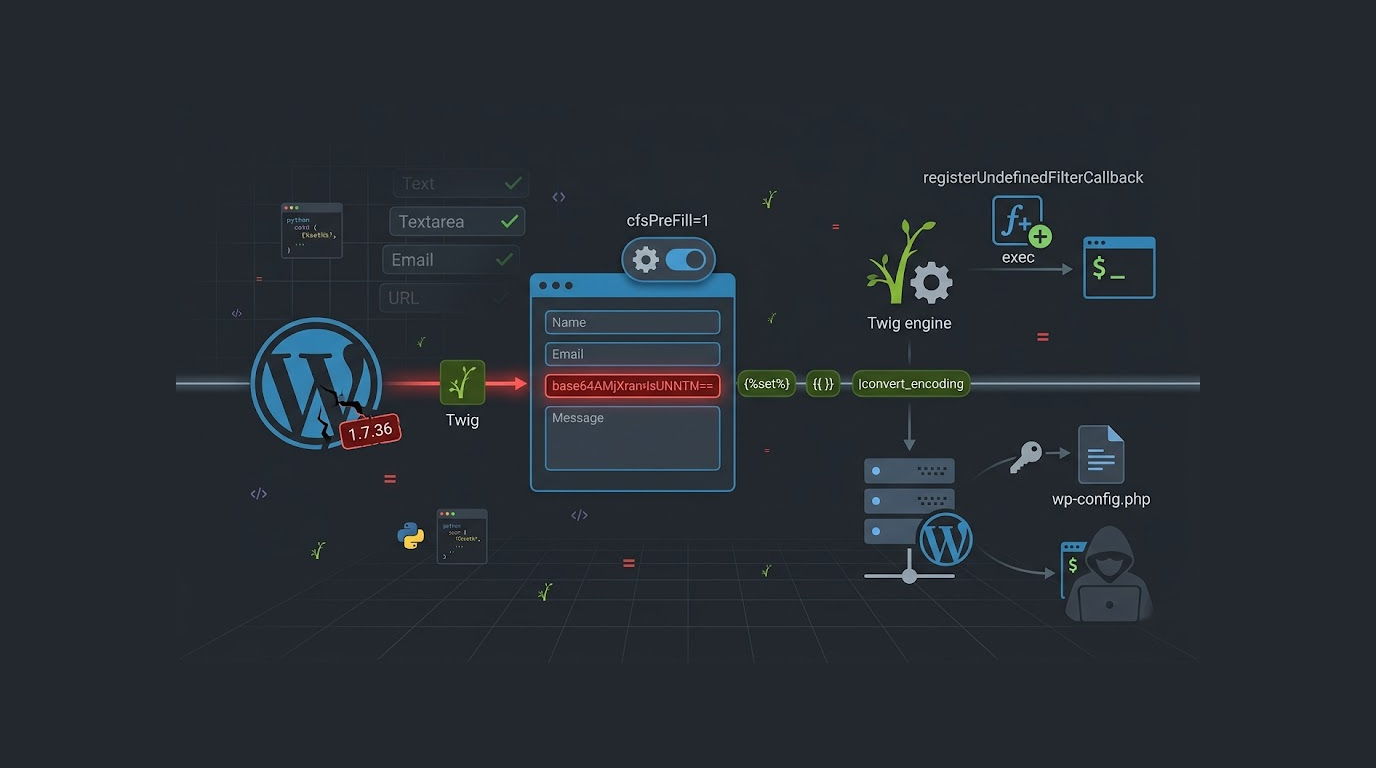
The Supsystic Contact Form plugin for WordPress contains an SSTI vulnerability that allows an attacker to run any command on the server. This vulnerability...
Found 142 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
The Supsystic Contact Form plugin for WordPress contains an SSTI vulnerability that allows an attacker to run any command on the server. This vulnerability...
Your network is set up like this, employees plug into the switch, servers plug into the same switch, everything can talk to everything, it is simple, it is...
You finally did the right thing, you hired a penetration testing firm to find security holes before the criminals do.You expected a few minor issues, maybe...
You spend thousands on marketing, you optimize your product pages, you run Facebook ads, you finally see sales rolling in.Then one morning you wake up to a...
A popular blogging platform has a serious problem, attackers can steal admin passwords and API keys without ever logging in, and the vulnerability has exis...
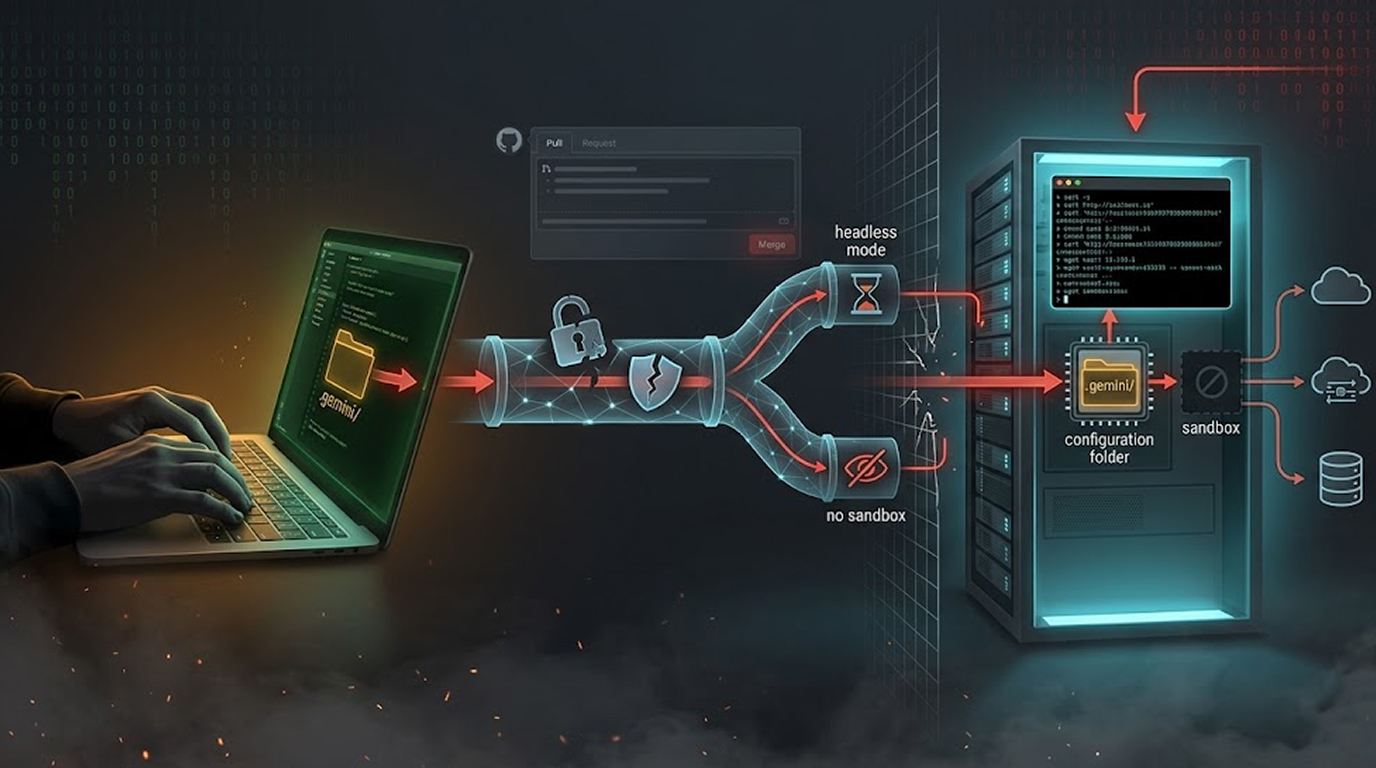
A perfect 10. That is the CVSS score Google assigned to a security flaw in its Gemini CLI tool. And for good reason. The Gemini CLI remote code execution...
A new phrase is spreading through developer communities and startup forums: "vibe coding". It sounds casual, even playful. For those building websites...
Tool calling (also known as function calling or tool use) is one of the most powerful features of modern large language models. It allows autonomous AI age...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067