pedit COW Linux Kernel Flaw Grants Root Access
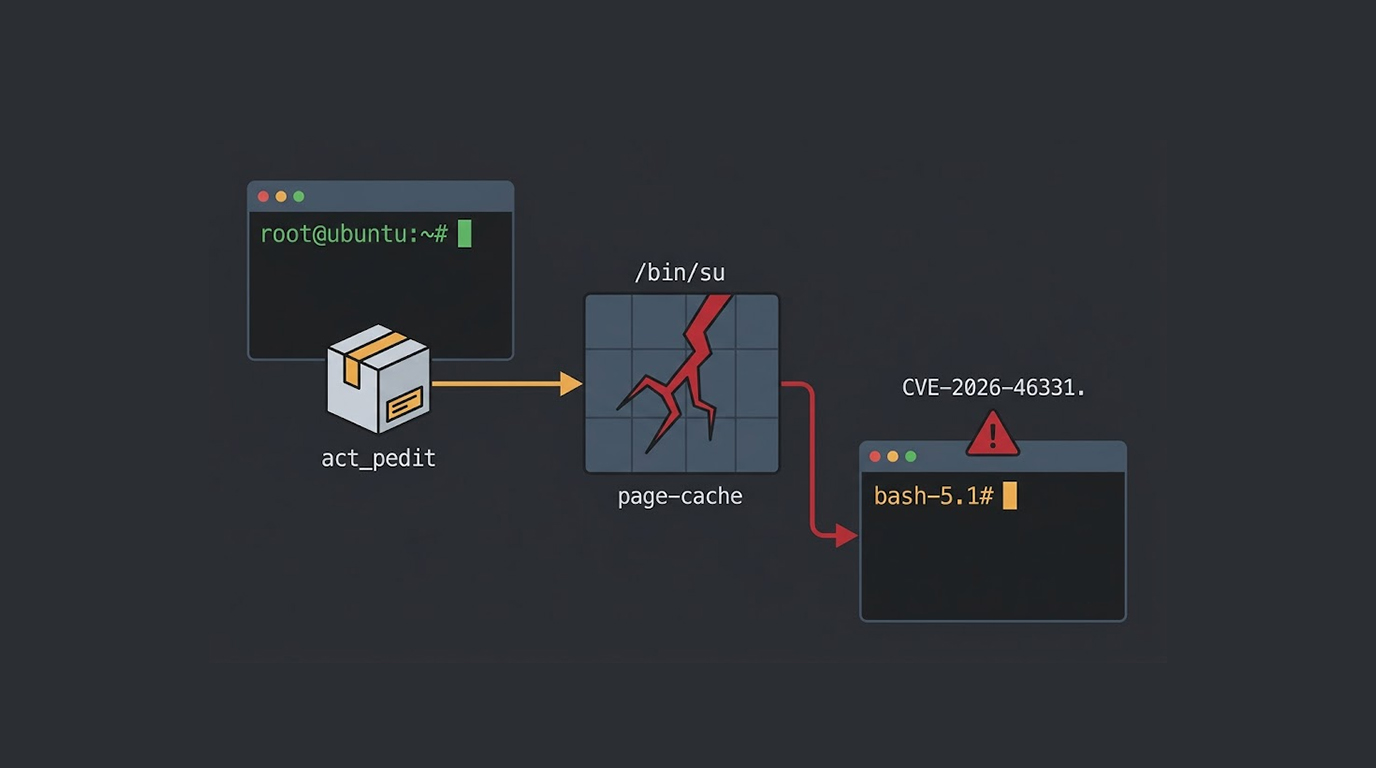
A flaw in the Linux kernel's traffic-control subsystem can let a local unprivileged user gain root on affected systems. The vulnerability, nicknamed pedit...
Found 141 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A flaw in the Linux kernel's traffic-control subsystem can let a local unprivileged user gain root on affected systems. The vulnerability, nicknamed pedit...
A new Linux kernel privilege escalation vulnerability has been published. It's called DirtyClone, and it belongs to the DirtyFrag family of flaws. A workin...
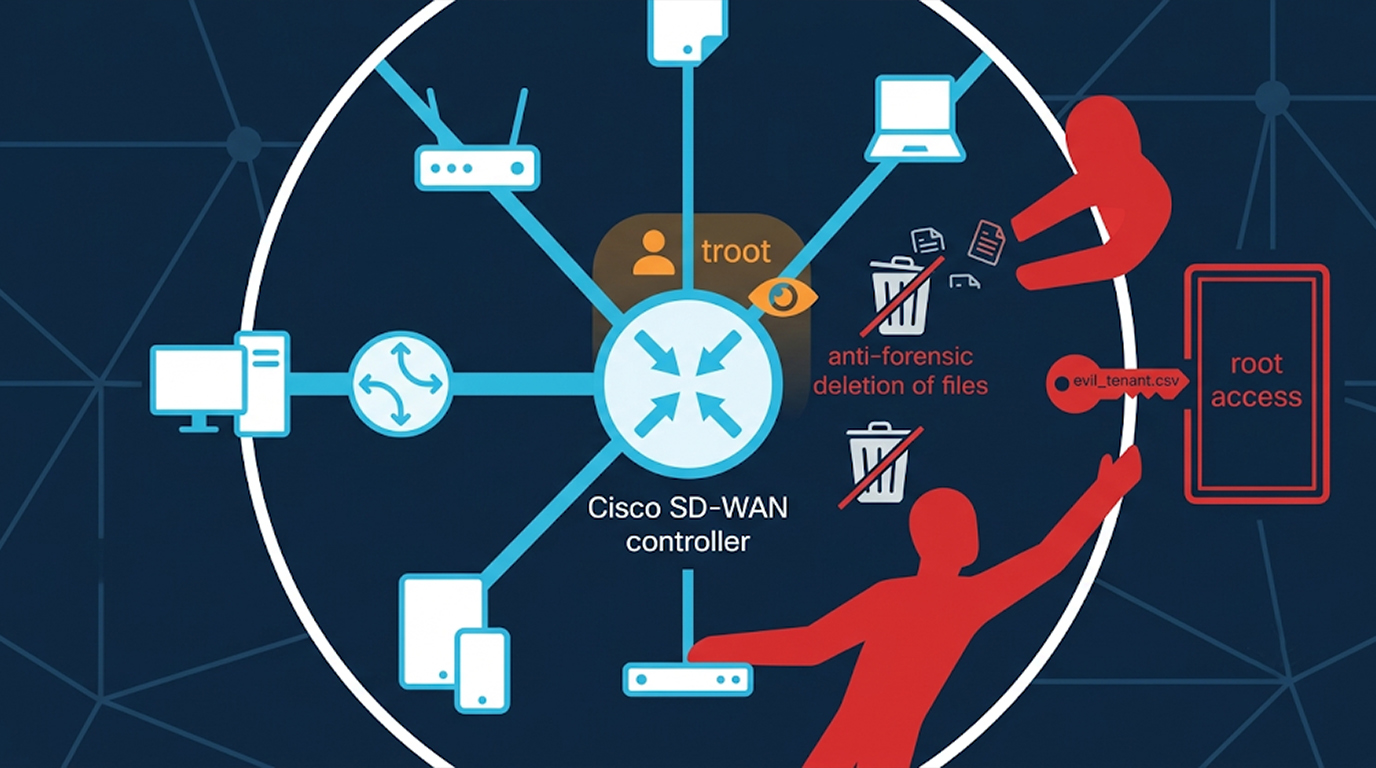
When Cisco disclosed CVE-2026-20245 earlier this month, the company acknowledged that it was already aware of exploitation. Now Mandiant has revealed the f...
You are in the middle of a penetration test. You have gained access to a Linux server. You need to find configuration files, passwords, sensitive data, or...
Microsoft has formally acknowledged the RoguePlanet vulnerability in Microsoft Defender. It now has a CVE identifier: CVE-2026-50656. The company describes...
You find yourself sitting in a job interview for a role in Cybersecurity when the interviewer leans forward with genuine interest and asks, “What is...
The U.S. Cybersecurity and Infrastructure Security Agency just added a new vulnerability to its Known Exploited Vulnerabilities catalog. Federal agencies n...
Here's a nightmare scenario for Arch Linux users. You install or update a package from the Arch User Repository, the community-driven collection that makes...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067