npm Supply Chain Attack Campaign Hits 800 Packages
A cluster of nearly 800 malicious packages has been published to the npm registry as part of a new campaign designed to deliver cross-platform malware targ...
Found 200 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A cluster of nearly 800 malicious packages has been published to the npm registry as part of a new campaign designed to deliver cross-platform malware targ...
A memory corruption flaw in the Linux kernel's Open vSwitch datapath gives ordinary local users a path to root on a broad set of default-configured distrib...
You have made a packet capture (.pcap file) of the live traffic and you want to see whether your firewall will be able to handle this traffic. Whether you...
Adobe has released security updates for a maximum-severity vulnerability in Campaign Classic, its enterprise marketing automation platform. The flaw could...
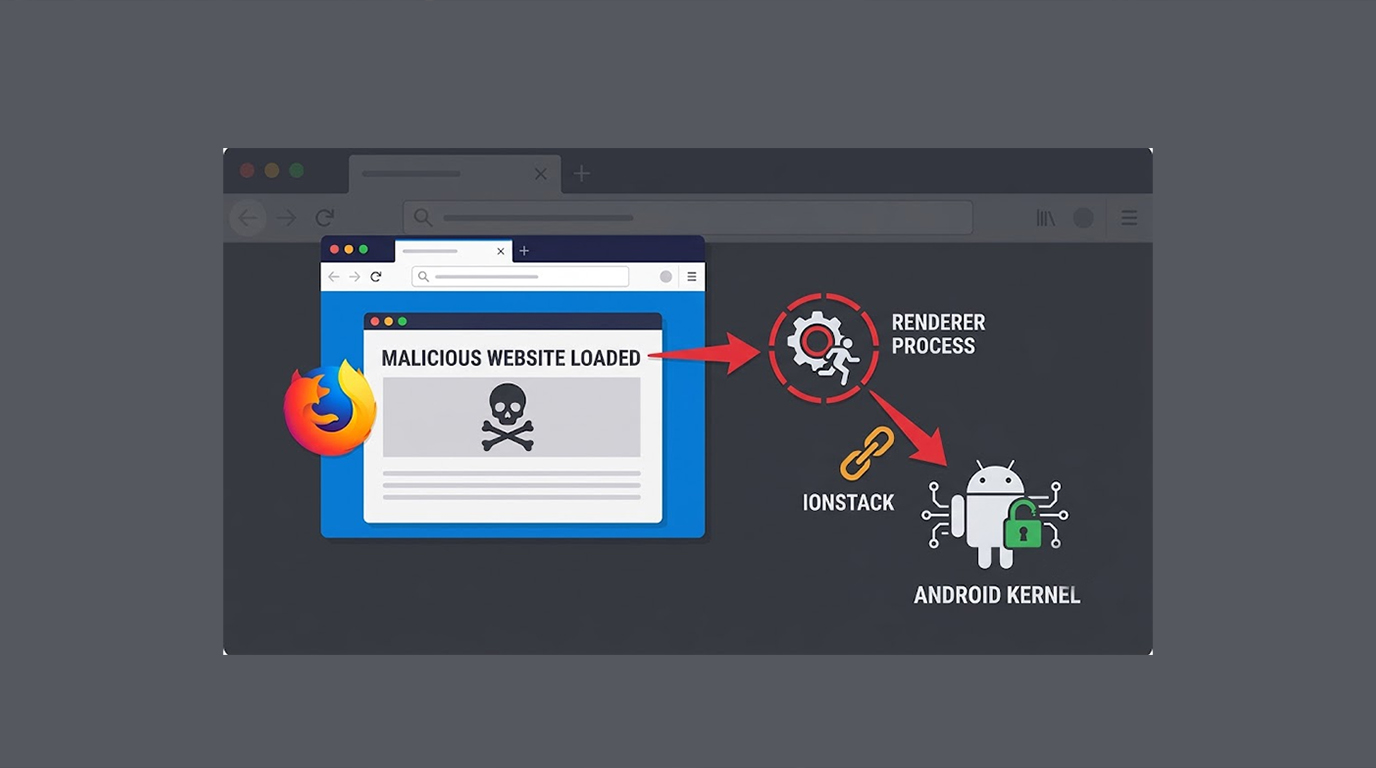
Here is a scenario that should make you update your browser immediately. A security researcher has demonstrated that simply visiting a malicious webpage is...
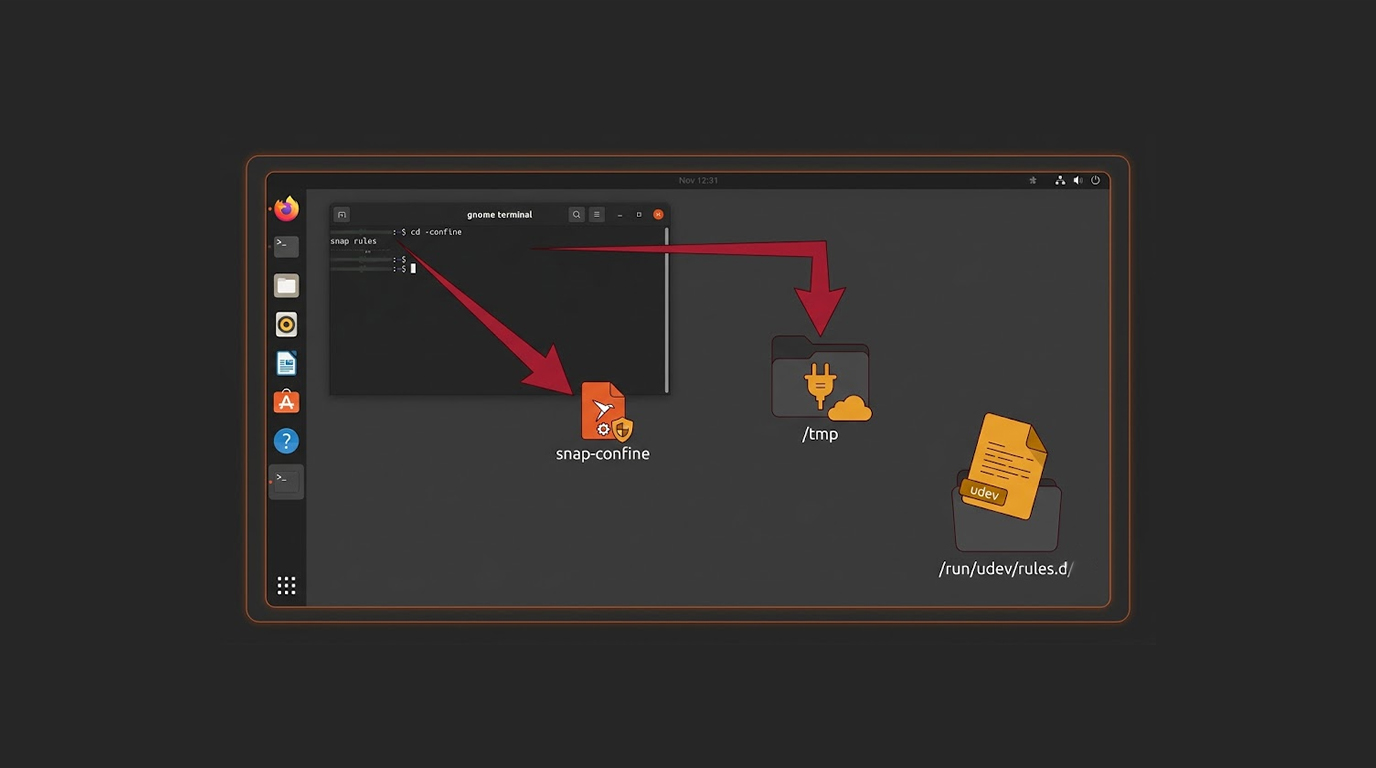
There is a local privilege escalation vulnerability in the snap-confine which lets an unprivileged user gain root permissions and full control over a targe...
You are browsing a news site. A page loads. You see the article. Everything looks normal. But behind the scenes, something else is happening. A WebAssembly...
You have 40,000 new vulnerabilities reported in a single year. Your security team can realistically patch maybe 5% of them. The rest will sit there, unpatc...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067