Cisco SD-WAN Authentication Bypass Zero Day Gets CVSS 10
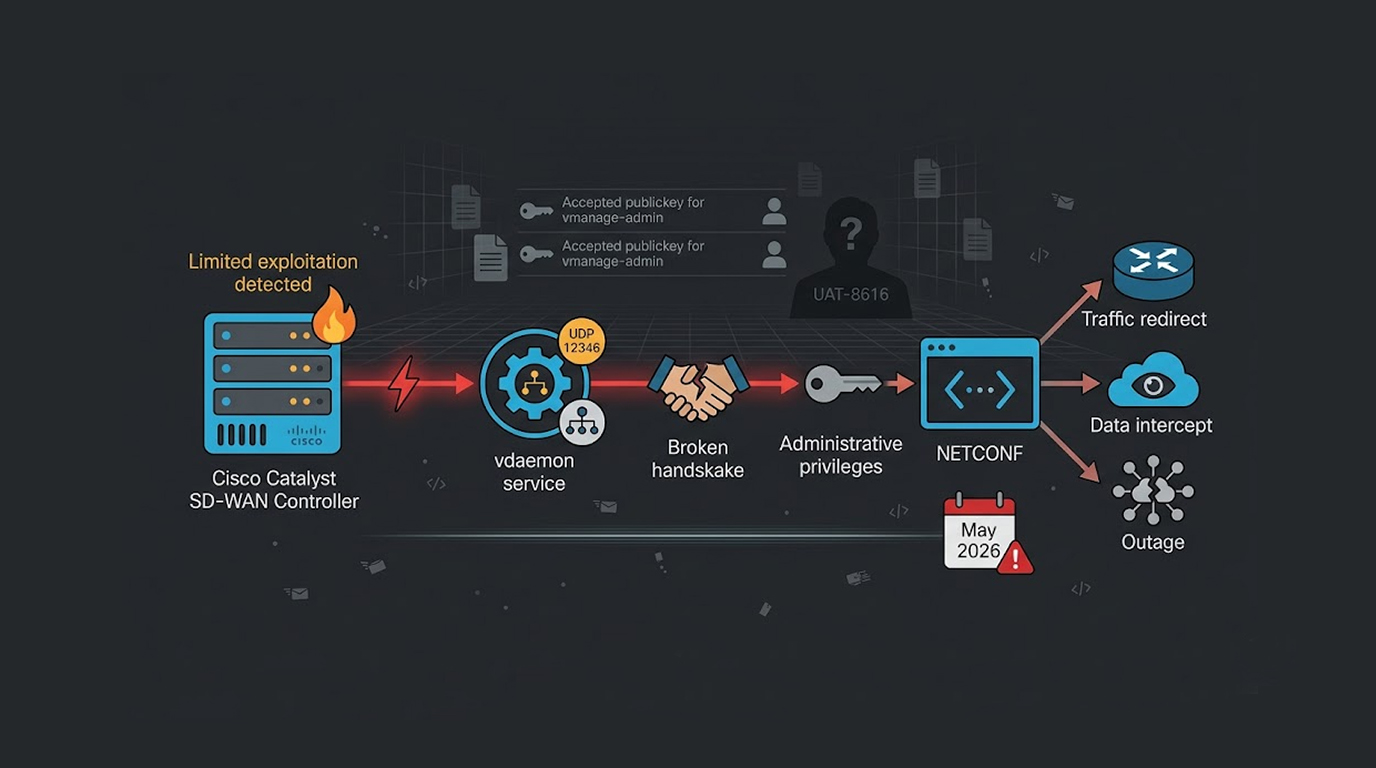
Cisco has released emergency updates for a critical vulnerability in its Catalyst SD-WAN Controller, and the flaw carries a CVSS score of 10.0 which is the...
Found 64 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Cisco has released emergency updates for a critical vulnerability in its Catalyst SD-WAN Controller, and the flaw carries a CVSS score of 10.0 which is the...
Local File Inclusion (LFI) is flagged as a high-severity vulnerability within the Madara Theme for Wordpress that permits unauthenticated attackers to read...
Citrix has just released security updates addressing two vulnerabilities in its widely used NetScaler ADC and NetScaler Gateway products, including one cri...
The open-source webcam security software, MotionEye, is vulnerable to remote code execution, identified as CVE-2025-60787 (motionEye <= 0.43.1b4). Authe...
MongoDB recently announced an extremely serious flaw in its security, which could allow an attacker who does not authenticate to obtain data from the heap...
The WordPress Quiz Maker plugin has been found to have a severe SQL injection vulnerability that could allow an unauthenticated attacker to retrieve sensit...
Two critical security vulnerabilities affecting the Spam Protection, Anti-Spam, and FireWall plugin for WordPress could enable unauthenticated attackers to...
Security researchers and agencies have sounded the alarm over the active exploitation of high-severity vulnerabilities in Progress Kemp LoadMaster and VMwa...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067