Cisco SD-WAN Authentication Bypass Zero Day Gets CVSS 10
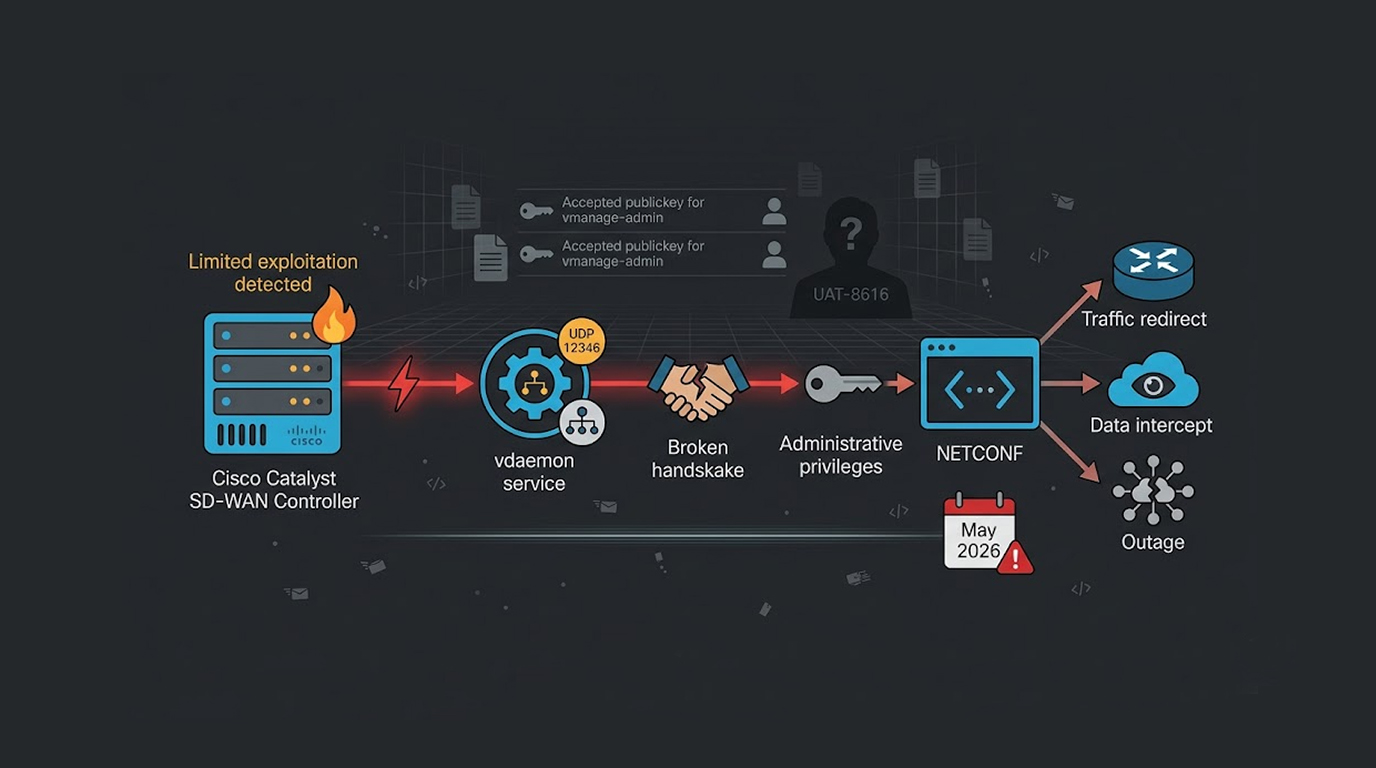
Cisco has released emergency updates for a critical vulnerability in its Catalyst SD-WAN Controller, and the flaw carries a CVSS score of 10.0 which is the...
Found 63 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Cisco has released emergency updates for a critical vulnerability in its Catalyst SD-WAN Controller, and the flaw carries a CVSS score of 10.0 which is the...
You type your SSH password, you press enter, you are logged in, everything seems normal, but someone else just logged in without any password at all, they...
Imagine waking up to find your email server locked. Your admin password does not work. Your users cannot send or receive messages.You did not click a phish...
Authentication state attacks take advantage of weakness in how applications manage login sequences and states. Rather than using encryption or guessing a p...
Bug bounty programs in 2026 still pay the highest rewards for vulnerabilities that give an attacker unauthenticated remote code execution (RCE), full serve...
Raspberry Pi enthusiasts who run RPi-Jukebox-RFID (the popular open-source project that turns a Pi into an RFID-triggered music jukebox, often called Phoni...
Microsoft has issued a warning about a highly coordinated, multi-stage adversary-in-the-middle (AitM) phishing campaign that has escalated into business em...
A vulnerability discovered in the telnet daemon (telnetd) included in the GNU InetUtils package has been present on production systems for almost 11 years....
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067