LiteSpeed cPanel Plugin Privilege Escalation CVSS 10 Exploited
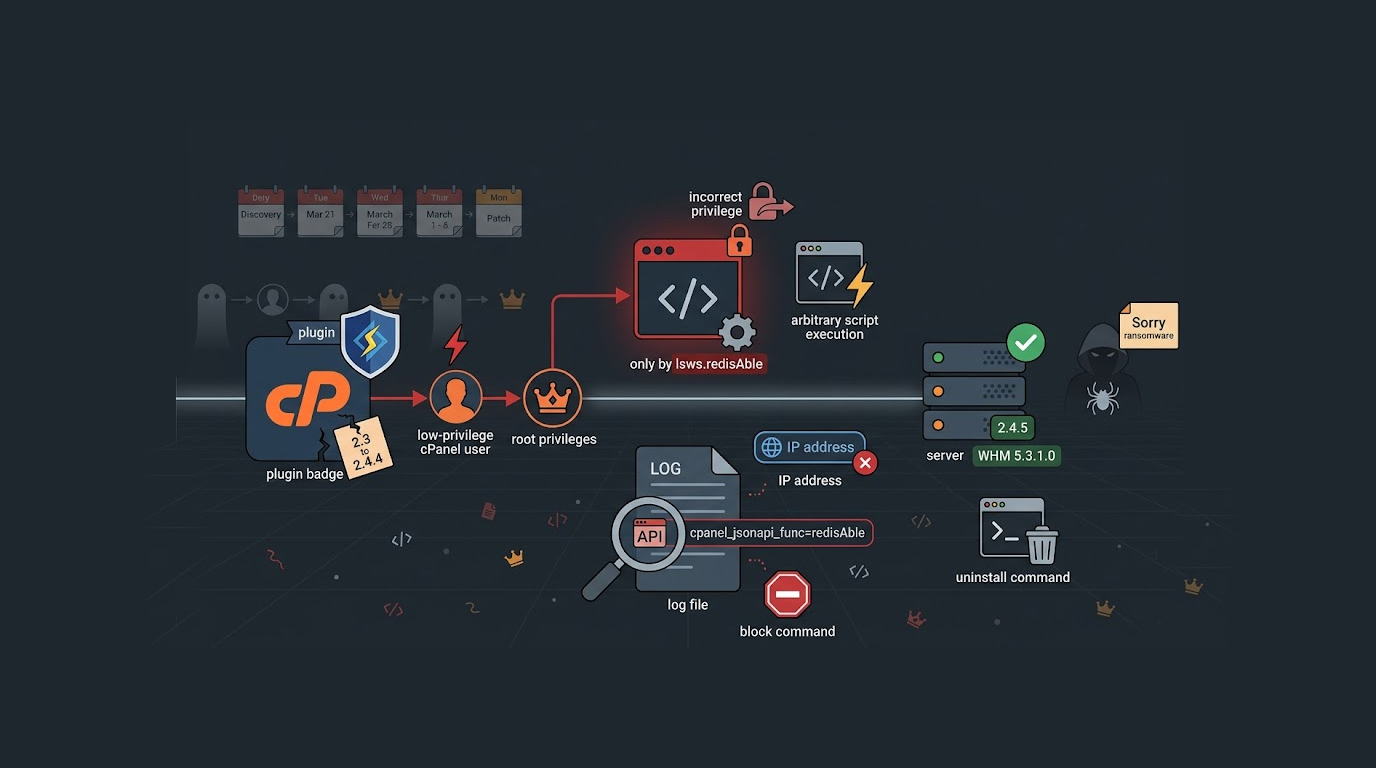
An active exploitation of an extremely severe vulnerability was found on the LiteSpeed cPanel Plugin for User-End usage. This vulnerability allows attacker...
Found 84 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
An active exploitation of an extremely severe vulnerability was found on the LiteSpeed cPanel Plugin for User-End usage. This vulnerability allows attacker...
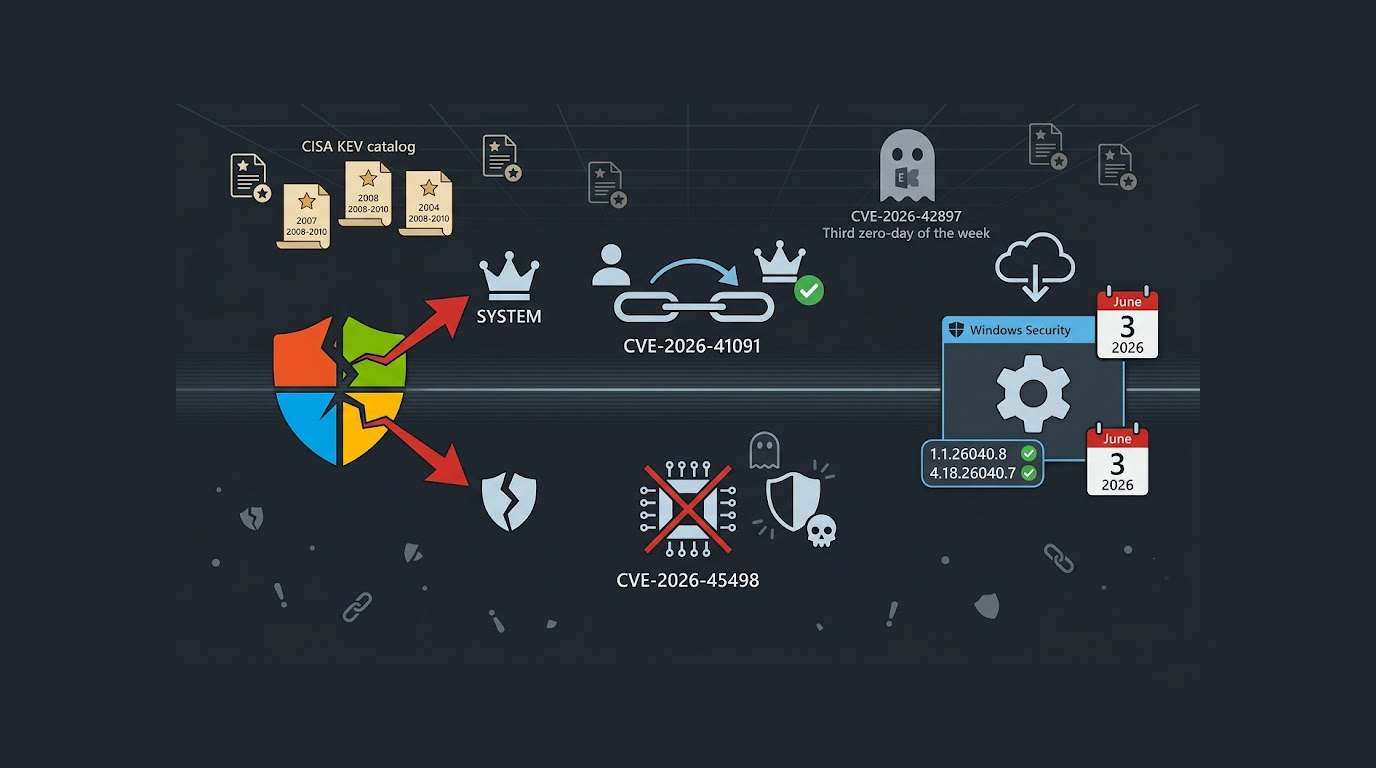
Microsoft has disclosed that two vulnerabilities in Microsoft Defender are under active exploitation, and one of these flaws allows an attacker to gain SYS...
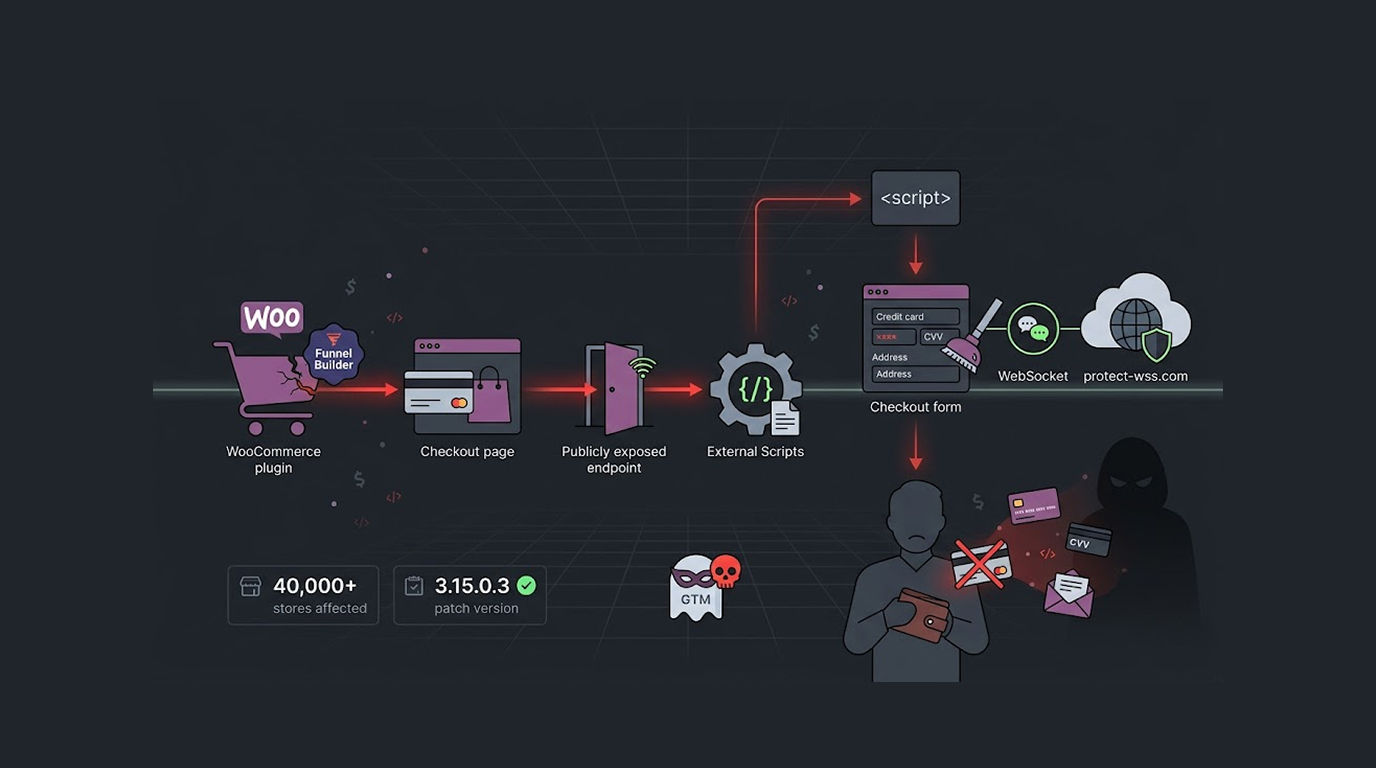
A critical security vulnerability in the Funnel Builder plugin for WordPress is under active exploitation, and attackers are using it to inject malicious J...
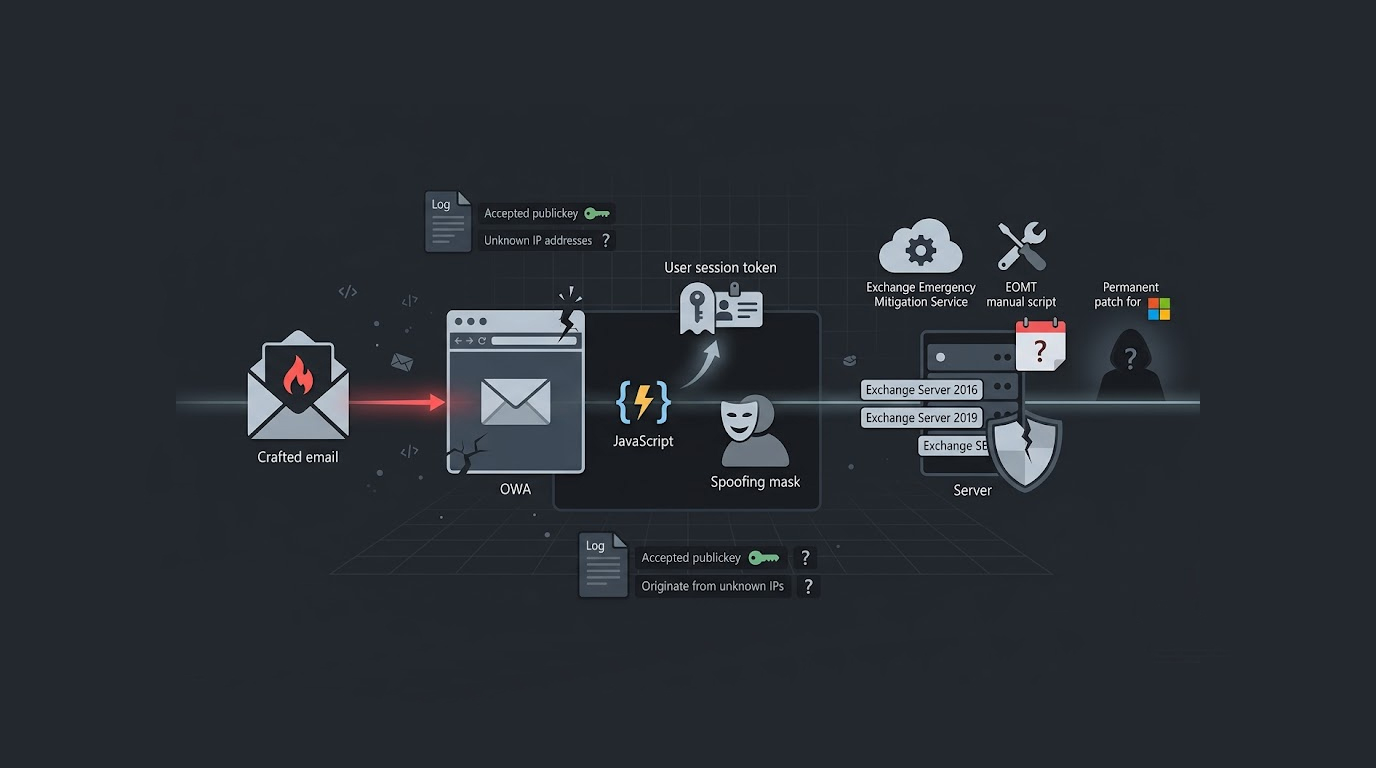
Microsoft has disclosed a new security vulnerability affecting on-premise versions of Exchange Server, and the company confirmed that the flaw has come und...
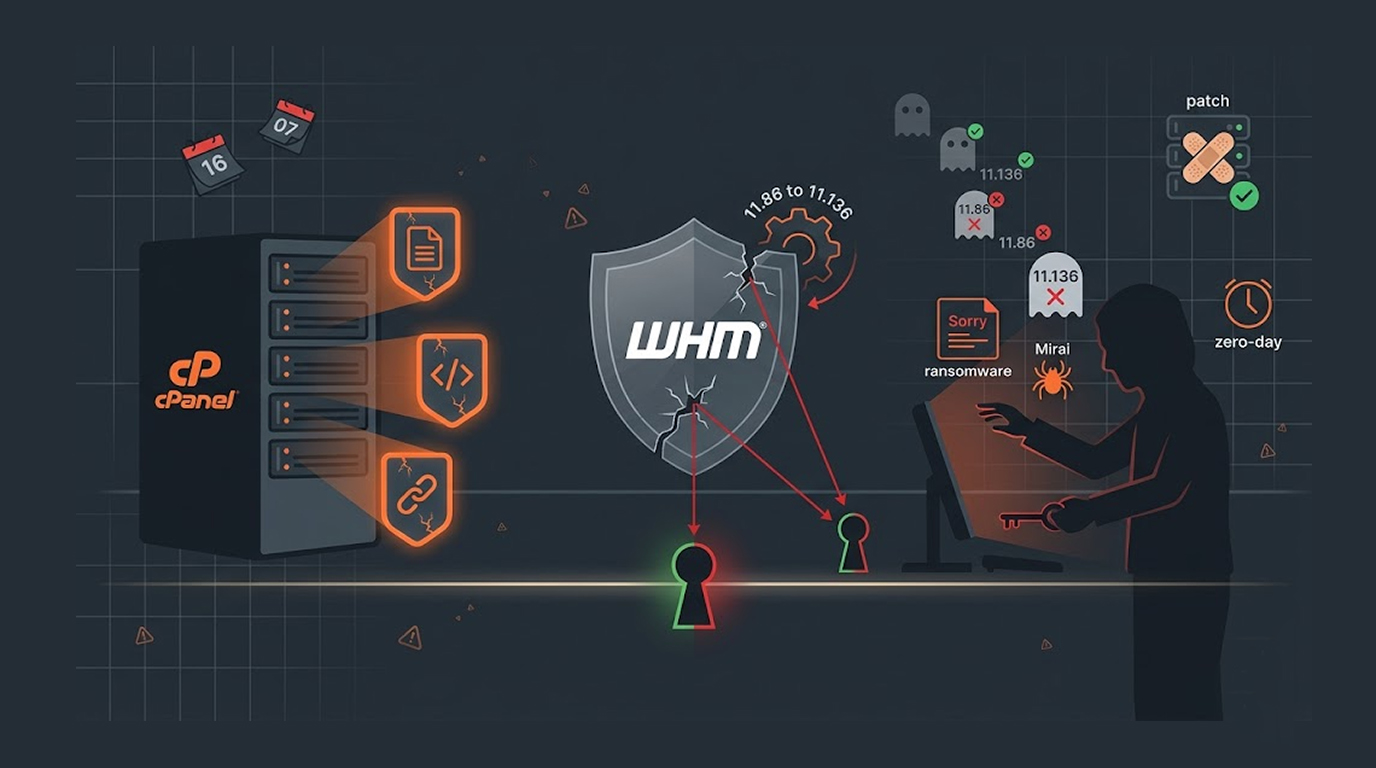
cPanel has issued security patch for three vulnerabilities within its cPanel/WHM software that may allow attackers to read arbitrary files, execute Perl sc...
A critical vulnerability in a popular enterprise office automation platform is being actively exploited. Attackers need no password. No username. No specia...
A critical security flaw in a popular open-source LLM toolkit was published on GitHub. Within half a day, attackers were already using it in the wild. The...
On Friday, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) announced that they have added a significant vulnerability of the F5 BIG-IP Acc...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067