CISA Adds Exploited FileZen OS Command Injection to KEV
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a recently disclosed vulnerability in Soliton Systems FileZen , a file transfer solu...
Found 1023 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a recently disclosed vulnerability in Soliton Systems FileZen , a file transfer solu...
Website hacks are more sophisticated than ever. From infostealer malware campaigns exposing billions of credentials to targeted attacks on WordPress sites...
A new operation called Operation Olalampo has been launched by the Iranian APT group MuddyWater (aka Earth Vetala, Mango Sandstorm, and MUDDYCOAST) that ta...
One of the best ways to identify early-stage intruders (i.e., stalking while still being able to gain access to valuable information) is through the use of...
When a database server is accidentally exposed to the internet (port open without firewall, NAT misconfiguration, cloud security group too permissive), the...
Banner grabbing is one of the oldest tricks in reconnaissance, and in 2026 it remains ridiculously effective, especially on internet-facing servers. You li...
Bug bounty programs in 2026 still pay the highest rewards for vulnerabilities that give an attacker unauthenticated remote code execution (RCE), full serve...
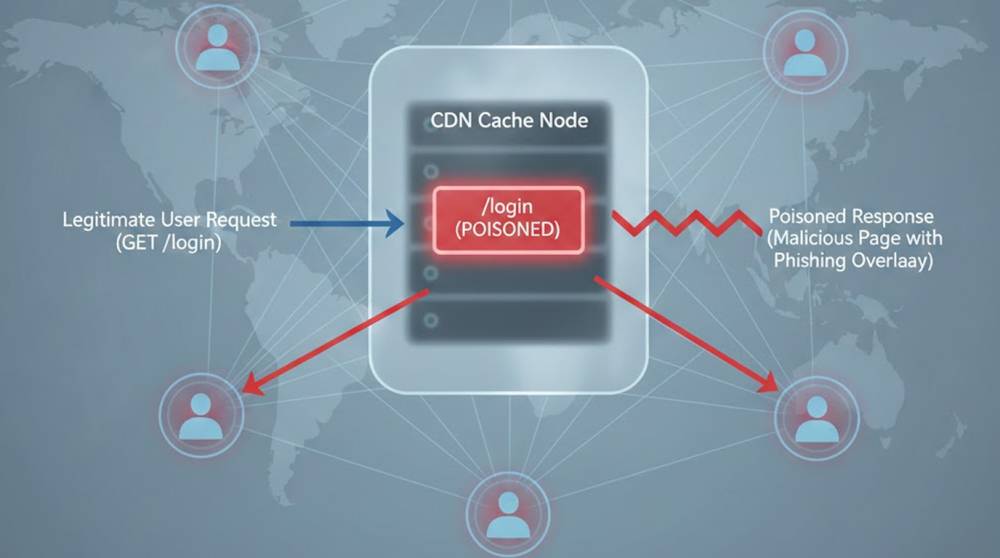
Web cache poisoning never really went away, but in 2026 it has become far more dangerous and far easier to execute than most security teams realize. The c...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067