Pwned Passwords: Why Reused Passwords Still Cause Breaches
A “pwned” password isn’t hacked from you directly. It’s a password that already appeared in a data breach somewhere else on the int...
Found 571 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A “pwned” password isn’t hacked from you directly. It’s a password that already appeared in a data breach somewhere else on the int...
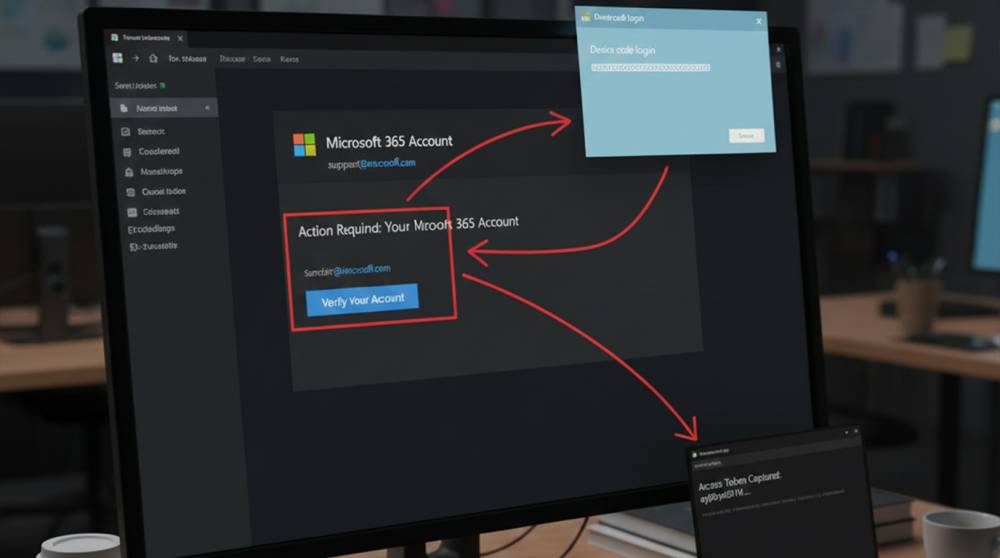
Proofpoint's Security Researchers identified UNK_AcademicFlare, a cybercriminal/actor operating out of Russia that has been running targeted phishing campa...
The majority of gamers assume that cheaters utilize either "cracked" programs or shady mods, whereas in fact most of the cheating occurs on the back end, i...
APIs form a core component to the design of modern applications. However, by only focusing on authentication ("Who Are You?"), you could be overlooking a m...
Cisco has confirmed active exploitation of a maximum severity zero day vulnerability affecting Cisco AsyncOS, the operating system behind Cisco Secure Emai...
Cross-Site Request Forgery (CSRF) attacks are one of the most underrated web attacks, and this is even more common in legacy applications, particularly in...
The SQL injection attack is not usually as dramatic as other cyber-attacks. In fact, it is generally present in everyday applications that had little or no...
Version 6.7.2 RosarioSIS contains a cross-site scripting (XSS) security flaw found in the scheduling module. This vulnerability allows an attacker to injec...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067