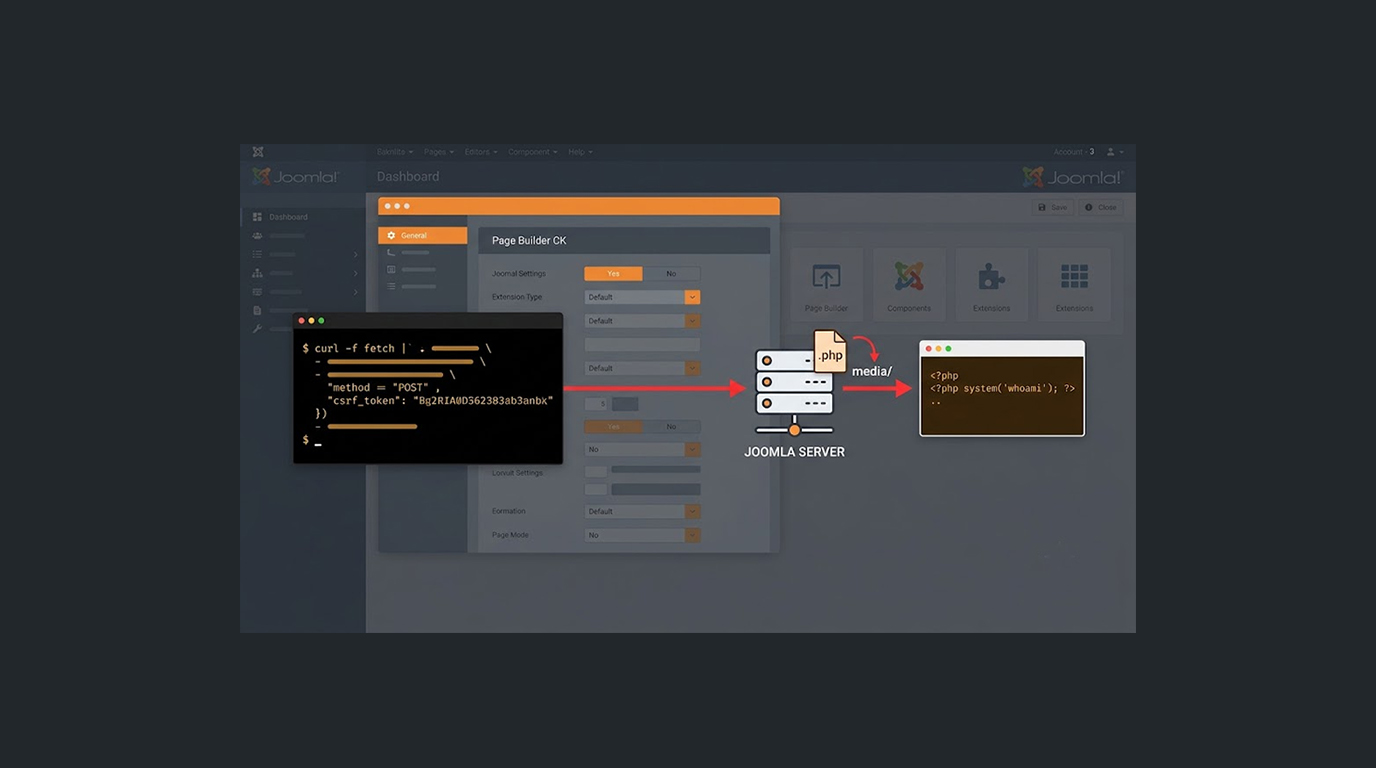
Joomla Page Builder CK RCE via Arbitrary File Upload
There is a serious vulnerability in Joomla Page Builder CK which enables an attacker without authentication to upload PHP files and run arbitrary code on t...
Found 135 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
There is a serious vulnerability in Joomla Page Builder CK which enables an attacker without authentication to upload PHP files and run arbitrary code on t...
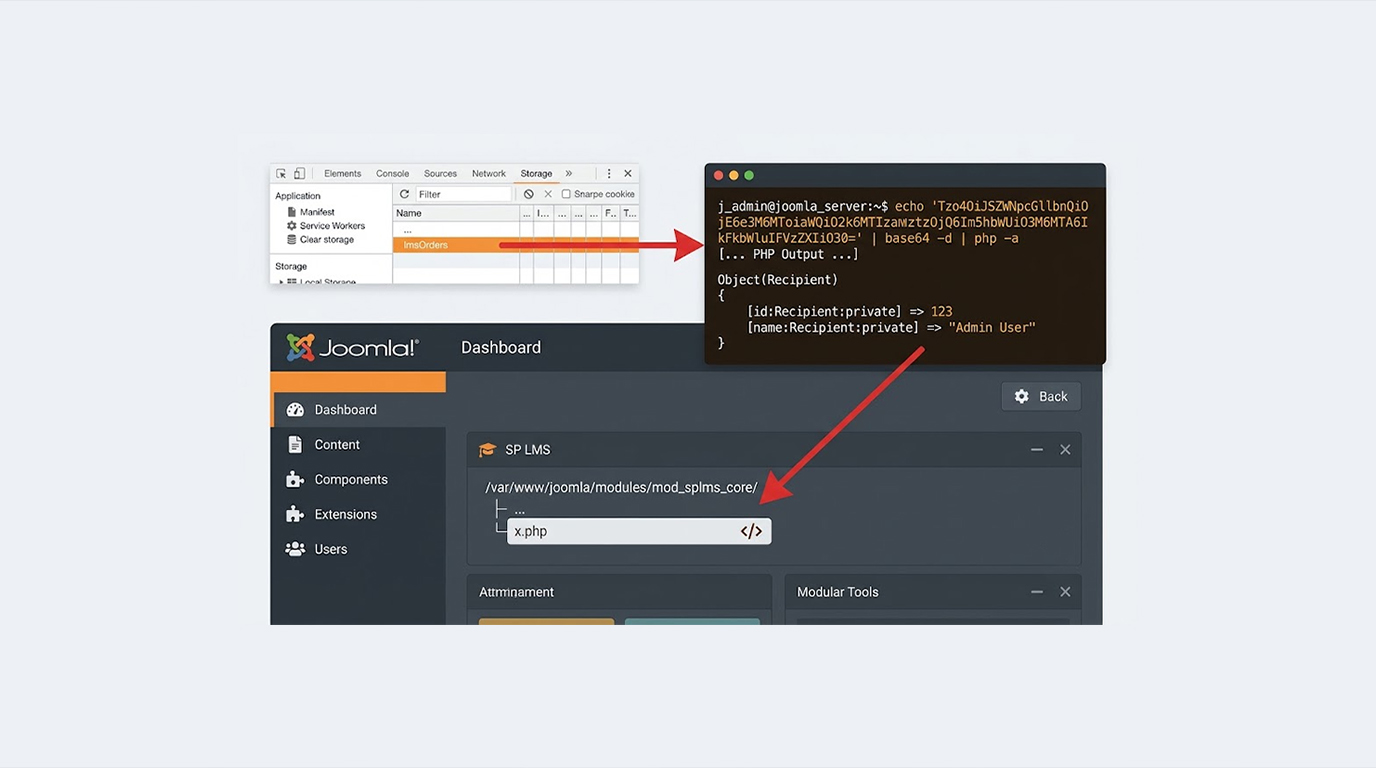
Joomla extension JoomShaper SP LMS contains an object injection vulnerability leading to remote code execution for the attacker. This vulnerability is iden...
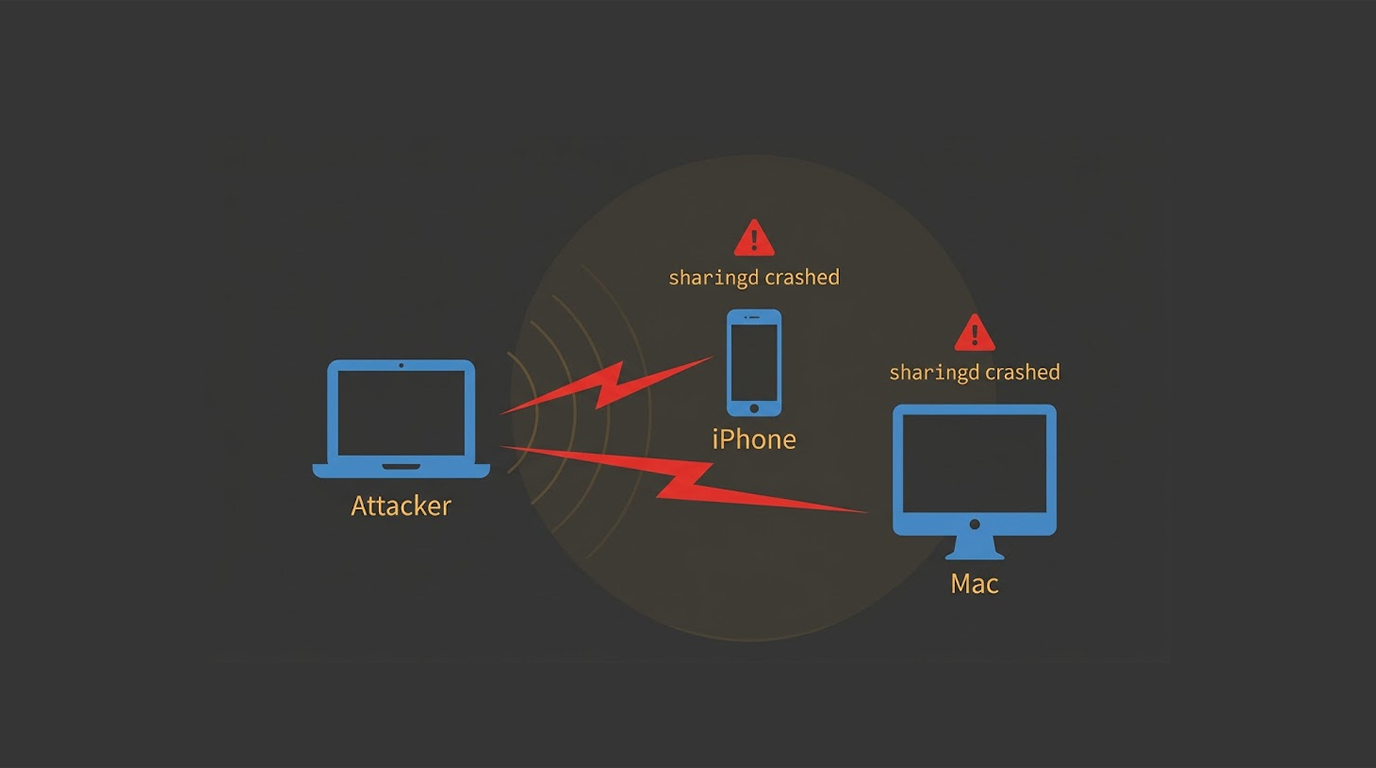
An attacker within wireless range, with just a laptop and no prior connection, can crash the sharing service on a Mac or iPhone set to receive from anyone....
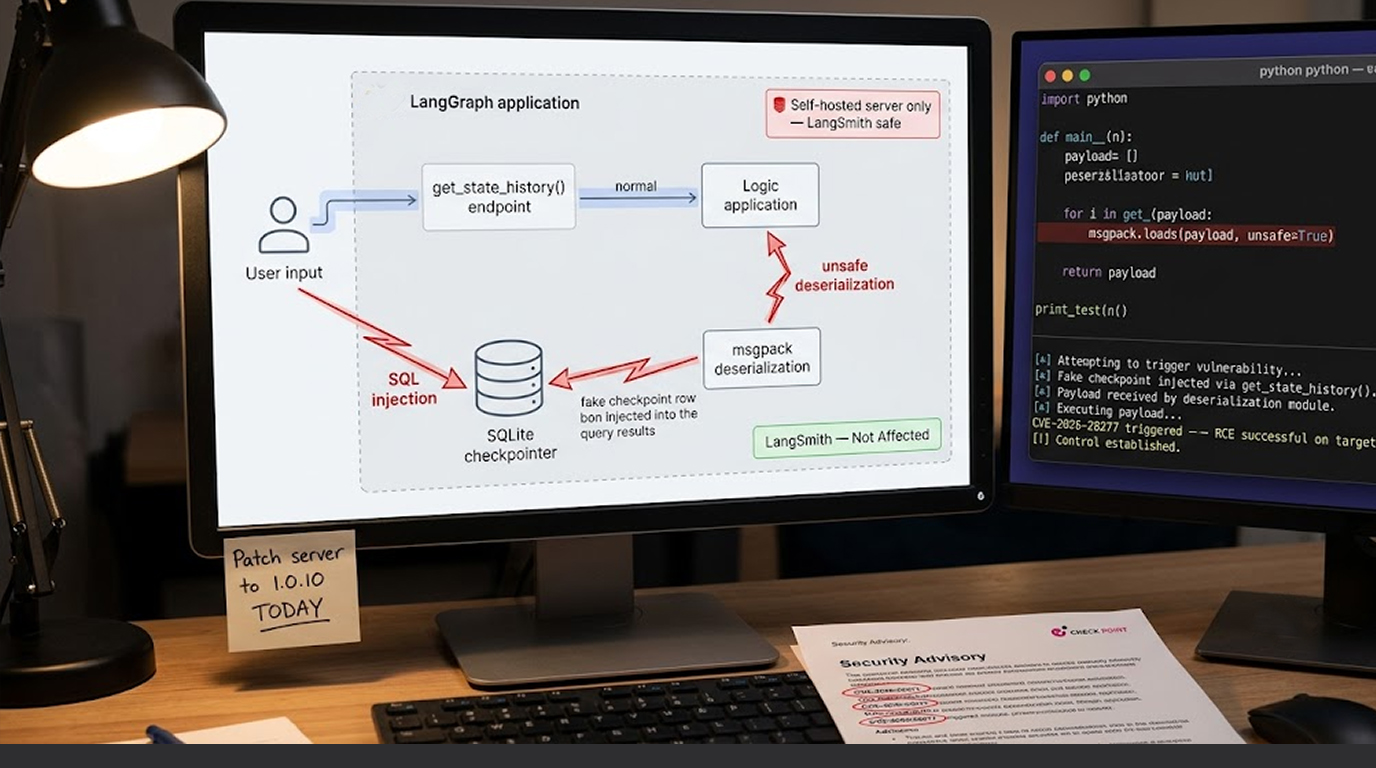
LangGraph is helping you build complex, stateful, multi-agent AI applications. It's open-source, built by LangChain, and widely used by developers who want...
You are working on an important project. Your computer slows down. The cursor moves on its own. Files open and close without you touching the mouse. You a...
Microsoft just released a record 206 Microsoft security patches for June 2026. That's not a typo. Two hundred and six fixes. Of these, 39 are rated Critic...
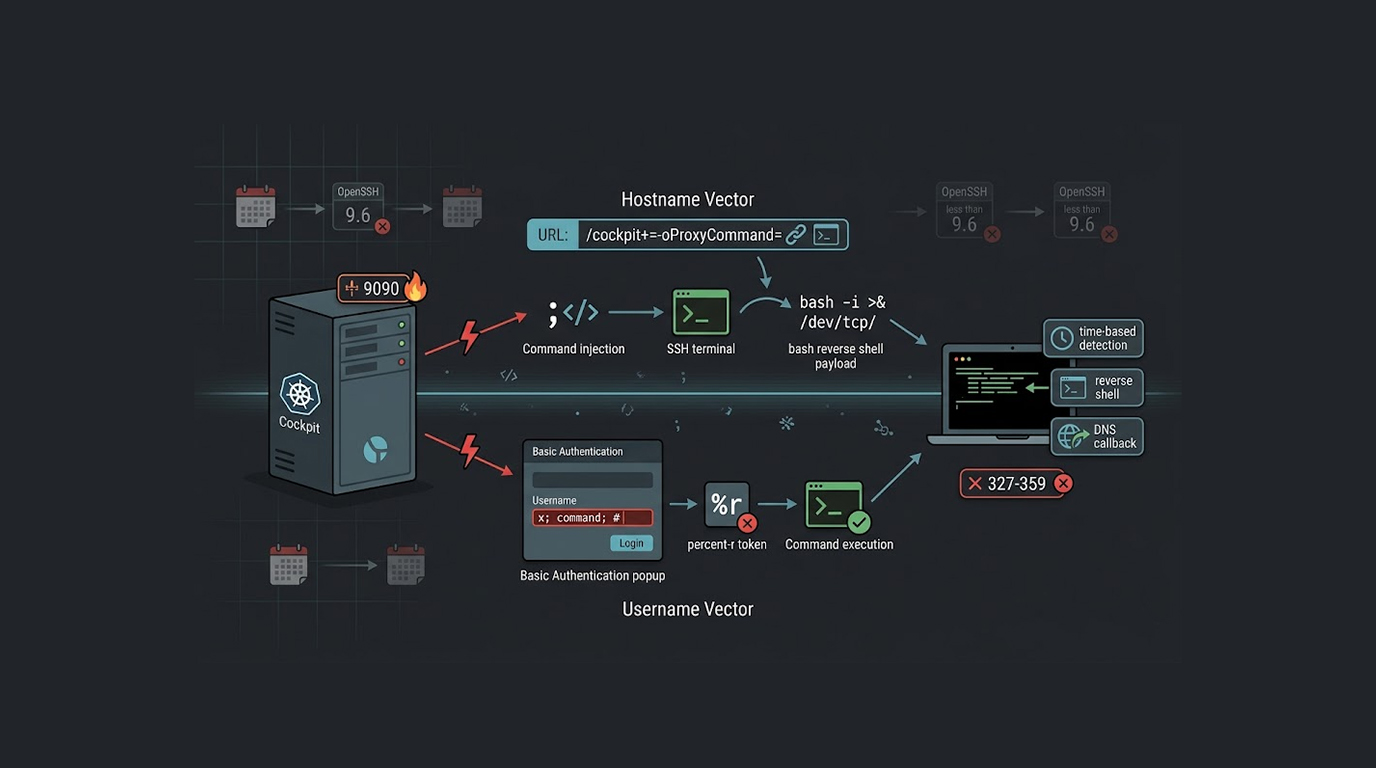
A security flaw in Cockpit allows an attacker to run arbitrary code on the server without authenticating first. The problem manifests itself through Cockpi...
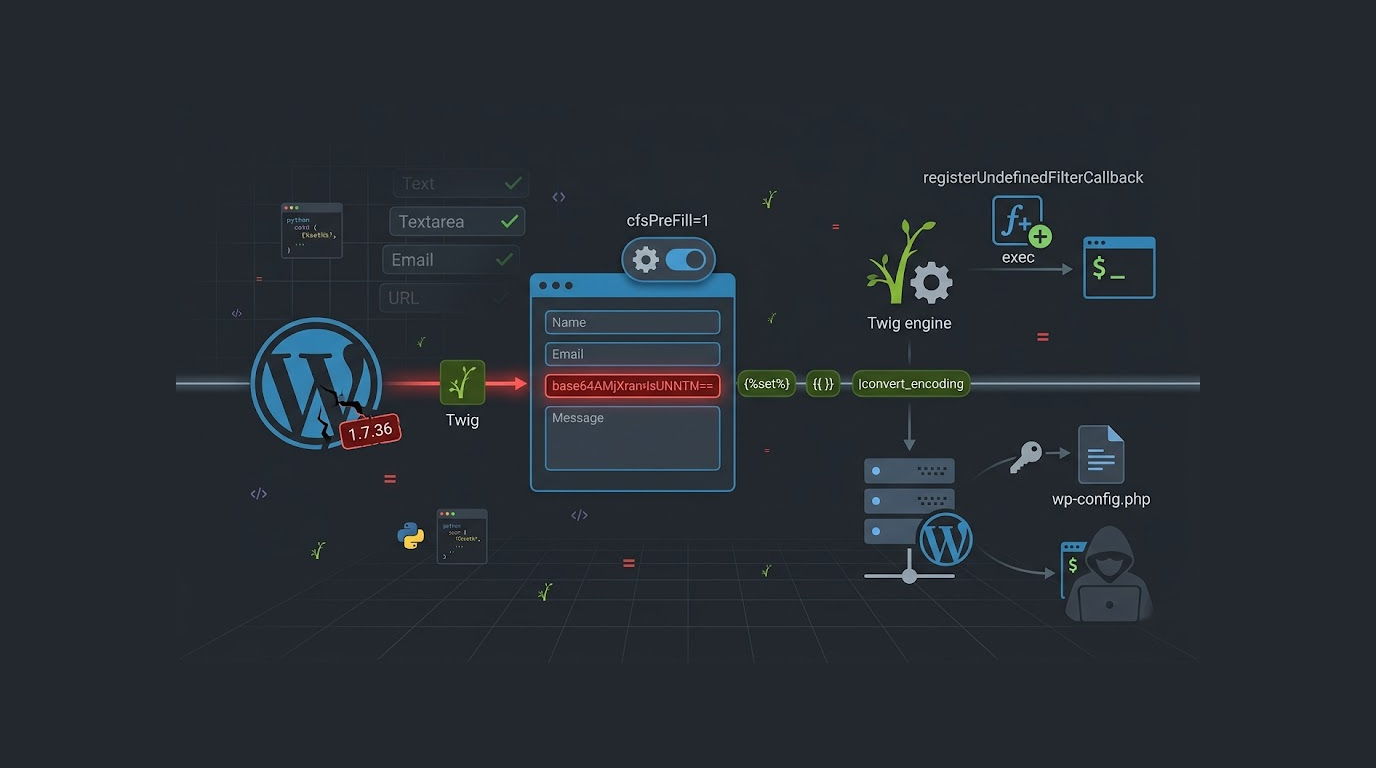
The Supsystic Contact Form plugin for WordPress contains an SSTI vulnerability that allows an attacker to run any command on the server. This vulnerability...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067