npm Supply Chain Attack Campaign Hits 800 Packages
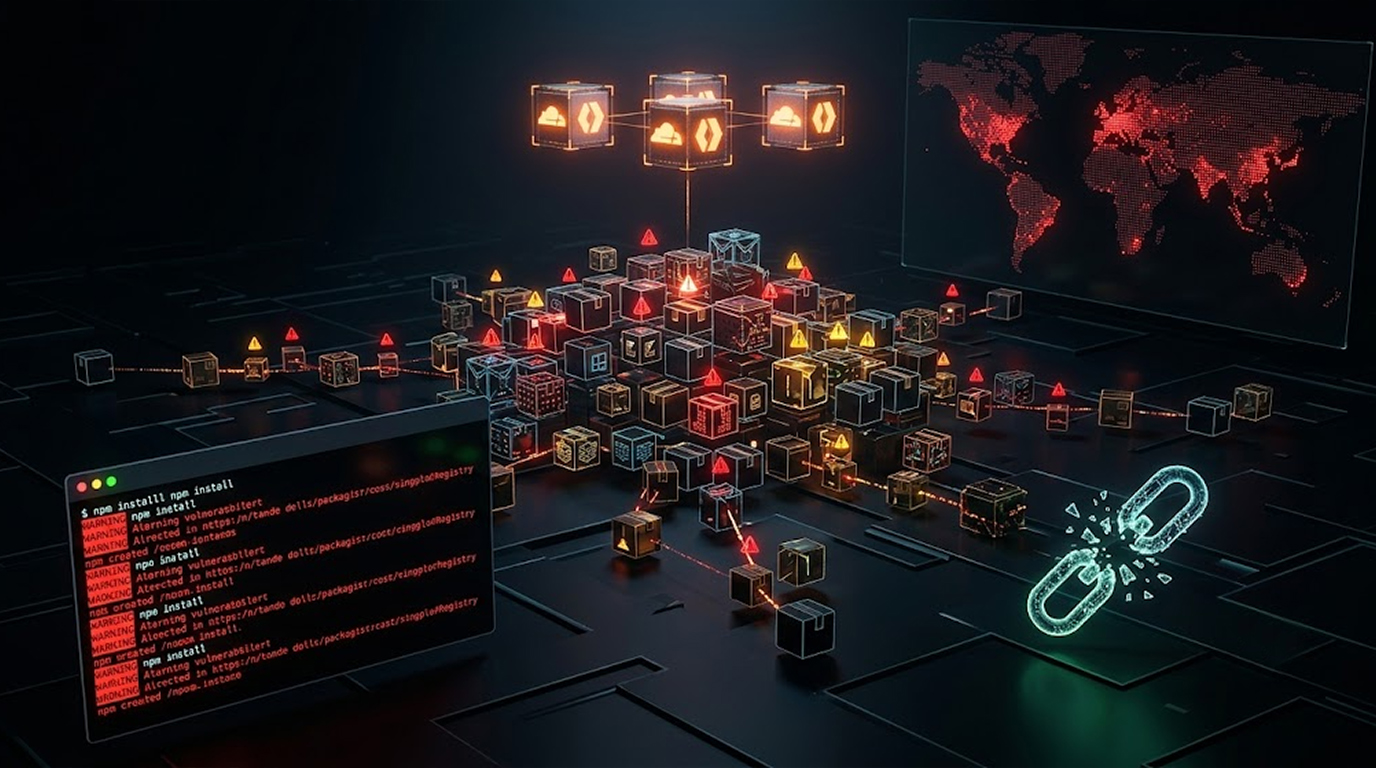
A cluster of nearly 800 malicious packages has been published to the npm registry as part of a new campaign designed to deliver cross-platform malware targ...
Found 199 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A cluster of nearly 800 malicious packages has been published to the npm registry as part of a new campaign designed to deliver cross-platform malware targ...
Picture this. You check into a hotel, connect to the Wi-Fi, and see a browser update prompt. It looks legitimate. You click it, install the update, and go...
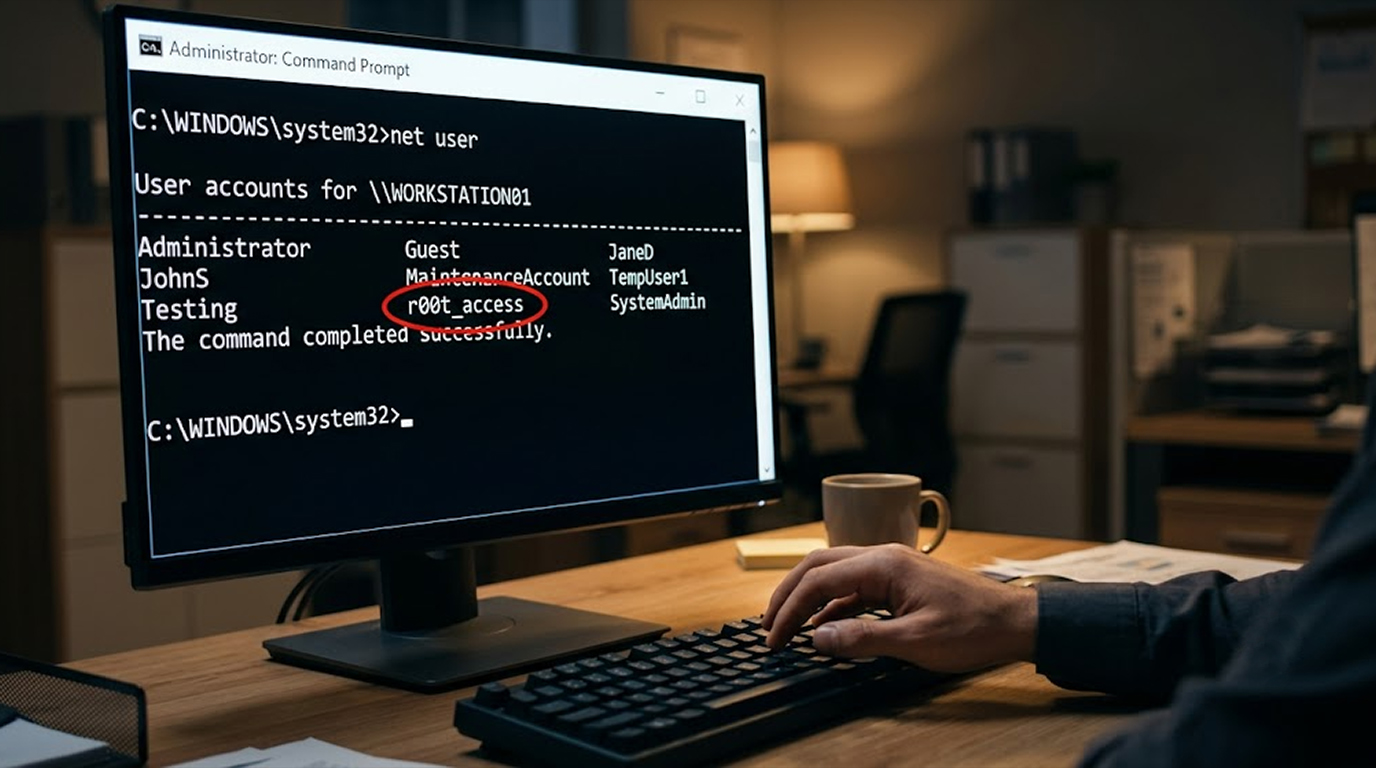
Now, you have started going through the accounts on your computer and you see something unusual. It may be some account which you did not create before or...
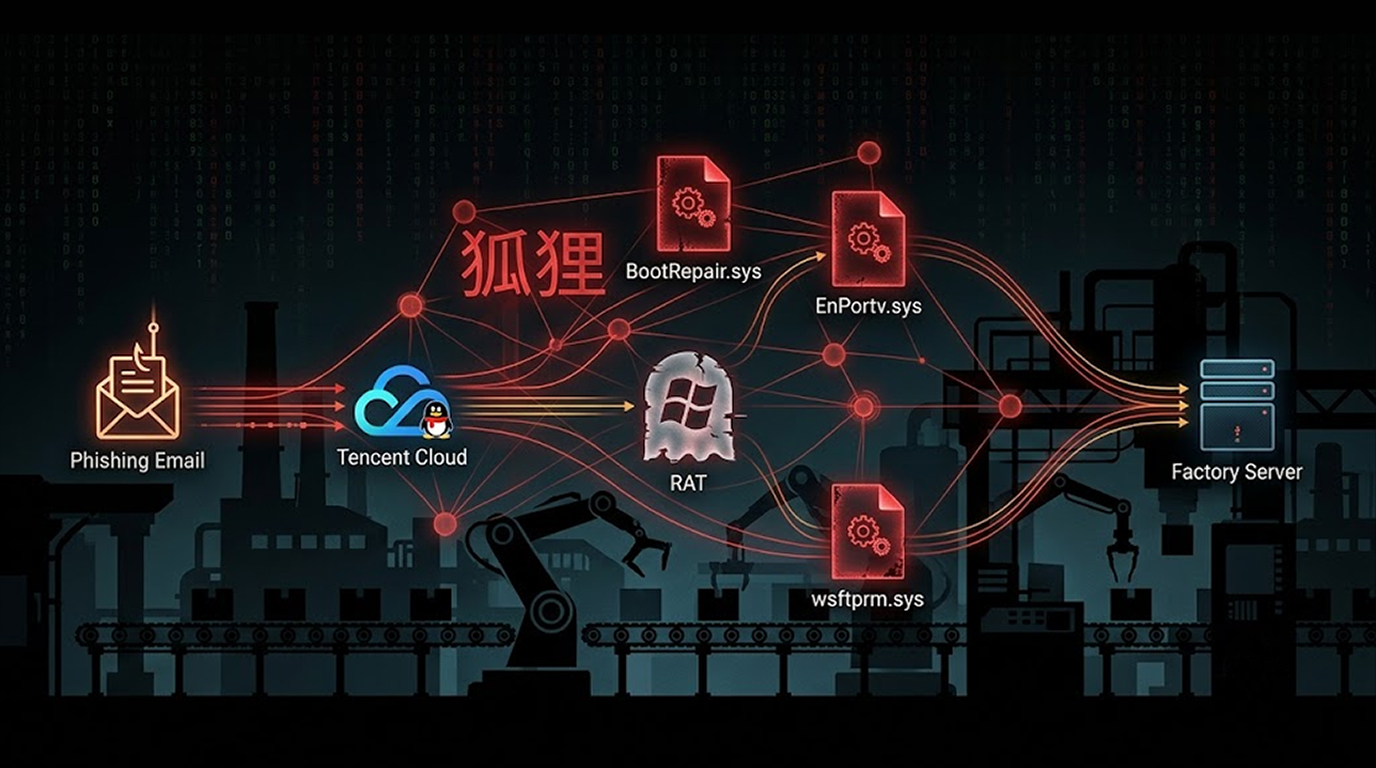
A Chinese cybercrime group known as Silver Fox is back with new tricks. The threat actors have been observed using previously unreported drivers as part of...
Here’s what happens. You are sitting at your desk, checking your WhatsApp, and there’s a file on WhatsApp sent to you by one of your colleagues...
You install a banking app. It looks legitimate. It even has the right logo and colors. You enter your credentials. You wait for the "loading" screen to fin...
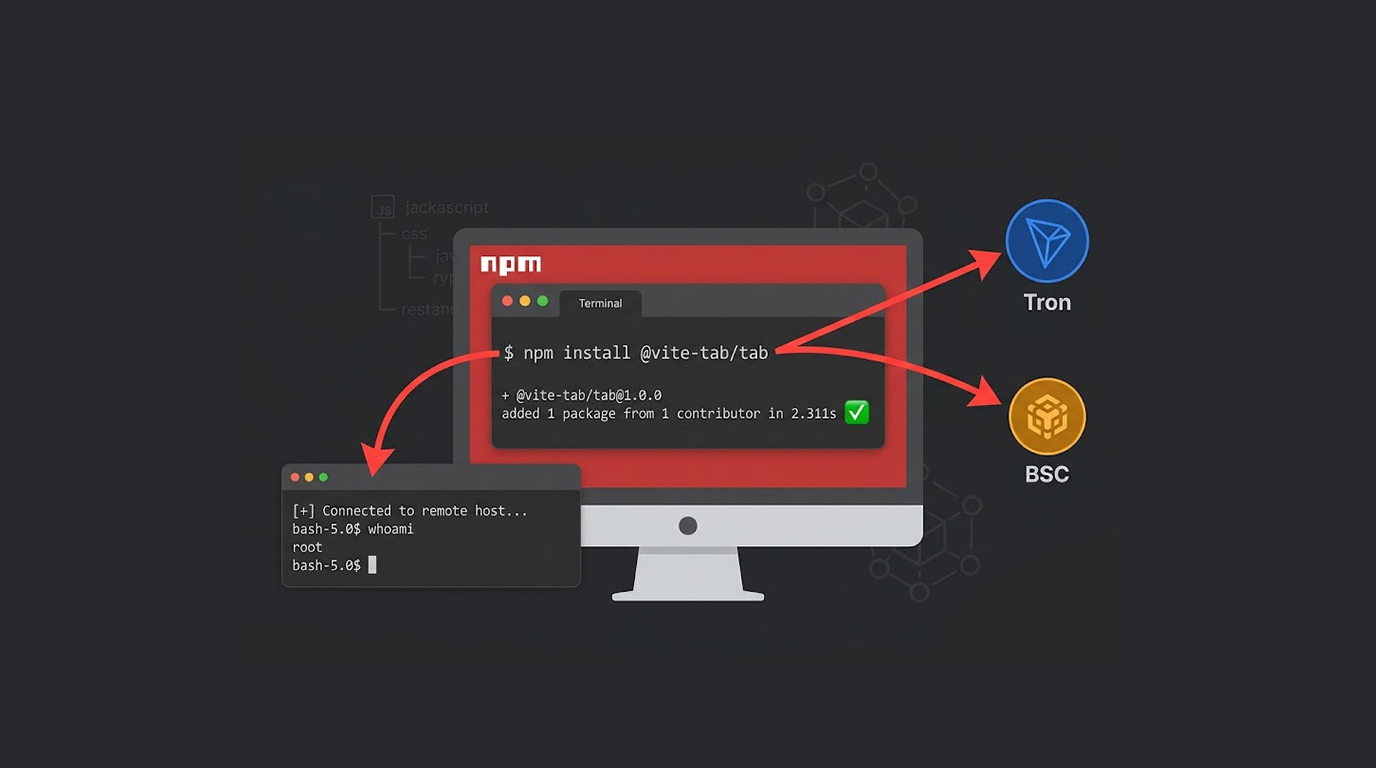
A cluster of seven malicious npm packages is targeting the Vite frontend tooling ecosystem. The campaign, codenamed ViteVenom, marks an expansion of ChainV...
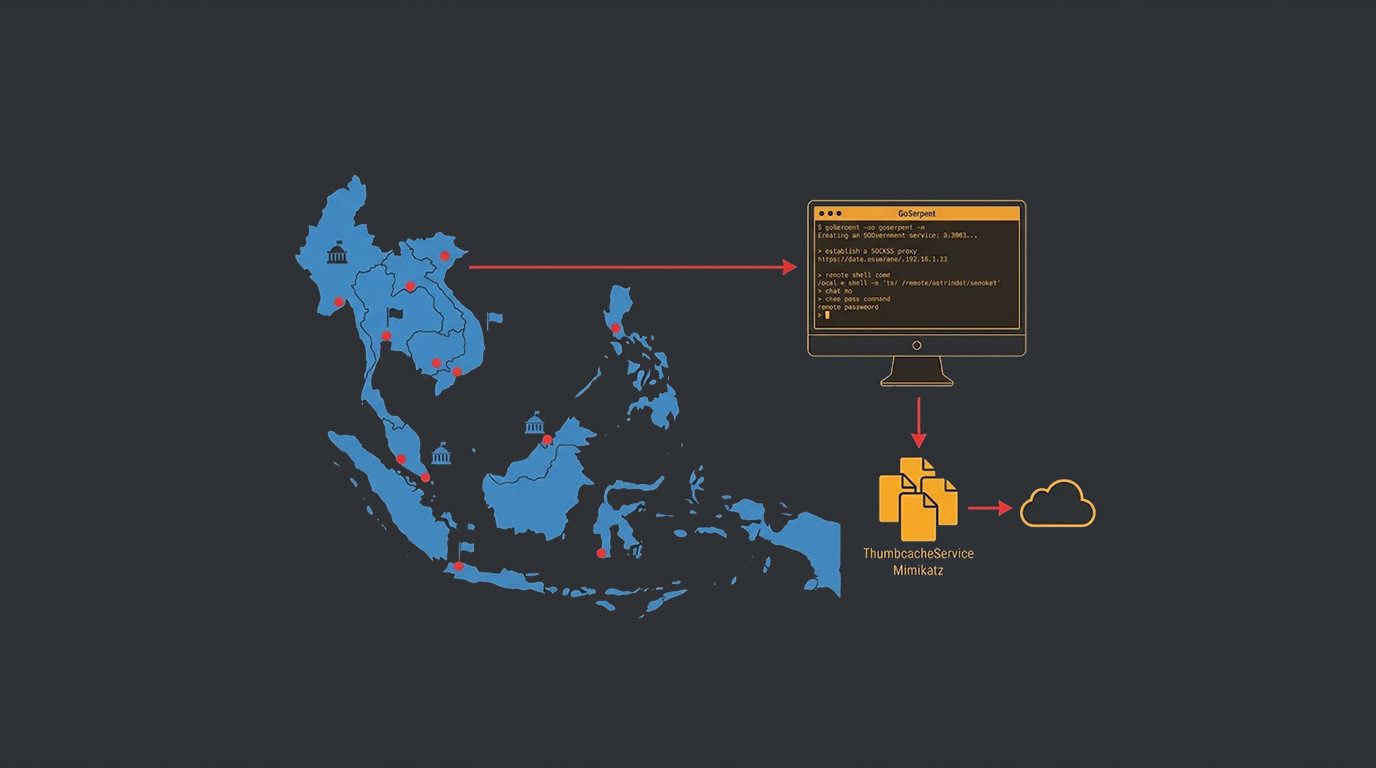
A new malware strain known as GoSerpent has been utilized in cyber attacks against targets from Southeast Asia starting in late 2025. As per Kaspersky, the...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067