How Malware Hides in Normal Files (PNG, PDF, LNK)
A common misconception people have about malware is that it has to have a frightening name (like “virus.exe”) and sometimes the malware will ha...
Found 79 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A common misconception people have about malware is that it has to have a frightening name (like “virus.exe”) and sometimes the malware will ha...
The three existing Android banking trojans are all up and running, performing successfully in the real world as well, but their methods of infection, level...
A multi-layer phishing operation that targets users in Russia across multiple stages using schemes isn't an uncommon tactic in this arena of internet-based...
Think of your smartphone as a central hub for all of your electronic communication and transactions; where the banking app, emails, photographs, work-relat...
Fake crack files are one of the most common malware delivery methods today.They don’t target experts.They target normal people trying to save time or...
Users often have two needs in conflict: 1. Convenience.2. Privacy.Business objectives create the same tension:1. Easy onboarding means a high conversi...
Since January 2022, cybersecurity researchers have discovered an ongoing web skimming operation targeting businesses associated with some of the largest gl...
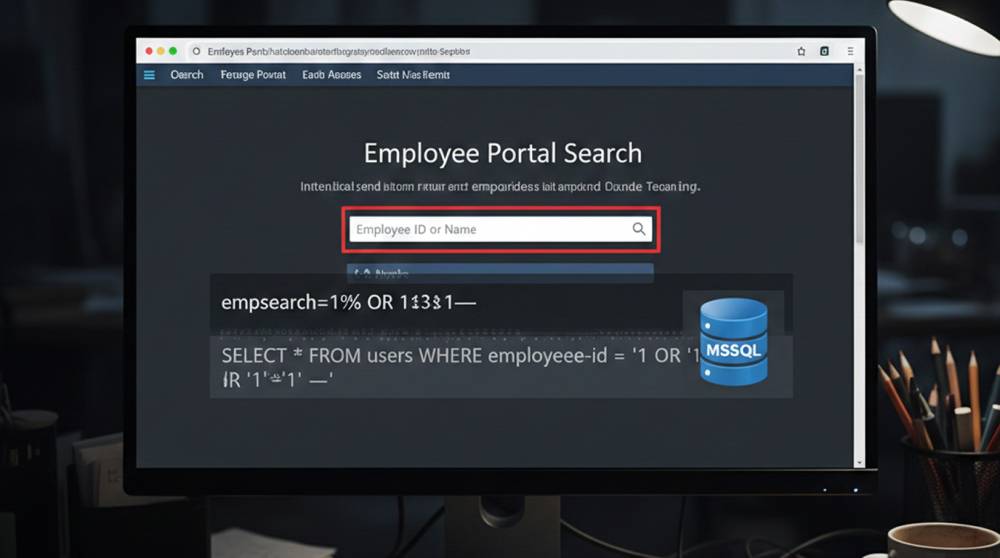
Summar Employee Portal versions before 3.98.0 had a SQL injection vulnerability. This affects the Employee Directories feature of the software under the au...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067