Miasma Supply Chain Attack Hits 73 Microsoft GitHub Repos
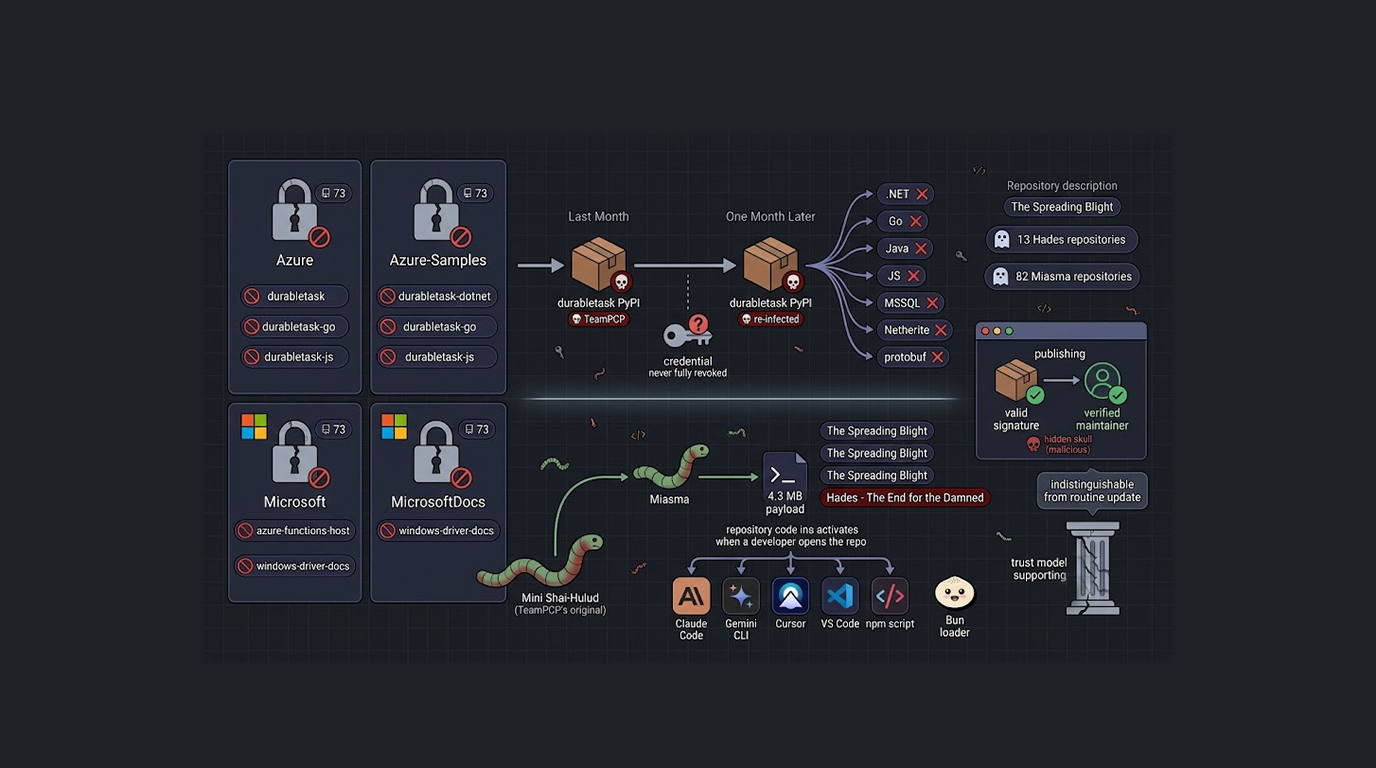
A recent Miasma self-replicating supply chain attack hit 73 different GitHub repositories owned by Microsoft in four different organizations: Azure, Azure...
Found 144 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A recent Miasma self-replicating supply chain attack hit 73 different GitHub repositories owned by Microsoft in four different organizations: Azure, Azure...
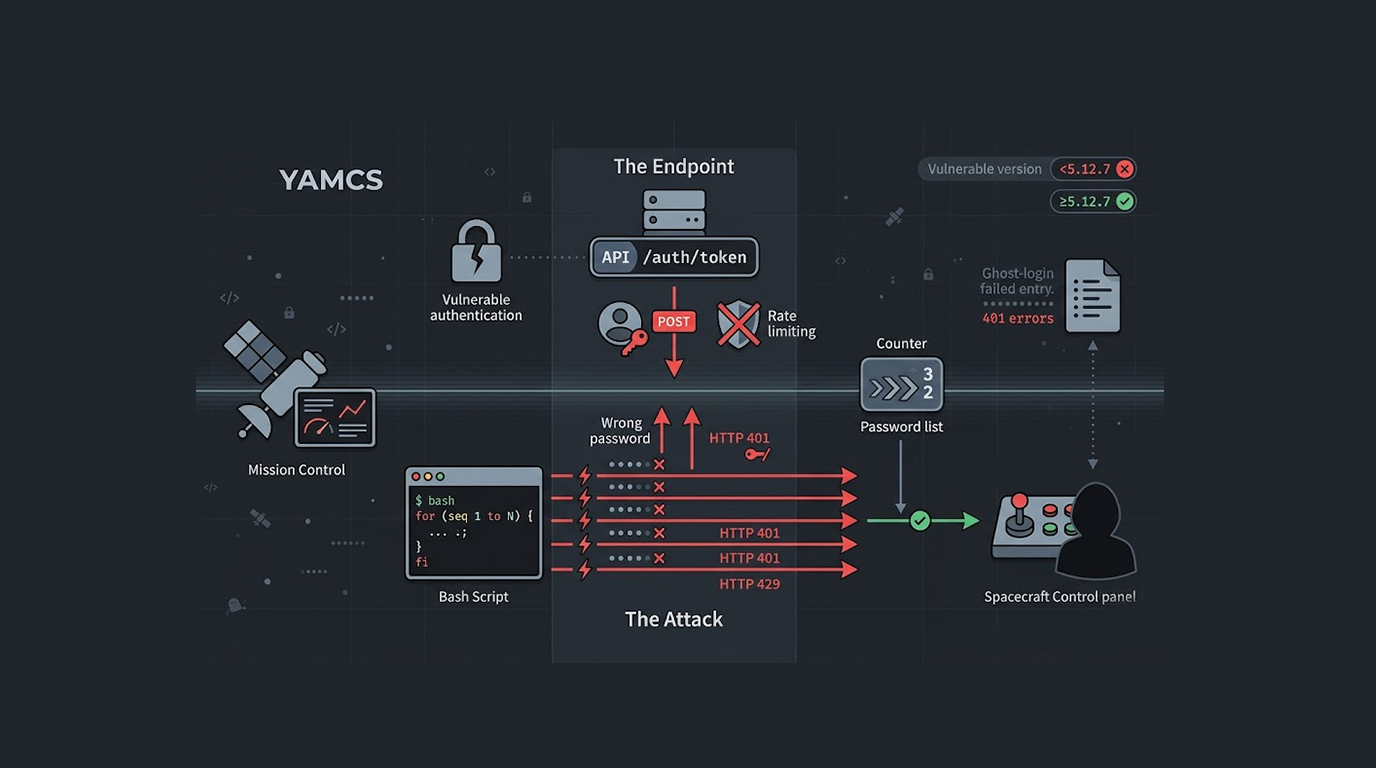
YAMCS contains an exploitable security vulnerability that allows endless brute-force attempts to log into the user accounts, meaning there is no limit on t...
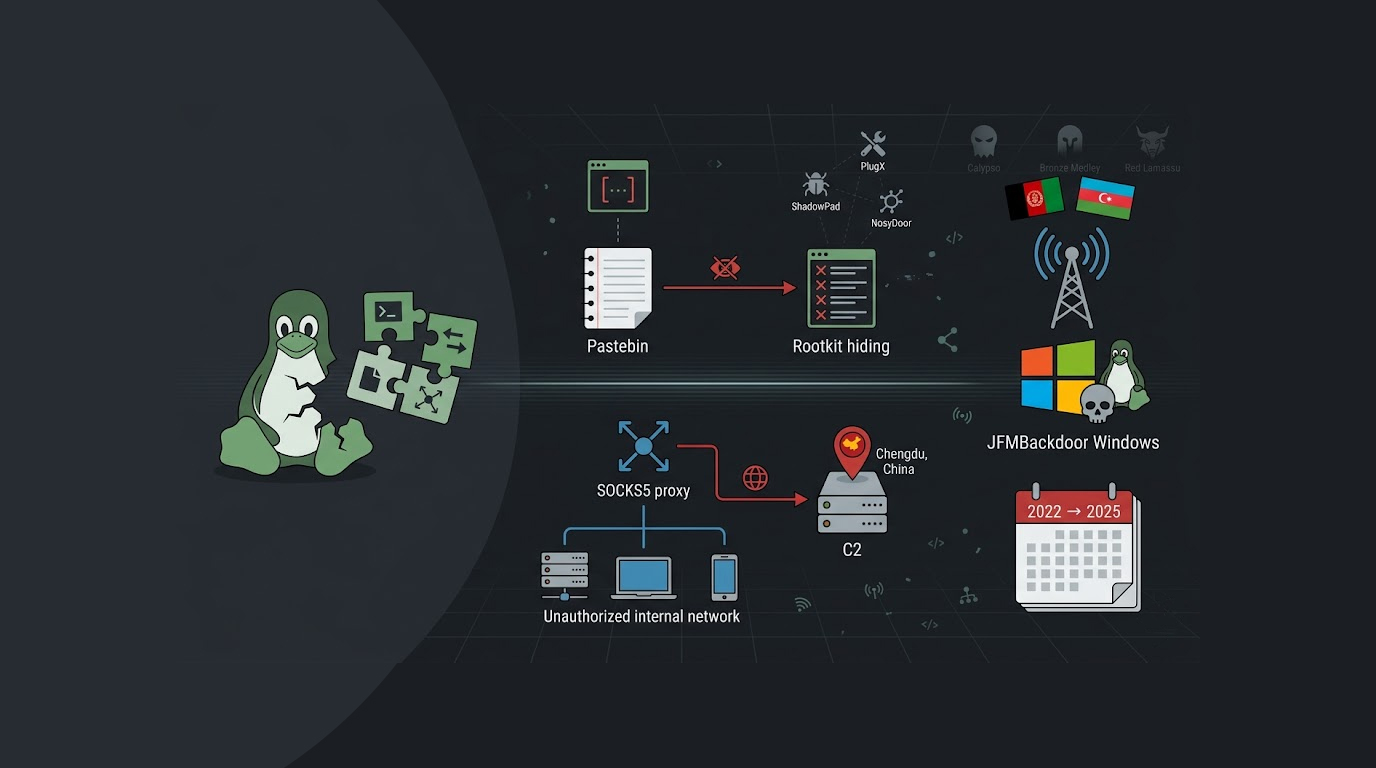
Showboat malware targets MT companies in the Middle East. It looks like was created by someone linked to Chinese-sponsored organizations and has been utili...
You finally did the right thing, you hired a penetration testing firm to find security holes before the criminals do.You expected a few minor issues, maybe...
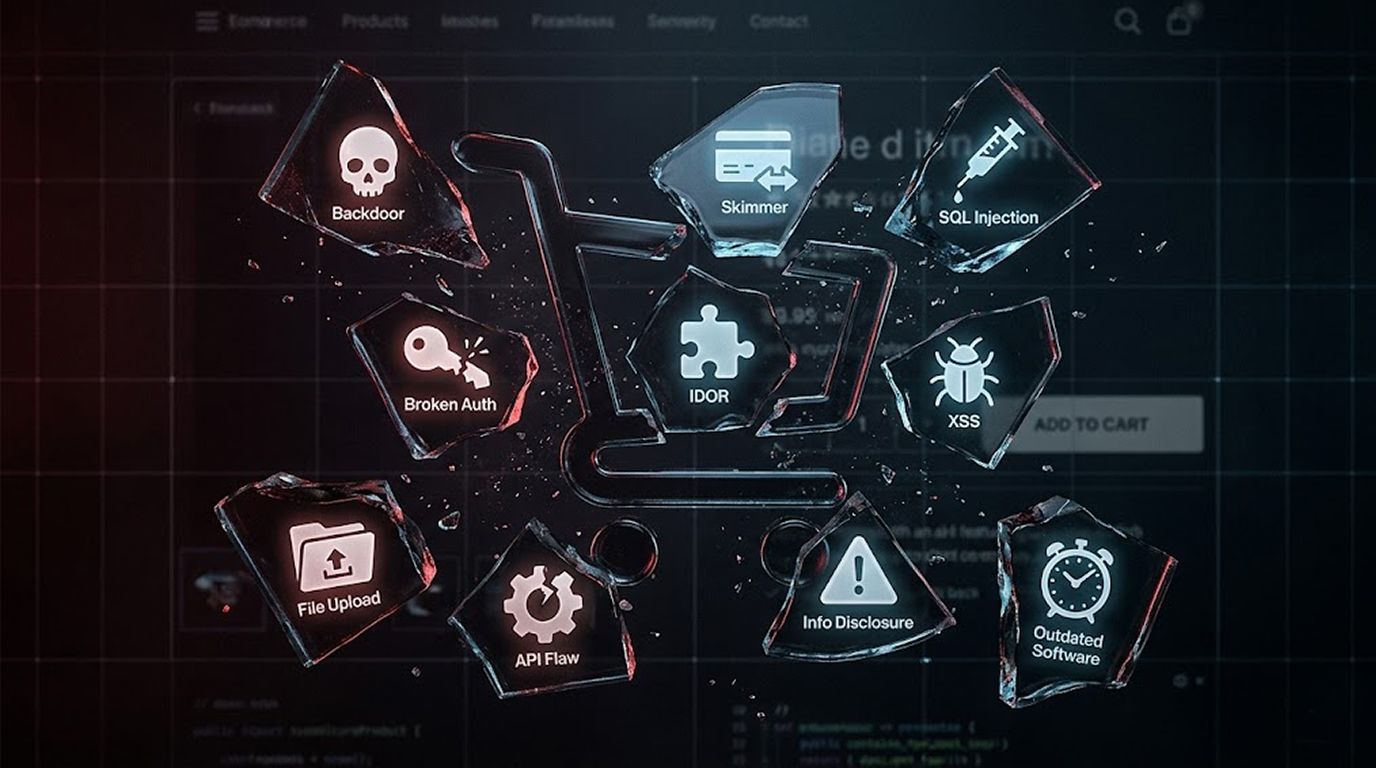
You spend thousands on marketing, you optimize your product pages, you run Facebook ads, you finally see sales rolling in.Then one morning you wake up to a...
Imagine waking up to find your email server locked. Your admin password does not work. Your users cannot send or receive messages.You did not click a phish...
You imagine a hacker. Dark room. Glowing screens. Fingers flying across a keyboard. Exploits. Zero-days. Firewalls crumbling.That is Hollywood. The realit...
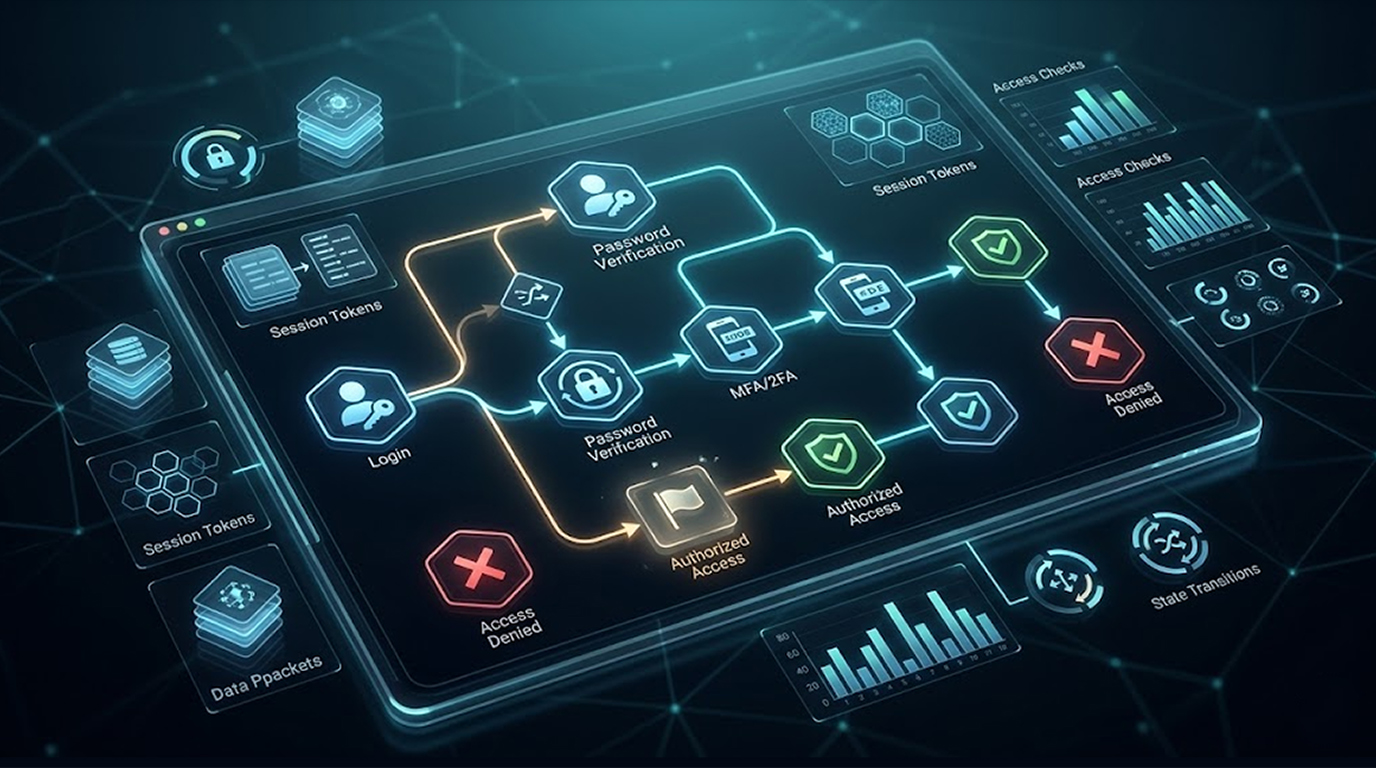
Authentication state attacks take advantage of weakness in how applications manage login sequences and states. Rather than using encryption or guessing a p...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067