Joomla Page Builder CK RCE via Arbitrary File Upload
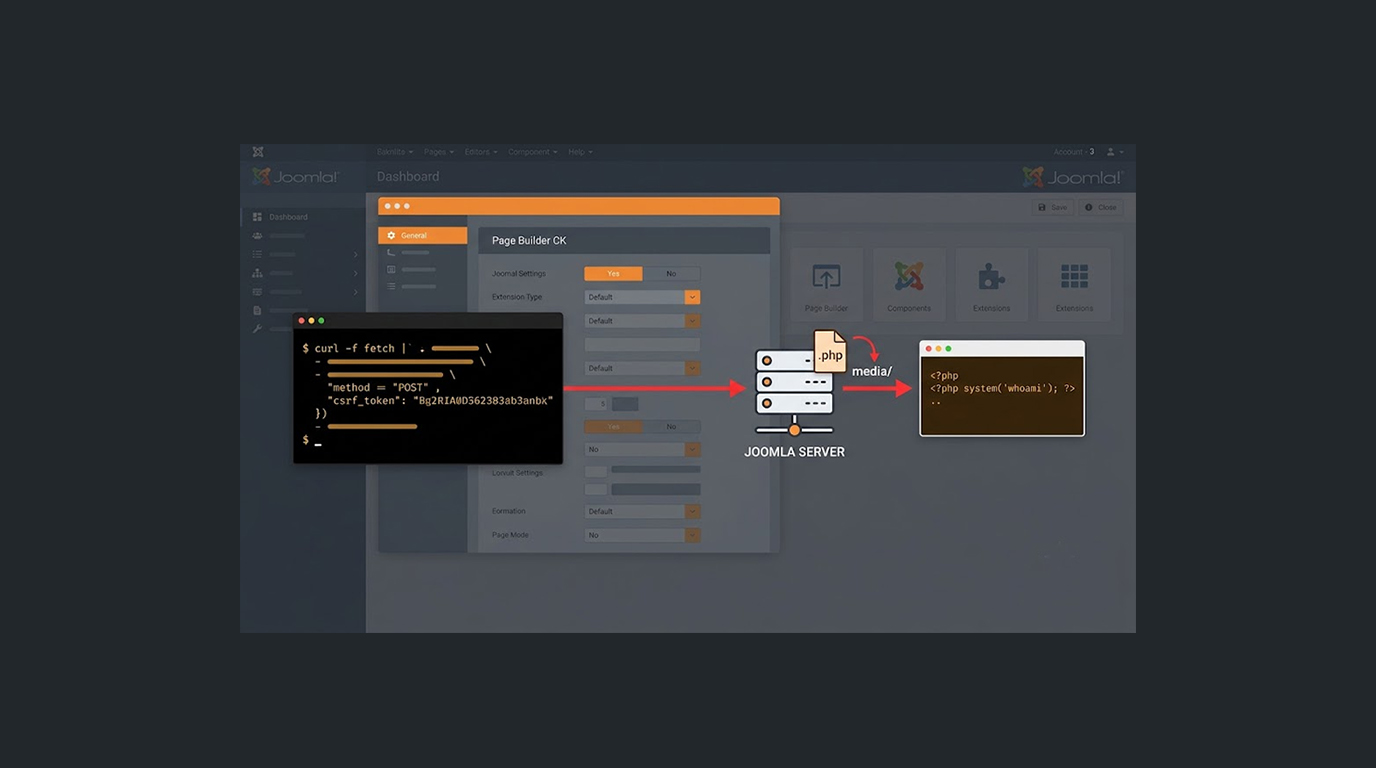
There is a serious vulnerability in Joomla Page Builder CK which enables an attacker without authentication to upload PHP files and run arbitrary code on t...
Found 199 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
There is a serious vulnerability in Joomla Page Builder CK which enables an attacker without authentication to upload PHP files and run arbitrary code on t...
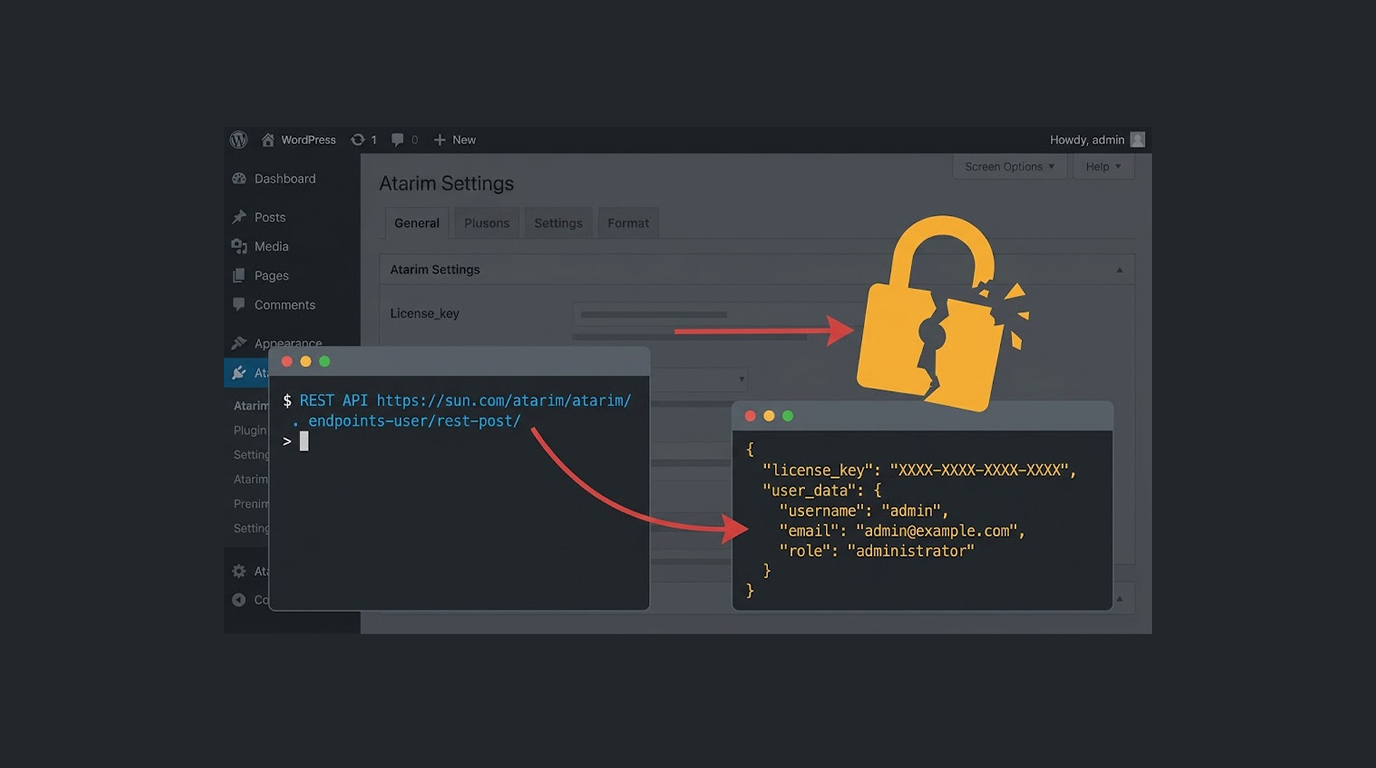
There exists a security vulnerability in the Atarim plug-in which exposes attackers to steal sensitive data without going through any kind of authenticatio...
You need to test your security. You have heard of black box and grey box penetration testing. But what do they actually mean? And which one is right for yo...
You have Kali Linux installed. You know the basics. But when you are in the middle of a penetration test, you need the right command at the right time. You...
This is a nightmare scenario for any business owner. One minute everything is fine, and the next, your website is either redirecting to spam pages or displ...
Is your business truly safe from a cyberattack? Many managers and entrepreneurs are somewhat ignorant toward digital resources, so many of them feel that...
When we talk about botnets, we usually mean armies of compromised devices slamming websites with traffic until they collapse. DDoS attacks, crypto mining t...
You check your email and see a message from your own address. The subject line is generic. The content is clearly spam. Someone is sending emails from your...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067