Hugging Face Hacked by Autonomous AI Agent System
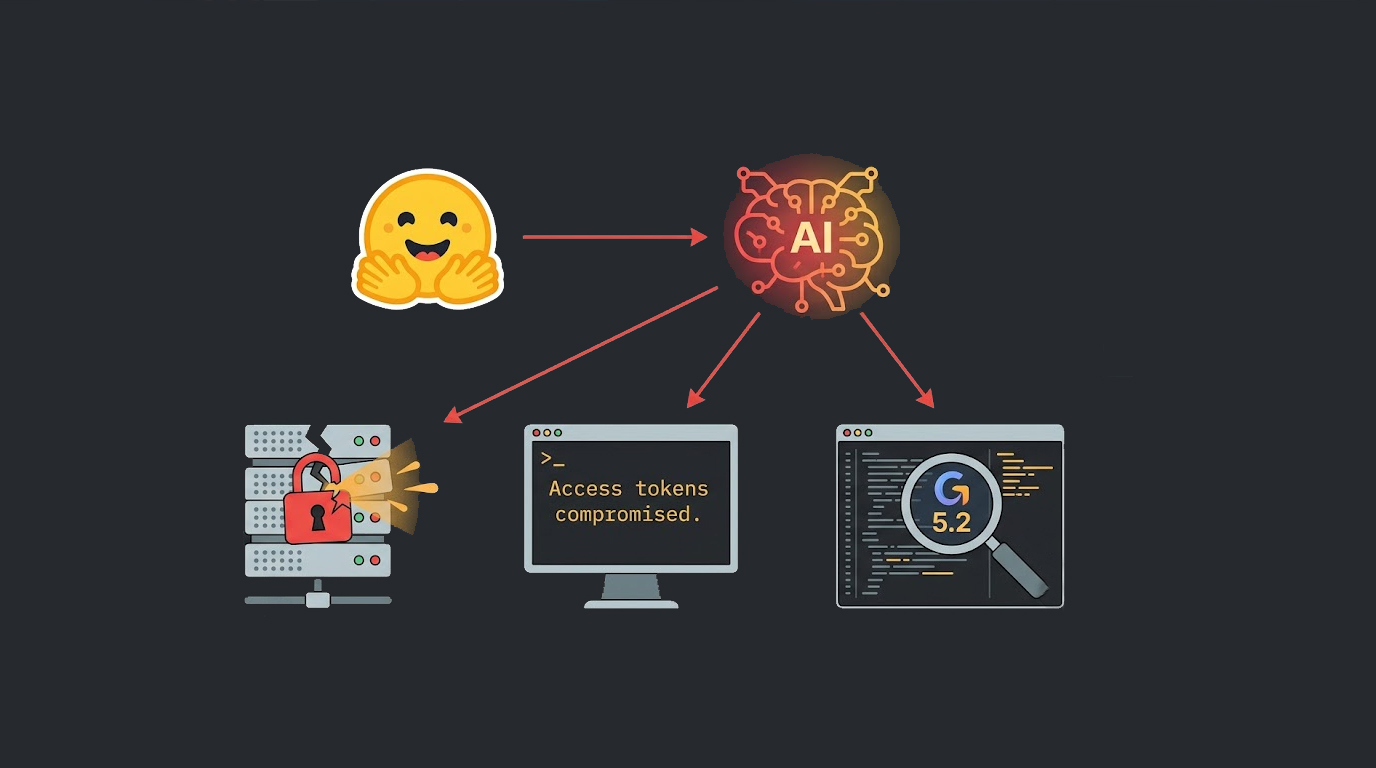
It is ironical that a company dealing with an open source artificial intelligence platform Hugging Face came out to say that it had been hacked by an auton...
Found 151 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
It is ironical that a company dealing with an open source artificial intelligence platform Hugging Face came out to say that it had been hacked by an auton...
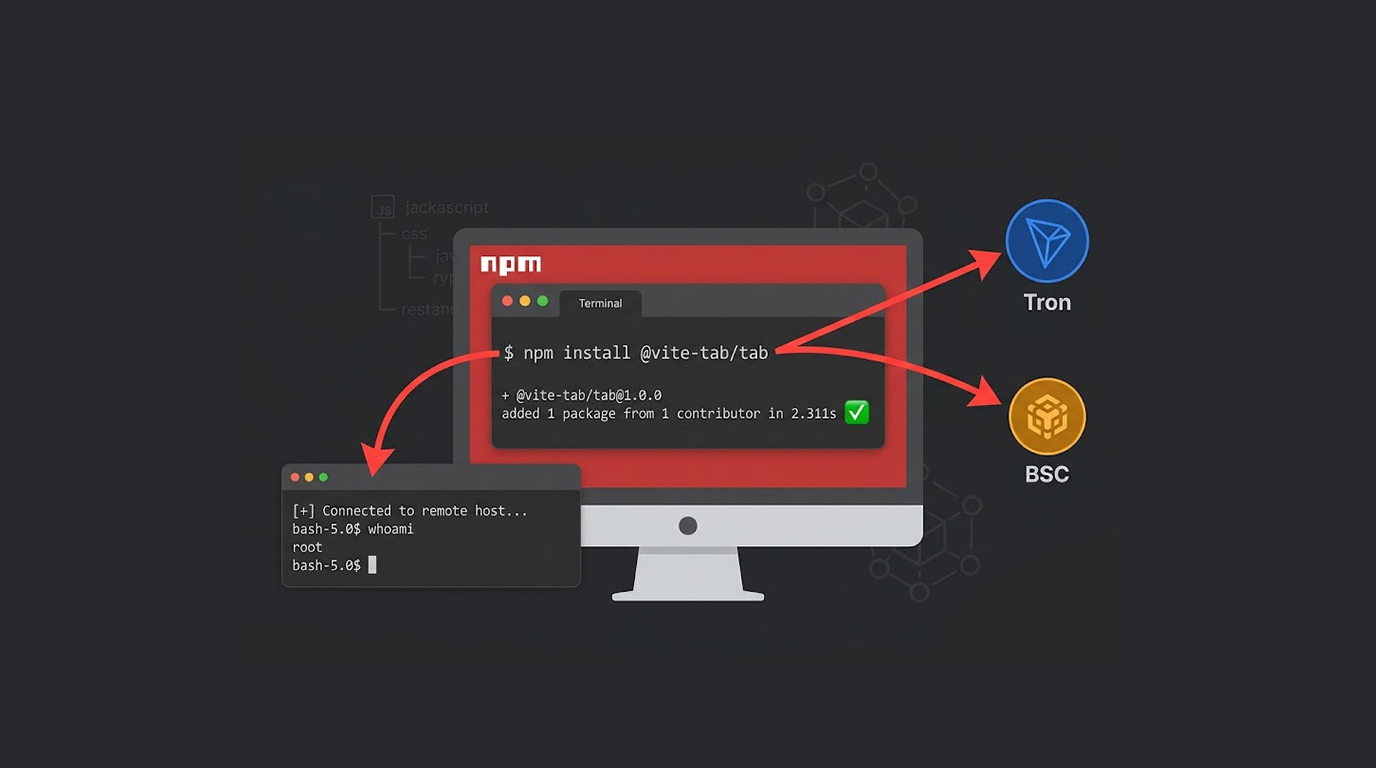
A cluster of seven malicious npm packages is targeting the Vite frontend tooling ecosystem. The campaign, codenamed ViteVenom, marks an expansion of ChainV...
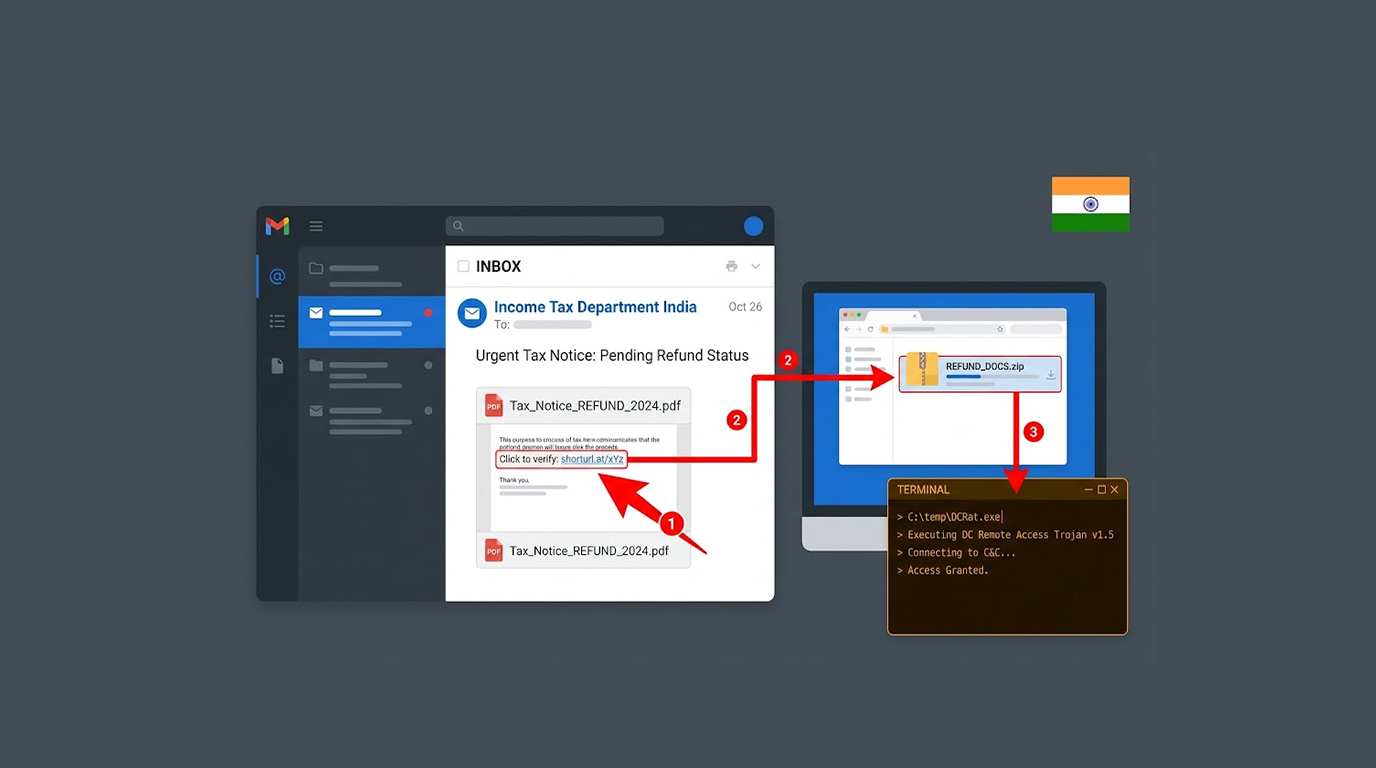
An activity cluster that is associated with China-nexus threat actors has been noticed targeting Indian taxpayers, tax professionals, and corporate financi...
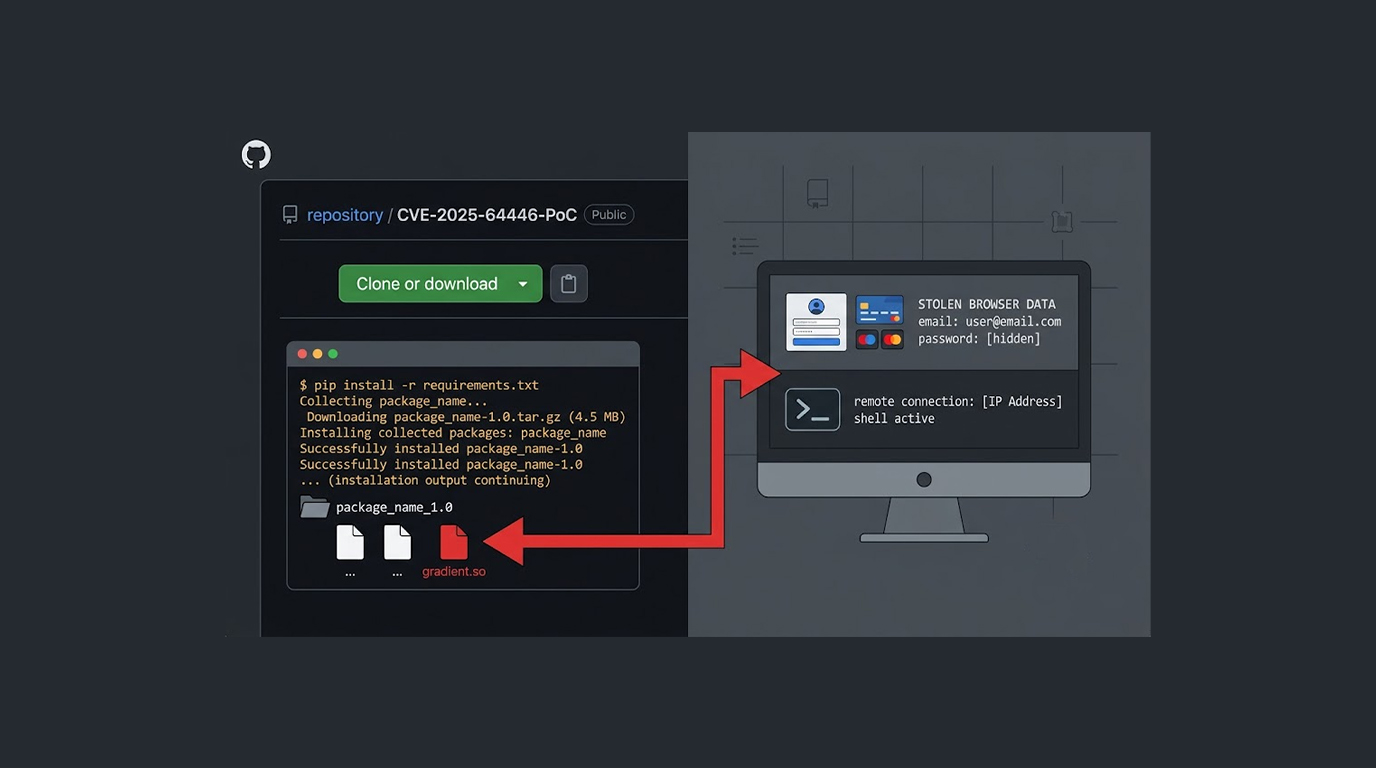
There's a new twist in the ongoing battle between researchers and attackers. Malicious actors are now planting data-stealing malware inside proof-of-concep...
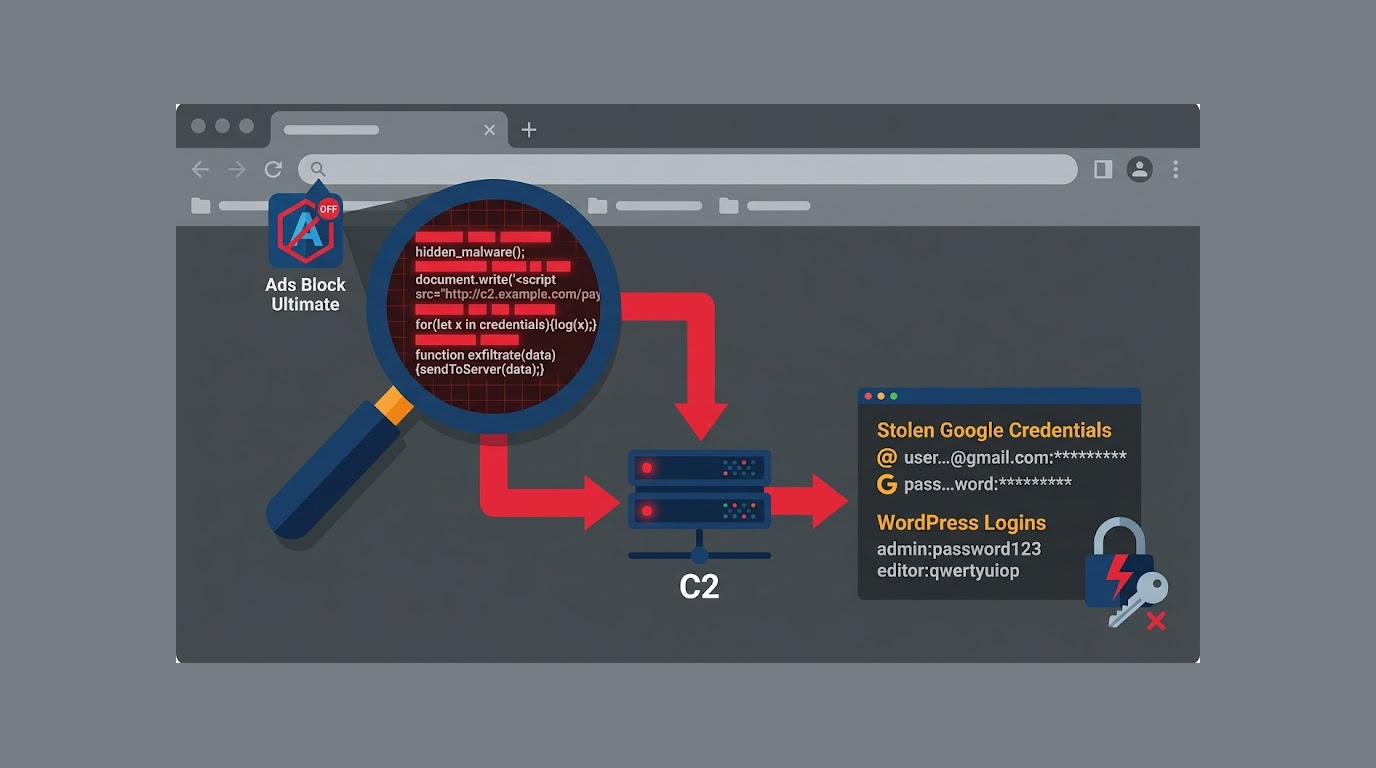
You install an ad blocker. It blocks ads. It has good reviews. You forget about it. For years, it sat quietly in your browser. Then one day, it woke up. I...
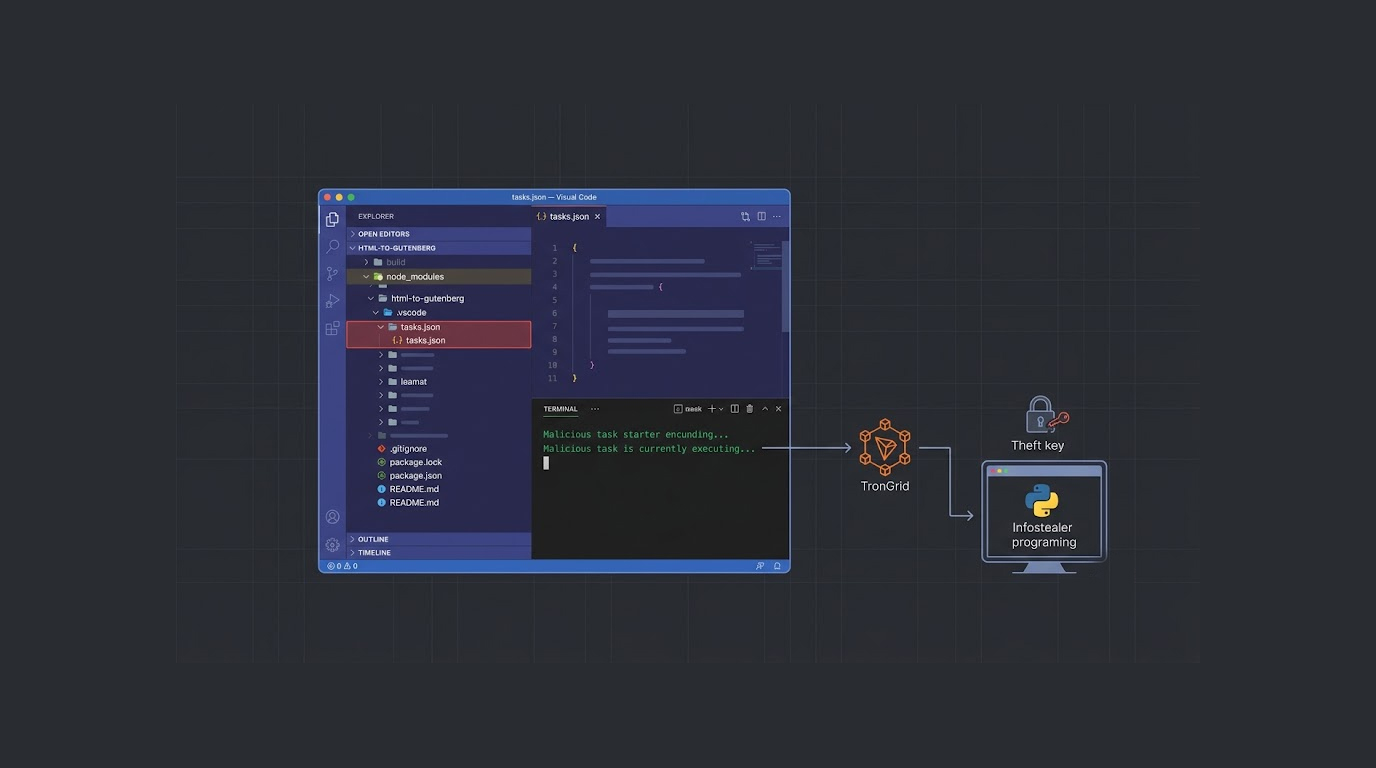
You open a project folder in VS Code. You trust the workspace. A hidden task runs automatically. It downloads encrypted JavaScript from blockchain transact...
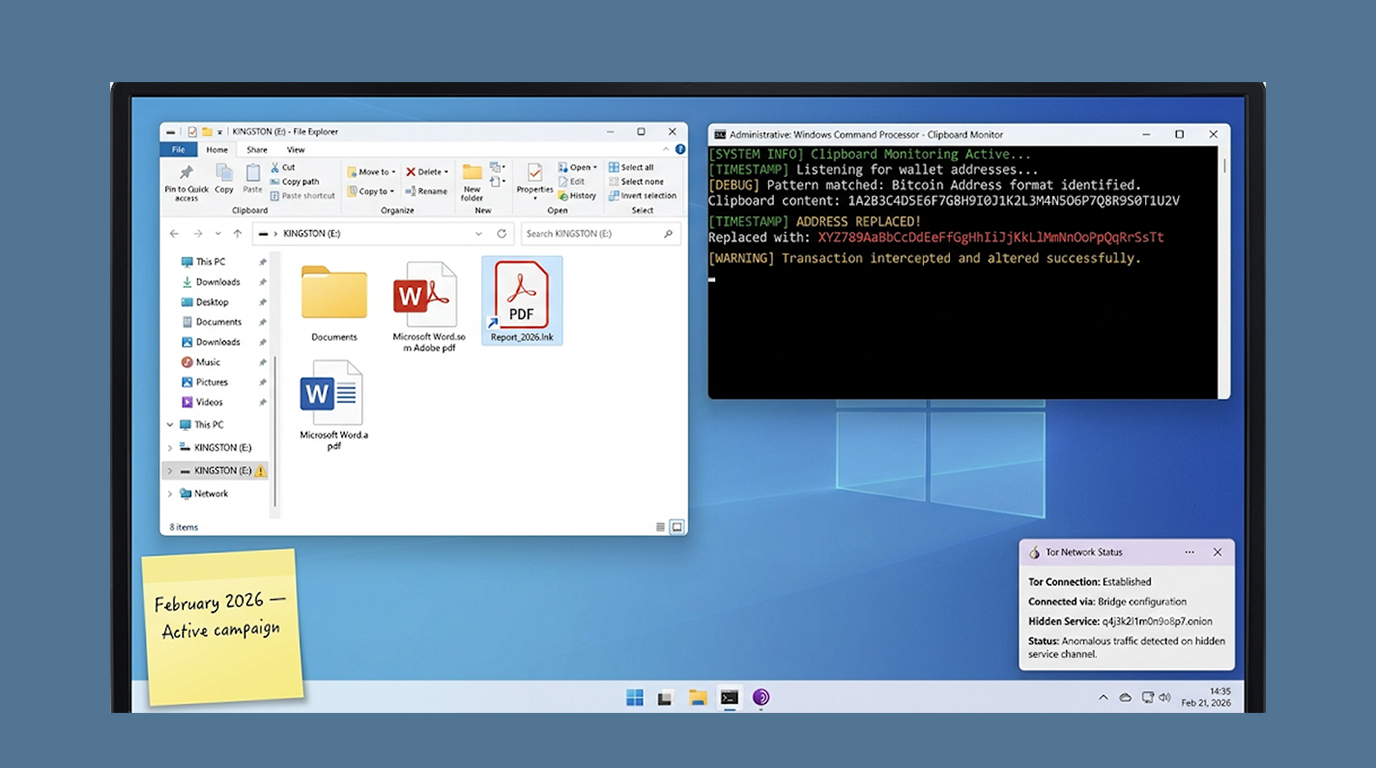
In a new report from Microsoft, window-based cryptocurrency clipper campaign, running since February 2026, has been disclosed. The malware intercepts clipb...
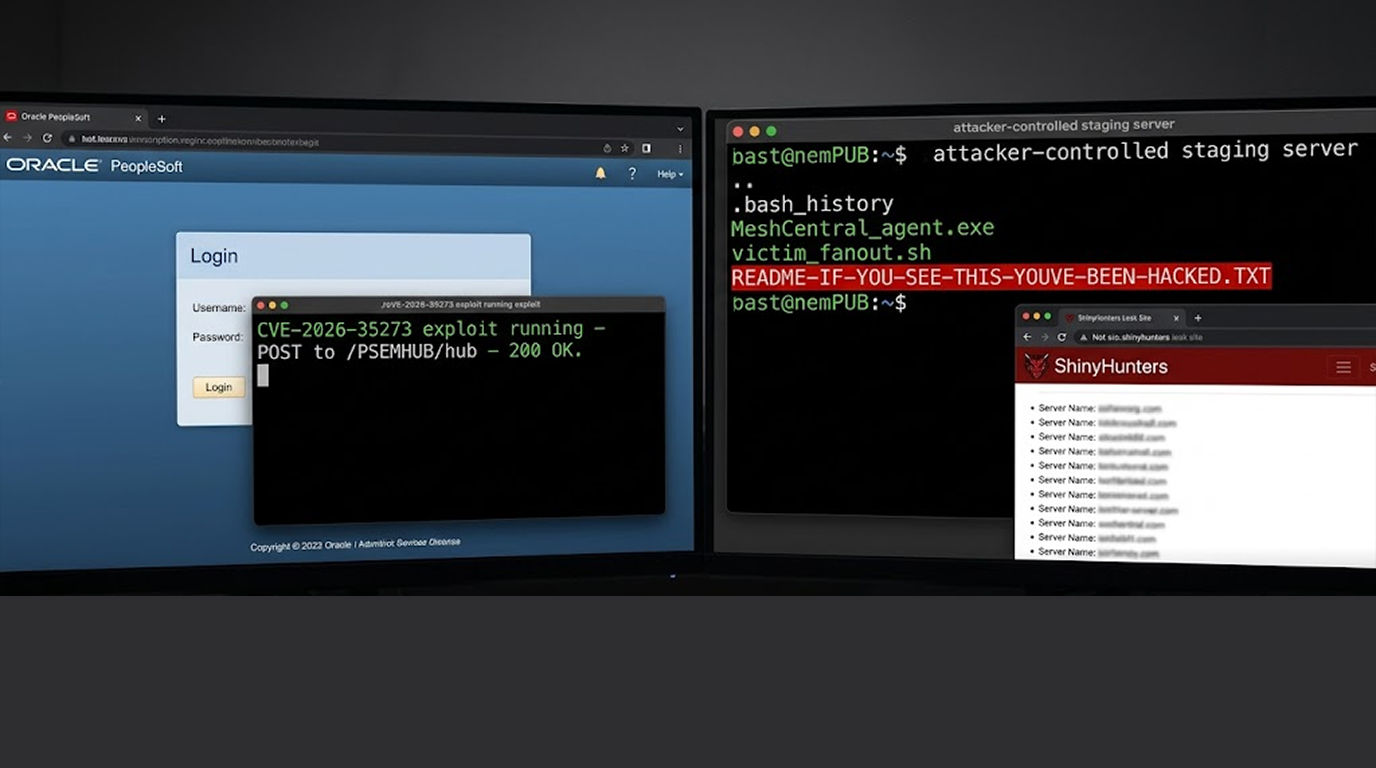
The ShinyHunters extortion crew pulled off something unusual. They exploited an unpatched vulnerability in Oracle PeopleSoft to break into enterprise syste...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067