Password Reset Poisoning, Host Header Attack
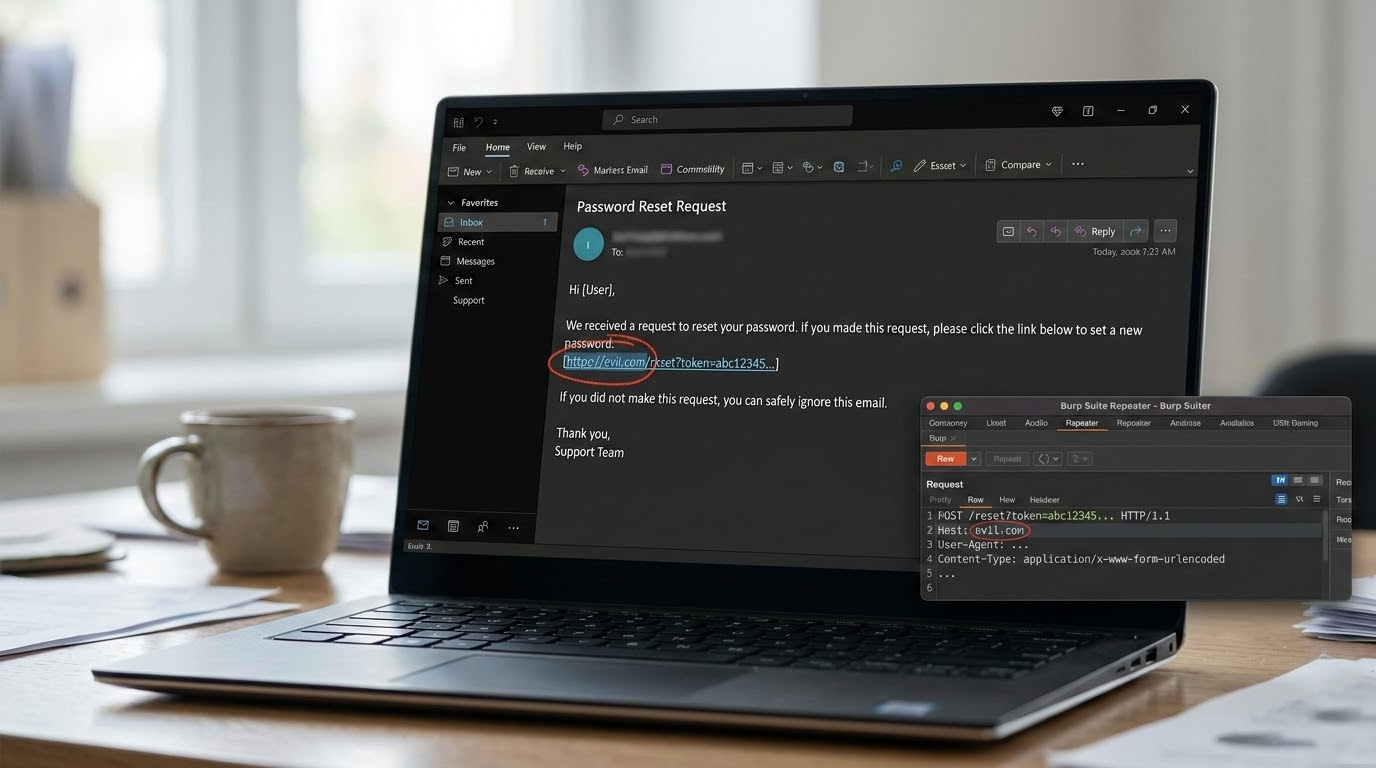
Password reset poisoning (also called Host header poisoning in reset flows) is one of those “old but gold” vulnerabilities that refuses to die....
Found 55 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Password reset poisoning (also called Host header poisoning in reset flows) is one of those “old but gold” vulnerabilities that refuses to die....
In 2026, the most damaging attacks rarely rely on exotic zero-days or nation-state tools. They exploit the same simple, long-standing gaps that companies k...
All three techniques are still responsible for a huge portion of account takeovers in 2026, but the balance has shifted noticeably over the last two years....
The fastest way attackers permanently destroy a brand’s entire social media presence isn’t hacking every account individually , it’s comp...
For executives and board members, credentials of a company are not only an IT issue; credential security is also a governance and risk management priority....
Mandiant (owned by Google) has reported seeing a troubling increase in these types of attacks - combining voice phishing (vishing) with fake login web page...
Advanced attacks rarely fail because an exploit did not work.They fail because something felt wrong.APT groups succeed by blending into normal operations.G...
Attackers are no longer trying to break systems first.They are trying to become users.Once identity is compromised, most defenses step aside.No exploit cha...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067