Securing Serverless Functions: What Developers Often Miss
Serverless is fast, simple, and powerful. You upload code, link it to a trigger, and it runs when needed. No servers to manage, no infrastructure headaches...
Found 39 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Serverless is fast, simple, and powerful. You upload code, link it to a trigger, and it runs when needed. No servers to manage, no infrastructure headaches...
Cybersecurity researchers have identified two high-severity vulnerabilities in Google's Vertex AI platform that could enable attackers to escalate privileg...
An advanced persistent threat (APT) group known as SideWinder, suspected to have ties to India, has ramped up its cyberattacks on high-profile organization...
The infamous cryptojacking group TeamTNT has likely resurfaced, launching a new campaign aimed at Virtual Private Server (VPS) infrastructures running the...
In today's evolving cybersecurity landscape, traditional network security models are no longer sufficient. The rise of cloud computing, remote work, and in...
A North Korea-affiliated cyber-espionage group, UNC2970, has been observed deploying sophisticated phishing lures to infiltrate entities in the energy and...
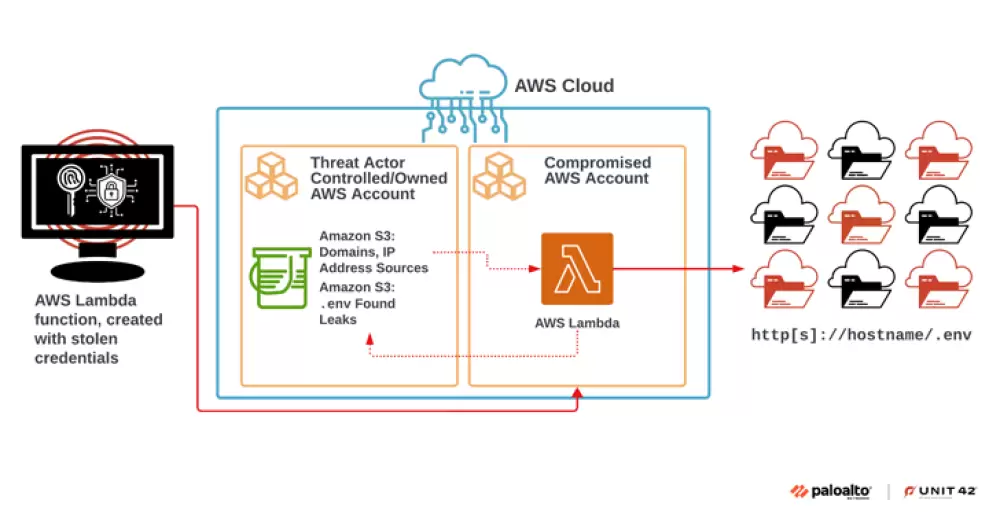
A large-scale extortion campaign has compromised various organizations by taking advantage of publicly accessible environment variable files (.env) that co...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067