Malicious npm Packages Spread Worm-Like Stealer & RATs
Cybersecurity firm Socket has uncovered an active supply-chain worm campaign codenamed SANDWORM_MODE that abuses at least 19 malicious npm packages to harv...
Found 792 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Cybersecurity firm Socket has uncovered an active supply-chain worm campaign codenamed SANDWORM_MODE that abuses at least 19 malicious npm packages to harv...
A new operation called Operation Olalampo has been launched by the Iranian APT group MuddyWater (aka Earth Vetala, Mango Sandstorm, and MUDDYCOAST) that ta...
One of the best ways to identify early-stage intruders (i.e., stalking while still being able to gain access to valuable information) is through the use of...
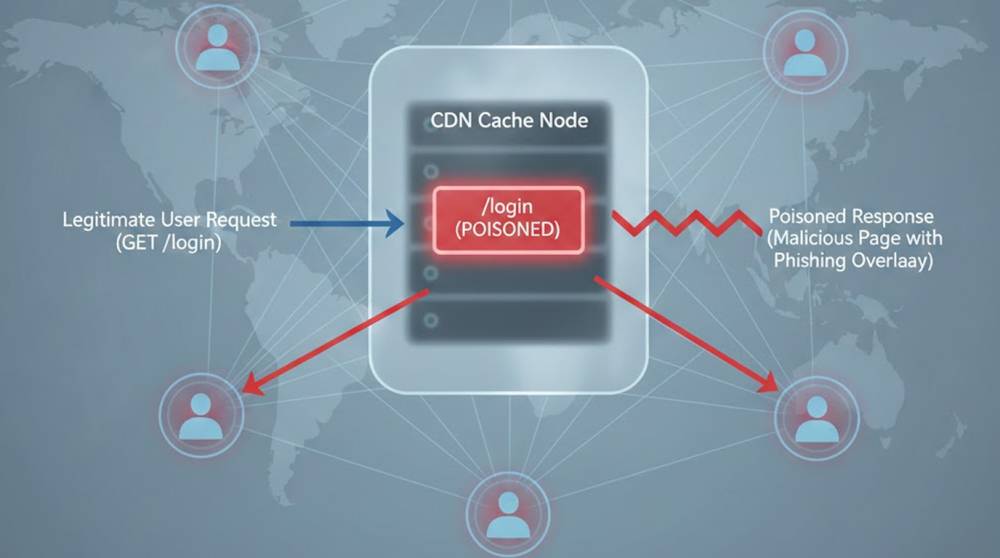
Web cache poisoning never really went away, but in 2026 it has become far more dangerous and far easier to execute than most security teams realize. The c...
In 2025–2026 one of the most powerful (and increasingly common) ways malware authors evade static detection and signature-based AV/EDR is letting a l...
According to Elastic Security Labs’ cybersecurity experts, they identified a highly advanced sophistication ClickFix campaign using legitimate websit...
Many security tools, remote-desktop solutions, banking apps, crypto wallets, trading platforms, and even some games now run “user presence” or...
Google Play Protect is Android's built-in malware scanner, it runs in the background, checks apps during install and periodically after, and can block or w...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067