Event ID 4104/4103: Catch Malicious PowerShell Scripts
Event ID 4103 (Module Logging) and 4104 (Script Block Logging) are two of the most valuable Windows security events for detecting malicious PowerShell acti...
Found 44 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Event ID 4103 (Module Logging) and 4104 (Script Block Logging) are two of the most valuable Windows security events for detecting malicious PowerShell acti...
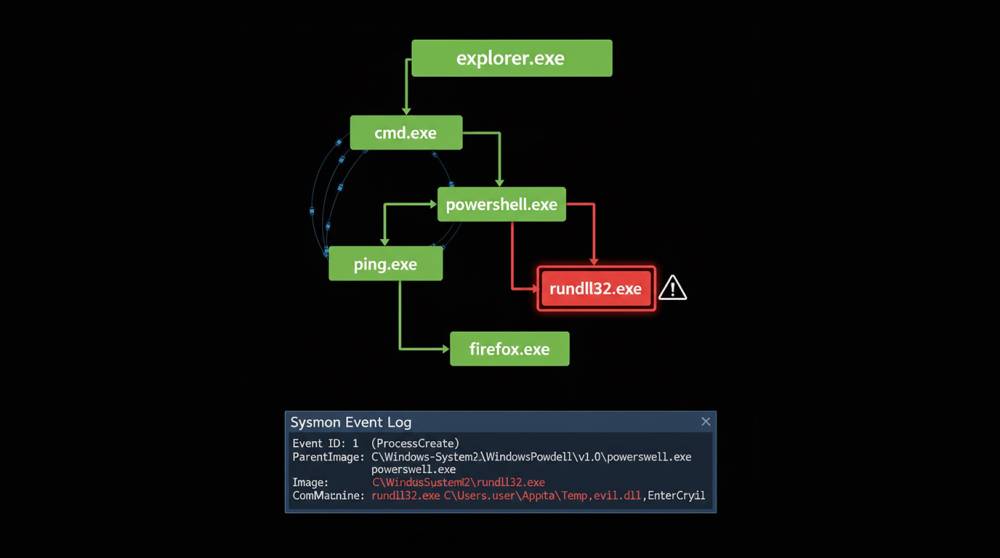
Process ancestry monitoring tracks the parent-child relationships between processes (who spawned what). This is one of the most reliable ways to detect liv...
Ethical hacking can only be conducted legally and safely. Building a home lab allows you to establish a safe and legal environment to simulate attacks, dev...
Red teams simulate real-world attacks ethically (with permission) to identify vulnerabilities before malicious actors do. Exploit tools automate discovery,...
The Iranian threat actor known as MuddyWater has been attributed to a new spear-phishing campaign targeting diplomatic, maritime, financial, and telecommun...
Getting In Is Just the StartInitial access gets all the attention.For red teams, that’s the warm-up. The real work begins after someone is inside.Th...
Security teams are now seeing real-world exploitation of the React2Shell vulnerability to deliver advanced Linux malware, including KSwapDoor and ZnDoor, a...
The threat actor known as Storm-0249 appears to be reinventing itself. Once known mainly as an initial access broker, the group is now leaning into more ad...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067