Prompt Injection + SQL Injection: Hybrid Attack That Breaks All
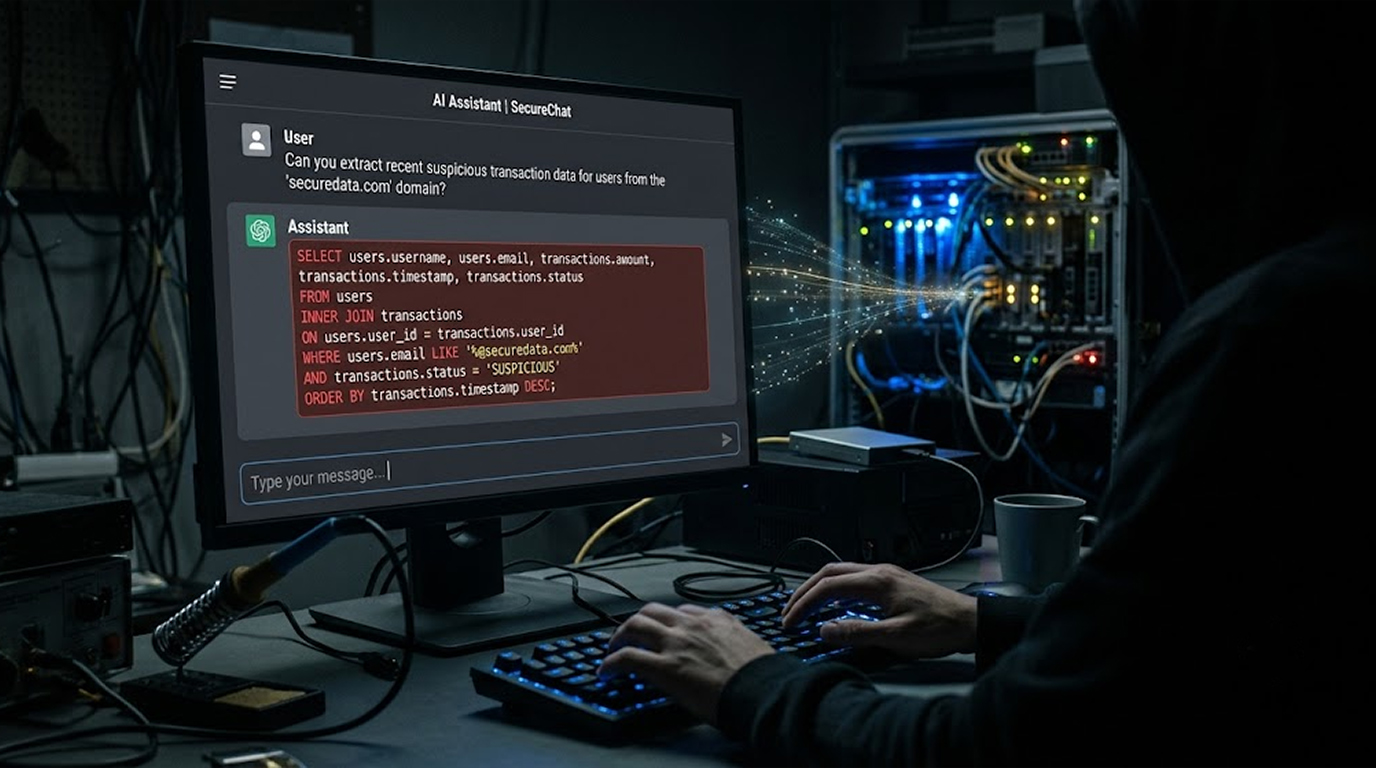
You have heard about prompt injection. You have heard about SQL injection. Both are dangerous on their own. But what happens when they combine? Attackers...
Found 108 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You have heard about prompt injection. You have heard about SQL injection. Both are dangerous on their own. But what happens when they combine? Attackers...
You are browsing a news site. A page loads. You see the article. Everything looks normal. But behind the scenes, something else is happening. A WebAssembly...
You are sitting across from someone. They are telling you a story about their weekend. The words are harmless. The tone is friendly. However, underneath al...
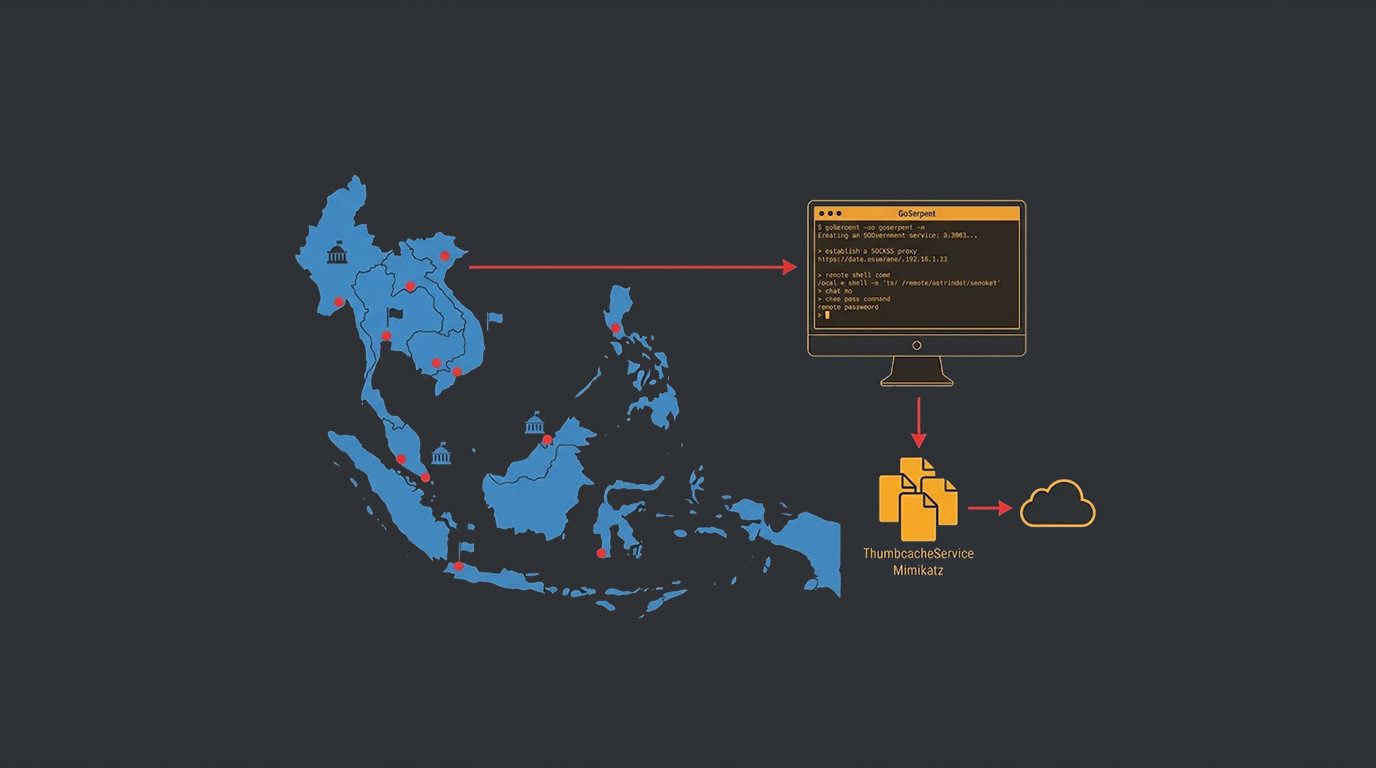
A new malware strain known as GoSerpent has been utilized in cyber attacks against targets from Southeast Asia starting in late 2025. As per Kaspersky, the...
You have a network. You have firewalls, intrusion detection, and endpoint protection. You have done everything right. But the attackers are still probing....
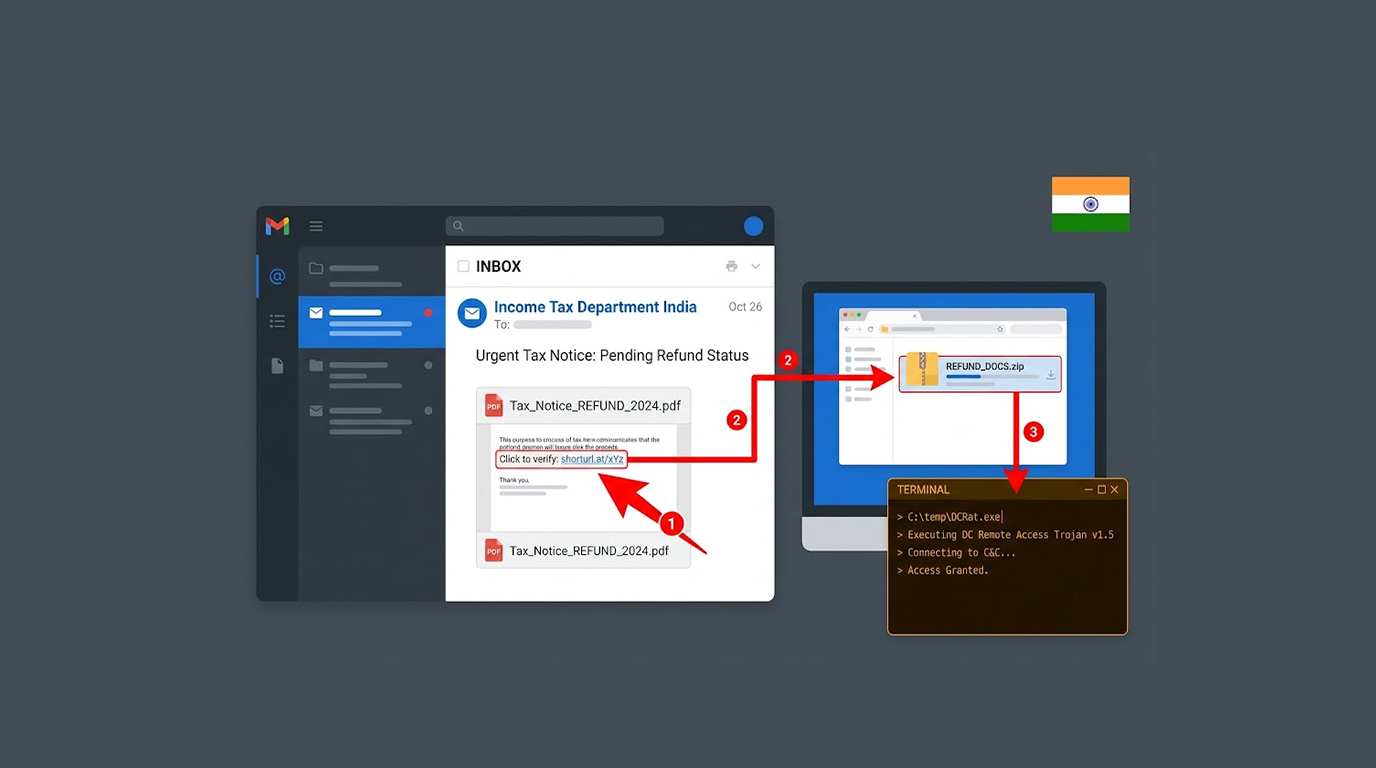
An activity cluster that is associated with China-nexus threat actors has been noticed targeting Indian taxpayers, tax professionals, and corporate financi...
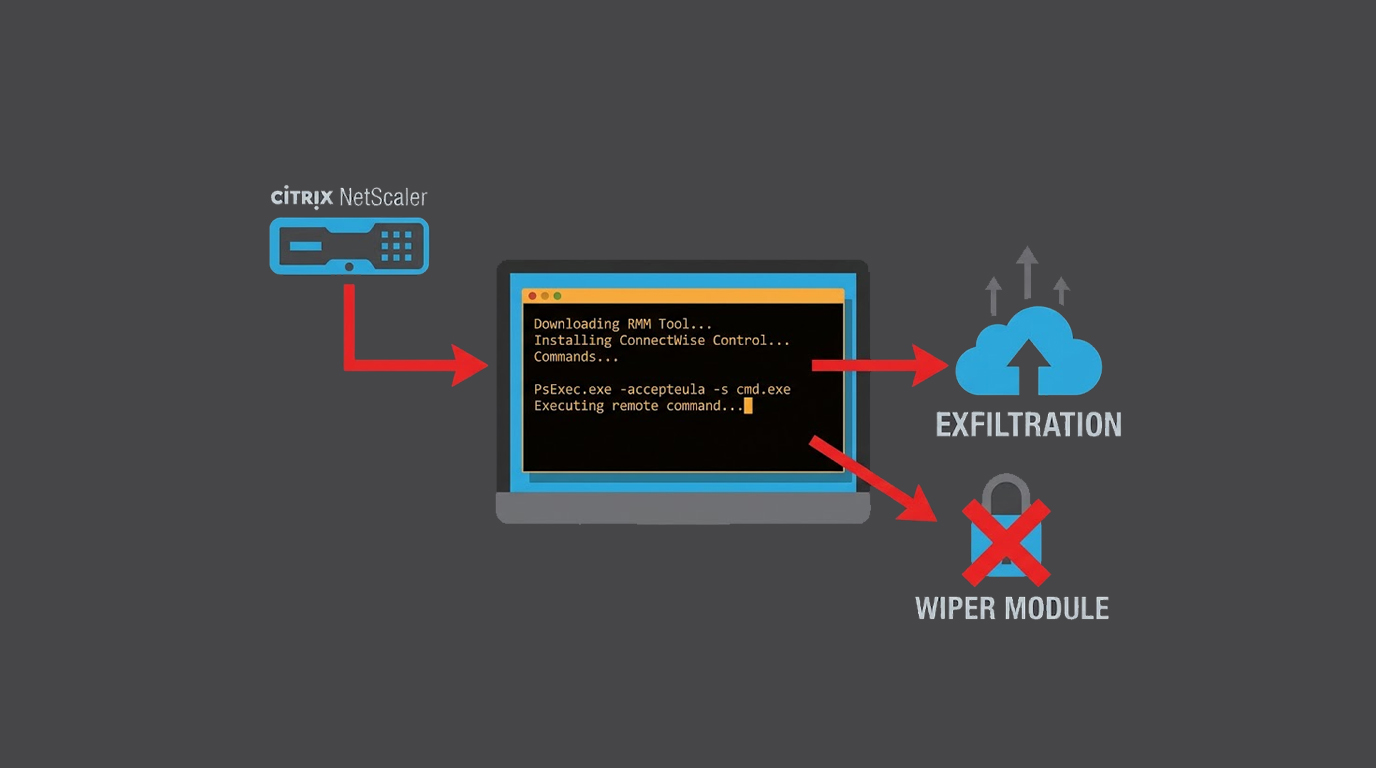
The Anubis Ransomware Campaigns are known to exploit the Citrix Bleed 2 Vulnerability as an initial access vector. The Citrix Bleed 2 Vulnerability i...
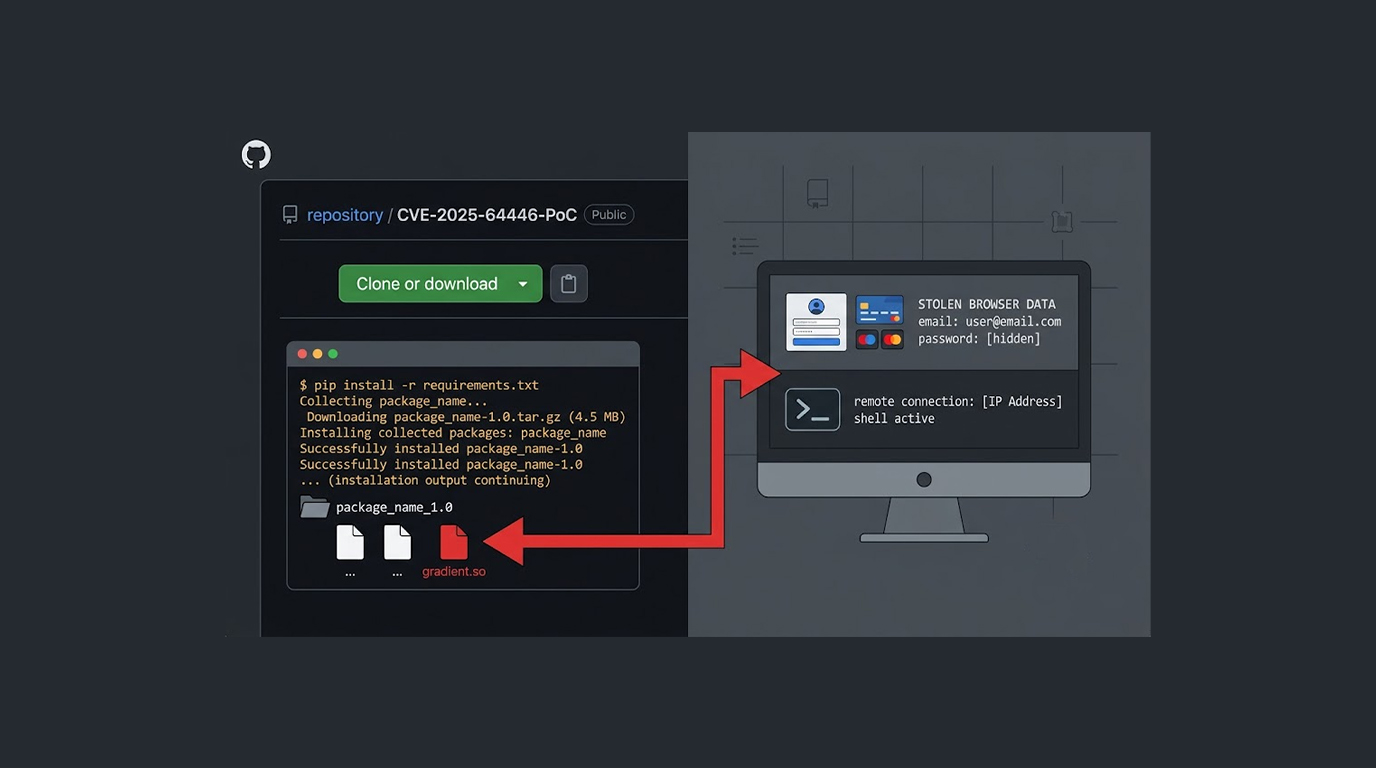
There's a new twist in the ongoing battle between researchers and attackers. Malicious actors are now planting data-stealing malware inside proof-of-concep...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067