Ransomware: Pull Cable or Trust EDR?
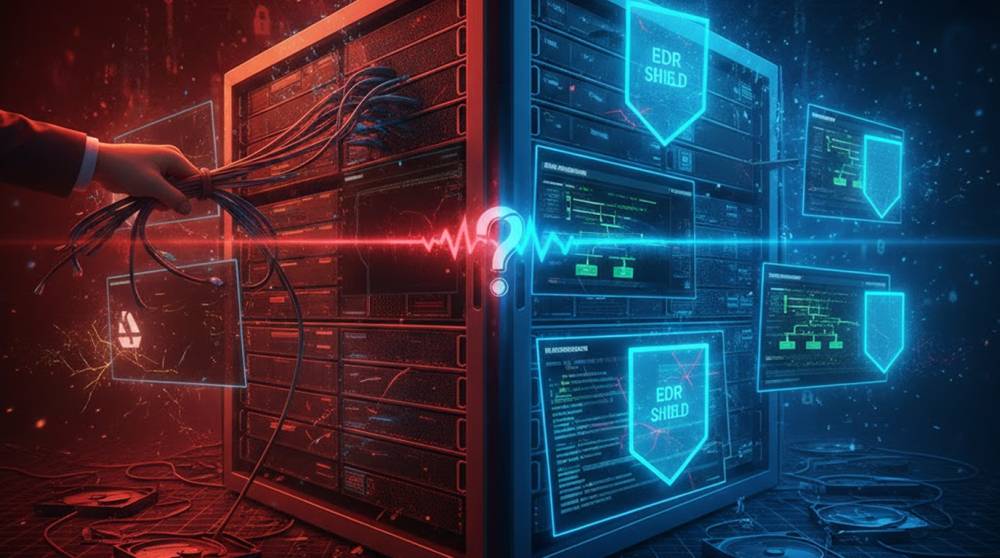
When you see clear signs that ransomware is spreading inside your network (multiple machines encrypting files, ransom notes appearing, abnormal process cha...
Found 33 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
When you see clear signs that ransomware is spreading inside your network (multiple machines encrypting files, ransom notes appearing, abnormal process cha...
Ivanti disclosed and patched two high-severity (CVSS 9.8) code injection vulnerabilities (CVE-2026-1281 and CVE-2026-1340) affecting Ivanti Endpoint Manage...
You can’t patch what you don’t know exists. Zero-day exploits, unknown vulnerabilities, and novel attack chains are the nightmare scenario for...
Most damage from a hack doesn’t happen instantly.It happens because people don’t realize what’s happening, or they freeze.The first 10 mi...
Most serious incidents do not begin with malware or exploits.They begin with a valid login.Once attackers authenticate, their objective changes.The questio...
Most security incidents unfold faster than expected.An account is accessed. A system is misused. Data is copied or altered.The actual intrusion often takes...
When I teach a class or walk into a red-team briefing, someone always asks the same thing - “so, what exactly is a payload?” It’s one of...
As robotics become more integrated into critical operations, the potential for cyberattacks on these systems grows. Robotic systems are not only complex bu...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067