Cisco Secure Firewall DoS Vulnerability Under Active Attack
A new vulnerability affecting Cisco Secure Firewall ASA and FTD software is currently being exploited in the wild, according to Cisco. The flaw allows unau...
Found 78 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A new vulnerability affecting Cisco Secure Firewall ASA and FTD software is currently being exploited in the wild, according to Cisco. The flaw allows unau...
Metabase has warned that a maximum-severity security flaw impacting its business intelligence and data visualization software has been exploited in the wil...
A critical severity vulnerability in the Progress Kemp LoadMaster load balancer has been added to CISA’s Known Exploited Vulnerabilities list. The ad...
Entra ID researcher Dirk-jan Mollema has uncovered a technique that allows malware already running on a compromised Windows machine to silently use a victi...
Cisco has rolled out updates to address multiple critical security vulnerabilities impacting Catalyst SD-WAN and IOS XE Software. The patches are part of a...
Attackers broke into an organization's Oracle database through a SQL injection flaw in a public-facing web application. Then they installed a post-exploita...
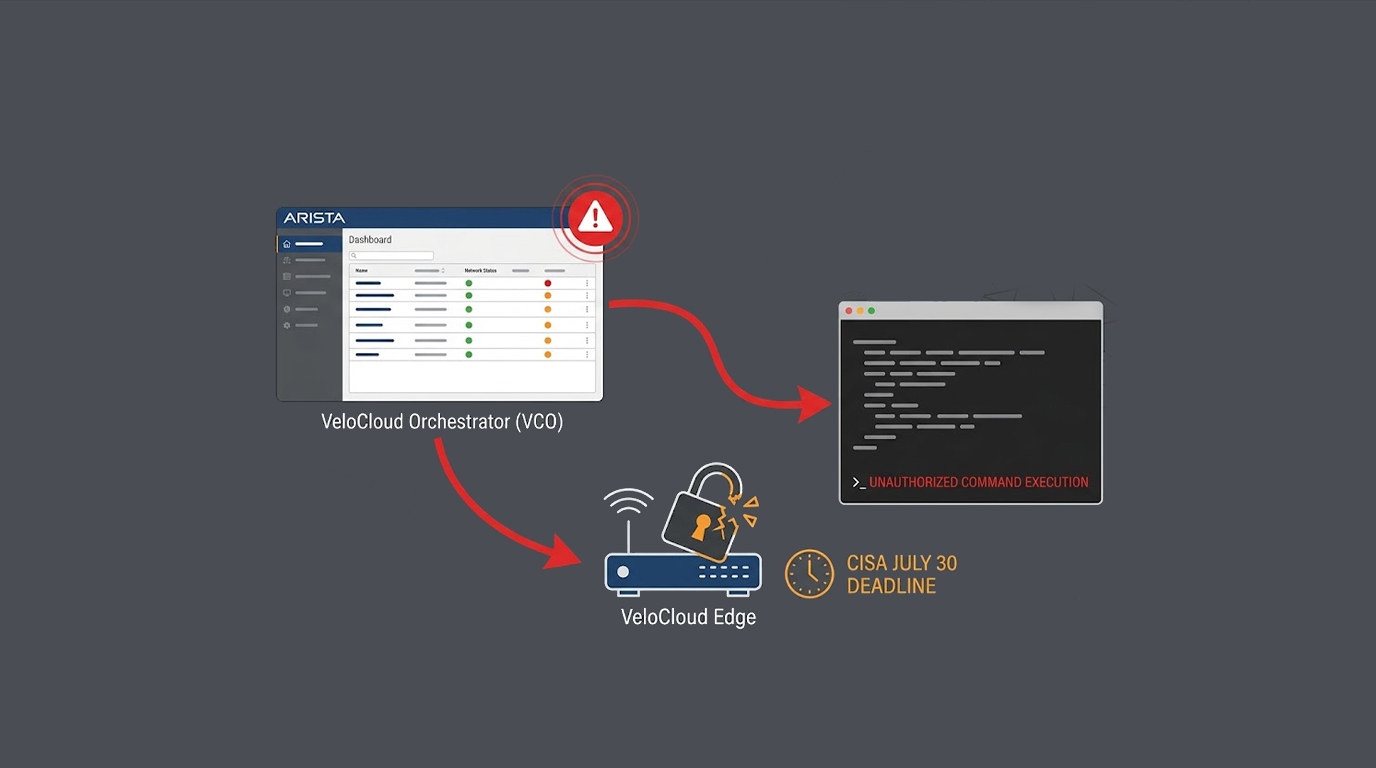
If you are running an on-premises version of Arista VeloCloud Orchestrator, you need to stop what you are doing and check your systems right now. A maximum...
You have 40,000 new vulnerabilities reported in a single year. Your security team can realistically patch maybe 5% of them. The rest will sit there, unpatc...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067