Why Most Businesses Fail Their First Penetration Test (Top Reasons)
You finally did the right thing, you hired a penetration testing firm to find security holes before the criminals do.You expected a few minor issues, maybe...
Found 56 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You finally did the right thing, you hired a penetration testing firm to find security holes before the criminals do.You expected a few minor issues, maybe...
Banner grabbing is one of the oldest tricks in reconnaissance, and in 2026 it remains ridiculously effective, especially on internet-facing servers. You li...
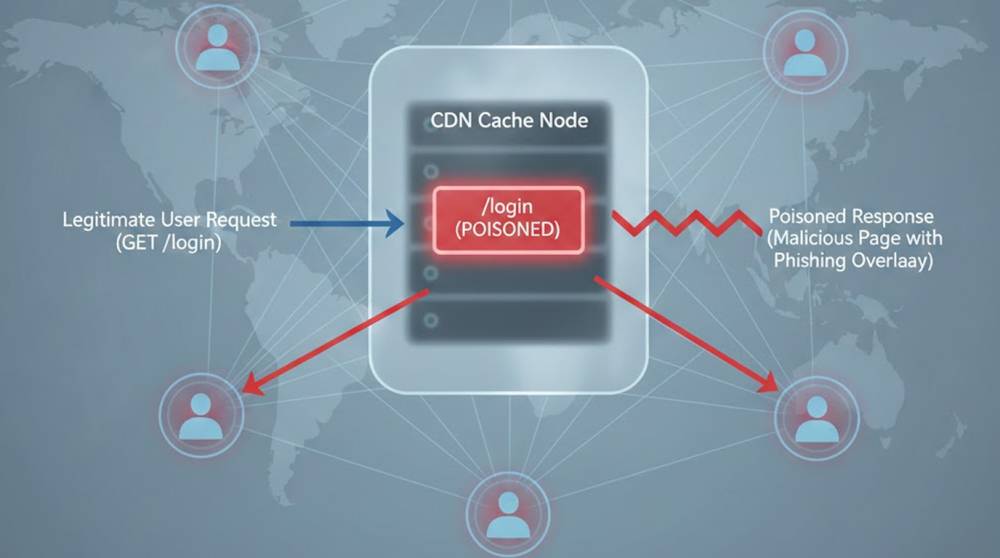
Web cache poisoning never really went away, but in 2026 it has become far more dangerous and far easier to execute than most security teams realize. The c...
In 2025–2026 one of the most powerful (and increasingly common) ways malware authors evade static detection and signature-based AV/EDR is letting a l...
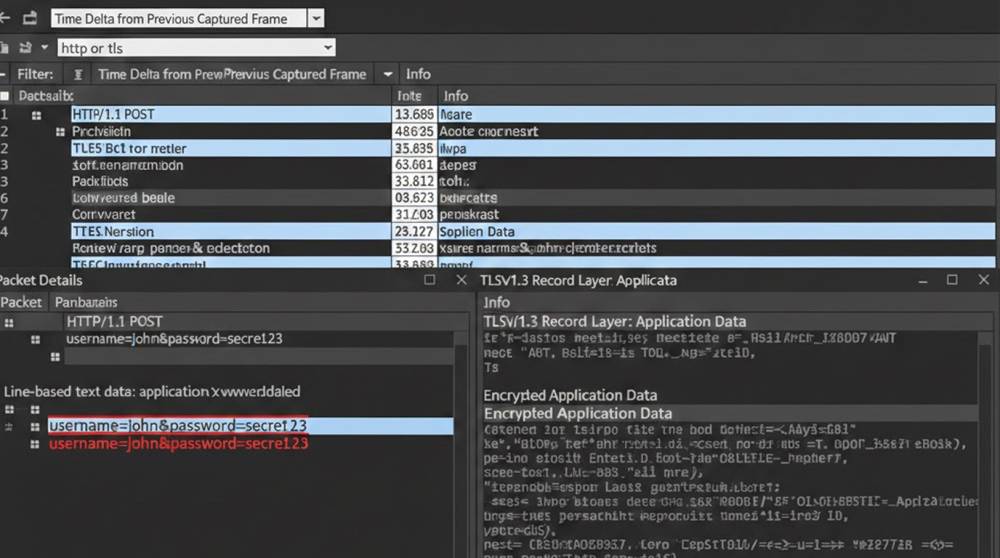
When you capture network traffic with Wireshark, the difference between plaintext (HTTP) and encrypted (HTTPS/TLS) becomes very obvious and very usef...
GPO (Group Policy Object) is one of the most effective, but also underused, tools for providing security to Windows networks as well as providing centraliz...
A serious remote code execution vulnerability (CVE-2025-32023) was identified in Redis HyperLogLog (HLL) for all versions greater than (>=) 8.0.0 but le...
Versions of Docker Desktop before 4.44.3 (released on 20 August 2025) had a serious vulnerability that could enable an attacker to use Linux containers to...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067