Dangling-Byte Attack: New OWASP Threat Changes Web Security
This is one way an attacker can use to exploit websites. The dangling-byte technique is a new and innovative approach to HTTP desync that enables an attack...
Found 91 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
This is one way an attacker can use to exploit websites. The dangling-byte technique is a new and innovative approach to HTTP desync that enables an attack...
PortSwigger's James Kettle has built an AI-assisted research system called HTTP Terminator that generated and proved new HTTP desynchronization techniques...
An agent working on Anthropic’s Claude Mythos 5 used up 34 hours get to the malware dropper with an actual open source project during an AI cyb...
Picture this. You check into a hotel, connect to the Wi-Fi, and see a browser update prompt. It looks legitimate. You click it, install the update, and go...
You right-click a file, you hit delete, and nothing happens. Or worse, you get an error message that makes absolutely no sense. "File in use." "Access deni...
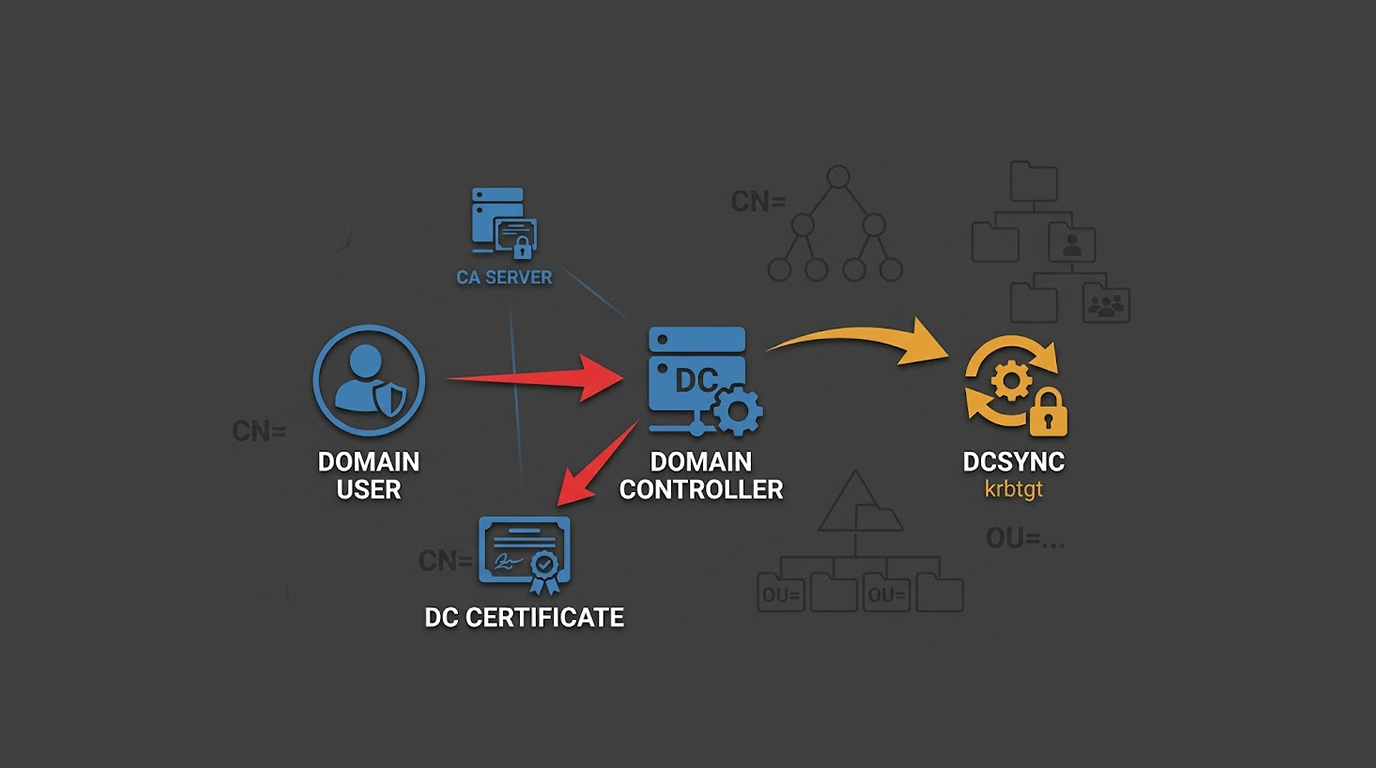
Let me paint you a picture. A regular employee with basic domain user privileges, no admin rights, no special access can walk away with a certificate that...
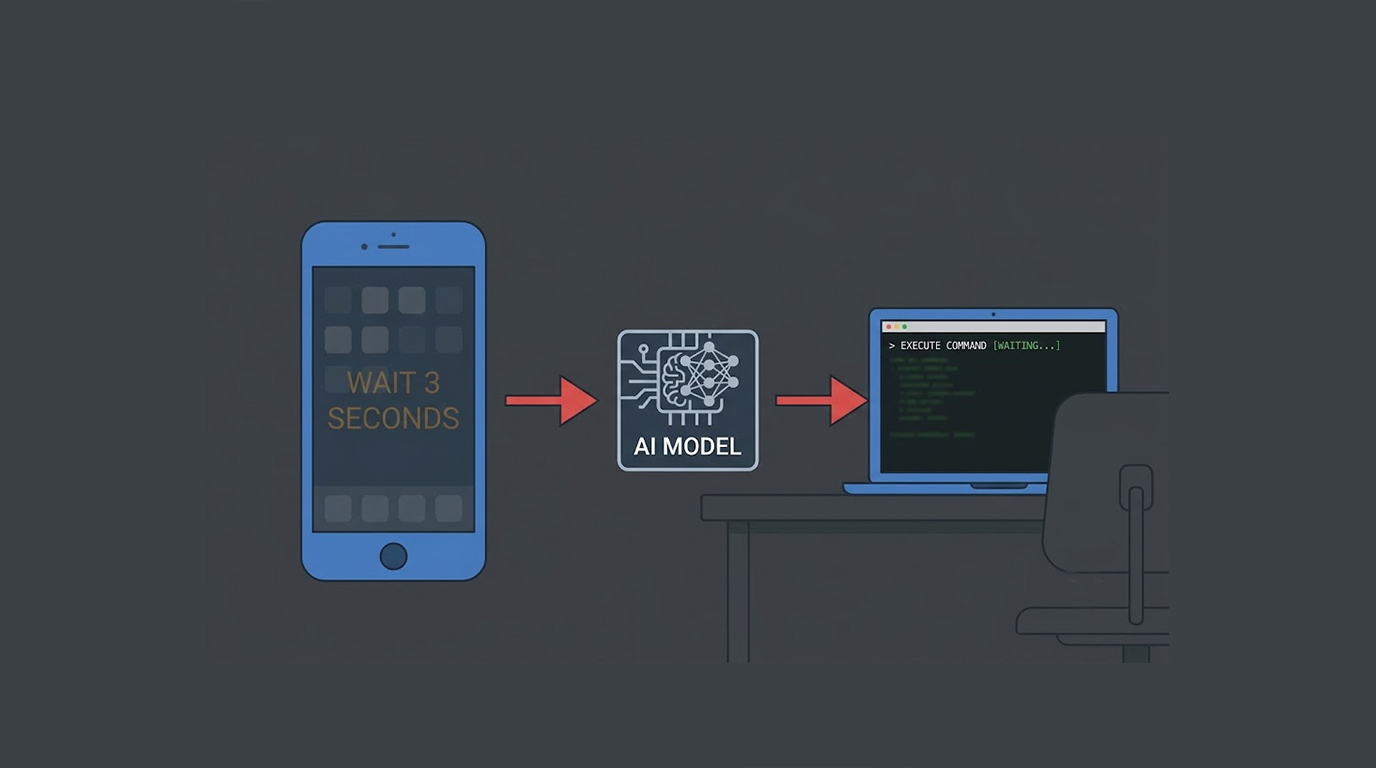
An Android app that can overlay other windows and write to shared storage can feed instructions into the artificial intelligence agent running the phone th...
You are in a coffee shop typing on your laptop. Music plays softly from the speakers above. You do not think twice about it. It is just background noise....
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067