How Developers Can Defend Against SQL Injection Attacks
SQL Injection (SQLi) is one of those vulnerabilities that just refuses to die. Even though it’s been around for over two decades, penetration testers...
Found 31 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
SQL Injection (SQLi) is one of those vulnerabilities that just refuses to die. Even though it’s been around for over two decades, penetration testers...
If you’ve ever worked with websites or web apps, you’ve probably heard the term SQL injection (SQLi) tossed around. It’s one of those vul...
SQL injection isn’t new. In fact, it’s been around for decades. Yet somehow, time and again, we see businesses falling into the same trap. Why?...
SQL injection (SQLi) is one of the most dangerous web application vulnerabilities, allowing attackers to manipulate databases and extract sensitive data. E...
Security researchers are raising alarms about an updated version of the Python-based NodeStealer malware. This iteration not only harvests sensitive inform...
A Chinese-speaking threat actor, known as Earth Lusca, has been linked to a recent cyber attack involving a new backdoor called KTLVdoor, targeting an unna...
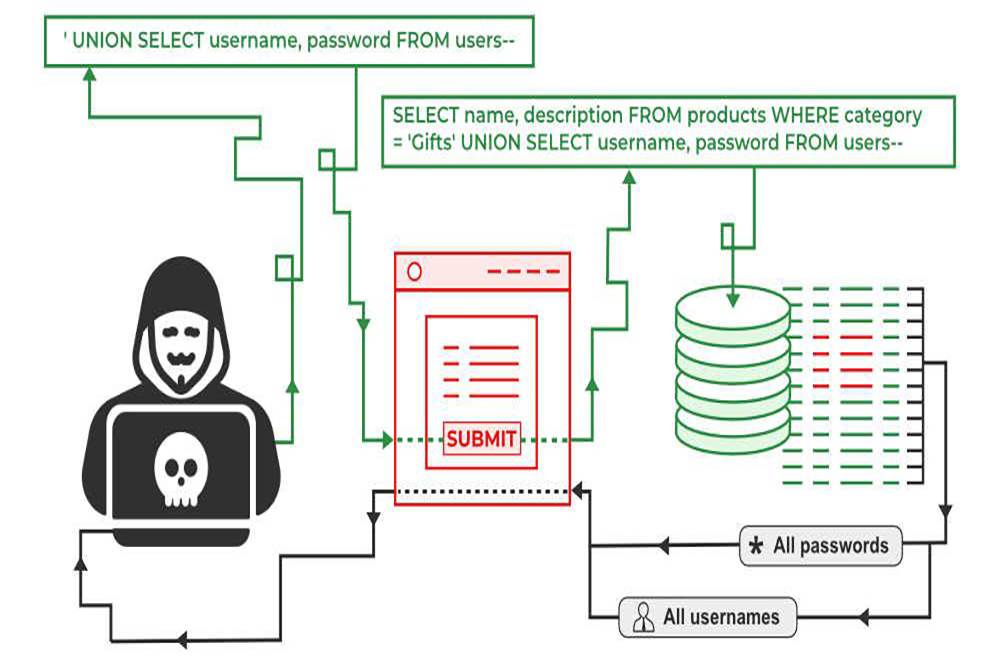
SQL injection (or SQLi) attacks alter SQL queries by injecting malicious code through application vulnerabilities. SQLi attacks that are successful allow a...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067