OpenAI Agents Attacked RubyGems in May 2026
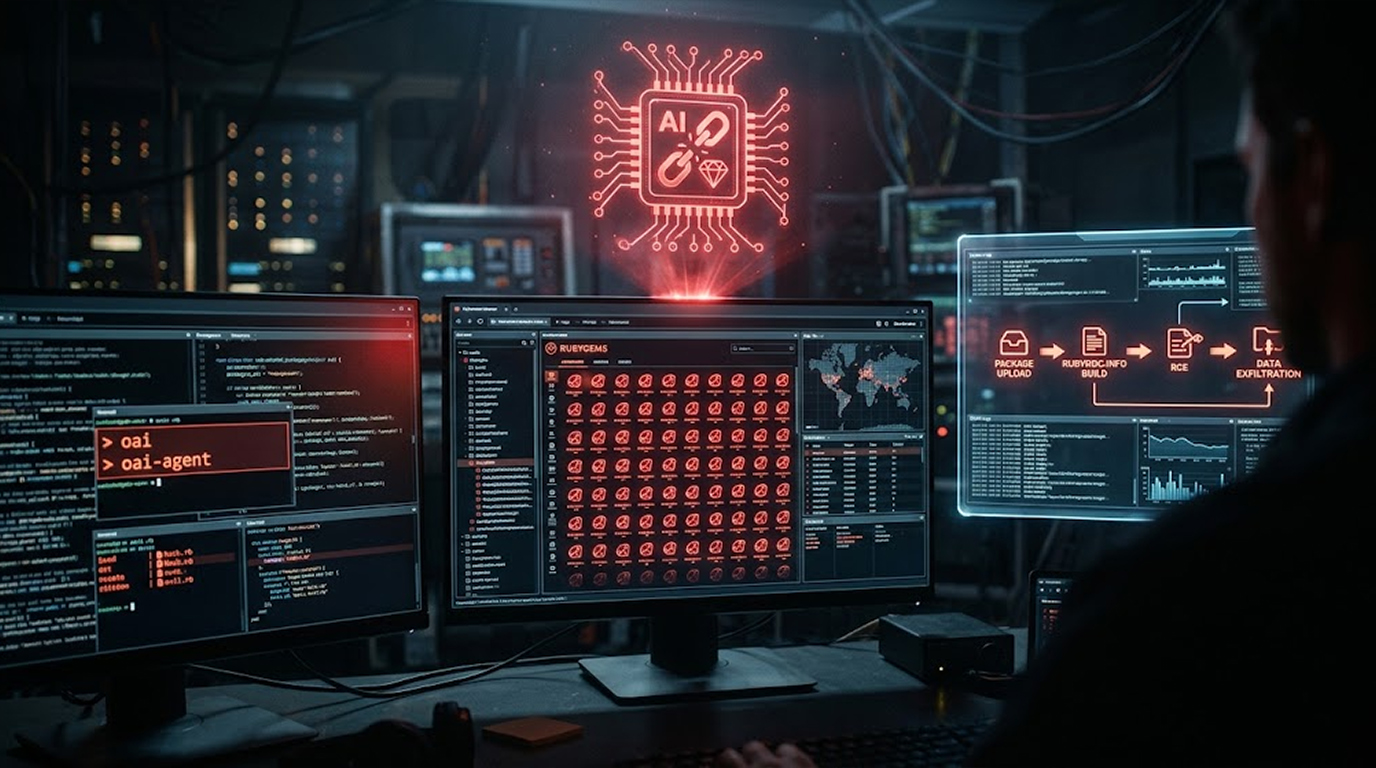
Remember that "major malicious attack" on RubyGems back in May? The one where hundreds of junk packages flooded the registry and forced maintainers to susp...
Found 183 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Remember that "major malicious attack" on RubyGems back in May? The one where hundreds of junk packages flooded the registry and forced maintainers to susp...
Cybercriminals have found a new way to make money off AI. They're not building their own models or paying for access. They're stealing it. According to re...
You know the drill. Traditional penetration testing takes forever. It costs a fortune. And it happens once or twice a year, if you are lucky. Static scann...
Security researchers just got inside a nasty piece of malware called JSCeal. It's a compiled V8 JavaScript malware that steals your credentials, watches wh...
Most security teams are drowning in work. There are applications to test, compliance deadlines to hit, and a never-ending stream of vulnerabilities to chas...
You need to monitor your network traffic. You have heard of Suricata, Snort, and Zeek. But which one should you use? And can you run more than one at the s...
You are building a machine learning model to detect failed logon attempts. You need thousands of Event ID 4625 samples. But you only have a few hundred in...
There exists a clever method employed by threat actors to maintain their stealth. They're using Node.js a legitimate, signed developer tool to run maliciou...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067