What Red Team Tools Revealed About the Organization
Red team exercises simulate real-world attackers to find weaknesses before malicious actors do. When the tools are used correctly, they don’t just sh...
Found 46 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Red team exercises simulate real-world attackers to find weaknesses before malicious actors do. When the tools are used correctly, they don’t just sh...
An example of unauthorized network authentication is when an attacker logs into your Wi-Fi, VPN, Active Directory, RDP, SSH, cloud console or any other ser...
Ethical hacking can only be conducted legally and safely. Building a home lab allows you to establish a safe and legal environment to simulate attacks, dev...
The security models of the past are based on the assumption that once someone has gained access to the internal network, that person can be trusted and all...
A China-nexus advanced persistent threat (APT), tracked as UAT-8837 by Cisco Talos, has been observed targeting critical infrastructure sectors in North Am...
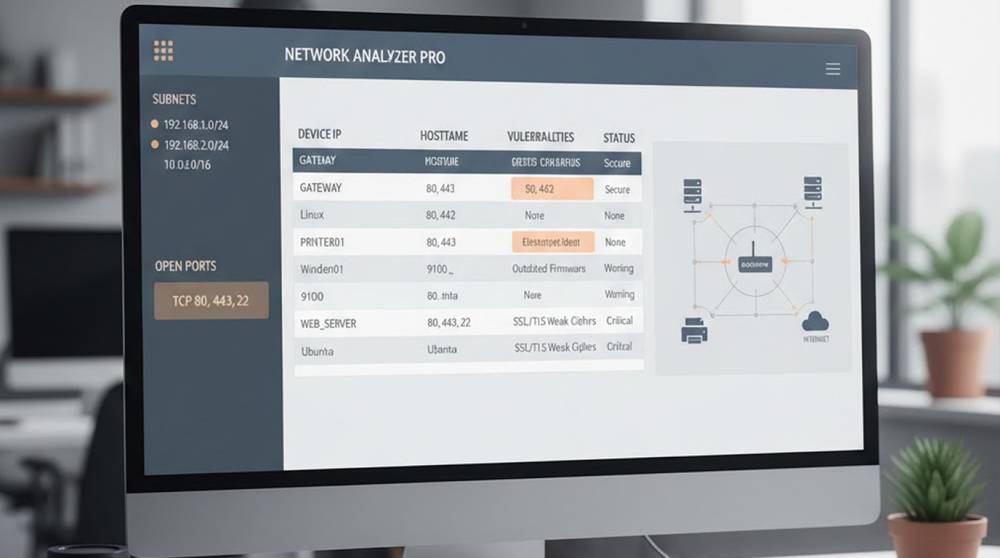
A Red Team not only tests the defenses of the organization during the engagement; however, a well-executed Red Team will also expose:1. The gaps in the mon...
Network segmentation limits lateral movement, so if one system is compromised, attackers cannot freely roam.Weak or inconsistent segmentation is common. Ev...
It Usually Starts SmallNo one wakes up and shuts down a city.It usually starts with something.A forgotten VPN account.An exposed remote desktop service.A c...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067