Redis HLL Overflow → RCE in 8.0.0–8.0.2
A serious remote code execution vulnerability (CVE-2025-32023) was identified in Redis HyperLogLog (HLL) for all versions greater than (>=) 8.0.0 but le...
Found 529 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A serious remote code execution vulnerability (CVE-2025-32023) was identified in Redis HyperLogLog (HLL) for all versions greater than (>=) 8.0.0 but le...
Local privilege escalation vulnerability in the glibc library affects versions 2.35 to 2.38 (build tested: 2.35-0ubuntu3.3) and allows an unprivileged user...
In December 2025, Gen Digital (the parent company of both Norton and Avast) discovered a new WhatsApp account takeover campaign called GhostPairing, which...
Atomic Red Team is an open-source library of small, focused tests mapped to the MITRE ATT&CK framework. These tests simulate real adversary behaviors t...
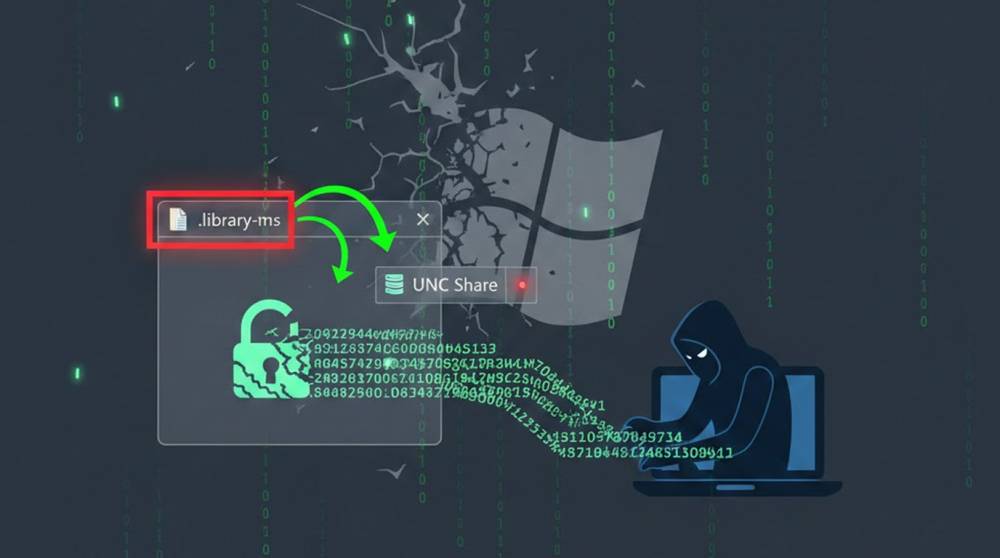
Windows NTLM hash disclosure/relay CVE-2025-24054 exploits how Windows Explorer handles a specially crafted library management file (.library-ms). When a u...
Aggressive or never-ending pop-ups are an annoyance, but they can represent the first signs that your computer has been infected with adware. In addition,...
A drive-by download is sneaky malware that can sneak onto your phone, laptop, or tablet just by visiting a website. You don’t have to click anything,...
Germany's domestic intelligence agency (BfV) and cybersecurity authority (BSI) have jointly warned of an active phishing campaign targeting high-profile in...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067