Red Team vs Blue Team: Command Differences in Linux
You have heard the terms. Red team attacks. Blue team defends. But when you look at the actual commands, what is the difference? The answer is not the too...
Found 77 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You have heard the terms. Red team attacks. Blue team defends. But when you look at the actual commands, what is the difference? The answer is not the too...
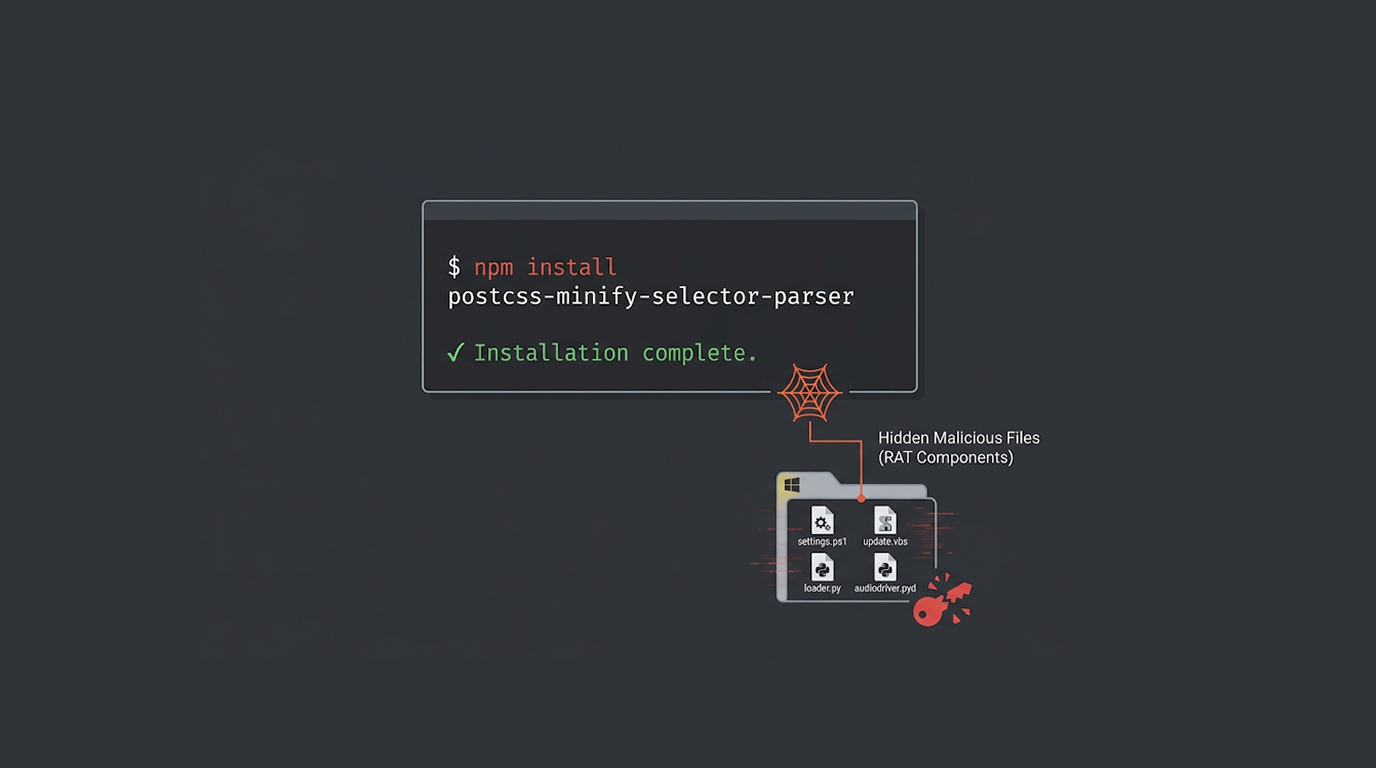
You install a package that looks like a legitimate build tool. It has a name similar to a popular library. It has hundreds of downloads. It seems safe. It...
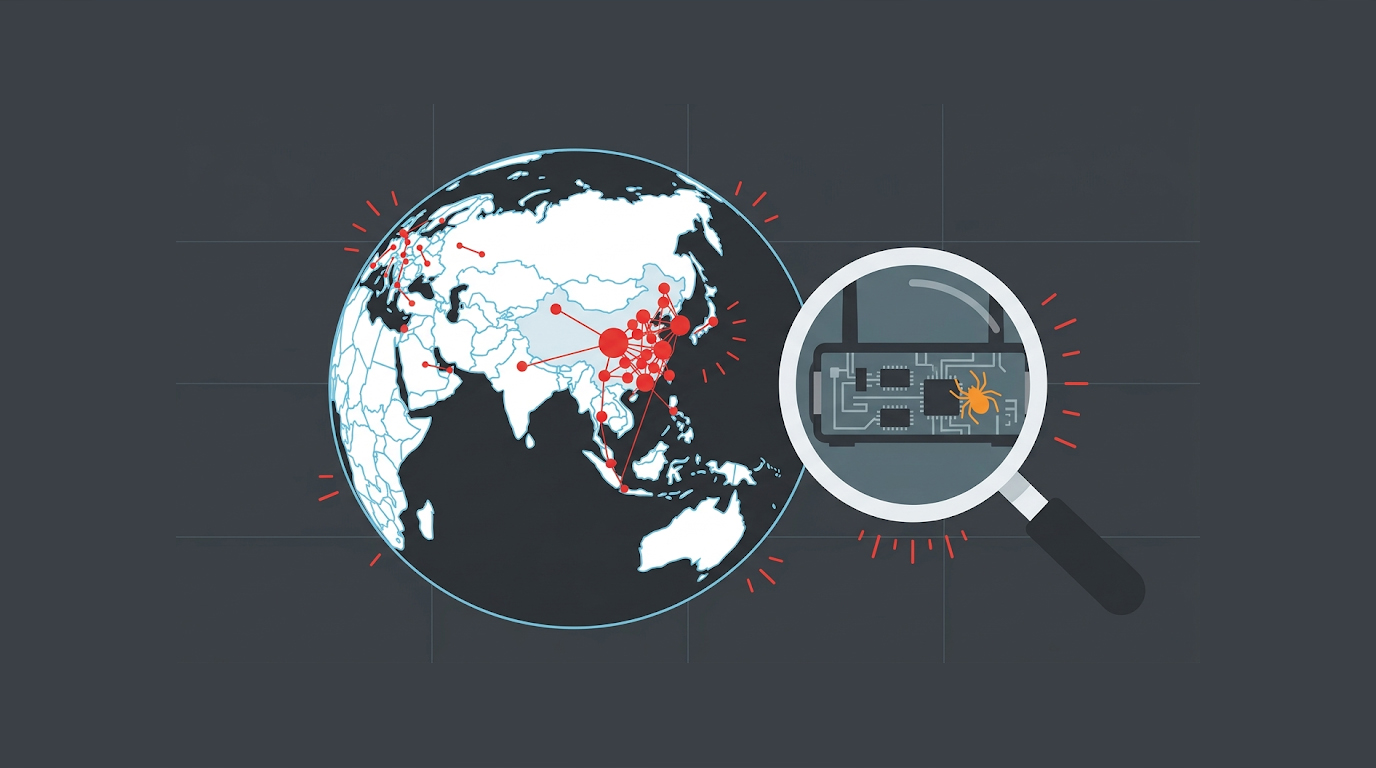
When we talk about botnets, we usually mean armies of compromised devices slamming websites with traffic until they collapse. DDoS attacks, crypto mining t...
In just 88 minutes, a single npm account published more than 140 malicious versions of packages in the Mastra namespace. Mastra is a popular open-source Ja...
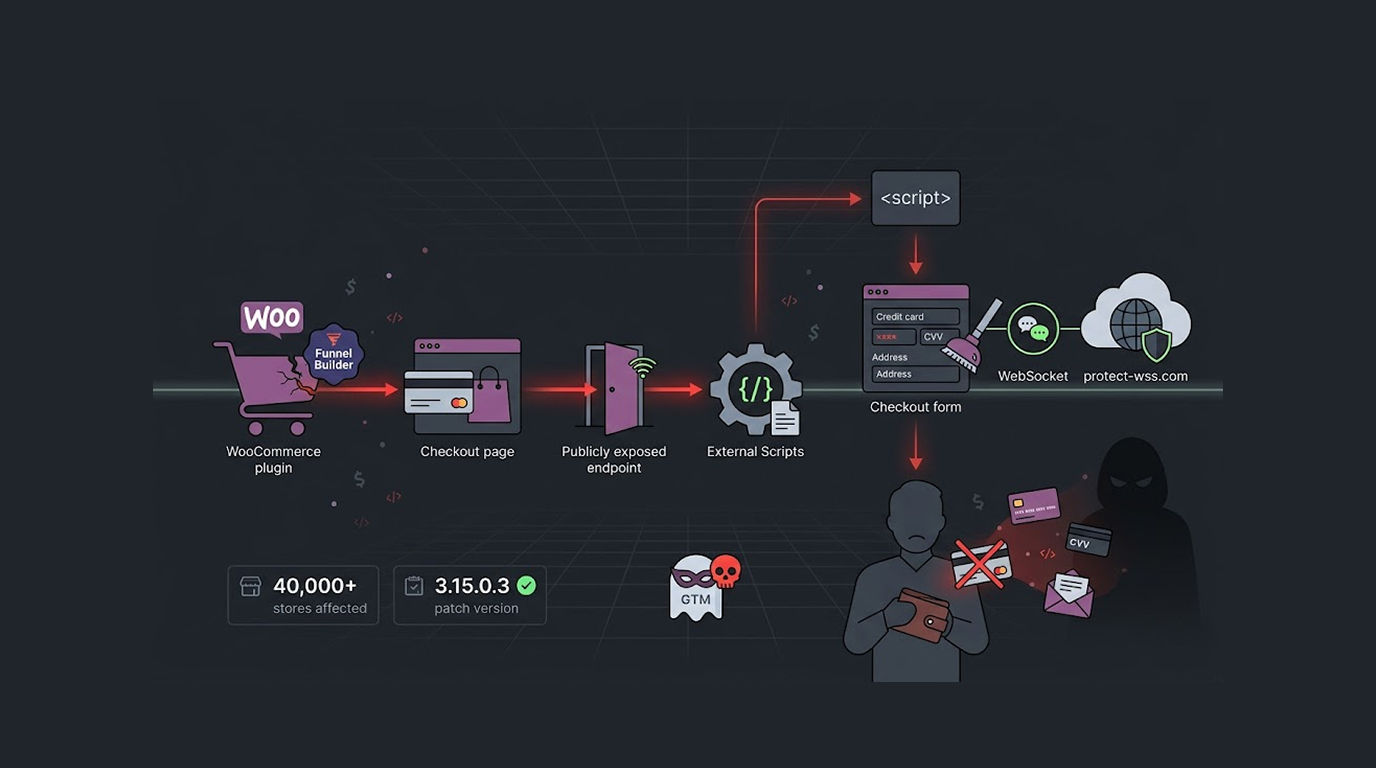
A critical security vulnerability in the Funnel Builder plugin for WordPress is under active exploitation, and attackers are using it to inject malicious J...
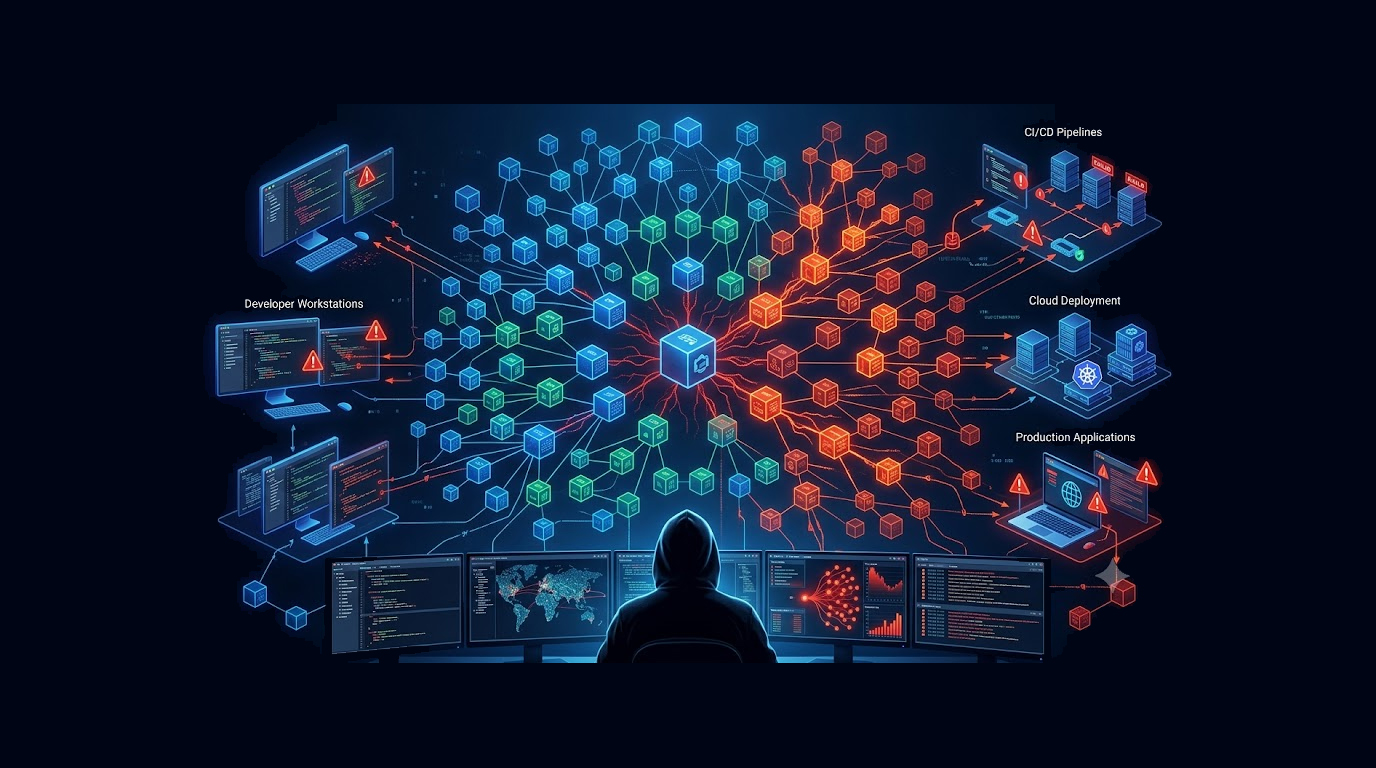
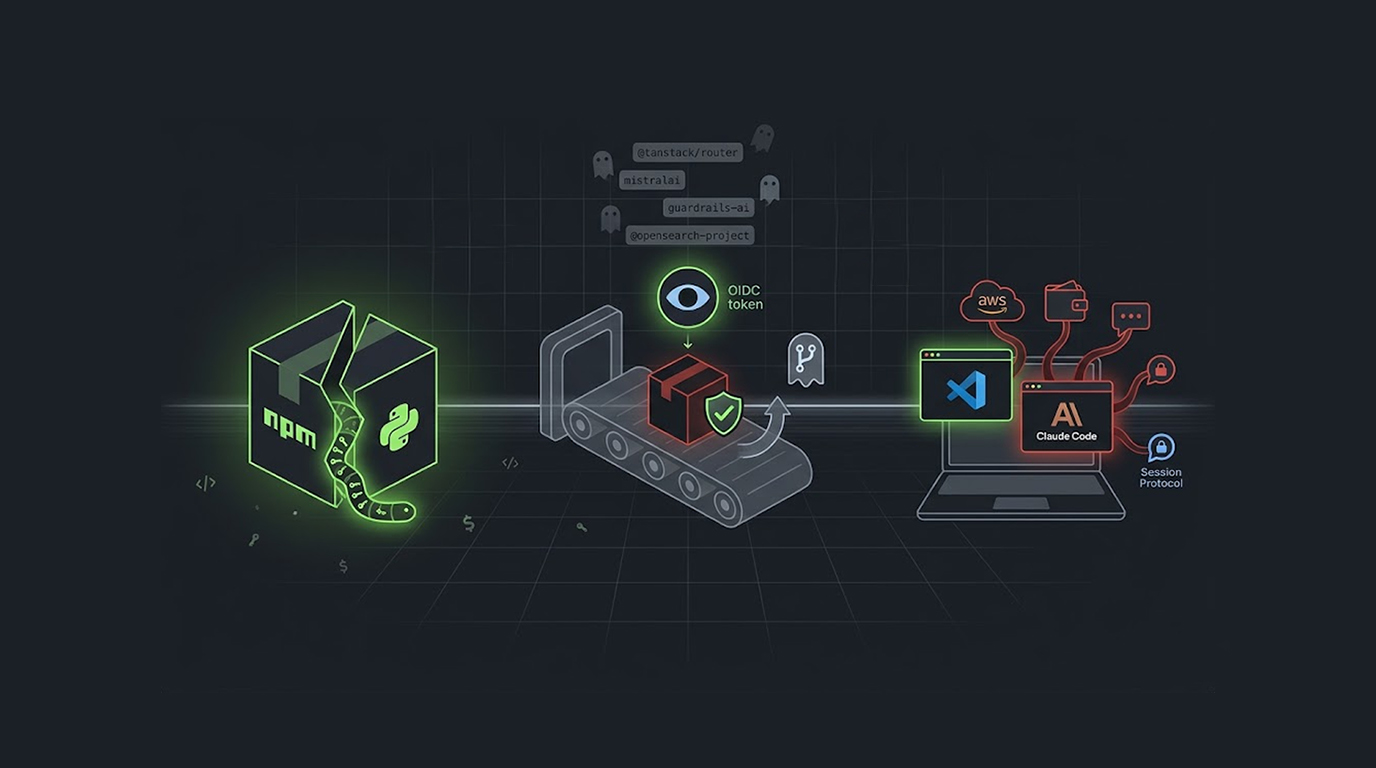
A single worm has spread across both npm and PyPI, it compromised packages from major companies like TanStack, UiPath, Mistral AI, and OpenSearch, and it u...
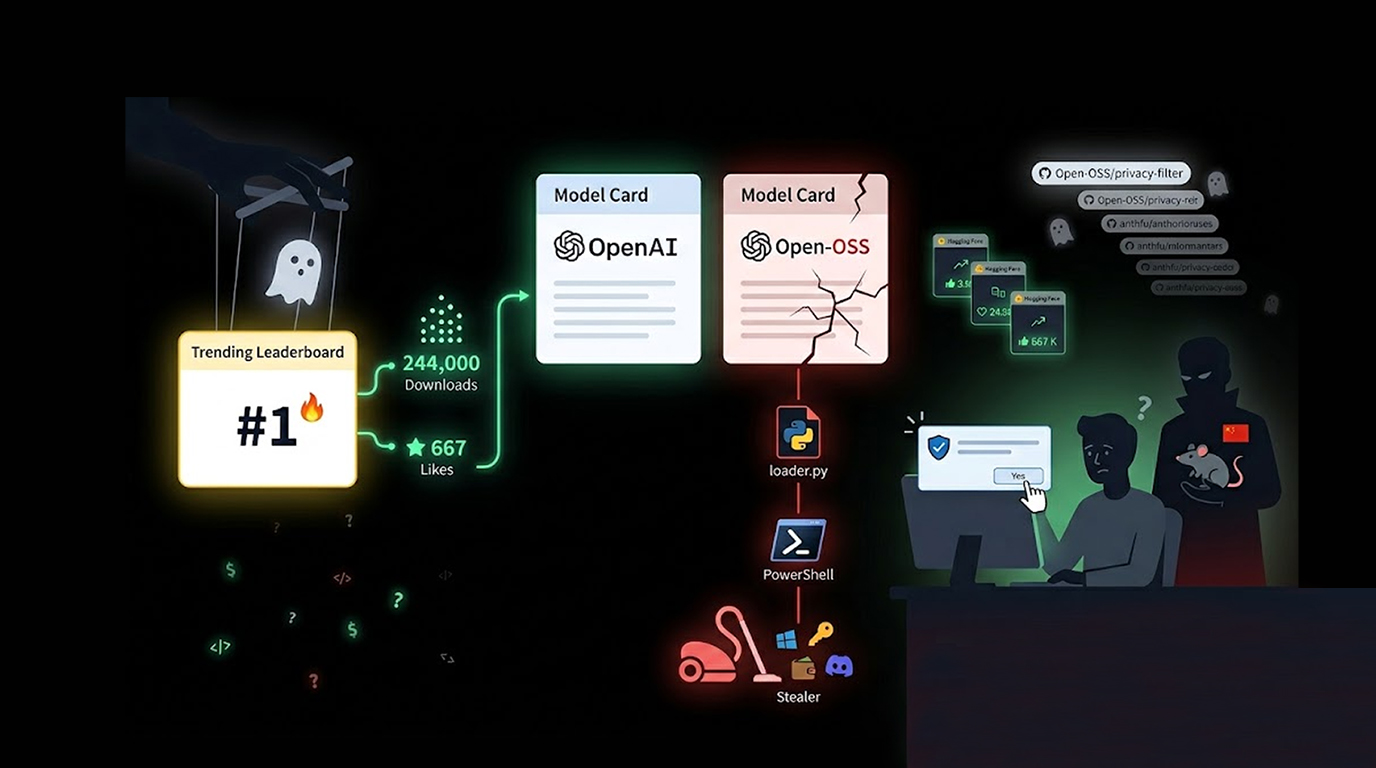
A malicious repository on Hugging Face ranked #1 on the platform by impersonating OpenAI's just-released Privacy Filter model while delivering a Rust-based...
You run npm install. Packages download. Dependencies resolve. The terminal shows a success message.Behind the scenes, postinstall.js executes automatically...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067