SAP Commerce Cloud Vulnerability Allows Unauthenticated RCE
A maximum severity level vulnerability was detected in SAP Commerce Cloud, for which patches have been released by SAP. The vulnerability would allow arbit...
Found 35 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A maximum severity level vulnerability was detected in SAP Commerce Cloud, for which patches have been released by SAP. The vulnerability would allow arbit...
A memory corruption flaw in the Linux kernel's Open vSwitch datapath gives ordinary local users a path to root on a broad set of default-configured distrib...
Security firm runZero has uncovered seven vulnerabilities in FatFs, a lightweight filesystem library that handles FAT and exFAT formats for USB drives and...
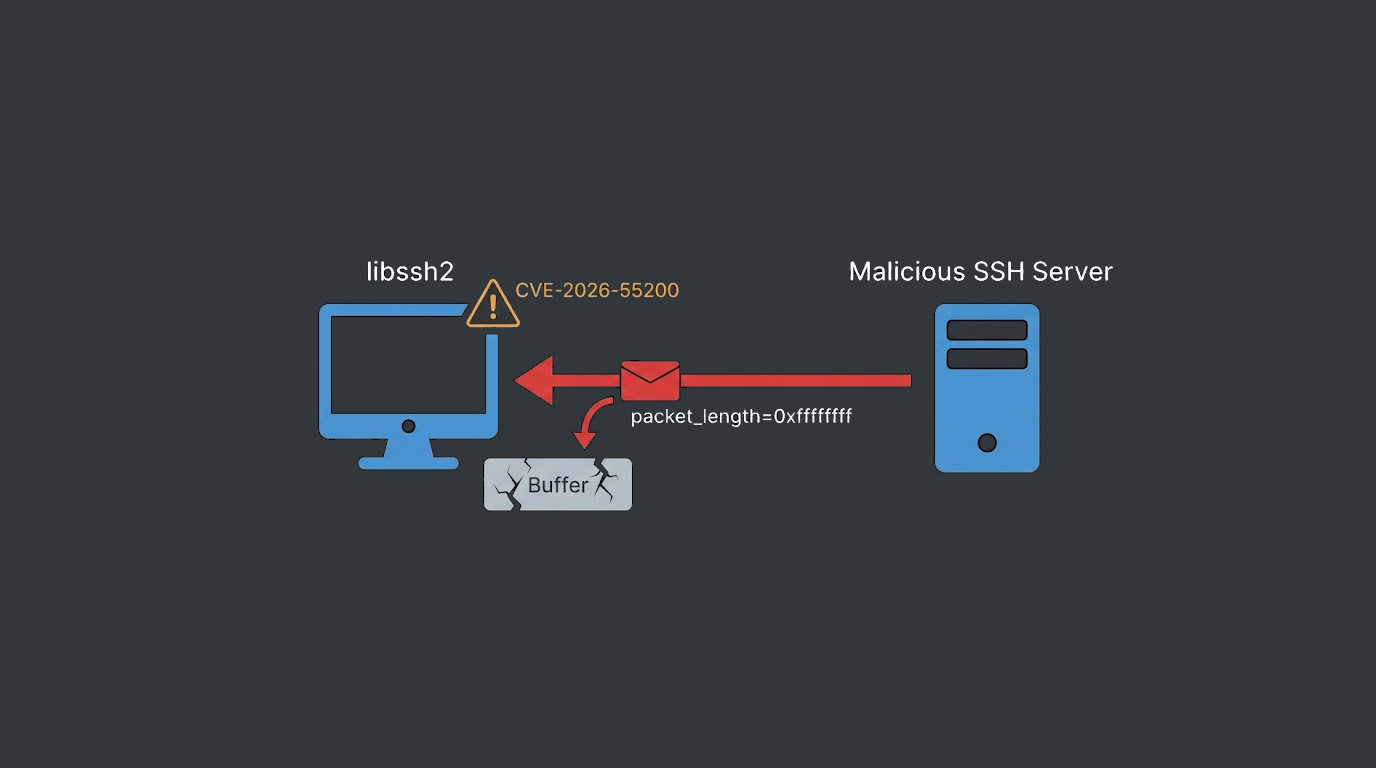
Proof of concept released to the public for CVE-2026-55200 – an extremely critical vulnerability in libssh2 where a malicious SSH server can cause me...
Microsoft has disclosed that two vulnerabilities in Microsoft Defender are under active exploitation, and one of these flaws allows an attacker to gain SYS...
60 seconds to summarize for you about DIRTPIPE (Dirty Pipe) security vulnerability. The TL;DR (10 Seconds) Question Answer What...
A potential compromise in the security of Chrome's CSS Engine, contains a vulnerability (CVE-2026-2441) which was found before even anyone had ever realize...
A single 732-byte Python script. Four controlled bytes. And root access on virtually every Linux machine shipped since 2017. That is the reality of Copy F...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067